


- Audit management software automates evidence collection, control monitoring, and auditor workflows so teams spend less time chasing documents and more time closing gaps.
- The tools here span compliance-first platforms (Scrut, Drata, Sprinto) and enterprise audit systems (Optro, Archer IRM, LogicGate).
- Judge each one on framework breadth, integration depth, continuous monitoring, auditor collaboration, and pricing transparency.
- Scrut supports 70+ frameworks, automates up to 70% of evidence collection, and runs daily checks against 230+ CIS benchmarks.
As compliance requirements grow and audit cycles get more frequent, security and compliance teams end up chasing evidence across spreadsheets, email chains, and last-minute scrambles that eat weeks of work every cycle. This causes audit prep to break down.
Two distinct audiences buy in this category, and this guide covers both.
If you run an internal audit program, Optro and Archer IRM are the clearest fits. If you are a GRC, security, or engineering team preparing for external audits against SOC 2, ISO 27001, HIPAA, or PCI DSS, the compliance-first platforms below will fit your workflow better.
The cost of getting this wrong compounds: 85% of compliance leaders say requirements have grown more complex over the past three years, and 82% say that complexity is already dragging on their ability to transform and adapt (PwC Global Compliance Survey 2025). That is time and money lost on every audit cycle, not just once a year.
This guide breaks down the 7 best audit management platforms in 2026, judged on automation depth, integrations, framework breadth, and audit readiness.
Audit management software compared: 8 tools at a glance
Top 7 audit management software: our best picks for 2026
1. Scrut Automation
Scrut is a compliance automation platform with integrated risk management, built to take cloud-native startups, mid-market companies, and enterprises from scattered evidence to audit-ready in weeks. It runs governance, risk, and compliance in a single platform rather than stapling three tools together.
Key features
- Continuous control monitoring. Scrut runs daily automated control tests across your cloud infrastructure and internal systems, benchmarking against 230+ CIS benchmarks. It flags gaps and misconfigurations in real time and assigns remediation tasks with automated alerts, so your controls stay healthy between audits, not just during them.
- Automated evidence collection. Scrut connects to 150+ integrations across cloud platforms, identity providers, and HR tools to automatically collect and map audit evidence across frameworks. This automates up to 70% of evidence collection. See how automated evidence collection works.
- Scrut Teammates (agentic AI). Scrut Teammates detects evidence gaps before auditors see them and maps policy documents to the controls they satisfy. In practice, the gap that would have surfaced during fieldwork gets flagged while you still have time to fix it.
- Native DAST. Scrut DAST adds native dynamic application security testing with CVSS severity scoring and external-ready PDF reports, removing the need for a separate scanning tool.
- Unified Controls Framework (UCF). The UCF maps risks and artifacts to controls to minimize duplication across frameworks. Adding a new framework only asks for evidence against controls not already covered.
- Audit center. Scrut's audit center gives you framework-specific checklists, control-level compliance overviews, and a centralized dashboard to collaborate with auditors, track requests and findings, and generate audit reports. BYOA (Bring Your Own Auditor) support with auditor SLA tracking keeps requests in one tracked workflow.
- Integrated risk management. The risk management module includes a risk register with custom fields and custom scoring: CIA triad, Risk Priority Number, or your own formula.
- Security questionnaires and Trust Portal. Unlimited AI-automated security questionnaire responses, plus a customer-facing Trust Portal for on-demand security documentation.
- Scrut also supports 70+ compliance frameworks, with custom framework creation at no additional cost and hands-on InfoSec expert support included.
Pros
- Automates up to 70% of evidence collection.
- Includes auditor-vetted policy templates and framework checklists.
- All modules included — no feature-based pricing walls.
- Hands-on InfoSec expert support included.
Cons
- Complements, but does not replace, your entire security stack. Scrut is best used alongside your existing security-only tools.
Pricing
Scrut uses Foundation, Growth, and Scale tiers. All modules are included, with no add-on fees for auditors or pen-testers and no extra charge for up to 5,000 users.
2. LogicGate
LogicGate's Risk Cloud is built for teams that need to configure their own GRC workflows without writing code. The platform grows with compliance requirements, which is why it tends to land with larger teams that have outgrown pre-built templates.
Key features
- Internal audit management. Pre-built workflows record controls, risks, logs, and findings in one centralized dashboard, so audit evidence does not live in scattered systems.
- Automated control testing. LogicGate assigns control tests, evidence requests, audit findings, and remediation workflows automatically, tying internal control verification into the audit program.
- Config Newton. Launched in Spring 2026, Config Newton is an agentic GRC engineer that builds and configures workflows from natural-language input rather than manual setup.
Pros
- Highly configurable platform that adapts to specific program requirements.
Cons
- Teams evaluating LogicGate alongside other platforms have noted limited pre-built templates, higher cost for small businesses, and a learning curve despite the no-code positioning.
Pricing
GRC applications and Power User licenses are priced separately, with add-on paywalls for some features. Contact LogicGate for custom pricing.
3. Archer IRM
Archer IRM's core bet is a single data model that connects enterprise, IT, operational, and third-party risk. Audit, risk, and compliance teams work from the same record, not separate systems they later reconcile. It is built for enterprise GRC programs, not mid-market compliance teams.
Key features
- Issues management. Issues raised by compliance, risk, and audit teams are tracked in one place, so findings from an internal audit and a compliance gap assessment do not live in separate systems with separate owners.
- Risk-based audit planning. Audit plans are built from the risk register, so the highest-risk areas get audited first rather than following a fixed calendar. Board-level reporting pulls from the same data, which removes the manual slide-deck assembly most audit teams still do.
- Archer Evolv. Archer Evolv (SaaS) monitors 8,000+ regulatory sources across 230+ jurisdictions, surfacing regulatory change before it becomes an audit gap.
Pros
- Single data model connects audit, risk, and compliance teams. Findings from an internal audit and a compliance gap assessment share the same record, which eliminates the reconciliation step most enterprise teams still do manually.
Cons:
- Requires significant implementation investment before it’s audit-ready. The platform’s breadth means teams spend considerable time on configuration before it works for their specific risk program. For enterprise GRC teams with dedicated implementation resources, this is manageable. For mid-market teams, it’s a real time-to-value problem.
- Archer does not ship with a pre-mapped framework library. Organizations must build or import their own control libraries, or purchase content packs separately through the Archer Exchange, which adds cost and lead time before a single audit can run.
Pricing
Enterprise, custom pricing. Contact Archer's team for a quote.
4. Sprinto
Cloud companies that need SOC 2 or ISO 27001 fast are Sprinto's core market. It automates key compliance automation processes and streamlines audit prep for teams moving quickly. Sprinto describes itself as the "World's first Autonomous Trust Platform."
Key features
- Security management. Sprinto integrates cloud and SaaS applications to identify security and compliance gaps, then automates mitigation workflows to reach audit readiness.
- Fix-it Agent. The Fix-it Agent handles auto-remediation across monitors, closing common failures without manual intervention.
- AI Governance. AI Governance covers ISO 42001, NIST AI RMF, and the EU AI Act, which is increasingly relevant as AI compliance obligations land.
- Collaboration dashboard. Share audit assets with auditors, provide requested documents, and track audit status from one centralized dashboard.
- Sprinto covers 200+ frameworks digitized and 25+ automated, including SOC 2, ISO 27001, GDPR, HIPAA, PCI DSS, ISO 42001, and the EU AI Act.
Pros
- User-friendly interface, easy-to-deploy integrations, and responsive support.
Cons
- Teams evaluating Sprinto alongside other platforms have noted that query response times can lag and that the platform can feel expensive for multi-framework programs.
Pricing
Foundation and Growth tiers, with enterprise add-ons for Risk, TPRM, and AI Governance.
5. Hyperproof
Hyperproof's strongest differentiator is Hypersync, cross-framework evidence sharing that reduces the manual work of maintaining controls across multiple audits at once. It fits mid-market compliance operations teams running several frameworks in parallel.
If you are weighing it against other tools, see Hyperproof alternatives.
Key features
- Hypersync. Hypersync connects 70+ integrations for cross-framework evidence sharing and control reuse, with a no-code workflow builder so teams can configure without engineering support.
- Controls integration. Controls and related evidence link automatically to audit needs, cutting prep time.
- Audit tracker. Monitor pending evidence requests, track audit status, and review progress on central dashboard.
- Hyperproof supports 70+ frameworks.
Pros
- Easy-to-implement solution with a clean UI and broad multi-framework support.
Cons
- Hypersync limits the proof types it can collect automatically for continuous monitoring, so some evidence still requires manual handling.
Pricing
Per-user tiers: Starter, Professional, and Business. Pricing is not published publicly.
6. Drata
Drata's Audit Hub is the feature that most distinguishes it from other compliance automation platforms. It brings auditors directly into the platform for sampling and evidence requests, rather than routing everything through email. If you are comparing options, see Drata alternatives.
Key features
- Audit Hub. Auditors work inside the platform for sampling and requests, which keeps the back-and-forth in one tracked place.
- Automated workflows. Drata automates evidence collection and gives clear visibility into auditor requests and pending items from a centralized dashboard.
- AI Questionnaire Assistance. Included across all tiers, it drafts security questionnaire responses.
- Drata supports 50+ frameworks, including SOC 2, ISO 27001, GDPR, HIPAA, ISO 42001, DORA, FedRAMP, CMMC, and Cyber Essentials. Drata has moved quickly on emerging requirements. It added AIUC-1 support in July 2026, APRA CPS 230 for Australian financial services in July 2026, and AI Agent Governance in June 2026.
Pros
- Strong customer support with live chat and a 24/7 chatbot.
Cons
- Modular pricing means Trust Center and Trust Vault sit behind a paywall, custom frameworks cost extra, and auditors and pen-testers are charged separately.
Pricing
Foundation (1 framework, up to 50 FTEs), Advanced, and Enterprise tiers.
7. Optro (formerly AuditBoard)
Optro (formerly AuditBoard, rebranded March 2026) is an enterprise GRC and connected-risk platform. It positions itself as an "agentic system of action" across audit, risk, InfoSec, and compliance. On this list, it is the clearest enterprise and Fortune 500 internal audit pick.
If you are comparing options, see Optro alternatives.
Key features
- Automated audit workflows. Optro automates audit planning, fieldwork, testing, remediation, and reporting to cut manual effort across the audit lifecycle.
- Centralized dashboard. Manage risks, evidence, and compliance issues from one connected-risk hub with real-time status visualization.
- Integrations. Connect across CRM, HRIS, accounting, and identity and access management to scale audit, risk, and compliance programs.
- Optro is trusted by 50%+ of the Fortune 500 and was named a Gartner Magic Quadrant Leader in 2025. It acquired FairNow to add AI governance capability. Supported frameworks include SOC 2, ISO 2700x, NIST, CMMC, PCI DSS, and custom frameworks.
Pros
- Intuitive UI with strong global expert support.
Cons
- Teams comparing Optro with other platforms have noted no built-in third-party vendor risk management module and some admin setup complexity.
Pricing
Enterprise, custom pricing. Request a demo and quote through Optro's site.
How to choose audit management software: 10 key features that matter
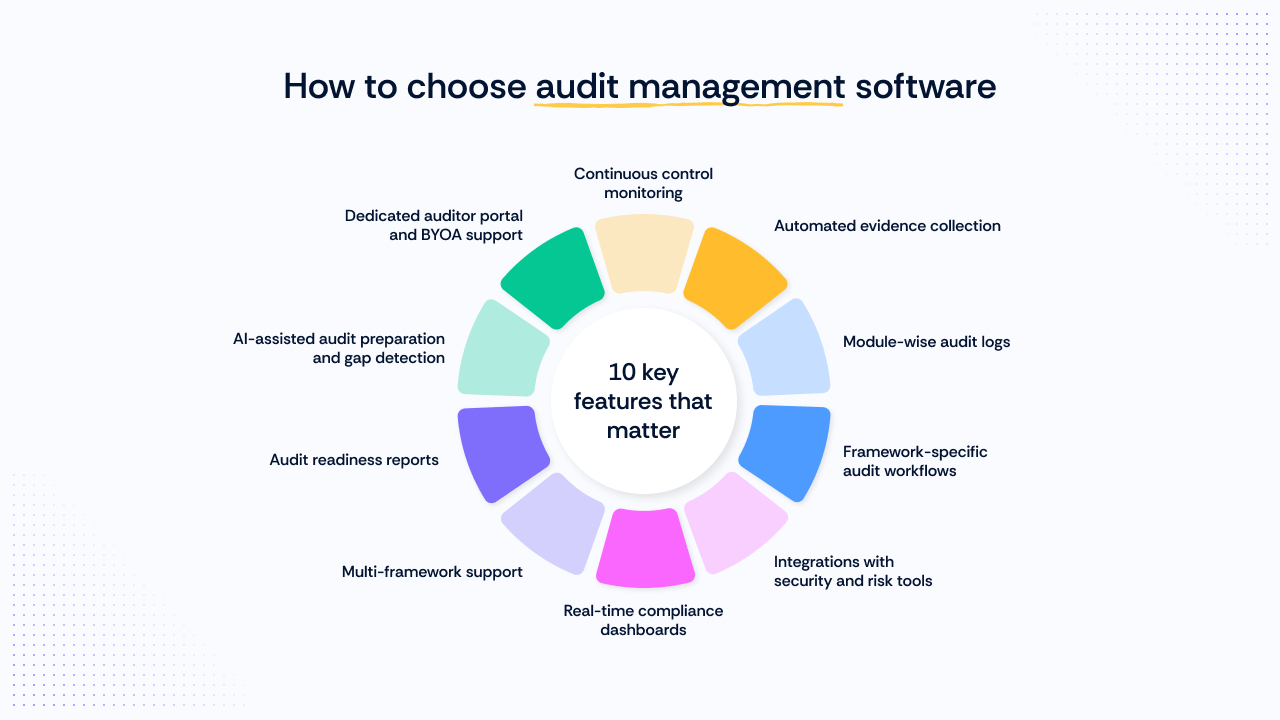
Preparing for an audit manually is time-consuming and risky. Missed evidence, outdated controls, or version mismatches can stall an audit or cause a report to fail. Here are the features that matter, and why.
1. Continuous control monitoring
A control that passed your last SOC 2 audit can drift out of compliance within weeks of the audit window closing. Continuous control monitoring tracks your controls across frameworks like SOC 2, ISO 27001, and HIPAA year-round, giving you real-time visibility into whether each control is active and effective. This is the core of continuous compliance.
2. Automated evidence collection
Top platforms connect to your cloud providers, identity tools, and ticketing systems to pull audit-relevant evidence automatically. Instead of chasing screenshots or exporting logs by hand, the platform collects and maps evidence to your controls in real time. This reduces prep time and eliminates the human error that creeps in during a manual scramble. See how automated evidence collection works.
3. Module-wise audit logs
For a clean audit, you need to track every action inside your compliance platform. Audit logs record every change, update, and addition across controls, evidence, policy, risk, and audit modules, with a timestamp, user ID, and the action performed. When an auditor asks "who changed this control, and when?", the answer is one query away.
4. Framework-specific audit workflows
The strongest platforms double as SOC 2 compliance software while covering other frameworks in parallel. That matters more now that DORA, NIS 2, ISO 42001, and CMMC are common requirements alongside SOC 2 and ISO 27001.
Built-in workflows walk your team through scoping, assigning owners, tracking progress, and generating reports, so you reuse shared controls and evidence across audits instead of starting from scratch. See the compliance frameworks overview
5. Integrations with security and risk tools
Integration quality matters more than raw count. A broken AWS connector that silently stops pulling IAM evidence is worse than no connector, because you think you are covered until the auditor asks for the last 90 days of access reviews and the evidence is missing.
Evaluate deep integrations with cloud providers (AWS, GCP, Azure), identity providers (Okta, Google Workspace), and ticketing (Jira, Linear). Scrut's 150+ integrations link risks to compliance controls through its risk management module.
6. Real-time compliance dashboards
Dashboards should show exactly where you stand: which controls pass, which are overdue, where evidence is missing, and how far along each audit is. Instead of hunting across spreadsheets, you get a live snapshot of your audit posture and can drill into specific frameworks like SOC 2 or ISO 27001.
7. Multi-framework support
Multi-framework support is not just about the count of frameworks a platform covers. It is about how the platform handles the overlap. The best implementations let you add a new framework and only ask for evidence against controls not already satisfied, so ISO 27001 does not restart work you already did for SOC 2. See the compliance frameworks overview.
8. Audit readiness reports
Great tools help you prove compliance, not just track it. Audit readiness reports consolidate control statuses, evidence logs, gaps, and mitigation actions into a clean, exportable format, often by framework, so you can share the right information with auditors and executives before they ask.
9. AI-assisted audit preparation and gap detection
AI does three things in an audit context that used to require manual review: it detects evidence gaps before your auditor sees them, maps policy documents to the controls they satisfy, and auto-responds to security questionnaires.
The payoff is fewer pre-audit scrambles, because gaps surface while you still have time to fix them. Competitors position AI differently (Optro's agentic system, LogicGate's Config Newton, Drata's AI Questionnaire Assistance), and Scrut's implementation is Scrut Teammates.
When you evaluate platforms, look for AI that reduces manual review work rather than AI that simply summarizes what you already know.
10. Dedicated auditor portal and BYOA support
An auditor portal gives your auditor role-based access to evidence and reports directly in the platform, instead of email threads and shared drives. Role-based access reduces back-and-forth and protects internal data the auditor does not need to see.
BYOA (Bring Your Own Auditor) means you can bring the auditor you already trust into the platform rather than being locked into the vendor's network, which matters for procurement flexibility. Scrut's dedicated audit center supports both.
Partner with Scrut to become audit-ready within weeks
If preparing for audits still means chasing evidence across spreadsheets, folders, and emails, you are losing time and setting yourself up for a last-minute scramble. Scrut gives your compliance, audit, and risk teams one platform to reduce audit effort and scale compliance as the business grows.
- Automated evidence collection across 150+ integrations to eliminate manual tracking.
- AI-powered gap detection via Scrut Teammates, which flags missing evidence before your auditor does.
- Scrut DAST folds application security evidence directly into your compliance program, with no separate scanning tool and no manual export. See native DAST.
- Pre-audit gap assessments that name specific missing controls and assign owners, so findings surface before the auditor does.
- A dedicated audit center with BYOA and role-based auditor access.
- Pre-mapped controls with continuous monitoring to catch issues in real time.
- Run multiple audits in parallel without duplicating evidence, 70+ compliance frameworks, one control library.
- Expert InfoSec guidance included in every tier; no add-on fees, no hidden costs.
Streamline your audits with Scrut. Book a demo to see automated, simplified GRC in action.
To automate evidence collection, Scrut offers 100+ integrations with popular business applications across various categories, including HRIS, CRM, IT, project management, collaboration, and security tools. This streamlines operations, enhances accuracy, and accelerates your business’s audit readiness while minimizing non-compliance risks.
Yes, Scrut supports 50+ compliance frameworks and offers essential features like pre-built control libraries mapped to specific industry standards, automated repetitive compliance processes, reusing overlapping evidence for different frameworks, customizable workflows, and reporting templates for each framework. This eliminates task redundancy, efficiently manages multiple audits on a single platform, and scales your compliance programs as needed.
Scrut addresses this by providing multi-framework support (including for various regions and industries), robust integrations with cloud platforms, and continuous control monitoring. It also offers streamlined reporting and workflow automation with flexible configurations to handle evolving regulations, such as GDPR and CCPA, as well as emerging global privacy laws.