

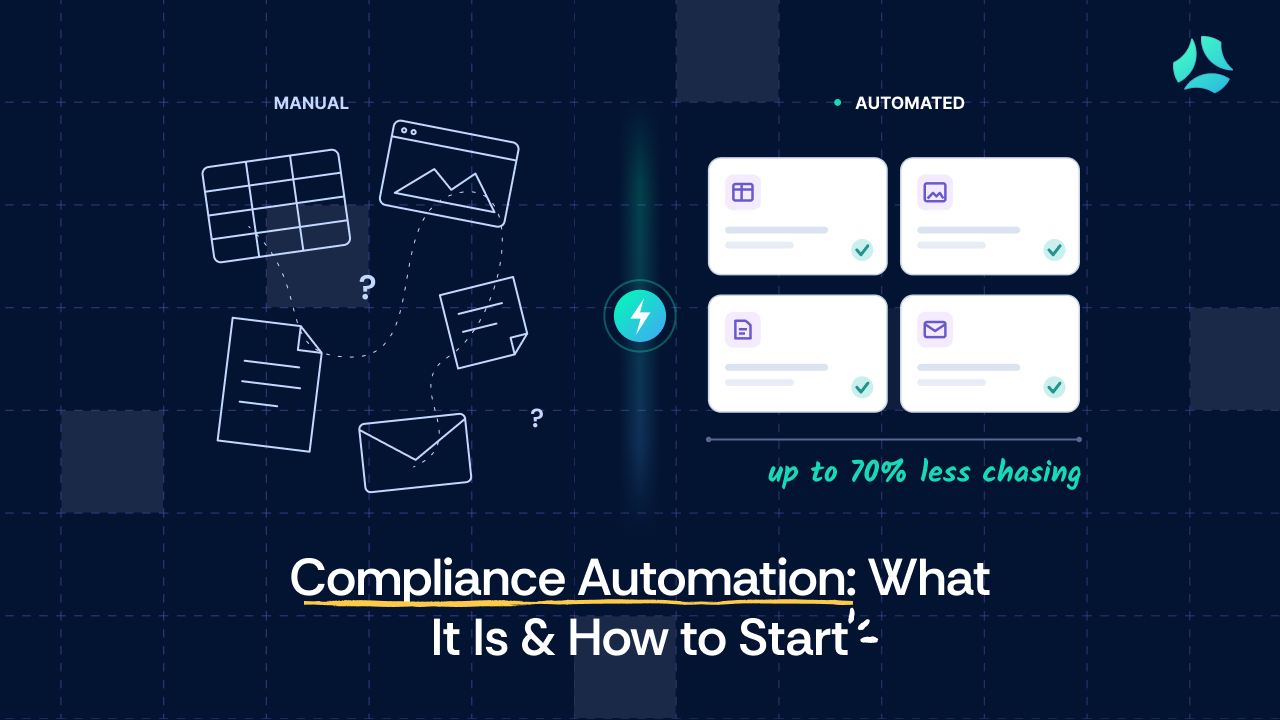


- Compliance automation uses software and AI to replace manual GRC workflows across evidence collection, controls testing, risk assessment, and audit preparation.
- Manual processes leave compliance data siloed, error-prone, and hard to scale. Automation centralizes oversight and can cut evidence-collection effort by up to 70%.
- Automate your highest-volume work first. Evidence collection, cloud controls testing, and security questionnaire responses deliver the fastest return. Access reviews, vendor risk, and policy management follow.
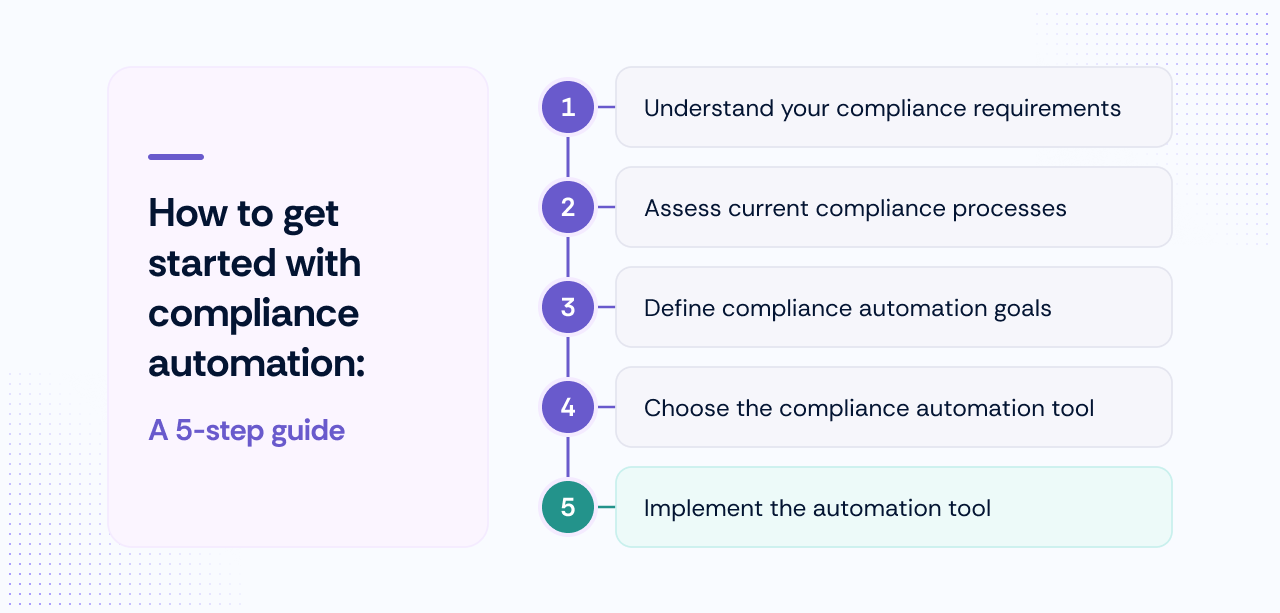
- Getting started takes five steps: scope your frameworks, audit current processes, set measurable goals, choose a platform, and implement with human oversight.
- Evaluate tools on framework coverage, integration depth, continuous monitoring, and transparent pricing.
A single missing SOC 2 report can stall a six-figure deal at procurement. An audit window can pull three engineers off a sprint to gather screenshots the week before it closes. If you own compliance without a full-time CISO, you have felt at least one of these.
This guide is for the people who carry that load: GRC and compliance managers, security managers, and the heads of engineering and CTOs who inherit security questionnaires because no one else knows the infrastructure well enough to answer them.
Manual compliance holds up for a while, then it doesn’t. In Regology’s 2025 State of Regulatory Compliance Survey, about 77% of compliance teams said they still run on manual processes, and 79% still track compliance requirements in spreadsheets.
Below, you will find what compliance automation actually does, which processes to automate, how to get started in five steps, and how to evaluate the tools on the market.
What is compliance automation?
The short definition
Compliance automation uses software and AI to replace manual compliance workflows by automating tasks like evidence collection, control testing, risk assessment, and reporting. It does not produce compliance on its own.
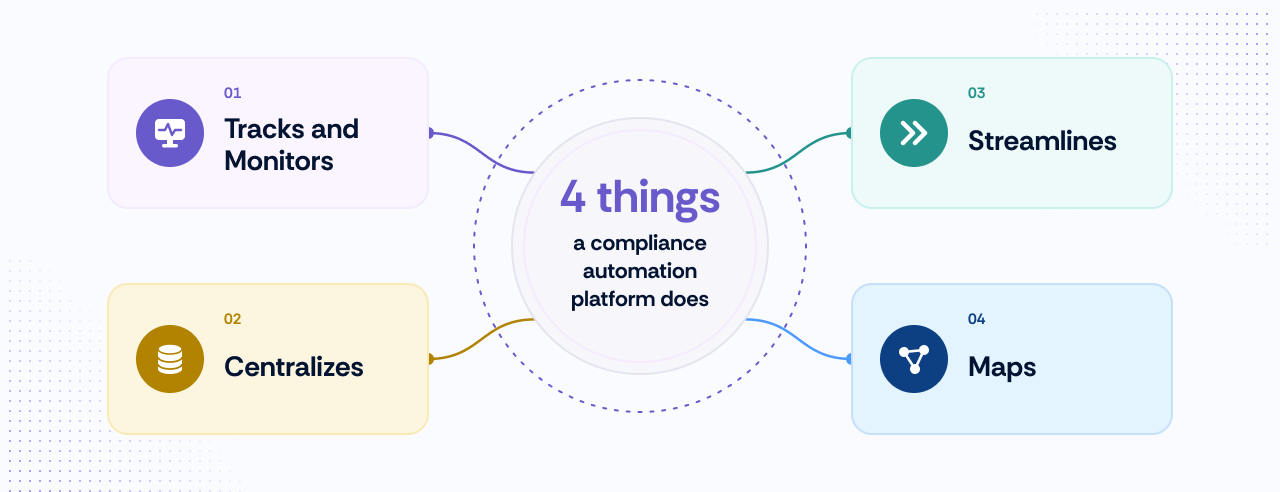
In practice, a platform does four things well:
What compliance automation does not do. It does not make human judgment calls for you. Deciding whether a control is effective, accepting a risk, interpreting how a regulation applies to a new business process, and signing a management assertion are all human acts no platform can substitute.
Also worth stating plainly: passing a compliance check does not make you technically secure. An attestation confirms controls were designed and operating during a defined period. It says nothing about a misconfiguration introduced the day after the window closed.
If you are weighing automation as part of a wider program, it fits inside broader GRC automation and underpins continuous compliance.
What compliance processes can you automate?
Most of the manual work in a compliance program clusters in a handful of repeatable processes. Here is where automation earns its place, and where it does not.
Testing of cloud and app systems
Cloud and application testing continuously validates security, access controls, and configuration settings that standards like ISO 27001 and HIPAA require. When done manually, these checks happen periodically, so a misconfigured S3 bucket can sit exposed for weeks between reviews.
Automated testing detects misconfigurations, unauthorized access, and vulnerabilities in near real time and produces audit-ready documentation as it goes. A platform like Scrut runs daily checks against 230+ CIS benchmarks, giving you a realistic picture of cloud posture rather than a point-in-time snapshot. See how automated controls testing works in practice.
Risk assessment
Manual risk assessments produce incomplete analysis and are a common reason SOC 2 and ISO 27001 timelines slip. Automation lets you identify risks, prioritize by severity, recommend mitigations, and track controls against each risk.
Good tooling computes both inherent and residual risk, the raw exposure before controls and what you actually carry after them, and keeps both current in a risk register rather than a stale Excel file. Pre-loaded risk libraries speed up the first pass, and heatmaps turn findings into something leadership can act on.
Mapping controls
Add a second framework manually and you redo work you have already done. Compliance platforms use pre-built templates for standards like ISO 27001, SOC 2, HIPAA, and GDPR, so you can map controls to requirements once and reuse that work.
A single repository manages every control, and when a control or regulation changes, the workflow updates mappings and flags gaps. Each requirement links to its proof, whether that is a log file, test result, or policy document, which makes audits faster and more accurate.
Creating policies
Manual policy management is slow and prone to decay. As regulations change, automation maps new rules and risks to existing policies and flags the gaps. It assigns policies to employees by role, reminds stakeholders of review deadlines, and builds an auditable trail at every step, so your policies stay current and people always have the latest version.
Evidence collection
Evidence management means collecting proof of compliance and storing it in one repository. Manually, that is screenshots, spreadsheets, and uploads. Automated evidence collection integrates with your tools and pulls data on a schedule you set, reducing manual evidence-gathering effort by up to 70%. The result is continuous evidence management, not a pre-audit scramble.
Collecting responses for security questionnaires
A security questionnaire evaluates an entity's security practices and posture. Information lives across teams and systems, making every questionnaire a recurring sales-cycle blocker: a single enterprise questionnaire can take hours, and they arrive constantly once you sell upmarket.
Automation stores standardized answers, uses pre-approved response libraries, auto-fills from past submissions, and maps responses to the relevant controls and certifications. Scrut supports unlimited, AI-automated questionnaire responses, so the volume stops being a tax on your sales cycle.
User access reviews
Nearly every framework requires periodic access reviews on the principle of least privilege. The implementation scales with headcount: an annual Excel review works at 50 employees and collapses at 500, where people move in and out weekly.
Manually, this means exporting IAM data and reconciling it by hand across tools. Automation collects access data from your identity providers, triggers scheduled review workflows, and records who approved what and when. See how user access reviews work under automation.
Vendor risk management
Third-party risk is a mandatory audit scope item for most frameworks, and it is where manual programs quietly fall behind. A vendor you assessed 14 months ago may have had a significant breach since then, and you will not know until a customer asks.
Done ad hoc, vendor assessments are infrequent and inconsistent. Automation dispatches questionnaires on a cadence, monitors vendors continuously, and keeps assessments current. Explore vendor risk management in depth.
Reporting
A compliance report pulled from Excel tells you what was true when someone exported it. By the time it lands in the board deck, it is already stale. Automated reporting pulls from live data, so stakeholders see current posture, not last quarter's snapshot, and gaps surface before an auditor finds them.
Remediation task creation and tracking
Reporting surfaces the gap. Remediation closes it. When a control fails, automation opens the corrective workflow, assigns the task, sets a deadline, and tracks it to resolution. A centralized record of changes and activity keeps a clean audit trail for internal and external reviews.
Compliance processes: manual vs. automated
How to get started with compliance automation: A 5-step guide
1. Understand your compliance requirements
Start by identifying the frameworks you need, such as ISO 27001, SOC 2, or PCI DSS. Each carries its own control requirements, documentation standards, and audit protocols. Then list the industry and region-specific regulations that apply. HIPAA is a US federal law for healthcare data; GDPR applies to anyone processing EU residents' data.
The highest-leverage move at this stage is finding where frameworks overlap: most framework pairs share 40% to 50% of their controls, depending on scope, which means a single control or evidence artifact can satisfy multiple requirements. Mapping that overlap between SOC 2, ISO 27001, and GDPR up front prevents duplicated effort as you scale. If you are unsure where to begin, a compliance frameworks primer and a tool to identify your applicable frameworks will narrow the scope quickly.
2. Assess current compliance processes
The most common automation mistake is digitizing a broken process. Before you select a platform, map your existing workflows against three questions:
- Which processes currently depend on one person's memory?
- Where is evidence stored today: email, shared drives, spreadsheets?
- How long did your last audit prep actually take?
Pay particular attention to auditor collaboration and data retrieval, where bottlenecks tend to hide. A structured compliance risk assessment is a useful companion to this step.
3. Define compliance automation goals
Set objectives and attach a measurable metric to each one, so you can judge whether automation is working. Vague goals like "improve compliance" cannot be defended to a CFO; specific ones can.
Set your own goals and metrics against your specific risk and compliance needs.
4. Choose the compliance automation tool
This is where most evaluations go thin. A ranked long list from review sites is a start, but the decision comes down to whether a platform fits your actual stack and scales with your program.
Score each candidate against clear criteria:
Schedule demos with at least 2 or 3 platforms and run a short proof-of-concept against your most-used integrations. If you lead engineering, this is the step you will likely hand to a staff engineer or DevOps lead, so make sure the evaluation checks real integration behavior, not marketing claims.
For a deeper framework, see how to choose GRC software and how the major GRC platforms compare.
5. Implement the automation tool
Stand up a small team that includes internal owners and the vendor's implementation contact. Connect the platform to your HR, cloud, asset, and identity systems so it can pull data for control testing automatically, then configure workflows for the recurring tasks you identified in step 2.
Document the new processes, record what changed, and train both technical and non-technical stakeholders. No platform removes the need for human review. The management assertion on a SOC 2 report is signed by a named individual, not the platform. Someone still decides whether a control is effective and whether a flagged risk is acceptable.
The tool surfaces the information. The human makes the call. This is the human element in compliance that automation supports but never replaces. Once live, track performance against your step 3 metrics and keep looking for new processes worth automating.
Download: compliance automation platform evaluation checklist
The criteria in step 4 above give you a starting framework. For a printable version with scoring weights, download the checklist below.
Benefits of compliance automation for GRC and security teams
Automation is easiest to justify when you can name the benefit to a specific stakeholder. Here is what changes.
Reduced compliance risk and fewer audit surprises
A misconfigured control that surfaces during an audit costs more to fix than one caught in week two. Continuous monitoring detects control drift as it happens, so you fix the problem in week two rather than discovering it in month eleven when the auditor samples the control.
Lower cost of compliance
Evidence collection alone can consume weeks of engineering time each audit cycle. That is before you count the hours pulled into questionnaire responses, access reviews, and prep. There is a breach cost dimension too: the IBM Cost of a Data Breach Report 2024 found that organizations using AI and automation extensively saved an average of $1.88M per breach. (Confirm no 2025 edition supersedes this before publish.) For a structured view of the business case, see ROI from a GRC platform.
Faster audit cycles
Automated evidence collection and an always-on audit trail compress preparation from weeks to days. Instead of assembling a package from scratch, you hand the auditor organized, timestamped artifacts. See how this changes compliance audit preparation.
Continuous compliance, not point-in-time
Automation shifts you from annual scrambles to ongoing monitoring. As noted above, continuous monitoring does not equal continuous certification: ISO 27001 requires annual surveillance audits and triennial recertification, and a SOC 2 Type II report covers a defined observation period. Automation keeps you ready for those checkpoints; it does not remove them. Learn what continuous compliance genuinely means.
Multi-framework efficiency
Because most framework pairs share 40% to 50% of their controls, depending on scope, a single evidence artifact can satisfy requirements across several frameworks when controls are mapped correctly. That is the difference between running SOC 2, ISO 27001, and GDPR as one program instead of three.
Improved stakeholder visibility
The board asks about compliance posture. The auditor asks for current evidence. The security team needs to know which controls are drifting. Right now, each of those questions gets a different answer from a different spreadsheet. Real-time dashboards give all of them one view: the board gets current posture, the auditor gets timestamped artifacts, and the security team sees which controls are drifting without anyone pulling a separate export.
Compliance automation benefits by stakeholder
How AI is changing compliance automation
- From rules-based monitoring to agentic detection
Traditional automation follows rules: if a control fails a check, raise an alert. AI-powered automation goes a step further. It detects evidence gaps before an auditor would, maps policy documents to the controls they support, and can generate configuration fix recommendations for a human to review. Scrut Teammates, an agentic AI layer, is one example of this shift from rule-matching to detection. The point is not that AI replaces the reviewer. It narrows what the reviewer has to look at.
- AI-assisted evidence and questionnaire work
Questionnaire auto-fill is where most teams feel the AI difference first. A security questionnaire that used to take hours of cross-team email can be drafted from a response library and prior submissions, then checked by a human before it goes out. The same applies to evidence: AI can surface which artifacts are missing or stale ahead of an audit, so the gap is closed on your schedule rather than the auditor's. For a wider view, see the role of AI in GRC.
- The human-in-the-loop imperative
AI accelerates the work; it does not own the judgment. A named individual still signs the management assertion, still decides whether a control is effective, and still interprets how a regulation applies to a novel situation. Treat AI output as a strong first draft that a qualified person reviews, not as a finished answer.
Top compliance automation tools to evaluate
Here is a quick comparison, followed by a closer look at three widely evaluated tools. For a broader list, see the best compliance automation software and top compliance management software.
Compliance automation tools: quick comparison
1. Scrut Automation
Scrut is a GRC and compliance automation platform built for cloud-native, growth-stage, and mid-market companies, spanning compliance, risk, and vendor management in one product. It automates evidence collection through 150+ integrations with the tools teams already use, reducing manual evidence-gathering effort by up to 70%.
It supports 70+ frameworks, including SOC 2, ISO 27001, HIPAA, GDPR, and PCI DSS, and its Unified Controls Framework maps risks and artifacts to controls once, so adding a framework only asks for the evidence you do not already have.
A few capabilities set the platform apart. Scrut Teammates, an agentic AI layer, detects evidence gaps before auditors do and maps policy documents to controls. Scrut DAST adds native dynamic application security testing, removing the need for a separate scanning tool.
The Trust Portal shares security documentation on demand. Security questionnaire responses are unlimited and AI-automated. Cloud posture is checked daily against 230+ CIS benchmarks, and the platform ships with 100+ pre-built policy templates.
Pricing is transparent and all-inclusive across Foundation, Growth, and Scale tiers, with no add-on fees for auditors or pen-testers and no extra charge for up to 5,000 users. Custom framework creation is included at no additional cost. See the full set of compliance automation integrations and vendor risk management capabilities.
2. Drata
Drata is a compliance automation platform that positions itself as "The Agentic Trust Management Platform." It supports 50+ frameworks, including SOC 2, ISO 27001, GDPR, HIPAA, ISO 42001, DORA, FedRAMP, and CMMC, with continuous control monitoring and automated evidence collection.
AI Questionnaire Assistance is included across all tiers, and the company launched AI Agent Governance for AI-system compliance in June 2026.
Pricing follows a tiered model: Foundation (1 framework, up to 50 FTEs), Advanced, and Enterprise, with tier features published at drata.com/plans but no prices listed publicly. For teams evaluating Drata as a primary platform, the Audit Hub is the standout. It brings auditors directly into the workflow for sampling and requests rather than managing them over email, which compresses the back-and-forth that typically stretches audit cycles.
If you are weighing options, see our breakdown of Drata alternatives.
3. Vanta
Vanta is a trust management and compliance automation platform founded in 2017 that describes itself as the "#1 Agentic Trust Platform." It supports 35+ frameworks, including SOC 2, ISO 27001, PCI DSS, GDPR, HIPAA, and CCPA, and offers 400+ integrations for evidence collection. The company launched an AI governance product in July 2026.
Vanta states that its platform automates up to 90% of the effort required for security audits; that figure is the company's own positioning rather than an independent benchmark.
For teams already deep in a cloud-native stack, Vanta's 400+ integrations are a genuine strength at the evidence-collection layer. One documented limitation to be aware of during evaluation is encryption-status tracking on Linux machines. As with any platform, confirm which capabilities are included in base tiers versus available as add-ons before you commit.
Conclusion
If you have pulled engineers off a sprint to gather audit screenshots, you already know the cost. Automation closes that loop: evidence collects continuously, monitoring runs in the background, and the audit package assembles itself.
Two things are worth keeping in mind. Automation supports compliance; it does not produce it, and a named person still signs the management assertion. And continuous monitoring keeps you ready for audits, but it does not replace the surveillance audits and recertifications that formal compliance status depends on.
Platforms like Scrut help teams centralize compliance workflows, monitor continuously across frameworks, and keep risk and vendor management in one system with transparent pricing. Book a demo to see how it fits your program.
Compliance automation uses software and AI to replace manual compliance workflows, automating evidence collection, controls testing, risk assessment, and reporting. It helps you demonstrate compliance; it does not make the human judgment calls, such as signing a management assertion, that compliance ultimately requires.
No. Automation handles the workflows and evidence that support compliance, but a named individual still attests to controls, accepts or rejects risks, and interprets how regulations apply. Compliance is a human-attested outcome, not a platform output.
It varies by program, but automating evidence collection alone can reduce manual effort by up to 70%. The larger gains come from shorter audit prep cycles and fewer engineering hours lost to questionnaires and access reviews.
No. Continuous monitoring keeps you aware of control status in real time. Formal compliance status still depends on periodic external checkpoints: ISO 27001 requires annual surveillance audits and triennial recertification, and SOC 2 Type II covers a defined observation period.
Prioritize framework coverage (50+ is a strong baseline), integration depth with your actual stack, continuous monitoring, multi-framework control mapping, built-in risk and vendor management, and transparent, all-inclusive pricing. Run a proof-of-concept against your most-used integrations before deciding.