


- A risk control matrix (RCM) maps identified risks to specific controls, owners, and monitoring evidence in a single structured document.
- It differs from a risk register: a register logs risks; an RCM connects each risk to the control designed to address it.
- A well-maintained RCM surfaces control gaps before auditors or incidents do, but only if the controls are operationalized, not just documented.
- RCMs support SOC 2, ISO 27001, and multi-framework programs by providing a shared audit trail.
- This guide covers what an RCM contains, how to build one, and how to keep it operationally relevant.
You already have a risk register that tells you what could go wrong. You already have controls that are supposed to address those risks. What most teams are missing is the connective tissue between the two: the document that maps each risk to the specific control designed to handle it and shows whether that control is actually working. That is a risk control matrix.
Most SMBs first encounter one in a financial services context, and the more common failure is not too little documentation but too much of it. RCMs that look complete on paper and mean nothing in practice.
This guide draws on GRC practitioner experience to explain what an RCM contains, how to build one, and how to keep it operationally relevant, not just audit-ready.
What is a Risk Control Matrix (RCM)?
A risk control matrix is a structured document that maps each identified risk to the control designed to address it, along with the control's owner, type, operating status, and supporting evidence. In one view, it answers two questions at once: what are we exposed to, and what are we doing about it?
That second question is what separates an RCM from the two things people most often confuse it with. A risk register logs risks, their likelihood, impact, and rating. It tells you what can go wrong. A control framework (SOC 2, ISO 27001, NIST CSF) is a catalog of controls a standard expects you to have. It tells you what good looks like in the abstract.
An RCM sits between them: it takes the risks from your risk register and connects each one to the specific control, chosen from your framework or built for your environment, that treats it, then tracks whether that control is designed, operating, or failing.
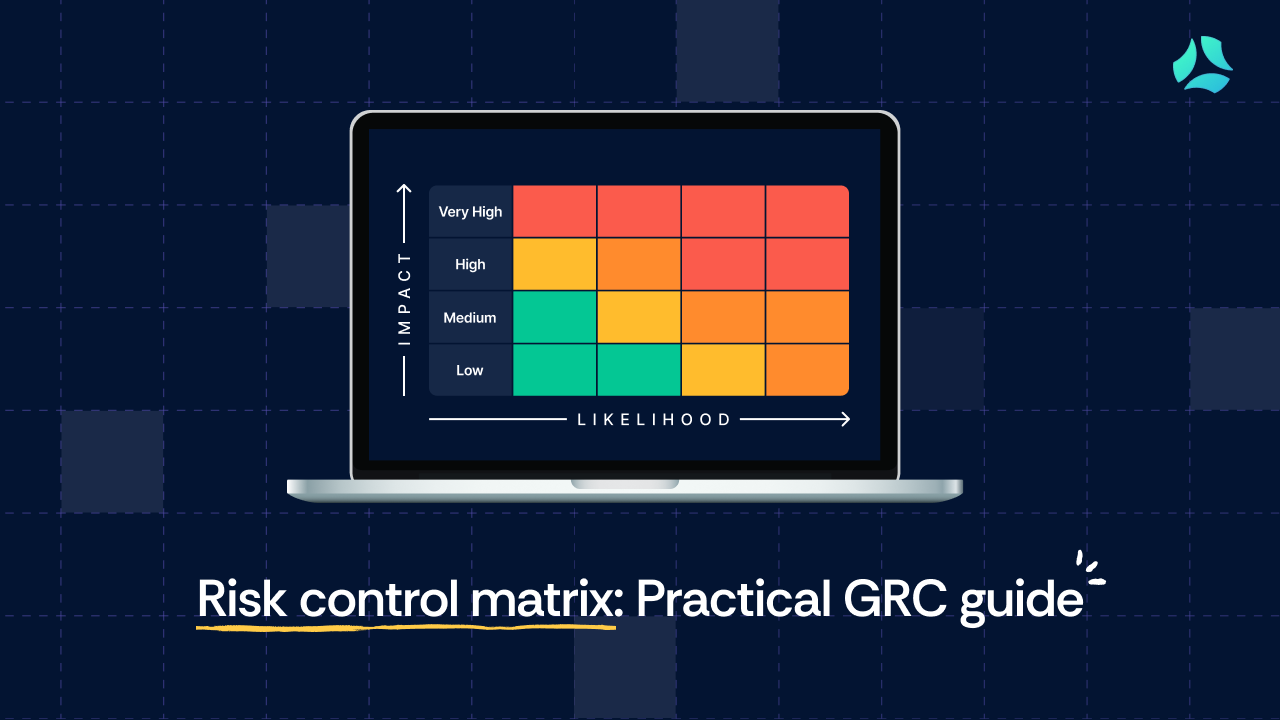
A standard RCM is built from a consistent set of columns. Each risk gets a Risk ID and a plain-language Risk Description, sorted into a Risk Category (strategic, operational, compliance, technology). It carries an Inherent Risk Rating, likelihood times impact scored before any control is applied, and a Residual Risk Rating, the exposure that remains once the control is in place. For a fuller treatment of that distinction, see inherent risk vs. residual risk.
Each risk is then mapped to a Control Name and Control Type (preventative, detective, corrective), assigned a named Control Owner, given a Review Frequency, tagged with an Operating Effectiveness status, and linked to an Evidence Reference.
Here is what a single populated row looks like in practice:
Standardized risk register record: Production database unauthorized access
Example RCM row showing a single technology risk mapped to a preventative control, its owner, operating status, and evidence reference.
That one row does something a risk register alone cannot: it tells you the risk exists, what you are doing about it, who owns it, and whether it is actually working right now.
Risk control matrix vs. risk register: What's the difference?
This is the single most common source of confusion in this space, so it is worth being precise. A risk register and a risk control matrix are not competing documents. The RCM extends the register.
A register answers one question: what could go wrong? It is the source document, the prioritized list of risks that leadership and the board care about. An RCM answers the follow-on question: what are we doing about each of these, and is it working? A register that is not tied to operationalized controls tends to become a compliance artifact nobody reads.
The RCM is what keeps it honest, because it forces every logged risk to point at a real control with a real owner.
Risk Register vs. Risk Control Matrix (RCM) structural comparison
A concrete example makes the relationship obvious. Your risk register has an entry: "Unauthorized access to production database." That is the register's whole job, to name the risk and rate it. The corresponding RCM entry takes that same risk and maps it to the controls that address it: MFA enforcement on production IAM accounts, quarterly access reviews, and an IAM role audit.
Each control gets an owner, a frequency, an operating status, and an evidence link. The register told you the risk existed. The RCM tells you it is being managed and gives you the paper trail to prove it.
If you are still building the source document, start with how to create and maintain a risk register, then layer the control mapping on top. Both sit inside the broader risk management process.
Why the RCM matters for cybersecurity and compliance
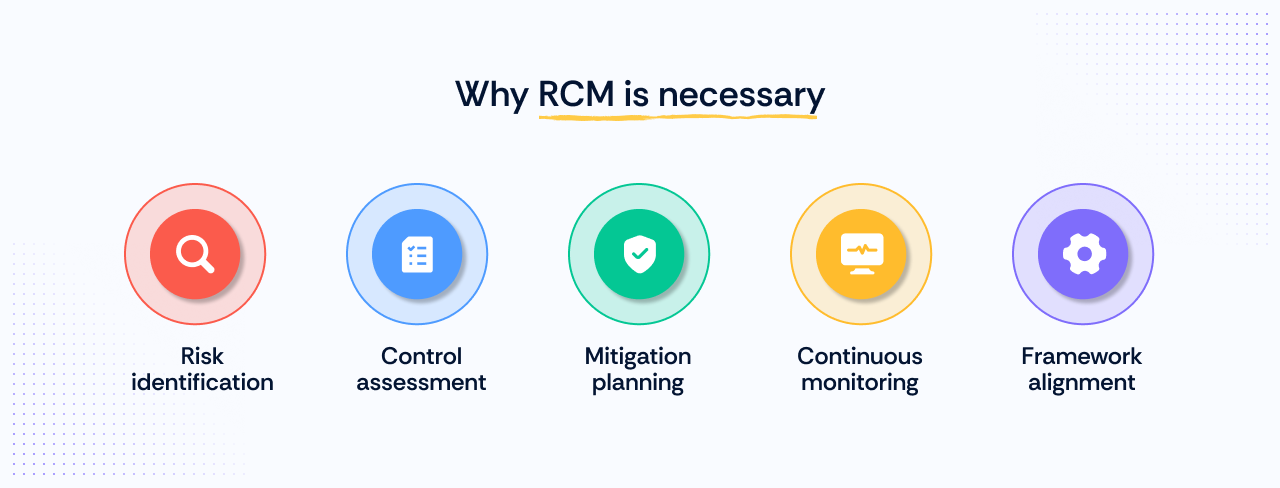
Risk identification. The RCM forces you to name specific cybersecurity risks, unauthorized access, credential compromise, unpatched vulnerabilities, and hold each one next to the control that addresses it. A risk sitting in a register with no mapped control is a gap you can now see. Without the matrix, that gap stays invisible until an incident or an auditor finds it.
Control assessment. By putting risks and controls side by side, the RCM lets you evaluate whether your controls actually cover your exposure. You can see, at a glance, which risks have layered controls, which have a single point of failure, and which have controls that exist on paper but have never been tested against the standard you claim to meet. For grounding on what those controls look like, see the SOC 2 controls list.
Mitigation planning. The RCM turns a flat list of risks into a prioritized remediation plan. Practitioners consistently want high-criticality risks surfaced first and are far less concerned with scoring low-priority items precisely. A business-critical system with an activated failure mode belongs at the top of your remediation queue; a low-impact risk with a working control does not need the same attention. The RCM makes that triage visible, so resources go where the exposure actually is.
Continuous monitoring. This is where most RCMs quietly fail. An RCM's value is determined by how often control effectiveness is actually tested, not how often the document is updated. A matrix that lists a quarterly access review as "operating" when no one has run the review in six months is worse than no matrix at all, because it manufactures false assurance.
For teams without dedicated GRC staff, automated control monitoring is what makes the operating-effectiveness column honest without requiring someone to manually chase evidence before every review cycle. Risk management automation and continuous compliance monitoring can keep status current where integrations exist.
Framework alignment. This is the payoff for anyone running a multi-framework program. An RCM maps each control to the specific framework requirements it satisfies: SOC 2 Trust Services Criteria, ISO 27001 Annex A, NIST CSF functions. One well-designed control frequently satisfies requirements across several frameworks at once.
A concrete example: an MFA enforcement control maps to a SOC 2 logical access criterion, an ISO 27001 Annex A access control, and a NIST CSF Protect function, simultaneously. You document it once; it satisfies three requirements.
That matters because cybersecurity consistently ranks as the top risk in enterprise risk management exercises. Getting the control-to-framework mapping right is not a paperwork exercise. It is where your highest-priority risk domain meets your compliance obligations. For teams pursuing ISO 27001 compliance alongside other standards, the RCM is the shared spine that connects one control to many requirements.
How does an RCM support GRC programs?
The RCM puts risks and controls in the same document as business objectives. That sounds obvious until you have spent an afternoon cross-referencing three spreadsheets to answer a single auditor question. A single shared view is not a luxury. It is what makes the GRC program legible to the people who need to act on it, rather than leaving governance, risk, and compliance functions with fragmented views owned by different teams.
Control effectiveness evaluation. A GRC program lives or dies on whether its controls actually work. The RCM's operating-effectiveness column is the mechanism that surfaces this. When a control owner marks a control as "not operating" or "unknown," that entry becomes a governance decision point.
Someone with authority has to decide: fix it, accept it on the record, or escalate it to leadership. The matrix makes that decision visible; it does not make it for you. Without the matrix, control failures stay buried in the gap between what a policy says and what actually happens.
Risk prioritization. A residual risk rating tells you what you are carrying after controls. It does not tell you whether the risks in your register are the right ones. An RCM built on a register populated with easy-to-define risks will prioritize the wrong things. You optimize for evidence and miss the operational exposures that never appear on a compliance checklist. The RCM's prioritization is only as good as the risks you chose to put in it.
Compliance assurance. The RCM is the shared audit trail. The matrix gives an auditor a single path: requirement to control to evidence, in one hop, without cross-referencing three spreadsheets. This is also where compliance risk and operational risk stop being conflated. The RCM makes the difference between "we can prove we address this in the audit" and "this is actually working" explicit.
Who owns the RCM in different org structures? This is the practical question most guides skip. Risk tends to stay siloed by function: the CISO owns cyber risk, the CFO owns financial risk, and a single unified owner is aspirational more often than it is real. In SMBs and mid-market companies without a CISO, the RCM typically lands with the Head of Engineering, the GRC Manager, or the VP of Engineering, whoever has the broadest visibility into how the systems actually work. In enterprises, it sits inside a formal GRC or internal audit function with dedicated staff.
Either way, the RCM operates within the broader risk management lifecycle: identify, assess, treat, monitor, report. The owner's job is to keep the matrix moving through that loop, not to let it freeze after the first audit. For a deeper look at breaking down silos, see integrated risk management.
What are the key components of a risk control matrix?
Every column in an RCM earns its place. Skip one and you will find out why during the audit. Here is what each standard component captures and why it matters.
1. Risk ID. In an audit, the auditor will ask you to trace TECH-007 from the risk register to the remediation ticket to the evidence package. Without a consistent ID on every entry, that trace takes an hour. With one, it takes a minute. That is the entire job of the Risk ID.
2. Risk category. Strategic, operational, compliance, or technology. The category is how different owners find their risks without reading the whole matrix. A CISO scanning for technology risks should not have to read through strategic and operational entries to find them.
3. Risk description. Plain language is the requirement here. Not "database risk," but "unauthorized access to the production database via compromised credentials." That specificity is what makes the downstream control mapping meaningful. Vague descriptions produce vague controls.
4. Inherent risk rating. Likelihood times impact, scored before any control is considered. This is the ceiling, the raw exposure you are working down from. If your rating mentions a firewall or MFA, you are describing residual risk, not inherent risk.
5. Control name/Control ID. The name and identifier of the control mapped to the risk. One risk can map to several controls, and one control can address several risks, so consistent naming keeps those many-to-many relationships traceable.
6. Control type. Preventative, detective, or corrective. Preventative controls stop the bad thing from happening; detective controls identify when it has happened; corrective controls fix it afterward. A mature matrix layers all three across its highest-priority risks. For more, see control types.
7. Control owner. A named individual accountable for the control. Not "the DevOps team," a person. This is where a lot of matrices quietly fail.
8. Control frequency. Continuous, quarterly, or annual. Worth reading carefully: this column is also the first place an auditor looks when they want to know whether your quarterly access review actually ran quarterly, or whether "quarterly" was aspirational.
9. Operating effectiveness status. Designed, operating, not operating, or unknown. "Designed" means the control exists on paper but has not been verified in practice. "Operating" means it has been tested and evidence exists.
This is the honesty column, and the rule is unambiguous: if a control has not been tested in the review period, its status is "unknown," not "operating." Marking an untested control as "operating" is how an RCM manufactures false assurance.
10. Residual risk rating. The exposure that remains after the control is applied. This is the number leadership actually cares about, because it tells them what the organization is carrying right now. See the residual risk guide for the full mechanism.
11. Evidence reference. A link to the audit evidence for the control: a compliance report, a screenshot, a completion record. This is what turns a claim into a receipt. For the categories auditors accept, see evidence collection.
12. Last/Next review date. When the entry was last reviewed and when it is due. This is what keeps the matrix from silently going stale.
Key columns of a complete Risk Control Matrix (RCM)
How to build a risk control matrix for your organization
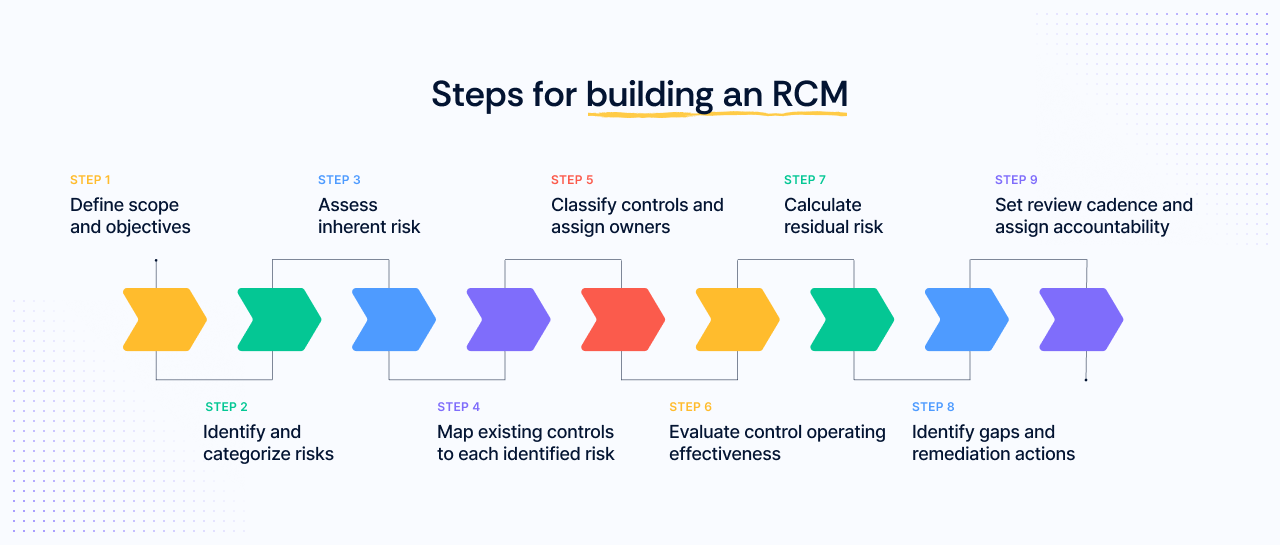
For companies going through SOC 2 or ISO 27001 for the first time, the RCM is often built alongside the risk assessment, not after it. Here is the process.
Step 1: Define scope and objectives. Before you populate a single row, decide what is in scope. Which systems, data, and processes are you covering? What framework requirements are you building toward? What is your organization's risk appetite? These decisions shape every row that follows. Most early-stage teams start with a template and adapt it to their environment rather than building from a blank sheet.
Step 2: Identify and categorize risks. Pull risks from your risk register and sort them by domain: technology, operational, compliance, strategic. Getting the right people in the room is half of a good risk assessment. One person rarely understands how the whole company works, so pull in someone who knows the technology, someone who knows operations, someone who knows the back office. And be honest about what belongs here: the register should reflect actual business risk, not just the items that are easy to define.
Step 3: Assess inherent risk. For each risk, score likelihood times impact before any control enters the picture. This is the ceiling, the raw exposure you are working down from. Be honest: inherent risk assumes zero controls exist. If your rating mentions a firewall, you are already describing residual risk.
Step 4: Map existing controls to each identified risk. Go through your risks and attach the control or controls that address each one. A risk like "unauthorized access to production database" might map to MFA enforcement, quarterly access reviews, and an IAM role audit: three controls, each with a different type and owner. Any risk with no control mapped is either a gap to remediate or a risk you are implicitly accepting, and both need to be explicit.
Step 5: Classify controls and assign owners. Tag each control as preventative, detective, or corrective, and assign a named individual as owner. This is where a lot of matrices quietly fail: owners are listed as teams rather than individuals. A control without a real owner is a control nobody runs.
Step 6: Evaluate control operating effectiveness. For each control, record whether it is merely designed or actually operating with evidence to prove it. The test is simple: can you point to a timestamped artifact (an access review completion record, an automated policy compliance report, a configuration screenshot) that shows the control ran during the review period? Documentation is not implementation. A control that looks perfect on paper but has never run is a control that will fail your audit and, worse, will not protect you.
Step 7: Calculate residual risk. After accounting for the control, score the exposure that remains. If your inherent rating was High and your MFA enforcement control is operating, the residual rating might drop to Medium, still above tolerance for some organizations, which means the work is not done. This is the number that tells you whether your treatment is sufficient or whether you need an additional control, a compensating control, or a formal risk acceptance decision.
Step 8: Identify gaps and remediation actions. Any risk where residual exposure exceeds your tolerance needs a remediation plan with an owner and a date. This is the output that turns the RCM from a static document into a work queue.
Step 9: Set review cadence and assign accountability. Decide how often each entry gets revisited and who is responsible for revisiting it. Without this, the matrix goes stale the day after the audit ends.
For the assessment that feeds this process, see the risk assessment process, and for scoring guidance, risk scoring. If you are cross-referencing the engineering discipline that shares the RCM acronym, that is FMEA analysis, a different method entirely.
Does a well-maintained RCM actually catch gaps before auditors do?
Yes, but only if the controls are operationalized, not just documented. This is the honest answer, and it is worth being clear about.
The distinction that matters is between documentation and implementation. People are far better at making documents than at implementing processes. An RCM that lists a quarterly access review as "operating" when no one has actually run the review in six months is worse than having no RCM at all, because it creates false assurance: a green status that stops people from asking questions.
A simpler, well-operationalized RCM that is genuinely understood beats a complex, better-diagrammed one that is poorly implemented, every time.
So the real detection mechanism is not the matrix itself. It is behavior. An RCM catches gaps when control owners actively update effectiveness status based on evidence, and when someone reviews the residual risk column at a defined cadence.
The question to ask is blunt: how many people in the company are responsible for implementing a given control, and how much time are they actually spending running and monitoring it? If the honest answer is "nobody really" or "they do not know they own it," the matrix will not catch anything.
For companies without a dedicated GRC team, the RCM is often maintained reactively, right before an audit. That is the reality for most SMBs, and it is a reasonable starting point. A quarterly check-in plus an annual comprehensive review is a workable cadence. Consistency matters more than frequency.
The practical recommendation: tie RCM review to an existing operational cadence, a quarterly business review or a monthly security review, rather than treating it as a standalone annual exercise. Reviews that ride along with meetings you already hold get done. Standalone reviews get skipped. For the monitoring layer that supports this, see compliance monitoring.
Best practices for documenting and maintaining RCMs
1. Set a minimum review cadence tied to business change, not the calendar. Frequency matters less than whether your business has actually changed. Review the RCM when something meaningful shifts: a new product, a new vendor, a new regulation, a new piece of infrastructure, plus a mandatory annual comprehensive review. For most SMBs, a quarterly check-in is the right rhythm. Updating a matrix every day when nothing has changed is theater; an out-of-cycle update when the business fundamentally changes is what actually matters.
2. Keep the RCM to a manageable size. A matrix with 200-plus entries that no one reads is less valuable than a focused one covering the 20 to 30 most impactful risks. Even large public companies rarely need 200 entries; kept strategic, a mature register often stays under a hundred. The RCM should only be as big as you are willing to care about it. If everything is a strategic risk, nothing is.
3. Assign named control owners, not team names. "The DevOps team" is not an owner. A named individual with accountability is. When ownership is diffuse, the musical-chairs problem sets in: everyone assumes someone else is running the control, and no one does. Force a name into every owner field.
4. Separate the RCM from the vulnerability management backlog. The RCM is not a security Jira board. Risk registers get polluted when people use them as an escalation path. "If I get this vulnerability onto the risk register, people will finally pay attention." That is how random findings end up inflating the matrix until it becomes meaningless.
Operational vulnerability tracking belongs in your issue-management system. The RCM is for strategic risks that went through the actual assessment process. Keep the two separate, and see risk register maintenance for how to keep the source clean.
5. Update effectiveness status based on evidence, not assumption. If a control has not been tested in the review period, the status is "unknown." Not "operating." Acknowledged gaps are manageable; false assurance stops everyone from looking. For the broader toolkit, see risk management techniques.
Risk acceptance and the RCM: What happens when you can't remediate?
Not every risk gets remediated, and an RCM that treats all risks as remediable is giving you a false picture of how risk management actually works. The four treatment options, accept, mitigate, transfer, or avoid, all belong in the matrix. Most teams handle mitigation reasonably well. Acceptance is where things go wrong.
Accepted risk materializes all the time. A company decides not to add friction to user signups, then deals with account takeovers. A finance team keeps an out-of-date, unencryptable database because migrating it costs more than the exposure seems worth. These are legitimate decisions: remediation cost genuinely can exceed expected impact. The RCM's job is not to eliminate every risk. It is to make the acceptance decision explicit and owned.
A documented risk acceptance entry in an RCM has structure: a named decision-maker (not "the business" as an abstraction, an actual person who signed off), a justification for why acceptance is the right call, any compensating controls in place to reduce the impact, a review date, and an escalation threshold that says when this decision needs to be revisited. Crucially, accepted risks do not disappear from the matrix. They stay in it, flagged as accepted, with an owner and a scheduled review, because a risk you accepted last year may not be a risk you would accept today.
For the strategic boundaries that govern these decisions, see risk tolerance vs. risk appetite. For the fuller menu of responses, see risk mitigation strategies and risk avoidance vs. risk reduction.
How Scrut supports risk control matrix management
Building an RCM by hand in spreadsheets works until it does not: until someone puts in incorrect data, until there is no version control, until no one is sure which copy is current.
Scrut's risk management platform is built to make the RCM operationally real rather than a static document. Risks identified in the risk register feed directly into the matrix, so the source and the control mapping stay connected. Continuous control monitoring updates operating-effectiveness status automatically where integrations exist, which is the difference between a matrix that reflects reality and one that reflects last quarter's assumptions.
Evidence links attach audit artifacts directly to control entries, so the receipt lives with the control. And multi-framework mapping means a single control in the RCM can satisfy SOC 2 and ISO 27001 requirements at once, rather than forcing duplicate work per framework. For the broader picture, see how Scrut helps with risk management and its approach to compliance automation.
Conclusion
An RCM is not just documentation. It is the operational link between the risks you have identified and the controls that address them, and its entire value depends on whether those controls are actually running, not just written down. A well-maintained matrix surfaces gaps before auditors or incidents do; a poorly maintained one manufactures false confidence.
If you are starting from scratch, keep it simple: take your top 10 risks, map one control per risk, assign a named owner, and set a review date.
That is a functional RCM. Everything else is refinement.
Ready to build one that stays current? Book a demo to see how Scrut connects your register to your controls, or start with our guide on how to create a risk register and choosing the right risk management software.
A risk control matrix is a structured document that maps each identified risk to the specific control designed to address it, along with the control's owner, type, operating status, and supporting evidence. It differs from a risk register: a register logs what could go wrong, while an RCM connects each risk to the control treating it and shows whether that control is actually working. In practice, it functions as the shared audit trail between your risks and your compliance obligations.
The core components are Risk ID, Risk Category, Risk Description, Inherent Risk Rating, Control Name, Control Type (preventative, detective, or corrective), Control Owner, Control Frequency, Operating Effectiveness Status, Residual Risk Rating, Evidence Reference, and Last/Next Review Date. Together they let you trace a risk from identification through the control that treats it to the evidence that proves the control runs. See the component table above for which are required by SOC 2 and ISO 27001.
A risk register answers "what could go wrong?" It is a prioritized list of risks with their likelihood, impact, and rating. A risk control matrix answers "what are we doing about it, and is it working?" It extends the register by mapping each risk to a control, an owner, an operating status, and evidence. The register is the source document; the RCM is the control layer built on top of it. See the comparison table above for a full breakdown.
At minimum, conduct a comprehensive top-to-bottom review annually. Add quarterly check-ins for most SMBs, and trigger an immediate out-of-cycle review whenever the business changes meaningfully: a new system, a new vendor, a new regulation, or a new product line. Frequency matters less than whether your business has actually changed since the last review. Updating a static matrix daily accomplishes nothing, while missing a review after a major change creates real exposure.
In practice, it is a table where each row is a single risk mapped to its treating control. A typical row reads: Risk ID TECH-007, "Unauthorized access to production database via compromised credentials," rated High inherent, mapped to an MFA enforcement control (preventative, owned by the VP of Engineering, monitored continuously), currently Operating, with Medium residual risk and a linked AWS IAM compliance report as evidence. See the example row table above.