


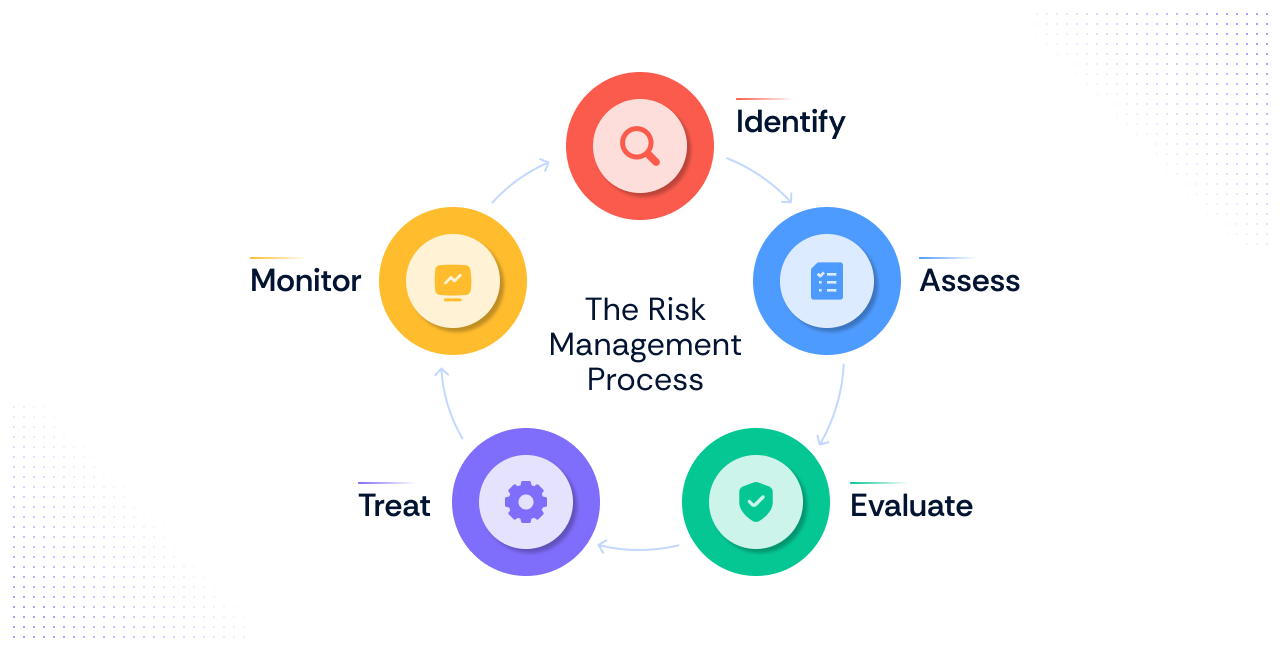
- The risk management process is a structured cycle: identify risks, assess likelihood and impact, evaluate against appetite, treat, and monitor continuously.
- Most frameworks (ISO 31000, NIST SP 800-30) share the same five-step logic regardless of industry.
- The first step is always risk identification. Without it, every downstream decision is uninformed.
- A risk register is the operational output. It only stays useful when ownership and review cadence are defined.
- Residual risk, what remains after controls, must be measured against your stated risk tolerance, not left as an assumption
The risk management process is a structured cycle for identifying, assessing, evaluating, treating, and monitoring the risks that could stop your organization from meeting its objectives.
Most frameworks organize it into five steps: identify, assess, evaluate, treat, and monitor. Its purpose is not to eliminate risk, which is impossible, but to give leadership a defensible way to decide where to spend limited time and money.
This guide is written for GRC managers, security managers, CTOs, VPs of engineering, and founders who own risk without a dedicated team. Done well, the process turns scattered worry into a program you can actually run and defend.
What is the risk management process?
The risk management process is the operational cycle an organization runs to identify what could go wrong, decide how much of that exposure it is willing to carry, and put controls in place to close the gap. It produces decisions, not just lists of scary scenarios.
Within a broader GRC program, it is the muscle that connects governance (what leadership decided to enforce) to compliance (the proof that you enforced it). Get it right, and every other security investment becomes defensible rather than a guess.
As Scrut’s CISO Nicholas Muy explains, “A risk assessment gives you a defensible methodology to identify and prioritize what you can actually do in a world of scarcity. You don't have unlimited resources, so it tells you what to focus on. Without one, you're not managing risk, you're guessing. Maybe an informed guess, but still a guess.”
That framing matters because it reframes the entire exercise: you are not doing this to pass an audit, you are doing it so you know what to protect first.
As Wendy Nather, Senior Research Initiatives Director at 1Password, put it, “Compliance is a method for managing risk for a very well-understood, well-scoped area across a population.” The risk management process is the wider net that catches everything compliance does not scope.
Three terms get used interchangeably and shouldn't be. The risk management process is the operational cycle. The risk management plan is the strategic document that describes how you will run that cycle. The risk register is the artifact the process produces, a living record of the risks you have identified and the decisions you have made about them. Confusing the plan with the register is one of the most common early-stage errors.
The process is not tied to any single framework. Whether you follow ISO 31000 or NIST SP 800-30, both describe the same underlying logic in five canonical steps:
1. Risk identification
2. Risk assessment
3. Risk evaluation
4. Risk treatment
5. Risk monitoring and review
For a broader grounding, see what is risk management and how it relates to compliance risk management. If you are operationalizing this, a risk management platform is where these steps stop living in spreadsheets.
The five-step risk management process
Every recognized framework maps to the same five steps. Here is what each one actually involves.
1. Risk identification. This is always the first step, and everything downstream depends on it. It involves surfacing the risks that could realistically affect your business, using workshops, historical incident data, and a risk register as the capture mechanism.
Critically, it requires cross-functional input. As Vignesh Kumar, Senior Manager, Security and Privacy at Microsoft, noted in our webinar, “Without speaking to business leaders and understanding their pulse, we might miss out on risks that are critical to the company."
A register populated only by the security team will miss operational and strategic exposure that lives in other functions. The quality of this step sets the ceiling for the whole process.
2. Risk assessment. Here you determine likelihood and impact for each identified risk, distinguishing inherent risk (exposure before controls) from residual risk (what remains after).
Assessment can be qualitative (heat maps, likelihood-impact matrices) or quantitative (financial loss estimates), and the right choice depends on your program's maturity.
3. Risk evaluation. This step compares each assessed risk against your risk appetite and tolerance. The output is a decision: monitor, escalate, or treat.
Without this step, every assessed risk flows directly to treatment, which wastes resources on risks the organization has already decided to carry.
4. Risk treatment. For risks outside tolerance, you choose a risk treatment strategy: mitigate, accept, transfer, or avoid. Treatment is where controls and countermeasures get implemented and documented.
Most programs default to mitigate, which means they over-invest in controls for risks they could transfer or accept at a lower cost.
5. Risk monitoring and review. The fifth step is continuous risk monitoring. Risk is not static, so you track key risk indicators, run a defined review cadence, and update the register when the business changes materially.
Monitoring is what separates a living risk program from an annual audit artifact. Without it, the register reflects the business as it was, not as it is.
Step 1: Risk identification, techniques, and common gaps
Identification is the foundation. Miss a risk here, and no amount of downstream rigor recovers it.
Common risk categories to identify:
- Unknown and emerging threats. New attack techniques evolve faster than you can characterize them, and emerging technologies like AI, IoT, and cloud services introduce exposure whose full impact isn't yet predictable. Both share the same underlying challenge: you are managing risk you cannot fully specify in advance.
- Regulatory changes. Shifting laws and compliance requirements create new obligations you must adapt to, sometimes on a fixed deadline.
- Human factor. Employees, contractors, and insiders introduce risk through error, negligence, or malicious action.
- Interdependencies. Interconnected systems mean a disruption in one area cascades into others.
- Third-party risk. Vendors and service providers extend your attack surface. Their security practices become your exposure.
The three core identification techniques
No single method surfaces every risk on its own, so most mature programs lean on three complementary techniques to build a complete picture.
Brainstorming and workshops. Bring the right people into the room. As Nicholas Muy emphasized, understanding how a 150 to 200-person company works across every function usually exceeds what any single person knows, so you need someone who understands the technology, someone who understands operations, and someone who understands the back office.
Run these sessions cross-functionally, at least annually, and treat the output as a working list of real weaknesses tied to how your business actually operates, not a list of softball risks everyone already knows about.
Historical data analysis. Review past incidents, near-misses, and industry breach reports to surface recurring patterns. This is where you learn from what has already gone wrong, both inside your company and across peers in your sector. The output is a set of risk themes grounded in evidence rather than speculation.
Risk registers and assessment tools. A risk register is the central repository that captures each risk, its likelihood and impact, its owner, and its treatment. Assessment tools layer a consistent scoring method on top. Together, they ensure nothing gets lost and everything gets prioritized on the same scale. Learn how to create a risk register and the discipline of maintaining your risk register.
Using the register as an identification tool, and what makes it actually useful
A register is only as good as the thinking behind it. The most common failure is populating it with what is easy to define rather than what matters most.
This is why a register run in spreadsheets tends to decay. Version control, permissions, and a single source of truth are what keep a register from becoming an audit artifact nobody reads. For the assessment side of identification, see IT risk assessment.
Step 2: Risk assessment, qualitative vs. quantitative methods
You have a list of risks. Now you need to know which ones are actually dangerous. Risk assessment assigns likelihood and impact to each identified risk so you can compare them on the same scale.
Two primary approaches exist:
Qualitative assessment uses heat maps, likelihood-impact matrices, and expert judgment. It is the realistic starting point for most organizations. For SMBs and early-stage programs, this is where you begin.
Quantitative assessment puts financial figures on risk using methods like FAIR, Monte Carlo simulation, or annualized loss expectancy. It is high effort and best reserved for mature programs.
Khush Kashyap, Senior Director of GRC at Vanta, who spent two years selling quantitative risk models to large tech and financial services companies, is candid that the same question dogs it now as then: “how do we know it's accurate?”
And Nicholas Muy is direct about the trap for smaller companies: quantitative analysis for a 50 to 200-person company can work, but only if the person doing it has the conviction and experience to make the judgment calls. Attempt it before you have that, and you bite off more than you can chew.
The deciding question is simple. As Muy puts it, is it going to change the decisions you make? If running the numbers won't change what you believe your biggest risks are or what you do about them, the effort is wasted.
Qualitative vs. quantitative risk assessment methodologies
Inherent risk vs. residual risk
Inherent risk vs. residual risk is the distinction that makes assessment meaningful. Inherent risk is the raw exposure assuming no controls exist. Residual risk is what remains after your controls are applied. If a ransomware scenario would be critical with no defenses but drops to medium once you account for backups, EDR, and segmentation, that medium rating is your residual risk.
The trap is assessing inherent risk once and never re-measuring residual risk when a control lapses.
A note on risk scoring
Organizations assign numerical risk scores to rank exposure, typically by multiplying likelihood and impact. The limitation is that a precise-looking number can mask vague underlying assumptions.
Scoring is useful for triage, but it is a starting point for judgment, not a replacement for it. For deeper method comparisons, see quantitative risk assessment and risk calculation methods.
Step 3: Risk evaluation, appetite, tolerance, and acceptance
Once you have a score for each risk, the next question is whether it falls within the bounds your organization has agreed to accept. Evaluation is where an assessed risk becomes an actionable one: not by treating it yet, but by comparing it against your stated risk appetite and deciding whether it requires escalation.
What is risk appetite?
Risk appetite is a strategic declaration of how much risk leadership is willing to accept in pursuit of the organization's objectives. It is set by the board and executive team, reviewed at least annually, and tied to specific categories. "We are willing to accept moderate operational risk but will not accept high reputational or regulatory risk" is an appetite statement with real teeth. Boilerplate like "we have a low risk appetite" is decoration.
What is risk tolerance?
Risk tolerance is the operational threshold that translates appetite into action. It defines the point at which residual risk requires escalation or remediation. "Any residual risk scored above 12 must be escalated to the CISO within five business days" is a tolerance statement. Appetite is the strategy; tolerance is the trigger mechanism that makes it enforceable.
The table below maps all four concepts side by side. The failure mode in most programs is conflating any two of them: treating residual risk as inherent risk, or writing an appetite statement that has no tolerance threshold to enforce it. The table shows where each concept sits, who owns it, and what breaks when it is missing.
Core risk parameters: Governance alignment and lifecycle properties
How they interact in practice
Appetite is set at the top. Tolerance operationalizes it. When a risk is evaluated, you check its residual score against tolerance. If it sits within bounds, you monitor it. If it exceeds tolerance, it escalates. This is the mechanism that keeps risk appetite and tolerance from being words on a policy page.
What happens when residual risk exceeds tolerance
Sometimes controls don't bring residual risk below your threshold, and more controls aren't affordable. In practice, you prioritize. You use company context and experience to decide which exposure is most likely to hurt you first, and you spend there. This is also where formal risk acceptance enters.
As Nicholas Muy notes, risk registers exist largely because so many things cannot be practically eliminated or avoided. Acceptance is not surrender. It is a documented decision that the benefit of an activity outweighs the cost of eliminating its risk.
Gary Hunter, Executive Director and Deputy Information Security Officer, The Walt Disney Company, frames the board-level reality:
The discipline is communicating the accepted risk in literal, practical terms to everyone it affects, so the decision is made with eyes open. See managing residual risk and risk avoidance vs. risk reduction.
Step 4: Risk treatment, controls, mitigation, transfer, and avoidance
Once a risk is evaluated, you choose how to treat it. There are four options, and the discipline is giving each genuine consideration rather than defaulting to "mitigate."
Mitigate. Implement controls to reduce the likelihood or impact of the risk. This is the most common path and covers the majority of day-to-day security work. See risk mitigation strategies.
Accept. Acceptance is a deliberate choice, not a gap. It should come with compensating controls, a named owner, and a documented rationale: the benefit of the activity outweighs the cost of eliminating the risk.
Transfer. Shift the financial consequence to a third party through cyber insurance, contractual clauses, or vendor agreements. Transfer does not remove the risk; it reallocates who absorbs the loss.
Avoid. Eliminate the activity that creates the risk entirely. This is the cleanest treatment when the activity isn't essential, and the least available when it is core to the business.
Preventive, detective, and corrective controls
Treatment gets implemented through controls, which fall into three functional types of security controls. Preventive controls stop a bad thing from happening, like IAM policies enforcing least privilege.
Detective controls identify when something has happened, like logging paired with alerting. Corrective controls fix the situation afterward, like an automated credential revocation or an incident runbook. Auditors test all three, and a mature program layers them.
When a risk control matrix stops being useful
A risk control matrix maps controls to risks, but documentation is not implementation.
Gary Hunter makes the same point from the prioritization angle: the business will only remediate so many findings with the resources it has, so the job is making sure they fix the right things first. The efficacy of an RCM breaks down when effort goes into diagramming rather than operationalizing. If you want to reduce that documentation burden, look at how to automate risk management.
Step 5: Risk monitoring and review
The fifth step is monitoring and review. It is what makes the process continuous rather than an annual snapshot. Identification happens at assessment time; monitoring never stops.
It relies on three things. Key risk indicators (KRIs) are leading metrics that signal a risk is changing before it breaches tolerance. A spike in failed access attempts, or a new critical vendor with no completed assessment, are typical examples.
A defined review cadence sets the rhythm for when the register gets examined. Clear triggers for out-of-cycle updates ensure that meaningful business change prompts an immediate revisit rather than waiting for the next scheduled review.
How often should you review your risk register?
For an SMB, cadence matters less than relevance, but a working rule holds. As Nicholas Muy frames it, this is a question you should ask roughly once a quarter: has enough changed in the business this quarter to warrant revisiting the register? At minimum, run one comprehensive top-to-bottom review each year. The register is a byproduct of a regular risk assessment cadence, not a document you build once and forget.
The trigger for an out-of-cycle update is meaningful business change. If today you are a B2B business and tomorrow you become B2C, so many fundamentals shift that a full revisit is warranted.
Vignesh Kumar described how mature teams operationalize this: continuous quarterly check-ins with leaders, and immediate reviews when a breach hits your industry, asking directly whether you are prepared to handle something similar.
Risk monitoring in a continuous compliance environment
Manual monitoring doesn't scale as your surface area grows. This is where automating risk monitoring earns its place. As Akil Murali, SVP, Product at Scrut, explained, the goal is not to score every risk exhaustively but to surface what matters most so a human can still make the judgment call.
Automation that surfaces critical signals, the high-confidence risk items that should never slip through, genuinely reduces toil. In a continuous compliance model, Scrut's risk management platform keeps the register live against changes in your environment rather than waiting for the next audit cycle.
Developing a risk management plan
Most teams confuse the risk management plan with the risk register. They are not the same thing. The plan is the strategic document that governs how you run the process; the register is the operational record that the process produces.
The plan is the blueprint. It defines how your organization will identify, assess, treat, and monitor risk, and who is accountable at each stage. A useful risk management plan includes, at minimum:
- Scope, what the plan covers and what it excludes
- Risk appetite statement, tied to specific categories and signed by named leaders
- Roles and responsibilities, so accountability is explicit
- Assessment methodology, qualitative or quantitative, applied consistently
- Treatment options, the sanctioned ways to mitigate, accept, transfer, or avoid
- Review cadence, how often the register and plan get revisited
- Escalation thresholds, the tolerance triggers that force a decision
Having a plan and operationalizing it are different things. A plan that lives in a shared drive and never touches day-to-day decisions is decoration. For how the plan fits a broader posture, see risk management strategy.
Building a risk-aware culture: The human side of risk management
Most risk programs fail on the human side, not the technical one. Jason Leuenberger, GRC & Cybersecurity Strategy Consultant, names the pattern:
Why culture determines whether your process works
You can have a pristine methodology and still get nowhere if the organization treats risk assessment as overhead. For most SMBs, no one owns the integrated view of risk, because the person doing IT risk management is often doing it part-time on top of another job. Culture is what fills that gap, or fails to.
Weigh-in before buy-in
Leuenberger draws a distinction that matters for anyone trying to drive change across functions. "There's a difference between weigh-in and buy-in. Weigh-in always has to happen before buy-in. If we're not taking the time to ask questions and allow the other side an opportunity to weigh in, they feel like they don't have a say in the direction."
Demanding buy-in without letting HR, engineering, and product teams weigh in first produces defensiveness, not participation. See our blog on integrated risk management.
Avoiding the crunchy trap
When process obsession replaces actual risk reduction, you have gone too crunchy. The signal is a team fixated on frameworks and documentation while real exposure goes unaddressed.
Building a genuine security culture means asking questions, listening, and treating risk management as a helping function rather than a control function throwing requirements over a fence.
Skills that make the risk management process work
The skills that matter for GRC are not generic. Here are the five that separate a functioning program from a paper one.
Risk communication. This is the hardest and most important skill. Muy is blunt about it: What still requires human judgment is all the communication, and if your communication skills are poor, stakeholders will not make good decisions, because a lot of risk management is decision support. In practice, this means translating a technical risk into the business impact a non-technical board or CTO can act on.
Critical thinking for prioritization. Most assessments end with a pile of high-impact, medium-likelihood risks and no obvious ranking. The skill is making defensible tradeoffs. In practice, this means being able to say: of these six high-scored risks, the one most likely to materialize first is the authentication gap, because we're actively expanding our customer base and credential stuffing is the attack pattern we see most in our sector.
That judgment, grounded in company context rather than just the score, is what separates a useful prioritization from a ranked list nobody acts on.
Cross-functional collaboration. Risk lives across every function, so the ability to pull the right people into the room and get honest input is foundational. Gary Hunter's own career pivot into security came because a CISO needed someone who could translate concepts the business could understand. In practice, this looks like running a workshop where engineering, ops, and finance each surface exposure the security team would never have seen alone.
Risk quantification literacy. You don't need to run Monte Carlo simulations, but you do need to understand quantification well enough to know when it helps and when it misleads. Khush Kashyap's insight is the practical anchor here: the most important risks are often not the ones quantified in dollar terms, but the ones around eroding customer trust or a compliance gate that locks you out of a market. In practice, this means knowing which risks deserve a number and which deserve a narrative.
Continuous learning. The threat landscape and regulatory environment shift constantly. In practice, this looks like adjusting your IT risk management framework as new regulations, technologies, and attack patterns emerge, rather than running last year's playbook. Grounding in recognized IT risk management frameworks keeps that learning structured.
Risk management frameworks: ISO 31000 and NIST SP 800-30
Frameworks give the process a recognized structure. Two dominate, and they map cleanly to the five steps described above.
ISO 31000 is an international standard published by ISO that provides principles, a framework, and a process for managing risk across an entire enterprise. It is principles-based rather than prescriptive, which means it tells you what good risk management looks like and leaves the implementation to you.
Its strength is breadth: it applies to any industry and any risk type, which makes it a natural anchor for organizations running multiple frameworks or operating internationally. It does not produce a certificate; it's guidance you implement, not a credential you earn. The practical value is a consistent, defensible cycle of identification, assessment, treatment, and monitoring that leadership can stand behind.
NIST SP 800-30 is a special publication from the U.S. National Institute of Standards and Technology focused specifically on conducting risk assessments for information systems. It is more granular on the assessment mechanics than ISO 31000, walking through asset identification, threat and vulnerability analysis, and likelihood and impact determination.
Originally written for federal information systems, it is now widely used across the broader IT ecosystem. Its practical output is a structured risk assessment report that gives you a clear, evidence-based view of your exposure. For organizations already in the NIST ecosystem, NIST CSF 2.0 is a complementary framework worth pairing with it.
Muy's practical reminder cuts across both: whether you are running the NIST risk management framework from 800-30 or the ISO series, most of it comes down to getting the right level of information and understanding, and because one person rarely holds all of it, you need the right folks in the room.
Risk assessment framework standards: ISO 31000 vs. NIST SP 800-30
How to choose the right framework
Three factors decide it. First, industry and regulatory environment: U.S. federal contractors and NIST-aligned organizations lean toward 800-30, while multinationals and multi-framework programs favor ISO 31000.
Second, size and maturity: 800-30 gives more assessment structure for teams that want a detailed method, while ISO 31000's principles suit organizations building a governance layer across many risk types.
Third, existing ecosystem: if you already run NIST CSF 2.0 or plan to, staying in the NIST family reduces friction. For implementation mechanics, see how to apply the RMF and how frameworks fit within broader compliance frameworks.
If you're ready to move from spreadsheets and annual snapshots to a risk register that stays live against your actual environment, book a demo with Scrut to see how it fits into your existing risk management process.
Risk identification is always the first step. It involves surfacing the risks that could realistically affect your business through workshops, historical data, and a risk register. Every downstream decision depends on it, because a risk you never identify cannot be assessed, evaluated, or treated.
There are five canonical steps: identify, assess, evaluate, treat, and monitor. Some frameworks describe them with slightly different labels, but the underlying logic is consistent across ISO 31000, NIST SP 800-30, and every recognized model.
The fifth step is risk monitoring and review. Unlike identification, which happens at a point in time, monitoring is continuous. It uses key risk indicators, a defined review cadence, and triggers for out-of-cycle updates to keep the risk register relevant as the business changes.
A risk register is the operational artifact the risk management process produces. It records each identified risk, its likelihood and impact, its owner, and the treatment decision made about it. It stays useful only when ownership is assigned and a review cadence is enforced; otherwise it decays into an audit artifact nobody reads.
The risk management process is the operational cycle you run: identify, assess, evaluate, treat, and monitor. The risk management plan is the strategic document that describes how you will run that cycle, including scope, roles, methodology, and review cadence. The process is the activity; the plan is the blueprint for it.