
Agentic GRC: Building trust through authority, approval, and accountability
AI agents are moving from assisting GRC teams to taking action inside compliance and risk workflows.
As AI agents take on more GRC work, teams need to decide when they are ready to act, what authority they should have, where approval is required, and how every action stays accountable.
Join us for a practical discussion on:
- Where agents can research, recommend, prepare, or execute
- Where human judgment and approval should remain essential
- How to keep agent actions traceable, reviewable, and defensible
Register now to get the practical bundle of AI GRC guides on responsible adoption, governance, and managing AI risk in practice.
In this webinar
As AI moves from assisting to acting, the question is what it should be allowed to do.
We’ll look at AI action through three practical lenses: authority, approval, and accountability, to determine where agents can act, where they should ask first, and where they should stop.
Join us to unpack how GRC teams can define authority, approval, and accountability as AI moves from assisting to acting.
Meet our panel
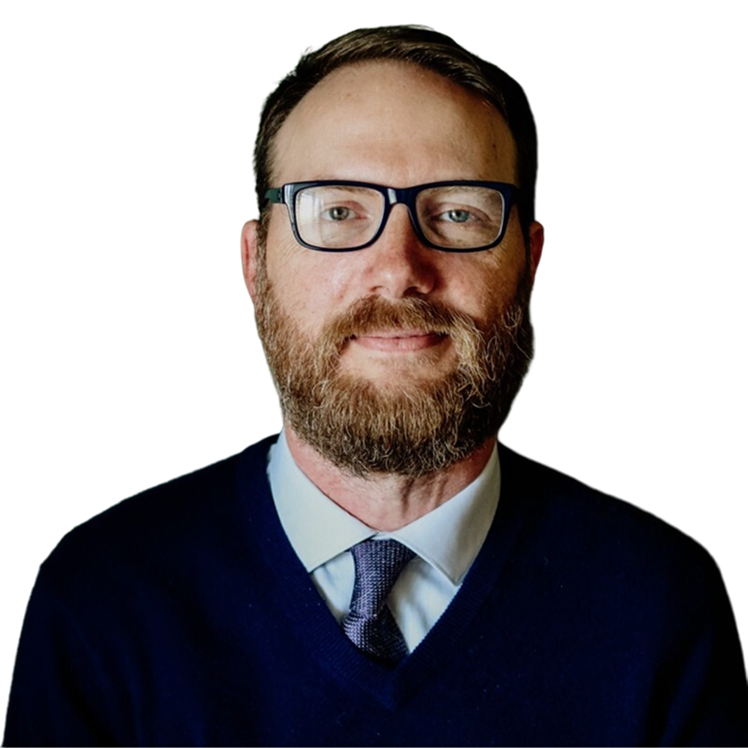
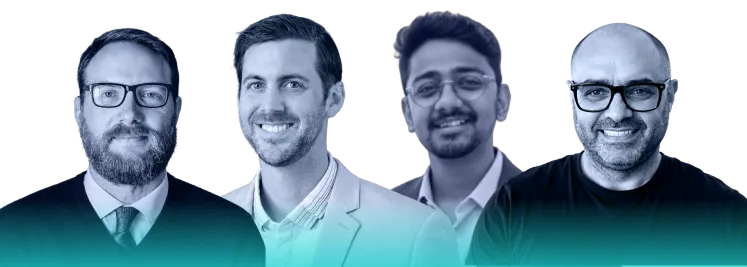
Justin is a cybersecurity and GRC leader with 29 years of experience across military, government, and private-sector environments. He specializes in enterprise risk, compliance, IAM, cloud security, and AI governance, with deep experience building scalable security programs aligned to business outcomes.
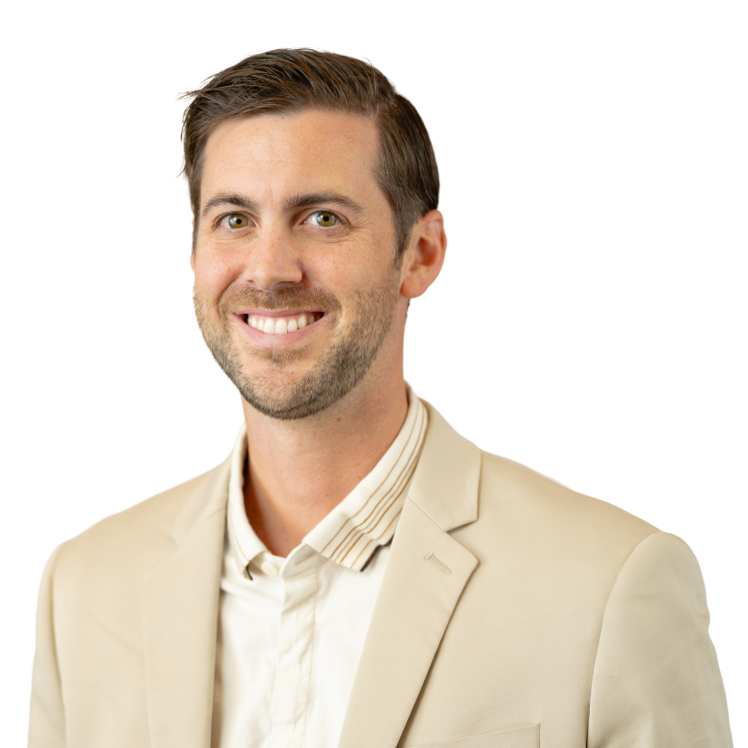
Ryan is a Security GRC leader with 13+ years of experience across audit, governance, compliance, and risk management. His background spans GRC engineering, controls, third-party risk, policy management, and scaling security programs across SaaS environments.
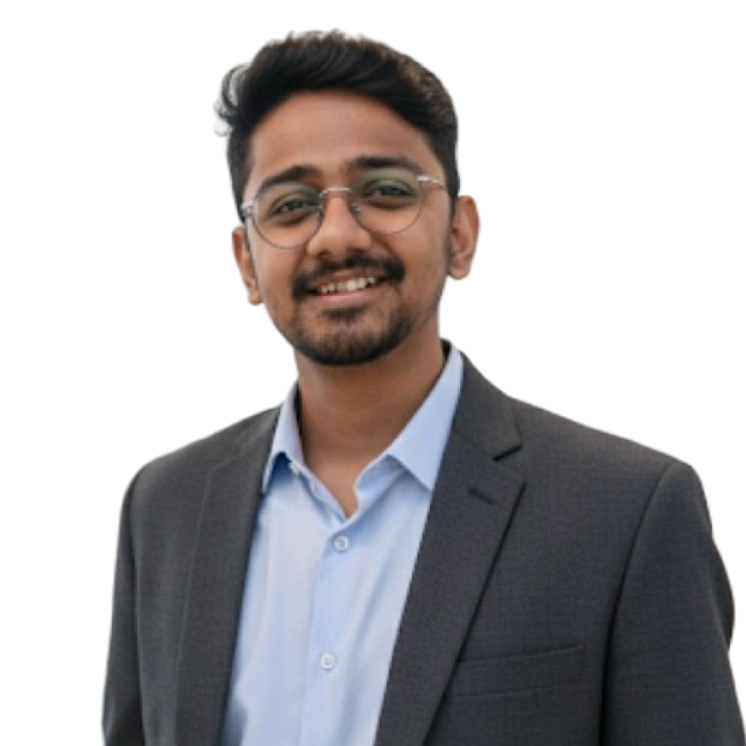
Aditya Iyer is a GRC Program Manager at Scrut Automation with 7+ years of experience across cybersecurity, risk, compliance, and IT audit. He works across SOC 2, ISO 27001, ISO 42001, GDPR, DPDPA, and NIST, focusing on practical cybersecurity, compliance transformation, and emerging AI governance.
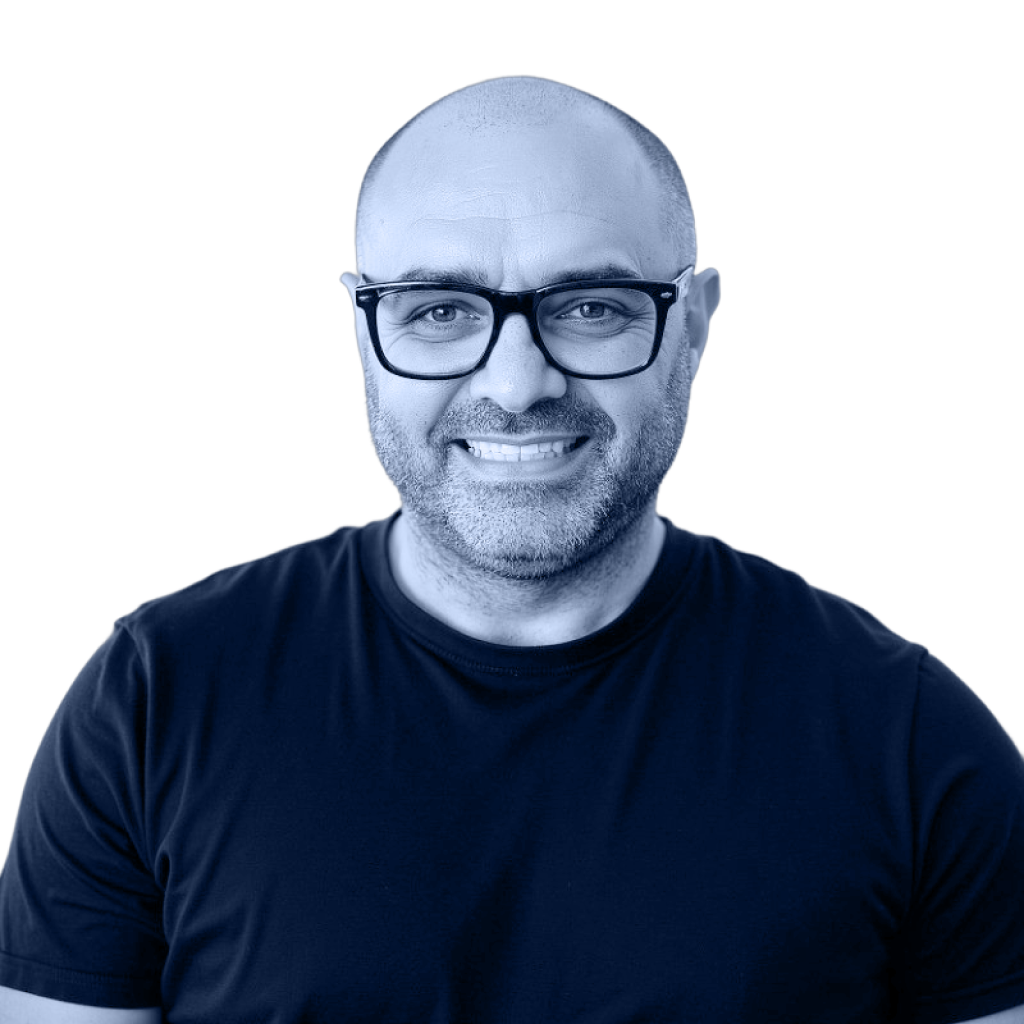
Marcio Moerbeck is an award-winning technology marketing leader with 25+ years of experience across demand generation, digital growth, and partner marketing. He has built global programs generating hundreds of millions in pipeline and revenue while leading multi-market teams.
In this webinar
As AI moves from assisting to acting, the question is what it should be allowed to do.
We’ll look at AI action through three practical lenses: authority, approval, and accountability, to determine where agents can act, where they should ask first, and where they should stop.
Join us to unpack how GRC teams can define authority, approval, and accountability as AI moves from assisting to acting.
Reserve your spot