


- Integrated risk management (IRM) aligns risk identification, governance, and treatment across an entire organization, not just IT or compliance.
- Most companies start with compliance-driven risk registers that miss operational, strategic, and financial exposures.
- IRM is structurally siloed in practice: security, financial, and operational risk rarely consolidate under one owner, even at mature companies.
- A risk register only works if it reflects real business decisions, not every risk, just the ones that matter most.
- Automation handles scoring signals and evidence collection; human judgment owns risk acceptance and board communication.
Most organizations build a risk register because a compliance framework told them to. What they end up with is an artifact nobody reads, not a program that influences a single decision.
If you are a security or GRC leader responsible for risk across more than one function, you already know the gap between the document you produced for the audit and the risks that actually keep the business up at night.
This guide is written for the people who live in that gap: CISOs, GRC managers, security leaders, and the engineering executives who inherit risk ownership because no one else is doing it. It draws on how integrated risk management works in real programs, not textbook theory.
Risk management is not a religion, and it is not a framework you mount on the wall. It is a working discipline, and this is how practitioners actually run it.
What is integrated risk management?
Integrated risk management (IRM) is a coordinated approach to identifying, governing, and treating risk across an entire organization rather than one function at a time. Unlike siloed risk management, where each team tracks its own exposures separately, IRM aligns security, operational, financial, strategic, and compliance risk under a shared view so leadership can make informed trade-offs.
In practice, the principles that make IRM work are less about a checklist and more about how the pieces interact. Proactive identification means surfacing what could hurt the business before it materializes, not documenting it after an incident. A holistic scope means the register reflects operational and strategic exposures, not just the technology risks that are easiest to name.
Risk-aware culture means the people closest to a process, an engineer maintaining a pipeline, a finance lead running an aging ERP, can flag the risk they see, because a single person rarely understands how the whole company works. Data-informed judgment means using signals and telemetry to prioritize, while a human still owns the decision. And governance means a named leader is accountable for the outcome, not just the paperwork.
It helps to separate IRM from compliance early. As Wendy Nather, Senior Research Initiatives Director at 1Password, framed it on our podcast Risk Grustlers, compliance is a method for managing risk for a very well-understood, very well-scoped area. Compliance is an input to IRM, not the whole picture. Treating audit readiness as your entire risk program is how operational and strategic exposures go unmanaged until they surface at the worst possible time.
The IRM vs. ERM distinction is worth naming here, even briefly. IRM tends to center on cybersecurity, IT, and compliance risk, the domains that a security and GRC program owns.
ERM covers all enterprise risk, including financial, market, and reputational exposure, and usually sits with a Chief Risk Officer or CFO. Most tech-native companies build IRM first, then grow into ERM as they scale.
IRM is not a software category or a compliance exercise. It is an operating model for how a company makes and defends risk decisions. Anchoring on that distinction is what separates a risk management framework that changes behavior from one that just generates evidence.
IRM vs. siloed risk management: Why integration fails in practice
IRM promises one view across IT risk, compliance risk, financial risk, and operational risk. The organizational reality is that these domains report to different leaders: the CISO, the CFO, the COO, the General Counsel, and rarely consolidate under one owner. Understanding why that happens matters more than any diagram of an idealized integrated program.
In practice, ownership falls into three common models. The first is CISO-owned, security-led, and most common in tech companies where the person maintaining the risk register sits in or near the security office. The second is CFO or CLO-owned, where the broader risk function reports into finance or legal because financial and legal risk dominate the company's exposure.
The third is committee-based, where multiple risk owners, each responsible for their own domain, meet periodically to reconcile a shared view. That periodic meeting of separate owners is, in honest terms, what the integrated version usually looks like in the real world. Even at large companies, consolidation into a single owner is rare. You are far more likely to find five or six risk owners who get together in one meeting than one person who owns everything.
At SMBs, the pattern is simpler and more accidental. The person doing IT compliance often becomes the de facto IRM owner, not because anyone gave them the mandate, but because no one else is doing it. For most companies under a couple of hundred people, risk management is not even a full-time job for the person carrying it.
Forcing consolidation can make things worse, not better. Financial risks tracked under the CFO and operational risks tracked under the COO tend to stay separate because they roll up under a different charter.
Trying to jam them into a security-centric risk register creates category confusion and register bloat rather than genuine integration. When they do belong in one system, they have to be tagged and workflowed separately: financial risks in one track, operational risks in another, kept distinct.
Siloed vs. integrated risk management dimensions
Integration, in practice, is not one owner and one register. It is defined ownership by domain, a shared escalation structure, and cross-domain visibility, usually through a GRC platform that lets separate workflows roll into one view.
Key components of integrated risk management
A useful IRM program has fewer moving parts than most framework summaries suggest. Grouped into three clusters, here is what each component is for, where it fails in practice, and what good looks like.
Foundation components establish authority and direction:
Governance. The leadership layer that assigns accountability for risk decisions. Where it fails: control ownership stays implicit, and most people who technically own a control do not know they own it. What good looks like: named, accountable owners who understand their role and the risk it maps to. As Nicholas Muy, CISO at Scrut Automation, put it, it is necessary to understand the risk in an organization first, because otherwise we buy lots of tools, get lots of findings, and nobody knows what to do with them.
Policies and standards. The documented intent and measurable criteria that make governance enforceable. Where it fails: teams write pristine documents and mistake documentation for implementation. What good looks like: policies tied to controls that actually operate and are evidenced.
Risk identification. The disciplined surfacing of what could actually hurt the business across all domains. Where it fails: the register gets populated with what is easy to define, phishing, weak passwords, rather than what matters most. The register that earns its keep names the structural weaknesses you have to manage because they are part of how the company operates, not the ones that are easy to write down.
Operational components handle risk as it lives and changes:
Continuous monitoring. Most early-stage programs skip this entirely. The result is a risk register that reflects last year's controls, not today's. What good looks like: signals that flag when a risk entry needs a fresh look.
Incident response. Incident response fails when it exists as a document nobody has rehearsed. The fix is not a better document. It is a runbook mapped to real roles and tested at least annually.
Vendor and supply chain risk. Managing exposure introduced by third parties. Where it fails: teams over-invest in expensive site visits. Most serious vendor compromises trace back to phishing and business email compromise, not to a missing site visit, so training and monitoring beat travel budgets. What good looks like: a structured questionnaire cadence, continuous monitoring of critical vendors, and security awareness training requirements written into vendor contracts.
Get this right with structured vendor and supply chain risk practices and dedicated third-party risk management.
Business continuity. Where it fails: plans go stale and untested. What good looks like: business continuity plans that reflect the current business, not last year's.
Measurement components tell you whether any of this is working. KPIs, performance reporting, and continuous improvement belong together, and we cover them in depth in the metrics section below.
Three components get skipped most often by early-stage programs: continuous monitoring, vendor and supply chain risk, and residual risk reassessment. If you are building an IRM program from scratch, these are the ones worth pulling forward.
IRM vs. ERM: What’s the difference?
The IRM vs. ERM distinction matters more in practice than most definitions capture. The three axes below, scope, ownership, and tooling, determine not just how you label the program, but who builds it, who funds it, and when it becomes necessary.
The first is scope. IRM is cybersecurity, IT, and compliance-centric. ERM is broader: it covers all enterprise risk, including financial, market, and reputational exposure. The second is ownership. IRM is typically CISO-led or owned by the GRC function. ERM typically sits with a Chief Risk Officer or CFO. The third is tooling. IRM usually runs on a GRC platform built for control and evidence workflows, while ERM leans on financial modeling alongside GRC.
For most tech-native companies, IRM is the right starting point. Startups keep everything consolidated out of necessity early on, then fragment by charter as separate leaders take ownership of financial and operational risk. That means IRM comes first, and ERM formalizes later as the organization has the scale to support a dedicated risk function.
In practice, typically around Series B, as risk committees form and separate owners emerge, the two begin to converge, and companies start bridging their enterprise GRC and IT risk management framework under a shared governance structure.
What changes when IRM works
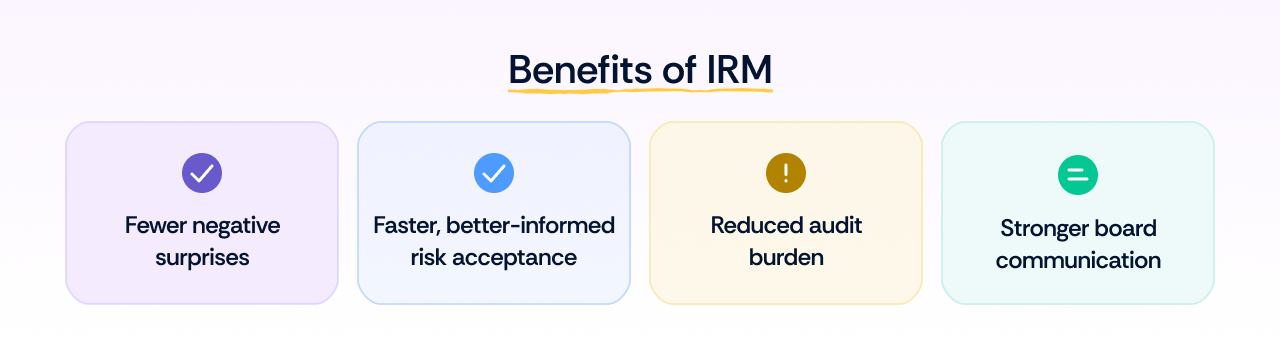
Reframing IRM around outcomes is more honest than listing benefits. Here is what actually changes when the program works, and what the absence of each looks like.
Fewer negative surprises. Risks get identified before they materialize because the program is looking for structural weaknesses, not just reacting to incidents. Without it, the business keeps getting blindsided by exposures that someone could have named in advance.
Faster, better-informed risk acceptance. When the register is tied to real business context, leaders can weigh a risk against the decision in front of them and accept or treat it quickly.
Without it, risk acceptance either stalls in analysis or happens implicitly, with no one on record.
Reduced audit burden. When risk documentation maps to control evidence, the same work serves both risk management and the audit, and every audit cycle stops being a scramble for evidence that a mapped program would have surfaced automatically. Handled well, this is where compliance risk management stops being a separate project and becomes a byproduct of running the program.onger board communication. Risk framed in business-impact terms lands with a board in a way technical metrics never will. A board that only sees vulnerability counts eventually stops asking questions, which is the worst outcome.
That last point is the one practitioners underrate. The most important risks are often not the ones you can quantify in dollar terms, but the ones around eroding customer trust or a compliance gate that locks you out of a market. Learning to frame risk communication to the board in those terms is what earns the program its seat.
Building a risk register that doesn't become an audit artifact
Most risk registers are built once for an audit, populated with whatever is easy to define, and never updated. That is how a decision tool degrades into a compliance artifact. A register that stays operationally relevant comes down to four practical questions.
What goes in. Only risks tied to specific business systems, processes, or decisions belong in the register, not generic categories. The common failure is a register bloated with entries everyone already knows are risks, phishing, weak passwords, that add no judgment value.
Listing your production database because it holds PII is a start, but incomplete: you also have to define the risk you are actually managing, the structural weakness you cannot simply engineer away because it is part of how the product works. That is the entry worth having.
Who owns it. Risk identification and risk treatment are different jobs with different owners. Identification belongs to people with cross-functional visibility, the ones who understand how the business actually works. Treatment flows down to operational owners who can act on it. The handoff between the two is where accountability breaks if it is not explicit, so the register has to name who owns each entry and track it through a real workflow, not leave it implicit.
How often it's reviewed. Frequency matters less than most people think, and it depends on how fast the business actually changes. At minimum, ask a quarterly question: has enough changed in our business that something needs updating? Run a full, top-to-bottom reassessment annually. Trigger out-of-cycle reviews when the business model, geography, key vendors, or a material incident change the picture.
Updating a register daily is meaningless if the underlying processes and people did not change. The cadence should match the rate of meaningful change, not a fixed calendar.
When to sunset an entry. Sunset a risk based on whether the underlying condition has changed, not on time elapsed. The register should not contain everything impactful, only the things impactful enough to require active oversight. A register that says everything is a strategic risk says nothing.
Risk register anti-patterns
- Using the register as a vulnerability escalation path. The register is not a security Jira. Do not let people shove vulnerabilities into it to get attention or resources.
- Treating 200+ entries as a sign of maturity. As Nicholas Muy, who once managed the register at a multibillion-dollar public company, pointed out, even at that scale, the register stayed under a hundred entries. A big register signals noise, not rigor.
- Never closing a risk once accepted. Accepted risk still needs to be revisited when conditions change.
- Not tying risks to specific accountable owners. An entry with no owner is a note, not a managed risk.
For the mechanics of building and maintaining the register itself, see how to create a risk register, risk register maintenance, and the distinction between inherent vs. residual risk
How to implement integrated risk management: A practical sequence
A textbook risk management framework implementation is a multi-year enterprise project. A growing company does not have that runway, and treating all fourteen textbook steps as equally weighted is not useful. Here is the sequence that reflects real program maturity, in four phases.
Phase 1 - Establish: Secure a leadership mandate, run a first risk identification pass, and put basic governance in place. The single most important input here is getting the right people in the room. One person rarely understands how the whole company works, so a defensible first assessment needs someone who knows the technology, someone who knows operations, and someone who knows the back-office processes. Bad information produces a bad assessment no matter how good your methodology is.
Phase 2 - Operationalize: Introduce a lightweight framework: policies, thresholds, a consistent scoring approach. Keep it simple enough that the team will actually use it. Build risk treatment plans and start embedding risk consideration into day-to-day business processes rather than treating it as a separate exercise.
Phase 3 - Instrument: Add technology for risk management automation, continuous monitoring, and reporting. This is where the program stops depending on one person remembering to chase evidence and starts surfacing signals on its own. Pair it with an effective risk management process so the tooling supports judgment rather than replacing it.
Phase 4 - Sustain: Set a review cadence, connect incident response to the register, and align with your compliance obligations so the same work serves both. This is also the phase where the register earns its keep between audits, not because someone is maintaining it, but because the program is designed so it updates itself when conditions change.
For companies under 200 employees without a dedicated risk function, Phases 1 and 2 usually overlap, and the framework may be a structured approach rather than a formal methodology. The minimum viable IRM program for a 50 to 200-person company is not complicated: a maintained risk register with documented owners, treatment decisions, and a quarterly review.
The end result you are after is an artifact of your top risks, organized and classified, with an accountable owner and a clear record of when and why each was resolved. What can wait: formal ERM tooling and heavy quantitative scoring. For the broader rollout, a GRC implementation roadmap helps sequence the later phases.
What IRM automation can and cannot do
Automation genuinely reduces IRM toil. The failure mode is subtler: when it is asked to do work that belongs to a person, the gaps it creates are harder to detect than manual ones. Knowing where the line sits is the whole game.
What automation handles well:
- Evidence collection and continuous control monitoring.
- Surfacing signals that a risk entry needs review, tracking treatment status, and keeping owner accountability visible so nothing falls through.
- Scoring inputs for known risk categories based on integration telemetry.
- Generating first drafts of risk reports.
Automation is at its best when it goes through large amounts of information in an honest, defensible way so you can organize it and make better-informed assessments. Automation that just takes random information to make pretty charts, without helping you make a decision, is worse than useless.
The boundary matters because the failure mode is not automation doing too little. It is automation doing the wrong things. These decisions belong to a person:
- Risk acceptance decisions, especially when residual risk exceeds appetite.
- Deciding whether a new business activity introduces a material new risk.
- Board-level risk communication.
- Interpreting how a regulatory change affects an existing risk entry.
- Closing a risk as resolved.
The signal vs. decision distinction. Automation is best used to surface signals: flagging that a critical system's access controls have weakened, or that a vendor's security posture has changed. The register is not meant to be exhaustive; it exists to give you the insight to make a judgment. So the tooling should surface the critical signals and leave the determination, does this become a register entry or not, to a person who has the context to decide.
For the underlying capabilities, see automating risk management, GRC automation, and the Scrut risk management platform.
Measuring IRM effectiveness: KPIs and metrics
Leading indicators tell you where risk is heading: risk exposure trends, treatment plan completion rates. Lagging indicators tell you what already happened: incident frequency, mean time to detect, mean time to respond.
Most boards see only lagging indicators, and that is usually the program's fault, not the board's. The programs that hold up track both, and they know which metric belongs in which room: business-impact framing for the board, program health for the CISO, operational detail for the risk team. The table below maps each category to its audience.
Enterprise risk metrics, KPIs, and reporting governance
The right metric set depends on maturity. Early-stage programs should not try to run the full table. Focus on four to five core metrics first, the bolded rows above, risk score trend, treatment timeliness, mitigation effectiveness, and incident response, and expand as the program matures. Chasing the whole table before the basics are stable is how measurement becomes noise. For deeper treatment, see risk scoring and the broader set of cybersecurity metrics.
Long-term impact of IRM on business resilience
Two things happen to a risk program that survives long enough to matter, and neither shows up in a benefits list.
The first is institutional knowledge. A program that has been running long enough accumulates a record of which risks actually materialized versus which stayed theoretical. That history is the single best input to future prioritization, because it grounds your judgment in what your specific business has actually experienced rather than what a framework says should worry you.
The second is defensibility. Organizations with mature IRM hold documented risk acceptance decisions, who accepted what, when, and why. That documentation becomes real evidence in regulatory inquiries, M&A due diligence, and cyber insurance claims, where the question is not just whether you were secure but whether you made and recorded reasonable decisions.
The mechanics of getting there are less dramatic than the payoff. As Anoop Thomas Mathew, Co-Founder at Docket AI, described it: “Prior to Scrut, we did this in spreadsheets. With Scrut, we have it all in one place and are able to manage version control and seeing the kinds of changes that exist across the organization.”
That shift, from a static artifact to a versioned, permissioned record, is what makes the move from point-in-time to continuous risk management possible, and it is where the ROI from GRC compounds over time.
Conclusion
IRM is an operating model, not a tool purchase or a compliance checkbox. It defines how a company makes and defends risk decisions across domains. The register only earns its keep when it reflects real business decisions and names accountable owners, not when it is exhaustive.
Automation surfaces signals; humans own acceptance, interpretation, and board communication. Knowing the line is the discipline.
Integrated risk management done well is a commitment: to make risk visible across the whole business, and to keep it current as the business changes. It is not the register you produce for the auditor. It is the judgment the register supports. If you are evaluating tooling to run that program, explore Scrut's risk management module.
If you want to go deeper on the foundational artifact first, start with how to create a risk register.
Integrated risk management (IRM) is a coordinated approach to identifying, governing, and treating risk across an entire organization rather than one function at a time. Unlike siloed risk management, where each team tracks exposures separately, IRM aligns security, operational, financial, strategic, and compliance risk under a shared view so leadership can make informed trade-offs. It is an operating model, not a software category or a compliance exercise.
Businesses face risk across many domains at once, and treating any one, usually compliance, as the whole picture leaves the rest unmanaged. IRM helps organizations identify exposures before they materialize, tie risk decisions to business context, and communicate risk to leadership in terms they can act on. The result is fewer surprises and defensible decisions.
Track both leading indicators (risk exposure trends, treatment completion rates) and lagging indicators (incident frequency, MTTD/MTTR). Start with four: how your risk score is trending, how many high-severity items are open, whether treatment plans are completing on time, and whether mitigations are actually working. Present them to the right room, business impact for the board, program health for the CISO, operational detail for the risk team.
Ownership depends on company size and structure. At smaller companies, the CISO or Head of Security is often the de facto owner, frequently because no one else is doing it. At larger companies, a Chief Risk Officer or a cross-functional risk committee holds the mandate. In practice, risk domains rarely consolidate under one person. IRM works best when ownership is defined by domain with a shared escalation structure.
The simplest way to separate them: IRM is the security and GRC team's domain. ERM is the CRO or CFO's domain. IRM is usually the starting point for tech-native companies and eventually feeds into a broader ERM program as the organization scales and risk committees form.