



- A compliance audit is a structured review of whether your organization's controls meet applicable laws, frameworks, or contractual obligations, conducted internally or by a third-party auditor.
- Audits differ by type: cybersecurity (SOC 2, ISO 27001), financial (SOX), data privacy (GDPR, HIPAA), and health and safety each follow distinct standards and produce different outputs.
- Auditors test both control design and operating effectiveness. Having a policy is not the same as running the control.
- Audits stall most often not because controls are missing, but because evidence is disorganized.
- Compliance automation platforms reduce the manual evidence scramble and keep controls audit-ready year-round.
Compliance audits help you verify that your organization operates within the boundaries of applicable laws, regulations, internal policies, and contractual obligations. They surface gaps in financial reporting, data privacy, or vendor oversight before those gaps escalate into legal, operational, or reputational risk.
This guide breaks down what a compliance audit is, the types you may face, the exact steps to run one, and the challenges teams hit most often while preparing.
What is a compliance audit?
A compliance audit is a systematic review of an organization's adherence to regulatory, legal, or internal requirements. Its purpose is to identify gaps, prevent violations, ensure accountability, and build customer trust. Depending on the requirement, it can be conducted internally or by an external third party.
The deliverable varies by type, and this is where most buyers get confused. SOC 2 produces an attestation report. ISO 27001 produces a certificate. GDPR and HIPAA are regulations, so no audit credential proves compliance with them. An assessor can evaluate readiness, but no certificate or attestation exists. Understanding how auditors evaluate risk during a compliance audit and which applicable frameworks govern your business is the first step in scoping the engagement.
Compliance audits were historically conducted annually, and frequency still varies with regulatory mandates and internal requirements. But the trigger has shifted. Many audits are no longer purely calendar-driven. They are increasingly request-driven, prompted by a customer, regulator, or insurer who wants proof today, not next quarter. For internal audits, compliance officers, risk managers, or internal audit teams initiate and coordinate the work. For external audits, the organization's role centers on preparation, documentation, and giving third-party auditors the access they need.
Example of a compliance audit
Consider a U.S. healthcare organization that must comply with HIPAA. A HIPAA compliance audit evaluates how the organization stores and secures patient records, who can access them, and whether safeguards like encryption are in place, all to protect patient privacy and avoid regulatory penalties. This kind of audit validates adherence to a legal obligation while protecting sensitive health information.
What is the purpose of a compliance audit?
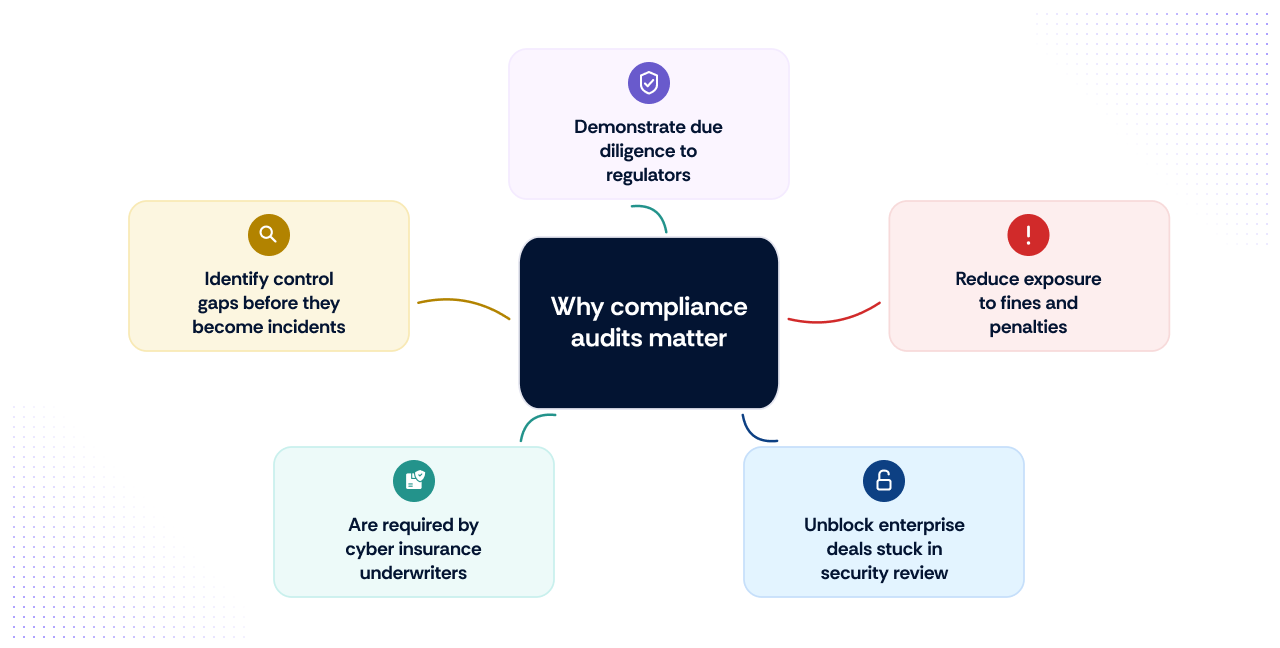
The first purpose is regulatory and legal. A compliance audit demonstrates due diligence to regulators, surfaces non-compliance with laws or policies before an enforcement body does, and reduces exposure to fines and penalties. For a company operating in a regulated space, the audit is often the difference between a documented, defensible control environment and a paper trail that collapses under scrutiny.
For most growth-stage companies, the purpose that matters day to day is commercial. Enterprise procurement teams now gate deals on audit status. A stalled SOC 2 can freeze a six-figure contract at the security-review stage. Cyber insurance underwriters ask specific questions about controls before they write a policy.
Compliance leaders increasingly describe this as the shift from proving controls exist to proving they actually operate. Audit status is no longer a back-office metric. It shows up in pipeline reviews, which is where compliance as a revenue enabler stops being a slogan and becomes a number the sales team watches.
The internal purpose gets the least budget, which is exactly why it produces the most surprises. Run well, an audit identifies control gaps before they become incidents and keeps the control environment from drifting between cycles. This is also why staying audit-ready year-round and treating compliance risk management as a continuous practice matters more than a two-month sprint before fieldwork.
One clarification worth making: a compliance audit is not a binary pass/fail exam. Auditors issue an opinion on whether controls are suitably designed and, in the case of a period-based audit, operating effectively. The output is a professional judgment supported by evidence, not a green checkmark.
Why compliance audits matter (and what's actually at stake)
The regulatory stakes are concrete. Under GDPR, violations can reach 20 million euros or 4% of global annual turnover, whichever is higher. HIPAA penalties reach up to $1.5 million per violation category per year at the highest culpability tier under the statutory cap, with HHS applying annual inflation adjustments that push the operative ceiling higher. These are not theoretical numbers. They are the reason a compliance risk assessment belongs in the budget conversation, not as an afterthought.
The commercial stakes are just as real and arrive sooner. GRC and security managers experience audit status directly in the sales cycle: enterprise buyers send security questionnaires before they sign, and a missing or lapsed report can stall a deal at procurement. Insurers price coverage against demonstrated control maturity. This is why audit posture functions as compliance as a revenue enabler rather than a cost center.
There is a third dimension that rarely makes it into the budget conversation: readiness posture. The teams that fare best treat audit readiness as a daily state, not a two-month sprint before fieldwork. Practitioners who have run their own audits describe the difference plainly. A company that can prove its controls on any given morning walks into fieldwork calm. A company that starts preparing 60 days out spends the audit scrambling to reconstruct evidence it should have been collecting all along.
Types of compliance audits (and which frameworks apply)
Compliance audits take different forms depending on your industry, risk exposure, and applicable laws. Each type serves a distinct function and produces a distinct output. The table below maps the landscape before we go deeper.
Audit categories by framework, deliverable, and target profile
Cybersecurity and data privacy
These audits assess whether you have adequate controls to protect sensitive information and mitigate cyber risk. Two things get grouped here that are not the same, and the distinction matters legally.
Standards and attestations are voluntary and produce a formal output you can hand to a buyer. SOC 2 is a framework developed by the AICPA that assesses security, availability, processing integrity, confidentiality, and privacy. It produces an attestation report, never a certificate. ISO 27001 is an international standard that produces an accredited certificate, valid for three years with annual surveillance audits, issued by an accredited certification body.
Regulations are a different category. GDPR governs the personal data of EU residents, and HIPAA governs protected health information in the U.S. Neither produces a certificate or attestation. An assessor can evaluate your readiness, but there is no credential that proves compliance. Treating them as "achievable frameworks" is exactly the misunderstanding that leads to broken warranties and failed enterprise reviews. PCI DSS and CCPA round out the common set for any data-processing business.
Financial and regulatory compliance
SOX changed the stakes for financial audits in 2002, and the personal liability it created for executives has never gone away. Under Section 302, the CEO and CFO personally certify the accuracy of financial reports and the effectiveness of disclosure controls. Under Section 404, management and the external auditor attest to the effectiveness of internal controls over financial reporting.
In practice, a SOX auditor tests whether the controls that produce financial statements actually operate: who can post a journal entry, whether segregation of duties holds, or whether system changes go through review and approval. A failure here is not abstract. It lands on a named executive. Broader financial compliance requirements extend to IRS guidelines, FINRA oversight, and state and local tax rules.
ESG and environmental sustainability
Until recently, ESG audits were largely voluntary. The EU's CSRD changed that for a large set of enterprises with sustainability reporting obligations. These audits examine environmental impact, ethical conduct, and governance practices against standards like ISO 14001, EPA regulations, and reporting frameworks such as GRI. The output is typically a third-party assurance report over disclosed ESG data.
Health and safety audits
In high-risk environments, the evidence auditors want is operational, not just documentary. These audits check compliance with occupational safety and public health standards under OSHA, ISO 45001, and CMS oversight for healthcare providers. In workplaces involving hazardous materials or emergency response, training records for hazardous-site operations often form part of the evidence reviewed.
Industry-specific compliance
Many industries require tailored audits driven by operational risk, data sensitivity, or government oversight. FISMA governs cybersecurity for U.S. federal agencies, CMMC applies to defense suppliers, and NIST frameworks underpin risk management for critical infrastructure. The deliverable is frequently an authorization to operate or a formal assessment report.
What is a social compliance audit?
A social compliance audit assesses whether an organization adheres to fair labor practices, non-discrimination policies, and workplace ethics. It reviews HR policies, wage and hour compliance, and adherence to standards like EEOC guidelines. The audit can be internal (a self-assessment of policies against labor law) or external (a third-party review, common in supply-chain and manufacturing contexts).
The output is usually an assessment report rather than a certificate, and it maps to the broader set of compliance standards an employer is expected to meet.
Navigating each audit type. The right auditor is framework-specific. For PCI DSS, check the assessor's QSA license and the regions they are approved for. For SOC 2, confirm the firm is enrolled in the AICPA peer review program with a passing rating. For ISO, confirm the certification body is accredited under a member of the International Accreditation Forum. These checks take minutes and separate a credible engagement from a worthless one.
Internal audit vs. compliance audit: what's the actual difference?
Both an internal audit and a compliance audit contribute to a strong governance posture, but they serve different purposes, answer to different audiences, and produce different outputs.
Internal audit vs. external compliance audit
In short: internal audits drive improvement, and compliance audits demonstrate conformity.
Before committing to a formal audit, most teams have a third option available, one that most underuse: the readiness assessment. A readiness assessment uses the same control checklist as the final audit, but its report only lists findings, the positives and the negatives.
The moment a firm starts telling you how to fix a finding, it has crossed into consulting. Independence rules require that the firm advising you cannot also be the firm that audits you, which is why "free readiness assessments" are usually a sales motion rather than a substitute for the real thing.
Teams running a compliance automation platform often have a live readiness score on their dashboard, which reduces the need for external readiness support. A human auditor still adds value for policy review and edge-case judgment a platform cannot make. A SOC 2 readiness assessment done well means no surprises during fieldwork.
For smaller companies, the question is often whether an internal audit function is worth building at all. It is. For organizations under 200 people without a dedicated GRC manager, the minimum viable program is a quarterly internal audit focused on the highest-risk controls: access control, incident management, and cryptographic controls. In the absence of a GRC specialist, ownership typically falls to the CTO's team, since compliance controls track closely with the technology.
In the experience of Aditya Iyer, GRC program manager at Scrut, a company already maintaining SOC 2 has done roughly 40% of the underlying work, because SOC 2 is a comprehensive control set that carries over into the internal audit. Working from an internal audit checklist and treating audit evidence and documentation as an ongoing discipline turns this from a scramble into a routine.
How to conduct a compliance audit: step-by-step
A compliance audit follows a phased process. The table below gives you the full arc before we go deep on the steps that matter most.
Standard audit lifecycle and execution steps
1. Scope and planning
Define the audit's objectives and scope first: which areas, processes, and systems are in scope, and why. Identify the applicable regulations or frameworks (SOC 2, ISO 27001, HIPAA, GDPR), then assign roles across the audit team and stakeholders so accountability is clear before any evidence changes hands.
2. Team assembly
Assign internal owners for each control area and engage an external auditor if the audit requires attestation or certification. Leadership needs to be involved here, not just at kickoff. A common failure is leadership treating the audit as purely IT's or the CISO's job, then being surprised when the auditor needs a management sign-off or a business-context answer.
3. Documentation collection
Auditors gather policies, procedures, security protocols, org charts, access logs, change-management records, and prior audit reports to establish a baseline of the control environment. How you organize this material determines whether fieldwork is calm or chaotic.
Organize evidence by control, not by date or department. When an auditor asks for the evidence behind a specific control, control-wise organization makes it findable in seconds.
Date-wise or department-wise storage turns every request into a scavenger hunt. As Aditya Iyer puts it, going control-wise is the priority for anyone trying to get into audits.
What poor organization actually costs. The cost surfaces during fieldwork, when the auditor pulls a population and asks for evidence on a random sample. If the GRC manager is visibly scrambling, the auditor's confidence in the next sample drops. That struggle can be read as a deficiency in its own right.
Common failure modes: approvals living as a thumbs-up on a Slack message (auditors do not accept that), evidence sitting on a departed employee's still-active drive, and screenshots with no timestamp. Automating this through access reviews and automating evidence management removes most of it.
In Scrut's own SOC 2 audit with EY, a missing sign-off email on one quarter's firewall review almost became a finding. The reviews were happening, but the CTO's approval for one quarter was never captured on email. The lesson: every piece of evidence you take on mail or a communication channel needs a sign-off from upper management. Close the loop, or the auditor will find the gap.
Understanding the types of audit evidence auditors actually rely on helps you spend effort where it counts.
4. Risk assessment
Map your compliance risks to specific controls and regulatory clauses. The question is not whether a control exists. It is whether it would actually catch the failure it is supposed to prevent. A quarterly access review that nobody reviews is a control on paper, not in practice.
5. Control testing
Auditors test controls for operating effectiveness through walkthroughs, evidence review, sampling, and interviews with control owners. The goal is to validate that controls run consistently and as intended, not just that they exist on paper.
Auditors do not test every control with the same intensity. They apply a risk-based approach, allocating more time and deeper sampling to controls where a failure would cause significant harm. A control governing production-environment access for a recently departed employee carries far higher inherent risk than a contractor's access to an outdated internal dashboard.
Better firms document this audit risk model explicitly and can explain their testing rationale if asked. In some cases, deeper sampling is a good sign. In Scrut's own audit, endpoint checks kept returning clean results, so EY expanded the sample specifically because the results held up, not because anything looked wrong.
What actually surprises first-time auditees
Access review depth. Expect to generate a timestamped active HR list, fetch user lists for every in-scope application, reconcile them, get department-head approval, and justify every instance of privileged access. First time through, this took Scrut's IT manager 20 to 25 days by hand.
Point-in-time evidence rigor. Auditors will reject a screenshot missing a timestamp or a signature, even when the underlying control clearly ran.
Small gaps in the trail. A single missing sign-off email on an otherwise-solid quarterly review can trigger a finding.
The observation period is unforgiving. Once fieldwork begins on a past period, you cannot retroactively fix evidence. What happened, happened.
An audit management platform that captures timestamps and logs automatically removes most of these surprises. After Scrut moved access reviews onto its platform module, the process that was pure chaos in the first audit became manageable, and the time required was cut in half.
6. Reporting
The auditor compiles findings into a report covering control weaknesses, associated risk ratings, and recommendations. The report goes to leadership, compliance officers, and, depending on the framework, external stakeholders.
7. Remediation and follow-up
Track remediation to closure and retest to confirm the gap is fixed. An open finding that sits untouched for a quarter tells the next auditor more than the original finding did.
Common compliance audit challenges (and how to resolve them)
Listing challenges without resolutions only validates the problem. The table below pairs each with a practical path forward.
Key audit execution challenges and practical resolutions
The regulatory landscape shifted significantly in 2025. The IIA's 2024 Global Internal Audit Standards took effect in January 2025. PCI DSS v4.0 replaced v3.2.1 when v3.2.1 was retired in March 2024, and v4.0.1 followed in June 2024 as a minor errata revision to v4.0. DORA applied from 17 January 2025. Staying current on common compliance mistakes and running continuous compliance monitoring turns regulatory change into manageable delta work rather than a fire drill.
The evidence gap is a technology problem. The accountability gap is not. Tracking the shift toward continuous auditing closes the first. Clear ownership closes the second.
What makes a compliance audit successful?
- Clear audit scope. Scope creep is the most common reason an audit runs long. Define which systems, processes, and frameworks are in scope before any evidence changes hands.
- Stakeholder involvement. When control owners can answer questions directly, the auditor verifies. When they can't, the auditor digs. The difference in fieldwork duration is significant.
- Automation. Technology that collects evidence and monitors controls continuously removes the manual scramble and gives you a readiness signal year-round.
- Timely follow-up. Findings that sit open for 90 days tell the next auditor more than the finding itself did. Retest and close.
- Audit trail maintenance. An auditor relies on the record, not your memory. Close the loop on every quarterly review, every policy sign-off, every firewall review. The evidence nobody questions internally is exactly what an auditor questions first.
How to evaluate an auditor. The choice of firm shapes audit quality more than most teams realize. Four criteria separate a strong auditor from a weak one.
Check accreditation first: AICPA peer-review enrollment with a passing rating for SOC 2, a QSA license for PCI, an IAF-accredited certification body for ISO. Second, check the individual auditors' technical credentials. CISA or CISSP-certified personnel understand the technology and audit deeper. Third, confirm the firm runs a separate QA team from the assessment team. Fourth, ask for references from organizations similar to yours in size, industry, and product. Cost matters, but it should be the last filter, not the first.
The tradeoffs between choosing between a boutique and Big 4 auditor come down to your data sensitivity and customer profile, and knowing what to ask about audit quality is what separates a rigorous engagement from a rubber stamp. All of it feeds into improving operating effectiveness over successive audits.
Compliance audit services: what to expect and when to use them
Firms ranging from the Big 4 to specialized boutiques offer compliance audit services across three areas: readiness assessments, the formal audit engagement itself, and post-audit remediation support.
The distinction that trips teams up: a readiness assessment is not the audit. It uses the same control checklist, but it cannot be relied on for certification. Independence standards require that the firm providing remediation advice cannot also perform your formal audit. The two engagements must come from separate firms.
External services are worth the investment when it is your first audit, when your scope spans multiple frameworks, when you operate in a regulated industry, or when a customer's procurement process requires a credibility signal you cannot generate internally. If you have mature internal capability and a platform that surfaces a live readiness score, external readiness support becomes optional rather than essential.
Automating compliance audits with Scrut
Compliance teams are asked to move faster with tighter resources while staying audit-ready all year. That is the gap Scrut closes.
Whether you are preparing for SOC 2, ISO 27001, HIPAA, or GDPR, Scrut keeps you ahead of both internal and external requirements. With Scrut, you can:
- Pull evidence automatically from cloud services, HR systems, and ticketing tools, so nobody is taking manual screenshots the night before fieldwork.
- Map controls across frameworks once. Each additional framework becomes delta work, not a fresh project.
- Watch control health in real time through dashboards and automated alerts, so drift surfaces before an auditor finds it.
- Assign ownership and track remediation in one place, so when an auditor asks who fixed what and when, the answer is already documented.
- Keep a single source of audit truth that is ready even for a surprise request.
Audit readiness stops being a two-month sprint and becomes part of how the team operates every day.
Begin by identifying which frameworks apply to your business (e.g., SOC 2 for SaaS companies, HIPAA for healthcare, ISO 27001 for global security). Document your systems, processes, and controls, then test them for effectiveness. Platforms like Scrut automate much of this, from control mapping to evidence collection.
If your organization operates in a regulated industry or handles sensitive data, compliance audits are not just recommended, they’re often required by law or contract. Even in unregulated sectors, audits are considered best practice for risk management and customer trust.
Not exactly. A regulatory audit is typically conducted by a government body to enforce specific laws (e.g., an IRS tax audit). A compliance audit, however, may be internal or performed by a third party to validate adherence to specific standards or contractual commitments (like SOC 2 or PCI DSS).
Most organizations conduct audits annually, but high-risk industries such as fintech, healthcare, and cloud infrastructure may opt for quarterly or bi-annual reviews to maintain assurance and prevent drift.
Preparation starts with organized documentation, defined audit ownership, and updated policies. Leveraging a compliance automation platform like Scrut ensures all evidence, policies, and controls are centralized and audit-ready at any time.