


- Risk management automation handles data collection, control monitoring, evidence gathering, and vulnerability scanning well. However, risk scoring and risk acceptance still need human judgment.
- The highest-value automation targets are repetitive, high-volume tasks: evidence collection, continuous monitoring, and vendor risk scoring.
- Risk registers work best when they stay focused on a small set of strategic risks, not every operational finding.
- A green dashboard tells you controls were in place during the observation window. It does not tell you what your posture looks like today.
- Matching your automation level to your organization's maturity stage prevents over-engineering.
Most teams evaluating risk management automation already have a GRC platform or a stack of tooling in front of them. The harder question isn't whether to automate. It's knowing what to actually hand over to software and where automation quietly creates false confidence.
Some teams want automation to score every risk in their environment. Others want it only to surface the critical signals and keep human authority over the final call. That tension is the whole game. Automation genuinely reduces toil in specific, repeatable areas. Applied without judgment thresholds, it produces misleading risk scores and a dashboard that looks reassuring while telling you very little about your real exposure.
This guide draws a practitioner-informed line between the two: what automation handles well, where humans stay in charge, and how to build a program that respects the difference.
What is risk management automation?
Risk management automation is the use of software and automated workflows to identify, monitor, score, and respond to organizational risks, reducing manual effort while keeping an audit-defensible evidence chain intact.
That means pulling evidence from cloud integrations, monitoring controls continuously, flagging control drift, and surfacing high-confidence signals for a human to act on. Done well, it takes the repetitive weight off a small team and lets them spend their time where judgment actually matters.
Worth being precise about what automation is not. It does not eliminate human judgment on risk acceptance, risk appetite setting, or escalation decisions. The most useful implementations don't try to score everything. They surface the risks that are inherently critical, like business-critical systems with known failure modes, and leave the final determination to a named human who has the context and the authority to make it. The register isn't meant to be exhaustive. It's meant to give you enough insight to decide what belongs on it.
There's also a distinction worth drawing between risk management automation and GRC automation more broadly, and between risk automation and compliance automation specifically. Compliance automation focuses on gathering evidence and proving adherence to a framework like SOC 2 or ISO 27001. Risk management automation has a wider scope: it covers operational, vendor, and strategic risks that live well beyond any single regulatory requirement.
The two overlap heavily (compliance automation is effectively a subset of a broader risk program), but they are not the same thing.
If you need to ground yourself in the underlying discipline first, risk management is the systematic process of identifying threats and vulnerabilities, evaluating their likelihood and impact, and deciding how to treat them. Automation doesn't replace that discipline. It scales the repetitive parts of it.
Key components of risk management
Understanding the moving parts of risk management helps you see which ones are actually good candidates for automation and which ones aren't. Each component maps to the underlying risk management process, but they differ sharply in how much of the work a machine can carry.
Core risk management components in operational practice
Read down the list and a pattern emerges: identification, monitoring, and reporting lean heavily toward automation, while analysis, communication, and the judgment calls inside assessment stay stubbornly human. The next section makes that line explicit.
Common challenges in traditional risk management
Manual risk management breaks down in predictable ways, and each of these is a place automation earns its keep.
Manual data collection eats your team's time. Chasing screenshots across Slack threads, cloud consoles, and spreadsheets is slow, error-prone, and impossible to scale. Every hour a security lead spends assembling evidence is an hour not spent on a decision that actually requires their judgment. This is the single most common reason teams reach for automation in the first place.
Risk registers go stale. Here's the failure mode competitors rarely mention: for a lot of companies, the risk register gets built once, usually because a compliance framework forced it and then never updated. It becomes a compliance artifact rather than an operational tool. Someone populates it for an audit, and a year or more later it still lists the same risks, long after the business has changed underneath it. A register nobody revisits isn't managing risk. It's decorating a folder.
Risk visibility stays siloed. When IT risk, vendor risk, and operational risk each live in a different spreadsheet owned by a different person, nobody has the full picture. Gaps hide in the seams between domains, and no single view surfaces them.
The posture is reactive, not proactive. Without continuous monitoring, you find out a control drifted when something breaks, not when it drifts. Manual review cadences (quarterly at best for most teams) leave long windows where your actual posture and your documented posture quietly diverge.
The math breaks before the headcount does. A team that reviewed 20 controls at 50 people cannot manually review 200 controls at 200 people. The risk register that worked as an annual Excel exercise at seed stage collapses under its own weight as the attack surface expands.
What can realistically be automated and what cannot
The line between what automation handles well and where it quietly misleads is not subtle once you see it. Most implementations blur it anyway. Automation reduces toil in specific areas. Applied without judgment thresholds, it produces false scores and false assurance. Getting this boundary right is the difference between a program that scales and one that generates a green dashboard nobody should trust.
What automation handles well
Automation is strongest wherever the work is repeatable, high-volume, and integration-driven.
- Evidence collection, aggregation, and routine reporting. The work that used to mean chasing screenshots across Slack threads and assembling status decks by hand. This is what GRC automation handles well at its core: pulling timestamped, auditor-ready evidence without a human touching a screenshot.
- Vulnerability scanning and control monitoring. Standardized output, continuous execution, and clean integration with SIEM and CSPM tooling make this a natural fit.
- Vendor risk scoring against predefined criteria. Automation can score third parties consistently, though the criteria themselves and the edge cases need periodic human validation.
- Continuous monitoring and alerting on control drift. A misconfiguration that appears on a Tuesday does not wait for your Friday review. Continuous monitoring catches it Tuesday, which is the difference between a quick fix and a finding in your next audit.
- Surfacing high-confidence critical signals for human review. The point isn't to score everything. It's to flag the items that clearly warrant a human's attention so the human keeps the authority to decide.
Where human judgment cannot be replaced
Everything above surfaces signals. The decisions belong to people.
- Setting risk appetite and tolerance thresholds. These require board and executive ownership. A platform cannot decide how much reputational or regulatory risk your leadership is willing to carry. See risk appetite and tolerance for why this is a leadership decision, not a configuration setting.
- Risk acceptance decisions, especially where business priorities conflict with security recommendations. When the business is comfortable accepting a risk the security function is not, that conversation has to happen between accountable humans. These decisions are not configuration settings. They are commitments.
- Final risk scoring for high-impact items. Automation should surface the signal. A human should validate the score. Handing the final call on a critical risk to a scoring model is how you end up defending a number nobody in the room actually stands behind.
- Risk register curation. Deciding what belongs on the register versus what belongs in a vulnerability management pipeline or a Jira board is a human triage act. Automation can suggest; a person must confirm.
- Communicating risk posture to boards and non-technical stakeholders. Narrative, context, and accountability are irreducibly human.
GRC task automation potential and human boundary analysis
For the tooling side of putting this into production, a risk management platform should make the automatable work disappear while leaving the judgment calls exactly where they belong: with your team.
Advantages of automating risk management
Once you know what to automate, the benefits follow naturally from targeting the right work.
Efficiency and accuracy. Manual evidence collection introduces two costs: time and error.
Automation removes both, streamlining data collection and assessment while stripping out the human mistakes and inconsistencies that creep into spreadsheet-driven processes.
Real-time risk assessment. The gap between when a control drifts and when you find out about it is where real exposure lives. Automated systems close that gap, flagging misconfigurations in hours rather than at the next quarterly review.
Scalability. Automation absorbs the growth in tools, people, and integrations that would otherwise force you to re-platform your process every time you double in size. The math breaks before the headcount does, and automation is what keeps the math from breaking.
Resource optimization. When automation handles evidence collection, your security lead stops chasing screenshots. That time goes to the decisions that actually require their judgment.
Audit defensibility. When an auditor asks for six months of control history, you either have it or you scramble. Automated evidence collection means you have it timestamped, organized, and ready without a last-minute sprint.
Better risk prioritization. Automation surfaces the highest-confidence critical signals so teams focus there, instead of managing a flat list where everything looks equally urgent. For a fuller picture of where the returns land, see ROI from a GRC platform.
Steps to automate the risk management process
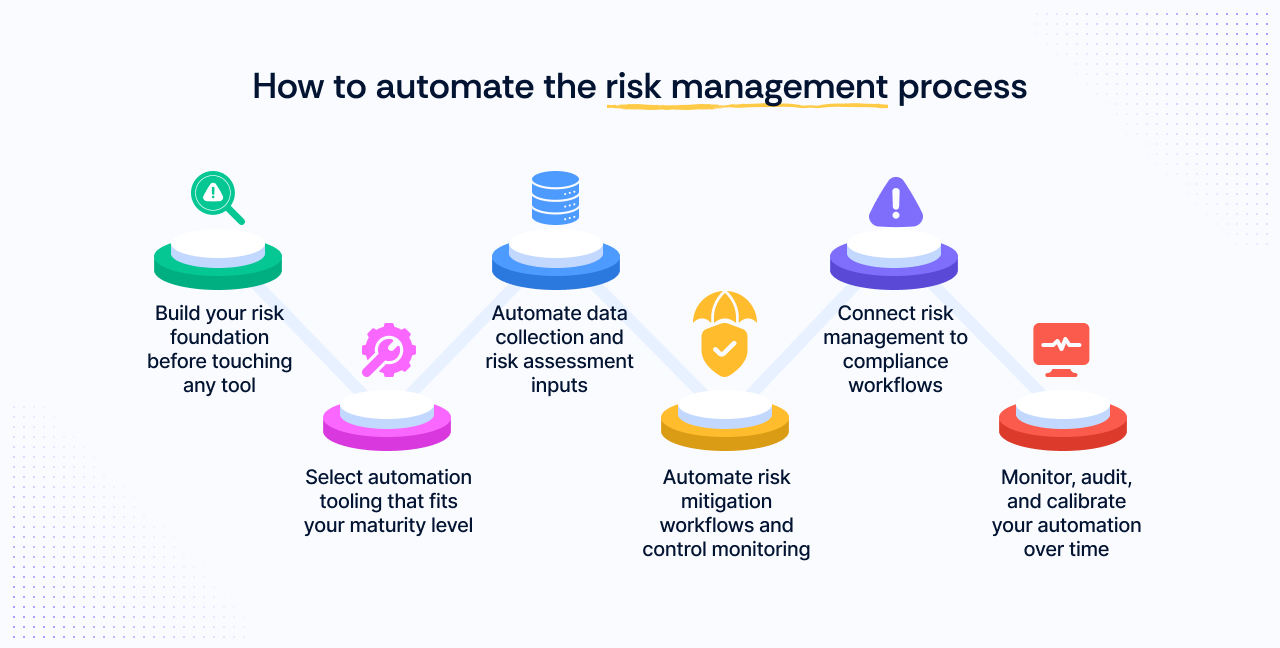
The path from manual to automated is six operational steps. Each one has work to do, work to hand off, and work to keep firmly in human hands.
Step 1: Build your risk foundation before touching any tool
Define your risk policies by naming the categories of risk your business actually faces (operational/vendor/infrastructure) and assigning a named owner to each. Complete an asset inventory that covers your cloud environment, identity providers, and any third-party integrations that touch sensitive data. Establish your risk tolerance by getting explicit agreement from leadership on what level of exposure is acceptable before you start scoring anything.
Most companies begin risk management because compliance forced them to, which means the foundation often gets skipped.
What stays human here is all of it: automation has nothing to automate until the policies, ownership, and tolerance are set. When you're ready, build your risk register around a focused set of strategic risks rather than every finding you can name.
Step 2: Select automation tooling that fits your maturity level
The tooling a 50-person company needs is not the tooling a 500-person enterprise needs. Early-stage teams want a template and a place to put risks; mature teams want deep integration with existing registers and tooling. Evaluate against your actual stage, not the feature list.
Automate the evaluation of integration coverage: does the tool actually connect to your AWS org, your Okta, your GitHub? But keep the strategic fit decision with the person who owns the program. Get the risk management software selection right and you avoid re-platforming later; get it wrong and you inherit a tool that fights your workflow.
Step 3: Automate data collection and risk assessment inputs
Automation earns its budget here. Connect your cloud platforms, identity providers, MDM, HRIS, and ticketing systems so evidence flows in without manual chasing. AWS, GCP, Okta, and Jira are the integrations that matter most for most teams.
Layer in vulnerability scanning and threat intelligence feeds so the assessment inputs stay current. The integration layer is the foundation everything else runs on. If it only covers two of your eight cloud environments, your posture data is fiction. See how automated evidence collection works in practice to get the coverage right the first time.
Step 4: Automate risk mitigation workflows and control monitoring
Set up automated security controls and, critically, continuous control monitoring that alerts on drift the moment a configuration changes. Automate the detection and the alerting; automate the routine remediation workflows where the response is deterministic.
What stays human is the judgment on anything ambiguous. Automated incident response is fine for revoking a stale credential, but a human decides how to handle a novel threat.
Step 5: Connect risk management to compliance workflows
Most compliance frameworks share at least 40 to 50% of their underlying controls, a figure that varies by framework pair. Evidence you collect for SOC 2 can satisfy ISO 27001 requirements you have not yet mapped, if your platform connects them. Tie your risk controls explicitly to framework requirements so a single control satisfies multiple obligations.
Are you running separate evidence projects for each framework? That's the problem this step fixes. Ground this in compliance risk management so the mapping reflects real regulatory obligations, not a checklist.
Step 6: Monitor, audit, and calibrate your automation over time
Establish KPIs, review your automated processes regularly, and recalibrate your scoring models as the threat landscape and business environment shift. Automate the monitoring and the KPI collection; keep the human oversight that validates whether the automation is still measuring the right things.
This is the move from point-in-time snapshots to continuous risk management, and it's the step teams most often skip. Automation is not a set-and-forget system. It is a living program that needs a human to validate it is still measuring the right things.
How to choose risk management automation software
The most useful lens for selection is organizational maturity, not feature count. A 50-person SaaS company wants a template and a place to start; a 500-person enterprise wants deep integration with existing tooling and registers. The right criteria shift accordingly.
Critical evaluation criteria for GRC platform selection
The three criteria most buyers overlook are multi-framework control mapping, auditor-friendly evidence packaging, and integration depth with cloud-native environments (AWS, GCP, Okta, GitHub). These are exactly the capabilities that separate a tool that saves your team time from one that adds another dashboard to watch.
Questions to ask any vendor before you commit:
- When an integration breaks, how do we find out, and how fast do you fix it?
- Does the platform actually collect evidence and monitor controls, or does it hand us a nicer checklist we still fill in manually?
- Can our own engineer own this day-to-day, or are we dependent on your support team?
- How do you handle multi-framework overlap? Do we solve a control once and reuse it, or re-do the work per framework?
- What does time-to-first-value look like, realistically, for a company our size?
For a broader take on the category, see choosing GRC software. If you want to see these criteria applied in practice, Scrut's risk management platform maps directly to each one.
The human element: What automation cannot replace in risk management
Here is the core insight practitioners keep returning to: automation surfaces signals; humans make decisions. That's not a limitation of automation. It's an intentional design principle for any well-run risk program. As Jason Leuenberger, Founder, Kinkou, LLC, put it, “Frameworks are crunchy: controls, matrices, checklists. The part that actually determines whether risk gets managed is squishy, and it's human.”
Who owns final risk scoring and acceptance. Automation should flag the high-impact items. A named human should validate them. The failure mode is a program where scoring is technically automated but no accountable human validates the high-impact items. When that happens, nobody can explain a score to leadership or an auditor, and the program loses credibility at exactly the moment it needs it most. Risk acceptance decisions are the sharpest example: the business is often comfortable with a risk the security function isn't.
Documenting risk acceptance when priorities conflict. This is where the "musical chairs" dynamic shows up. When a risky decision needs sign-off, everyone points at "the business" as the one who insisted, but nobody wants to be the business.
A good process forces the question: who specifically is accepting this risk, and on what basis? Then it documents that person, that reasoning, and that date. Without a named accountable owner, risk acceptance is just diffusion of responsibility.
Board reporting is a product, not a template. Every board cares about different things. Treat board reporting like a product: communicating risk to the board means shipping a version, collecting feedback, and iterating until the format actually lands with your specific audience, not drowning them in technical detail they can't use.
Keeping the register from becoming a security Jira board. Registers bloat when people use them as a backdoor escalation path: "if I get this vulnerability onto the risk register, people will finally take it seriously." That's how a register grows to 200 entries nobody reads.
The risk register is not your vulnerability management pipeline. Operational findings belong in a ticketing system; the register stays reserved for genuine strategic risks. This is a core part of the human element in compliance: the judgment about what matters cannot be automated away.
Key challenges in risk management automation
Automation is worth adopting, but a realistic picture of what can go wrong builds a stronger program than a sales pitch does.
Data quality and coverage gaps. Automation distorts your risk posture when it pulls from only one or two integrations instead of the full environment. A well-connected integration layer is a prerequisite, not an enhancement. If the tool sees two of your eight cloud environments, your posture data is fiction dressed up as fact.
Risk register bloat. Without deliberate curation, registers grow to 200-plus entries and become compliance artifacts nobody reads, too many even for a large public company. The fix is a defined escalation path that keeps operational findings (vulnerabilities, Jira tickets) separate from strategic risks. Understanding inherent vs residual risk helps here, because it forces the question of what actually belongs on a strategic register versus what's already controlled.
False confidence from dashboard green states. A passing dashboard reflects that controls were in place during the observation window. It does not guarantee your current security posture. Boards that see green stop asking questions, and security quietly gets under-resourced between audit cycles.
Automation without ownership. A control that's technically automated still needs a named human owner who understands what it does and can explain it to an auditor. "The platform was green" is not an answer when someone asks who validated the control.
Calibration lag. Scoring criteria set at implementation and never touched again is the norm, not the exception. Automation is supposed to be the thing you don't revisit, which is exactly why it goes stale. As the threat landscape and business change, stale scoring criteria produce stale risk rankings. Reviewing calibration is the step that separates a living program from a decorative one, and it's one of the common compliance mistakes that quietly erodes a program over time.
Risk management automation for SMBs versus enterprises
The failure modes above are not equally likely at every stage. The same automation tools serve different purposes at different maturity levels, and the risks of over-engineering or under-investing shift depending on where your organization sits.
Early-stage (under 100 people). This is minimum viable risk management. Start with a focused register of 15 to 25 high-impact risks, use automation to collect evidence and monitor a small control set, and prioritize getting the right people into the review cadence over sophistication of tooling.
The whole exercise is really about getting the right folks in the room, applying a consistent methodology, and producing an artifact with clear ownership and a review cadence. A textbook multi-year RMF rollout compresses down to that.
Mid-market (100 to 500 people). Automation handles evidence collection and control monitoring. Risk scoring stays partly manual for high-impact items. The register is owned by the security or GRC function, with a quarterly review cadence and monthly attention on high-risk items.
Enterprise (500-plus people). Risk domains often separate by function: IT risk, operational risk, financial risk, each owned by a different leader and rolling up under a different charter. Integration depth matters, continuous monitoring is non-negotiable, and board-level risk reporting becomes a formal, recurring deliverable.
GRC lifecycle scaling: Risk register sizing, automation, and governance
For growing companies, the GRC implementation for growing companies roadmap maps this progression in detail. If you're scaling, compliance for growth-stage companies and enterprise risk management speak to the two ends of this arc.
Conclusion
Automation works best when it's pointed at the high-volume, repeatable tasks: evidence collection, continuous monitoring, vendor scoring, and kept away from the decision points that need a human. The teams that get this right treat automation as leverage, not as a replacement for judgment.
Three takeaways to act on:
- Automate the toil: evidence, monitoring, reporting, and keep risk acceptance, appetite setting, and final scoring on high-impact items firmly human.
- Keep your register lean and strategic. It's not a security Jira board, and a register nobody revisits manages nothing.
- Match your automation to your maturity stage. Over-engineering at 50 people wastes effort; under-investing at 500 creates real exposure.
Book a demo to see how Scrut automates risk management.
The core components are risk identification, assessment, analysis, mitigation, monitoring, communication, and reporting. Automation carries the repeatable parts: identification, monitoring, and reporting, while analysis, communication, and the judgment inside assessment stay human.
Automation improves efficiency and accuracy, enables real-time assessment, scales without re-platforming, and optimizes your team's time. Two advantages competitors often miss: audit defensibility, because automated evidence creates a timestamped, auditor-ready trail, and better prioritization, because automation surfaces high-confidence critical signals instead of a flat list.
Data collection, vulnerability scanning, control monitoring, vendor risk scoring, and evidence aggregation: these belong to automation. Risk acceptance decisions, risk appetite setting, and high-impact risk scoring require a human.
Risk management automation identifies, scores, and monitors risks across the whole organization. Compliance automation gathers evidence and demonstrates adherence to specific frameworks like SOC 2 or ISO 27001. The two overlap heavily: compliance automation is effectively one part of a broader risk program, but risk management has a wider scope covering operational and strategic risks beyond regulation.
Start with 15 to 25 high-impact, strategically relevant risks, not every vulnerability or finding. Assign a named owner to each. Use your automation platform to flag signals that may warrant new entries, but keep human authority over what enters the register. Review it at least quarterly and do a full top-to-bottom update annually.