

The Compliance Theater Reckoning: Shortcuts That Cost You Later
What makes a claim on a trust page defensible rather than compliance theater?
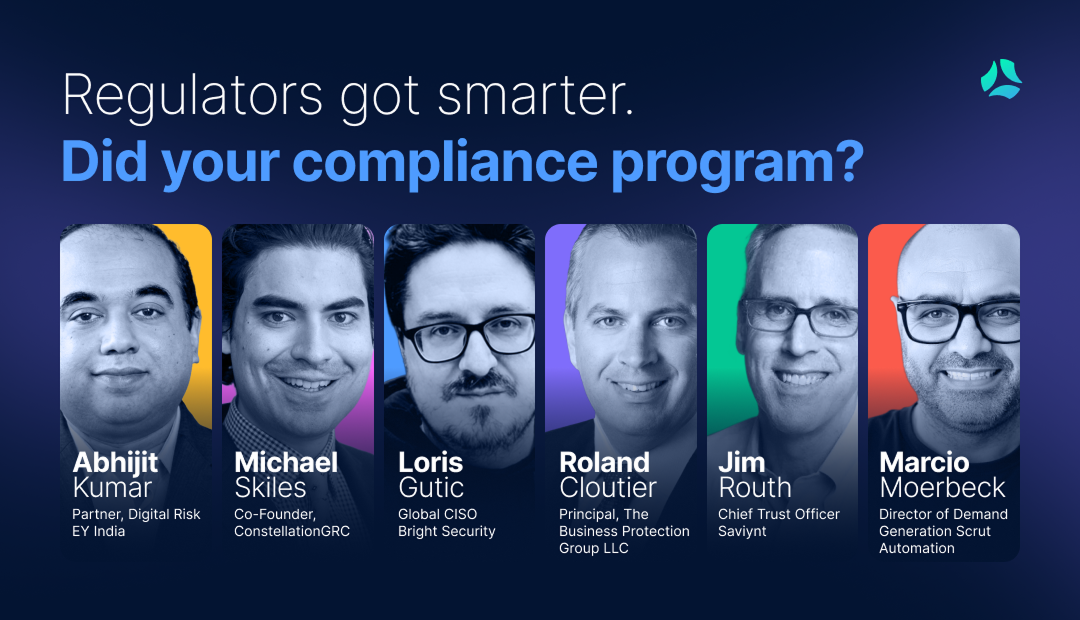
Watch security and GRC leaders help you judge where program drift happens, which shortcuts are reasonable, which business and AI changes should trigger another review, and how to disclose open gaps or unfinished work accurately to customers and auditors.
Watch the recording and get the Compliance Gap Assessment Workbook, 30-day Compliance Starter Plan, and Business Impact of Compliance Automation Report 2026 for free.
Get instant access
What you’ll take away
- How to tell whether last year’s controls, evidence, and scope still reflect how the business operates today
- Which changes, from new control owners and production environments to AI workflows and integrations, should trigger another review
- What to verify before relying on automated evidence, integrations, or an all-green readiness view
- How to keep customer answers and trust-page claims tied to current evidence, accountable owners, and clear review triggers
- Where reasonable shortcuts can save work without turning planned, assumed, or outdated activity into something the business cannot defend
Who should watch
- GRC and compliance teams responsible for controls, evidence, and audit readiness
- Security teams assessing how business and technology changes affect risk
- Company leaders accountable for the claims made to customers, auditors, and partners
- Engineering teams whose systems, integrations, and AI workflows support those claims
- Teams preparing for a renewal audit, enterprise security review, or closer scrutiny of their trust-page claims
Meet our panel
Mackenzie Thomas is a GRC expert specializing in controls, risk management, and assessment readiness. Her expertise spans SOC 2, HIPAA, and HITRUST, helping organizations build control environments that can stand up to scrutiny and support credible compliance claims.
Michael Argast is a cybersecurity leader with 20+ years of experience designing and running security programs for cloud-focused organizations. His expertise spans security strategy, cloud security, risk, SOC 2, ISO 27001, and NIST, with a focus on building credible, scalable security programs.
Marcio Moerbeck is an award-winning technology marketing leader with 25+ years of experience across demand generation, digital growth, and partner marketing. He has built global programs generating hundreds of millions in pipeline and revenue while leading multi-market teams.
What you’ll take away
- How to tell whether last year’s controls, evidence, and scope still reflect how the business operates today
- Which changes, from new control owners and production environments to AI workflows and integrations, should trigger another review
- What to verify before relying on automated evidence, integrations, or an all-green readiness view
- How to keep customer answers and trust-page claims tied to current evidence, accountable owners, and clear review triggers
- Where reasonable shortcuts can save work without turning planned, assumed, or outdated activity into something the business cannot defend
Who should watch
- GRC and compliance teams responsible for controls, evidence, and audit readiness
- Security teams assessing how business and technology changes affect risk
- Company leaders accountable for the claims made to customers, auditors, and partners
- Engineering teams whose systems, integrations, and AI workflows support those claims
- Teams preparing for a renewal audit, enterprise security review, or closer scrutiny of their trust-page claims