


- Risk mitigation strategies reduce the likelihood or impact of threats before they disrupt operations, compromise data, or trigger compliance failures.
- The five core approaches are avoidance, reduction, transfer, acceptance, and monitoring, each suited to a different risk level and business context.
- Effective mitigation follows a structured process: identify, assess, prioritize, treat, then monitor continuously.
- Compliance risk (failing an audit) is not the same as operational or strategic risk, and conflating them leaves dangerous gaps.
- A well-maintained risk register, with named owners and a quarterly review cadence, is the operational backbone of any mitigation program.
Most risk mitigation strategies fail not because the framework was wrong, but because the risk register became a compliance artifact nobody opened again. If you are a GRC manager, a security manager, a CTO, or a VP of engineering, you already know the gap: documenting a risk and actually managing it are two different jobs.
This guide is about the second one. It covers the five core strategies, how to build a plan that survives contact with a real business, and why treating a passed audit as a finished risk program leaves the exact gaps that end up hurting your organization.
What is risk mitigation?
Risk mitigation is the process of identifying threats, assessing their likelihood and impact, and applying controls to reduce them to an acceptable level. It sits downstream of risk assessment: you mitigate against a prioritized list of risks, not against a blank page. Its goal is to bring exposure down to a level the business can live with, not eliminate it entirely.
Two terms every GRC manager uses daily anchor this work. Inherent risk is your raw exposure before any controls exist; it’s the ceiling. Residual risk is what remains after controls are applied, the number you are actually carrying. The distinction matters because most programs skip inherent risk or quietly conflate the two, and then never update residual risk when a control lapses.
Effective mitigation is the discipline of moving from the first number toward the second, and keeping that second number honest. The point is not to score every risk, but to surface what is genuinely critical so leadership can make an informed call.
Note: Risk tolerance vs. risk appetite are the thresholds that determine which mitigation strategy applies to a given risk, and appetite should be tied to specific business commitments, not generic boilerplate. For the underlying measurement distinction, see inherent risk vs. residual risk.
Types of risk organizations face
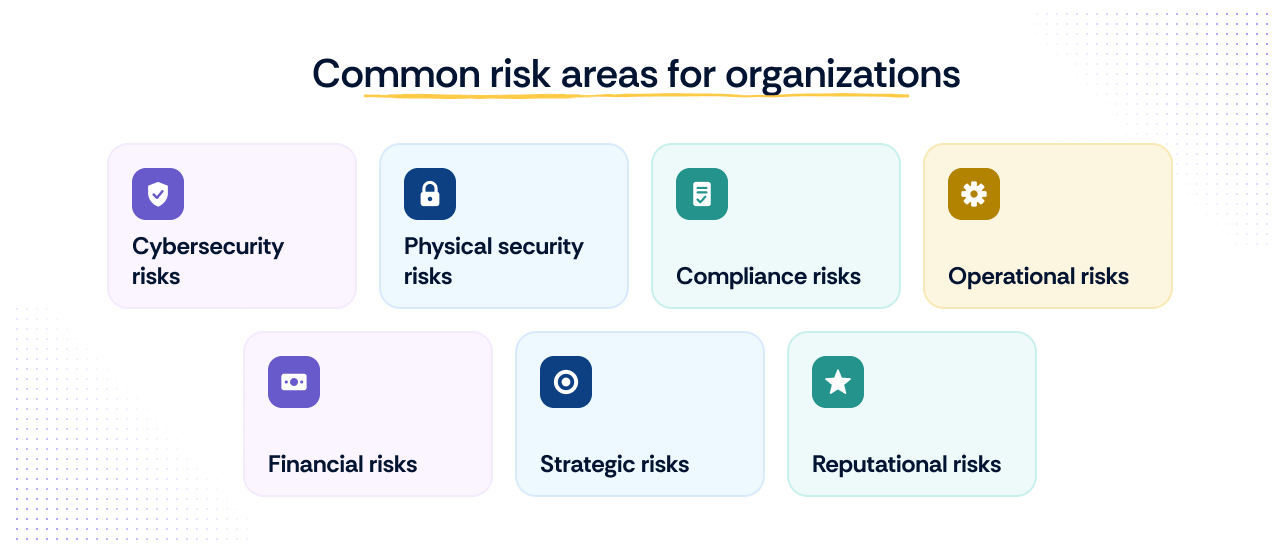
Security teams tend to catalog cybersecurity and physical risks well and stop there. That is the gap. A company can pass every technical control and still be blindsided by a risk that never appears in a vulnerability scan. Below are the risk types a mature program tracks.
Cybersecurity risks
Threats and vulnerabilities in the digital realm, including data breaches (unauthorized access to sensitive information), malware, phishing, distributed denial of service (DDoS) attacks, and insider threats.
Physical security risks
Threats to physical assets and infrastructure: theft and burglary, vandalism, natural disasters like earthquakes and floods, unauthorized access through tailgating or lock picking, and social engineering.
Compliance risks
The risk of failing an audit, incurring a regulatory penalty, or losing a license. This is real and tangible because there is usually an audit happening and a customer asking for the report. The danger is that it feels so urgent it crowds out everything else.
Example: a SaaS company misses a SOC 2 control and a stalled enterprise deal follows.
Operational risk
Process failures, key-person dependency, and supply chain disruption. These are the risks most likely to fall outside a compliance framework's scope. A company that needs to start doing business in a new country can face trickle-down effects on where data must be stored and whether existing controls even work there.
Example: a contact center that a whole product line depends on loses critical staff during a hiring crunch.
Strategic risk
Market decisions, competitive shifts, and business model changes. A company moving from B2B to B2C would have to rethink an enormous amount of its risk posture, because almost everything downstream changes.
Financial risk
Budget exposure and forex-rate changes that hit your controls budget. Your technology stack has nothing to do with it. Your controls budget does. If you buy security tooling in USD but hold another currency, an unpredictable swing in exchange rates directly changes what you can afford to protect, and that has nothing to do with your IT.
Reputational risk
Erosion of customer and stakeholder trust after an incident, a breach, or a public compliance failure. It rarely sits in a single owner's lap, which is exactly why it gets missed.
Why conflating compliance risk with your whole risk picture is dangerous
When you focus only on the risk of failing an audit, you optimize for shiny evidence and artifacts. But every hour an engineer spends chasing audit evidence is an hour not spent making sure backups work, permissions are correct, or the CI/CD pipeline is monitored. The operational and strategic risks feel far away and abstract, until they are not.
A SOC 2-compliant company can still face severe operational risk from key-person dependency, supply chain concentration, or geographic regulatory exposure that no control checklist captures. Producing evidence for an audit does not mean you are doing those things well.
See our guides on compliance risk management, the operational risk guide, and cloud risk management.
How to conduct a risk assessment before selecting a mitigation strategy
A risk assessment is a structured process for identifying, evaluating, and prioritizing risks. It produces the artifact that everything else depends on: the risk register. Here are the steps.
Step 0: Define your risk appetite
Before assessment begins, leadership has to set the threshold for how much risk the business is willing to accept in pursuit of its objectives. This belongs with executives and the board, not the security team. Without it, the team has nothing to prioritize against and ends up setting guardrails based on its own interpretation of what secure means.
Risk appetite is a leadership conversation because every growth decision carries risk, and if nobody has explicitly said how much is acceptable, security operates in a vacuum. Tie it to specific commitments, not a generic line like “we have a low risk appetite.”
Step 1: Identify assets
List every asset, physical and digital, that is critical to the organization: data, systems, infrastructure, people, and facilities. For a 100-person SaaS company this means the production database, the customer PII it holds, the cloud accounts, the source repositories, and the SaaS tools that touch sensitive data.
The exercise fails when it is done in a silo. Getting the right people in the room matters more than the methodology, because one person rarely understands how the whole company works across engineering, operations, and back office. A pen-testing team's findings that never reach the broader business is the classic failure mode here. Involve the people who actually know where the data lives, or you will assess an incomplete picture.
Step 2: Identify threats
For each asset, identify what could harm it. Threats fall into natural (earthquakes, floods), human (theft, insider action), and technological (malware, misconfiguration) categories, but the useful version goes further. Think about which threats are actually relevant to your business context and industry, not a generic list copied from a template.
A fintech faces transactional fraud that a horizontal SaaS company never sees. The threat landscape changes fast, so this is not a once-a-year exercise you file and forget. When a breach hits a company similar to yours, revisit whether you are exposed to the same thing.
Step 3: Assess vulnerabilities
Determine the weaknesses that make each asset susceptible to those threats. Vulnerabilities are technical (outdated software, misconfigured cloud storage, missing MFA) and procedural (no access-control process, no offboarding checklist, no documented owner for a control).
The procedural ones are easy to miss because they do not show up in a scanner. A control that exists on paper but that nobody actually owns or operates is a procedural vulnerability, and it is where a lot of programs quietly fail. Ask how many people are responsible for implementing a given control and how much time they actually spend on it. Often, the honest answer is that no one is sure.
Step 4: Calculate risk levels
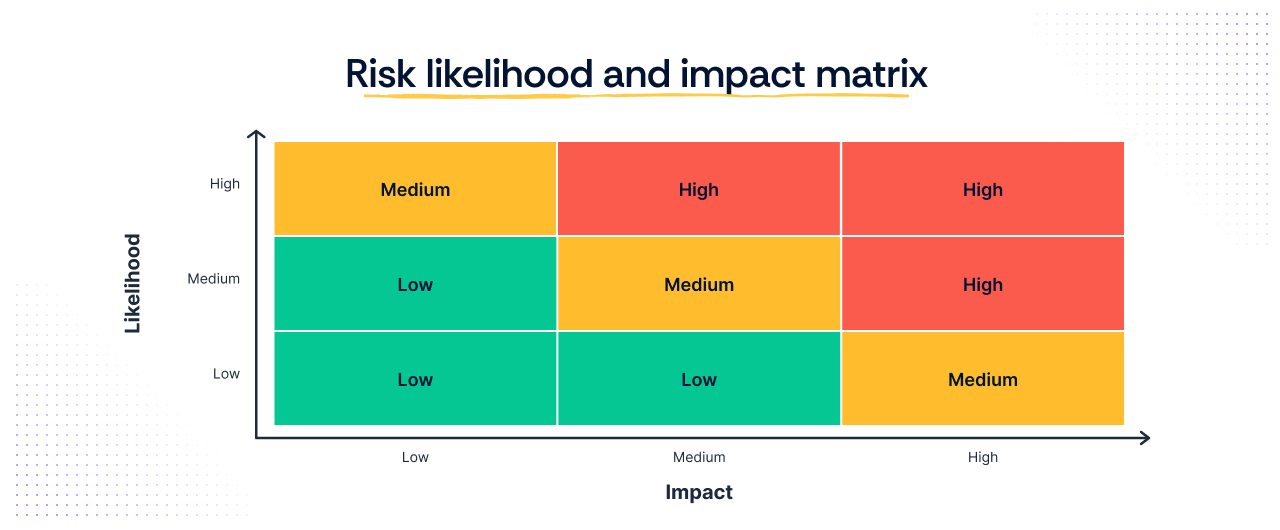
Assess the likelihood of each threat and its potential impact, then combine them.
Risk = Likelihood × Impact
Assign levels (low, medium, high) based on the score. On method: for 50-to-200-person companies, a well-maintained qualitative heat map is the most commonly used approach and usually produces more actionable output than a Monte Carlo simulation built on uncertain inputs. Quantitative methods like FAIR or Monte Carlo add value only when you have sufficient data inputs and the decisions you would make would actually change as a result.
The test is simple: if running the more rigorous analysis will not change what you do, do not run it. The mechanics are in mastering quantitative risk assessment.
The risk register as the output
The assessment produces the risk register, and a good register is not an exhaustive list. It captures the most strategically impactful risks, each with a named accountable owner and an evidentiary trail for why it is there and when it will be reviewed.
A register where everything is a “strategic risk” means nothing is. Keep it as big as you are actually willing to care about. See how to create a risk register and our guide to IT and cyber risk assessment.
How often should you update your risk register?
At a minimum, once a year for a full top-to-bottom review. Quarterly check-ins are best practice: ask whether enough has changed in the business to revisit anything. Then run out-of-cycle updates whenever the business changes materially: a new geography, a new product line, or a shift from B2B to B2C. For a relatively stable business, twice a year may be enough. The cadence matters less than the honesty of the question you ask each time.
The five core risk mitigation strategies
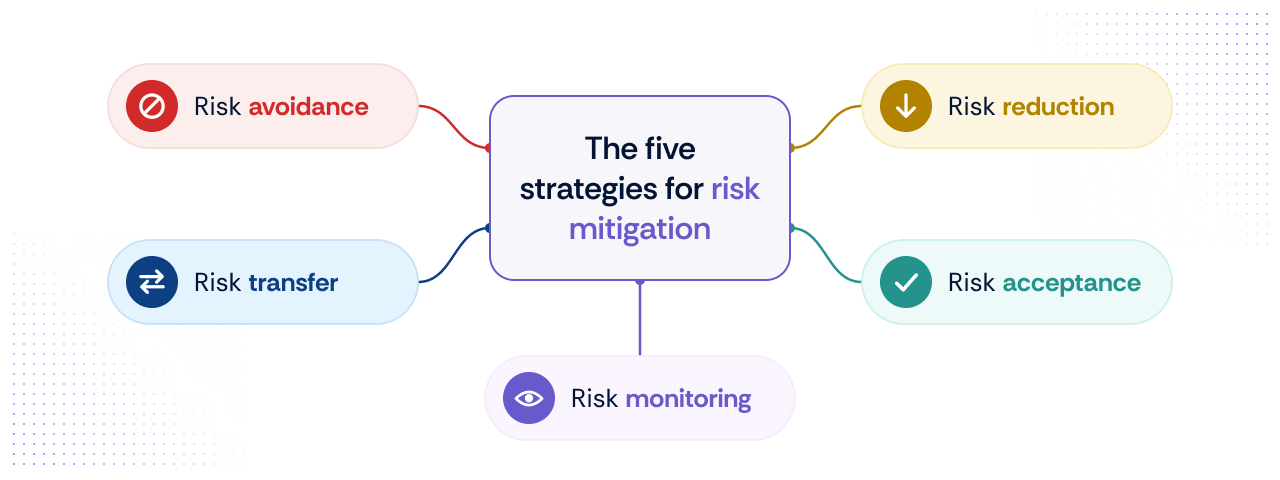
Once risks are assessed and prioritized, you choose how to treat each one. The first four approaches map directly to the ISO 31000 treatment options GRC managers recognize from frameworks. The fifth, monitoring, is a separate step in the ISO 31000 process, but it is what keeps the other four working.
1. Risk avoidance
Eliminate the risk entirely by not engaging in the activity that creates it. This is used when the potential impact is too high to justify exposure.
Example: avoiding non-compliant vendors to eliminate regulatory and security risk.
2. Risk reduction
Minimize the likelihood or impact using controls and mitigation techniques. The most common approach in cybersecurity and compliance.
Example: enabling multi-factor authentication to reduce unauthorized access.
3. Risk transfer
Shift responsibility to a third party through contracts, outsourcing, or insurance.
Example: purchasing cyber insurance to transfer the financial impact of a data breach.
4. Risk acceptance
Risk acceptance is the strategy most likely to cause a fight. The business wants to accept, but security is uncomfortable. That tension is normal, and it happens every day. The path through it is documentation, not resistance.
5. Risk monitoring
Track each risk and the controls applied to it over time, so you know when exposure changes. Monitoring keeps the other four strategies honest. A reduced risk can creep back up when a control lapses, an accepted risk can outgrow your appetite, and a transferred risk depends on a vendor or insurer whose terms can change.
Example: setting key risk indicators (KRIs) for a critical vendor and reviewing them quarterly, so a change in its security posture triggers a reassessment before it surfaces as an incident.
Combining strategies
Organizations rarely rely on one strategy per risk. You layer them: reduce likelihood with controls, transfer residual financial exposure through cyber insurance, and accept minor operational risks that sit below your appetite threshold.
The right combination is proportionate to the risk, and prescriptive standards like PCI DSS work well precisely because they make that layering concrete. Accepting a risk does not mean removing controls. It means deciding the remaining controls plus the residual exposure are an acceptable trade.
Risk acceptance: Documentation and escalation
The hardest conversations happen when the business insists on accepting a risk the security function finds uncomfortable. This happens every day, and businesses have to run. The path through it is not resistance; it is specificity.
Document exactly what is being accepted, in plain and practical language, including how big, how small, and how frequent the risk is. Name the person accepting it, and make sure they hold the appropriate authority.
A useful model here is matching risk-acceptance authority to your financial schedule of authorizations: if a director can approve a $50,000 purchase, a director can accept a $50,000-scale risk, and a larger exposure escalates to a VP or the board. Avoid letting “the business” become a faceless boogeyman, because when accountability is vague, everyone plays musical chairs and points at someone else.
Communicate the risk in language the specific decision-maker understands, since the same risk has to be framed differently for an engineer, a CFO, and a board member.
Set a review date. And document the controls that remain in place even under acceptance, because accepting a risk almost never means doing nothing about it. See risk avoidance vs. risk reduction and risk tolerance vs. risk appetite for more on risk management.
Risk mitigation vs. risk management
Think of risk management as the strategy layer and risk mitigation as the execution layer. Management surfaces what needs attention; mitigation is what you actually do about it. Neither works without the other. A sound management process with weak mitigation leaves risks identified but unaddressed, and strong mitigation techniques applied to the wrong risks is just well-executed guesswork.
Risk management includes activities such as risk identification, assessment, monitoring, and reporting. Risk mitigation applies specific techniques, avoidance, reduction, transfer, acceptance, or monitoring, to the risks that management surfaces. They depend on each other, and effective risk management means risks are not just identified but actively controlled. That only happens when strong mitigation strategies sit underneath a sound effective risk management process.
How to build a risk mitigation plan (step-by-step)
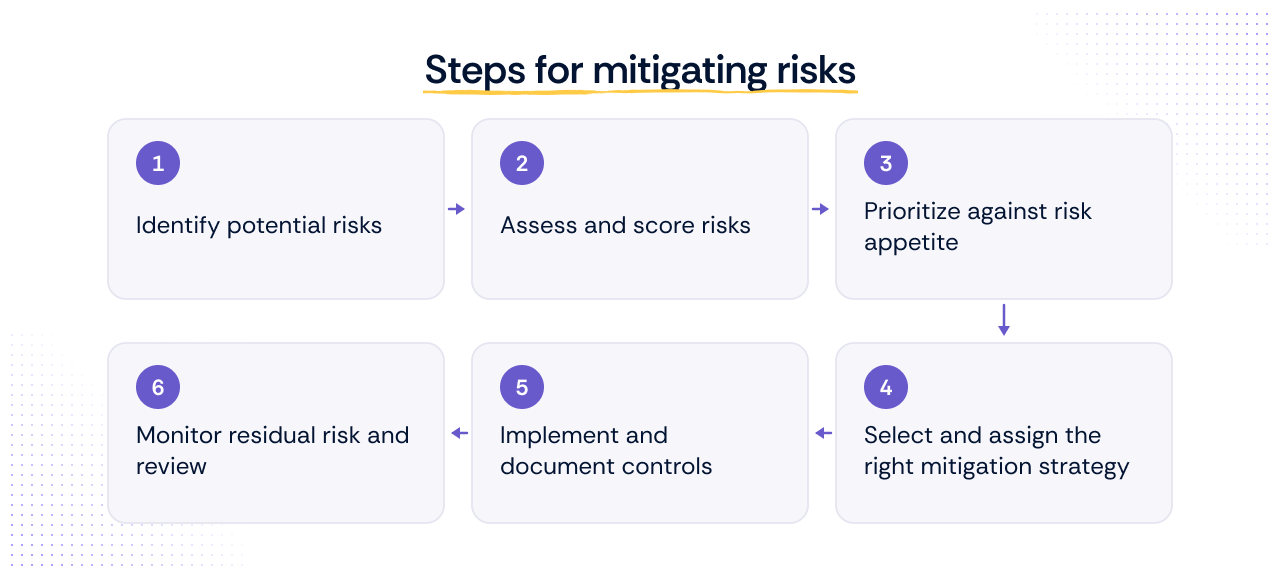
Here is the workflow. Six steps, each with a named owner and a common failure mode, because that is where most plans actually break down.
Step 1: Identify potential risks
Draw on the risk types from the section above and the assessment process that follows. The critical move is involving cross-functional stakeholders, not just security. The failure mode here is narrower than it looks: the person who identifies the risk rarely has full visibility into how it lands operationally, and the person who has to fix it rarely understands why it was flagged. That gap is where plans stall.
For an SMB, getting the right people in the room, someone who understands the technology, someone who understands operations, someone who understands the back office, is what makes the difference between a defensible risk picture and a guess. Engineers receiving only action items without seeing the overall picture means that they never understand how other teams are affected or why the risk matters.
Step 2: Assess and score risks
Score each risk using Likelihood × Impact. For most teams under 200 people, a qualitative heat map is the practical starting point and the most commonly used method. Reserve FAIR or Monte Carlo for organizations with mature data inputs where a quantitative result would genuinely change a decision.
The output is a ranked view of what threatens the business most, not a spreadsheet of everything that could theoretically go wrong. Do not push to be quantitative if you do not have the data to support it.
Step 3: Prioritize against risk appetite
Risk appetite, the board and leadership decision, sets the threshold. Residual risk must stay below it, or escalation triggers. A register with 200-plus entries where everything is labeled “strategic risk” is a triage failure: nothing is strategic if everything is. Even a multi-billion-dollar public company should keep its strategic register under a hundred entries. Keep it lean enough that people actually read it.
Step 4: Select and assign the right mitigation strategy
Apply the five-strategy framework, and assign a named risk owner to every item. A risk control matrix (RCM) belongs here too, mapping controls to risks. But a beautifully diagrammed RCM does not mean your company is safer. People are better at making documents than implementing them. Documentation does not equal implementation, so put the effort into operationalizing the matrix, not perfecting the picture.
Step 5: Implement and document controls
Distinguish between preventive controls (stop the bad thing), detective controls (catch it when it happens), and corrective controls (fix it after). Layer all three. Document every accepted risk with accountable sign-off, and record the controls that remain in place even under acceptance.
Step 6: Monitor residual risk and review
Residual risk has to be tracked, not assumed resolved once a control ships. Set a cadence: quarterly check-ins, an annual full review, and out-of-cycle updates when the business changes materially. This is where programs fail most often. After a control is implemented, organizations rarely go back to reassess whether residual risk actually dropped as expected, because there is always a new fire. Skipping that reassessment is the single most common gap in risk mitigation.
The handoff problem: From identification to remediation
The people who identify risks have broad visibility across functions. Remediation, though, flows down to operational teams, and that handoff is where things stall.
Use tools to keep it honest. Keep board-level, strategic items in the risk register, and push operational sub-items, CVEs, misconfigurations, patching queues, into a separate tracking system like Jira. The risk register is not a security Jira board.
Conflating the two produces a bloated register nobody reads and a vulnerability queue that never gets the attention it needs.
See risk management automation, the guide to risk control matrix, and automate risk management to dive deeper.
Security risk mitigation strategies and techniques
Every control in the previous section depends on a human to implement it, own it, and keep it honest. When those humans are not aligned, the controls become academic exercises. These techniques protect systems, data, and infrastructure from evolving cyber threats, organized here by control type: preventive, detective, and corrective.
A. Implementing layered security
Deploy multiple security layers such as firewalls, antivirus, and intrusion detection to build a robust defense.
- Defense in depth: A multi-layered approach spanning technology, policies, procedures, and personnel training. Zero trust architecture is the modern evolution of this idea, treating no user or system as inherently trusted.
- The weakest link principle: Identify and strengthen your most vulnerable elements, because security is only as strong as its weakest point.
B. Building access control
Control who can reach specific resources, systems, or data, across both physical and logical access.
- Authentication and authorization: Verify identity, then grant permissions based on role and responsibility. Update your MFA approach to current standards.
- Role-based access control (RBAC): Assign permissions by role, limiting access to what each job requires. User access reviews are the operational mechanism that keeps least-privilege access intact over time.
C. Applying encryption
Protect sensitive data so it stays unreadable to anyone without the right keys, whether it is stored or moving between systems.
- Data encryption: Encrypt data at rest, on devices, in databases, in cloud storage. If someone walks out with the drive, they walk out with ciphertext.
- Communication encryption: Encrypt data in transit with SSL/TLS. Any credential or customer record crossing an untrusted network without it is readable to anyone positioned between the two endpoints.
D. Enforcing security policies and procedures
Develop and enforce policies governing how security is maintained: acceptable use, incident response, and more.
- Developing effective policies: clear, comprehensive policies with defined expectations and consequences.
- Enforcement and training: consistent enforcement plus regular training on security best practices.
E. Executing monitoring and logging
Track system activity and surface potential incidents.
- Intrusion detection systems (IDS): Detect and alert on suspicious activity in real time.
- Security information and event management (SIEM): Aggregate and analyze security data across sources. SIEM is also what operationalizes the continuous monitoring requirement in frameworks like SOC 2 and ISO 27001, not a point-in-time check but an ongoing one.
Know what you have and be able to control changes to it before you buy more tooling. That principle holds across every stage. See security control types for how these map to a broader control taxonomy.
Conclusion
If you take three decisions away from this guide, make them these. First, decide where your compliance program ends and your real risk picture begins, because a passed audit does not cover operational, strategic, or financial risk, and treating it as if it does is how companies get blindsided.
Second, decide who actually owns each risk on your register, by name and at the right level of authority, because accountability that lives with "the business" lives with no one. Third, decide on a cadence for reassessing residual risk after controls ship, because that reassessment is the step almost everyone skips and the place programs quietly fail.
Risk mitigation is not about eliminating risk. It is about making conscious, documented choices at the right level of the organization. If you have an IP address, you have risk. The real question is whether you understand it well enough to manage it.
Ready to move from a static register to a living risk program? Explore the Scrut risk management platform, and if you are starting from scratch, begin with our guide on how to create a risk register.
The five main strategies are risk avoidance, risk reduction, risk transfer, risk acceptance, and risk monitoring. Each helps you manage a risk based on its likelihood and potential impact.
Security risk mitigation is the process of reducing cybersecurity risk by implementing controls such as access management, encryption, monitoring, and security policies to protect systems, data, and infrastructure.
Examples include enabling multi-factor authentication (MFA), avoiding high-risk vendors, purchasing cyber insurance, implementing layered security controls, enforcing access-control policies, and accepting a known residual risk with documented compensating controls and named executive sign-off.
Start by identifying potential risks with cross-functional input, then assess and score them by likelihood and impact. Prioritize against your risk appetite, select and assign the right mitigation strategy for each risk with a named owner, then implement and document controls. Finally, monitor residual risk and review on a set cadence, because tracking whether controls actually worked is where most plans fail
Tools that support risk mitigation include GRC platforms, SIEM systems, vulnerability scanning tools, intrusion detection systems, CSPM tools, and incident response solutions that help monitor, manage, and reduce risk.