



- A well-implemented GRC system replaces scattered evidence and reactive fire drills with continuous, audit-ready controls.
- GRC matters when customers ask for security proof, audits approach, or deals stall on security questionnaires.
- Governance sets the rules and accountability. Risk management identifies what could go wrong. Compliance proves your controls are working.
- GRC (governance, risk, and compliance) is an operating model that connects how you make decisions, what risks you manage, and how you prove compliance, in one continuous system.
- A GRC platform like Scrut can automate up to 70% of evidence collection, freeing your team from manual work.
GRC stands for governance, risk, and compliance: the three disciplines that determine how a company makes decisions, manages threats, and proves it meets the rules that apply to it.
The reason you are reading this is probably more specific than a definition. A deal is slowing down because of a security review.
A customer has sent a compliance questionnaire you cannot fully answer. Or an investor has asked about SOC 2, and you do not yet have a clear plan. These moments tend to arrive suddenly, but they are rarely isolated.
This page covers what GRC means, how the three components work together, why it matters, when you actually need it, and how to implement it without slowing down everything else you are building.
What is Governance, Risk, and Compliance (GRC)?
GRC stands for governance, risk, and compliance: the structured approach organizations use to align operations with business goals, manage threats, and meet regulatory requirements.
At its simplest, GRC is how a company defines the way it operates (governance), identifies what could go wrong (risk), and proves it is meeting the rules and standards that apply to it (compliance).
The term was popularized by the Open Compliance and Ethics Group (OCEG) as a way to describe these three disciplines working as one.
Every company, even a 10-person startup, already does some version of this. You have policies, even informal ones. You make decisions about which risks to accept. And you follow rules, whether that is a customer contract, a privacy law, or a security framework like SOC 2. GRC is what happens when you take those scattered efforts and turn them into a system, so you are managing all of them together instead of reacting to each one as it lands.
In the context of technology companies, GRC almost always refers to cybersecurity GRC: the governance, risk management, and compliance practices that protect digital systems and prove that protection to customers and regulators. When we work on cybersecurity GRC, we are talking about the controls, compliance frameworks, and evidence that show your digital environment is actually secure.
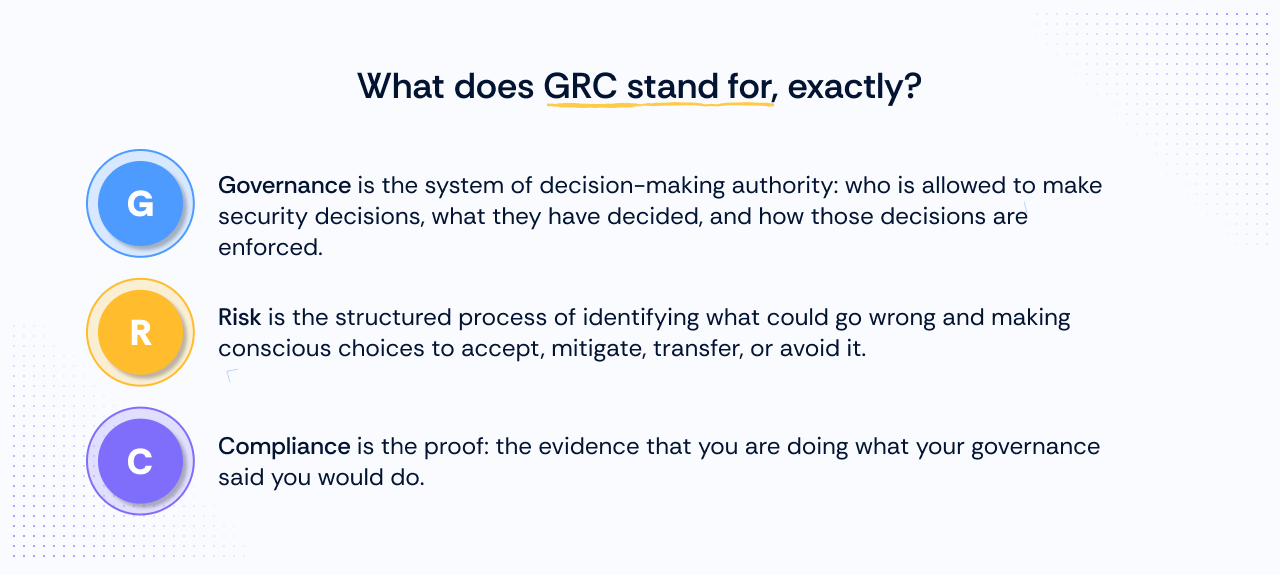
The three components of GRC: Governance, Risk, and Compliance
Each component answers a different question. Together, they form a continuous feedback loop: governance sets direction, risk shapes priorities, and compliance provides the proof and the correction signal.

GRC is built on three core components, each crucial to ensuring a well-structured and resilient organization. Each component answers a different question about how your company operates.
Governance
Governance answers the question: how do we make decisions, and who is responsible for what?
Governance is the set of policies, decision-making authority, and accountability structures that guide an organization toward its objectives. It is not just a stack of policy documents. It is the leadership layer that gives everything else legitimacy, by assigning who is authorized to decide and who is accountable for the outcome.
In practice, governance looks like a board-approved information security policy that names the CISO as the accountable owner for data protection, plus an executive risk committee that meets quarterly to review the threat landscape.
At an early stage it can be simpler: documented key policies and clear ownership. The point is that someone is accountable, and the decisions are written down.
Risk
Risk answers the question: what could go wrong, and how bad would it be?
Risk management is the structured process of identifying potential threats and deciding what to do about them. These threats may come from cybersecurity vulnerabilities, financial uncertainty, legal obligations, or operational gaps. A strong risk process produces decisions, not just lists of scary scenarios.
Risk management is not about eliminating every risk, which is impossible. It starts with inherent risk (the exposure before any controls exist) and works toward residual risk (what remains after controls are applied). The goal is to keep residual risk within the risk appetite the organization has defined, and to escalate when a risk crosses that line.
Compliance
Compliance answers the question: are we meeting the rules and standards we need to follow?
Compliance is the evidence. It is the proof that you actually enforced what your governance said you would enforce. It involves monitoring regulatory changes, running audits, and maintaining controls so you can demonstrate adherence to regulators, auditors, and customers.
Reaching the right standard is easier with compliance frameworks like SOC 2 and ISO 27001 mapped to the controls you already run.
How the three interact
The three do not run in a line, they run in a loop.
- Governance sets the direction: leadership decides to pursue SOC 2 and defines the risk appetite.
- Risk informs priorities: the risk assessment reveals that unauthorized access to production is the highest-priority threat, which decides where controls go first.
- Compliance provides the proof and the feedback: audit evidence reveals a gap, such as access reviews not happening quarterly, which feeds back into governance as a decision and into risk as an updated assessment.
The mistake that creates silos is treating these as three separate departments. In a tech-native company, they should be one muscle.
What is GRC in cybersecurity?
In cybersecurity, GRC is how you define, monitor, and enforce security controls across your systems. Governance sets direction through policies and accountable owners. Risk management identifies and prioritizes the threats that matter most to your environment.
Compliance produces the evidence that controls meet regulatory and customer expectations. In practice, cyber GRC connects what should happen in your systems with what is actually happening, so you can prove your security posture rather than just assert it.
The operating model of GRC
GRC is not just a set of policies or frameworks. In practice it works as a system that connects what you define to what actually happens in your environment. At the core, the flow is simple:
Controls → Signals → Evidence → Decisions
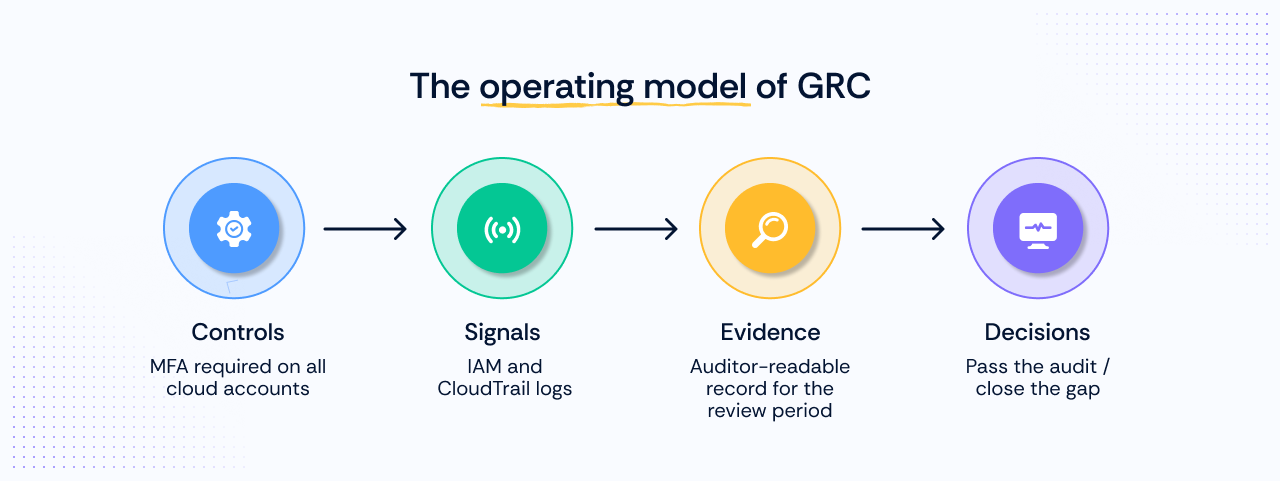
Controls define what should happen. A policy requiring MFA on all cloud accounts is a control. The intent is defined; what matters is whether it is enforced, not just documented.
Signals are the real-time data your systems generate: IAM authentication logs, CloudTrail activity, GitHub commit events.
They tell you whether the control is actually operating, moment to moment.
Evidence is the structured, auditor-readable record of those signals. It is the proof that the control worked during the period under review, not just that it was written down somewhere.
Decisions are what the evidence enables: passing an audit, identifying a gap before an auditor does, or triggering a corrective action.
This loop is what continuous monitoring and automated evidence collection are built to run. A GRC platform operationalizes this model, which we come back to later in this guide.
Why is GRC important for business today?
That threat environment is not abstract. The IBM Cost of a Data Breach Report 2026 puts the global average cost of each successful breach at $4.99M, a record high and a 12% jump over the prior year.
In response, governments are tightening cybersecurity expectations. Initiatives such as the EU's NIS2 Directive, Singapore's Operational Technology Cybersecurity Masterplan, and India's Digital Personal Data Protection Act (DPDPA) are all raising the bar for accountability and resilience.
Together, the threat volume, the cost, and the regulatory pressure are why "why is GRC important" has moved from a back-office question to a revenue question.
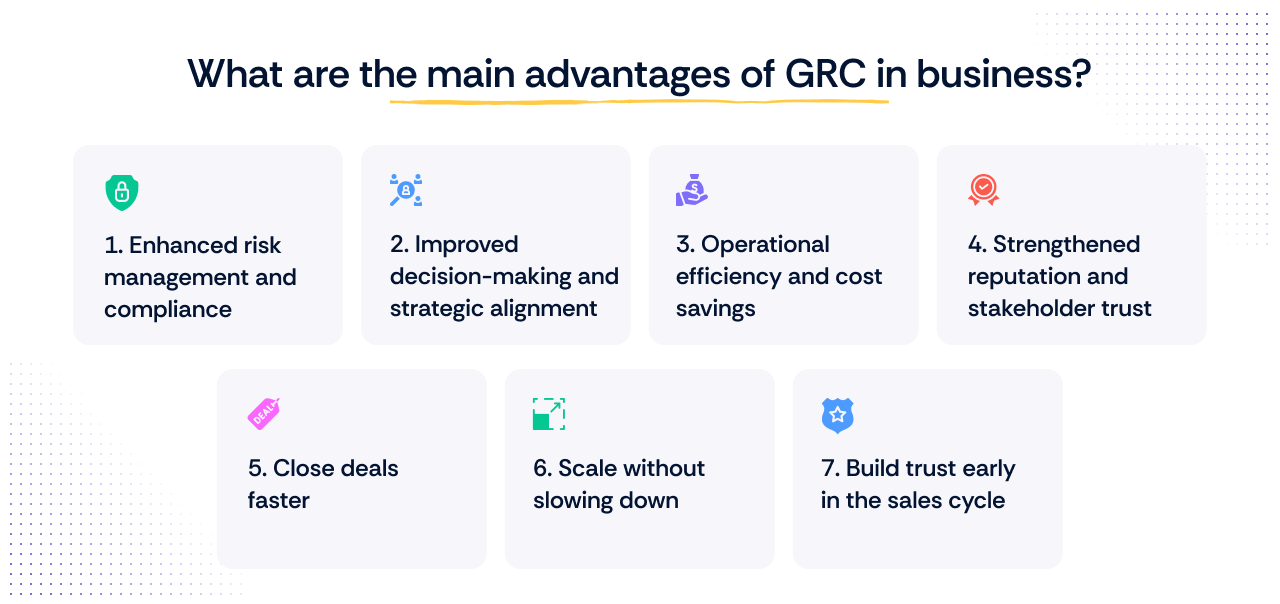
Here is what a working GRC program actually buys you.
- Enhanced risk management. A working GRC program helps you identify, assess, and mitigate risk before it becomes a breach or a penalty. Staying ahead of legal and security requirements reduces exposure to data breaches, fines, and reputational damage.
- Improved decision-making. With a centralized view of risks, gaps, and control performance, leadership makes data-driven decisions that align with long-term goals instead of reacting to the latest fire.
- In regulated markets, a documented GRC program is visible to the buyers and partners who vet you. That visibility is the reputation signal, not the certification itself.
Operational benefits for growing companies
- Close deals faster. When a customer asks for security proof or sends a questionnaire, a structured GRC system lets you respond quickly and confidently instead of stalling the sales cycle. Fewer deals die in security questionnaires.
- Scale without slowing down. As your customer base grows, so do compliance demands. A system-driven approach absorbs that growth without overloading your team or derailing engineering velocity.
- Build trust early. Clear evidence, consistent responses, and audit readiness signal maturity to prospects and move conversations forward that might otherwise stall.
Where this leads over time is GRC maturity: moving from reactive, ad hoc effort toward an integrated program that runs continuously. That is the trajectory the rest of this guide maps.
What GRC actually looks like in a startup
In a SaaS team of 10 to 15 people, GRC rarely starts as a structured program. It shows up as scattered work: policies written late at night from templates, engineers manually exporting logs from systems like AWS or GitHub without clear direction, and evidence spread across folders, screenshots, and spreadsheets with no audit-ready view.
It feels manageable at first. Then requirements grow, and you realize compliance is not about collecting documents, it is about consistently proving your systems work as expected.
Here is the difference a system makes.
Making that shift usually depends on compliance automation integrations that pull evidence from the stack you already run. For most teams, the realization is the same: the hardest part was not the tech. It was the documentation, the coordination, and the day-to-day discipline of keeping everything current.
Why GRC feels harder than it should
GRC does not usually fail for lack of intent. It fails because the reality of implementation does not match what the process looked like on paper.
The biggest expectation gap is automation. GRC automation accurately handles evidence collection, control monitoring, and workflow triggers. It does not replace the human judgment required for policy decisions, risk acceptance, and audit attestations. The CISO personally signs the SOC 2 management assertion.
That is not an automated act, and no platform makes it one.
Underneath that, three root causes show up again and again:
- unclear ownership, so nobody is responsible for keeping a control current;
- manual evidence collection, which becomes repetitive and fragile;
- and disconnected systems, where policies, evidence, and day-to-day operations never actually connect.
Gaps only become visible once you are already deep into the process.
This is exactly what GRC automation is designed to solve, not by replacing judgment, but by removing the manual burden that eats the time you need for it. To understand what a GRC platform is and how to implement it, keep reading!
What is a GRC platform?
A GRC platform is software that connects the three components of GRC: governance (policy management), risk (risk register and assessment workflows), and compliance (control monitoring, evidence collection, and audit management) into a single system.
It is also often described as a GRC tool or a GRC system. The alternative is managing each component separately across spreadsheets, shared drives, and point tools, which does not scale past the first audit.
Here is what a GRC platform typically handles.
Manual burden is where small GRC teams lose the most time. Pulling artifacts from AWS, GitHub, and Okta by hand, screenshot by screenshot, is what makes audit prep a fire drill. A platform like Scrut can automate up to 70% of that evidence collection through integrations with the systems you already run, which is what makes it routine instead.
If you are weighing options, a dedicated GRC platform overview and a guide on how to choose GRC software cover the evaluation in depth, including vendor risk management requirements.
How to implement GRC: A practical path
Once you move past definitions, the next question is simple: what should you actually do now? Before the steps, one decision shapes everything that follows: how you want to approach the work.
With that decided, here is the path.
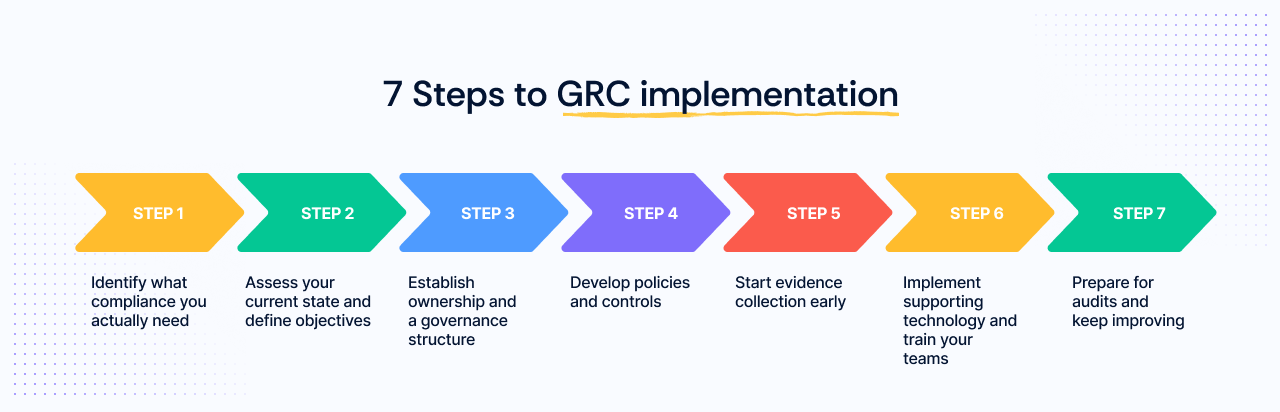
Once you move past definitions, the next question is simple. What should you actually do now?
1. Identify what compliance you actually need. Define which frameworks apply based on your customers, market, and the data you handle, such as SOC 2, ISO 27001, or GDPR. No tool can tell you which frameworks are legally required for your business.
That determination requires reviewing your customer contracts, your regulatory environment, and your data handling practices. A platform can map the frameworks once you know the scope; it cannot set the scope for you.
2. Assess your current state and define objectives. Run a gap assessment to understand what exists, what is missing, and what needs attention first. Doing this manually across systems, policies, and documents is slow and often incomplete. Automated checks and integrations give faster visibility into where the real gaps are.
3. Establish ownership and a governance structure. Define roles and responsibilities across engineering, security, IT, and HR. In practice this means naming a specific owner for each control domain, not just a team. A common failure: the CISO owns "security" and engineering owns "infrastructure," but nobody owns the quarterly access review that sits between them.
A platform with built-in task assignments and automated reminders closes that gap by making ownership visible and trackable.
4. Develop policies and controls. Create policies and controls aligned with how you actually operate. The failure mode here is a policy library that exists on paper but has no connection to what your systems do.
A policy that says "all production access requires MFA" is only useful if it is mapped to a control that checks whether MFA is enforced, and that control is tied to evidence your auditor can verify. Pre-built, customizable policies mapped to framework controls reduce the gap between intent and proof.
5. Start evidence collection early. Capture logs, access controls, and system activity continuously rather than retroactively. Automation earns its place here: a platform can pull evidence automatically through integrations.
Note the boundary. Automation handles the evidence that systems generate automatically. Evidence that requires human judgment, such as attestations, management reviews, and board decisions, remains manual.
6. Implement supporting technology and train your teams. Use a system that connects controls, evidence, and workflows instead of fragmented spreadsheets and point tools, and make sure employees understand the policies and their role.
Informal training, a Slack message or a shared doc, tends to be inconsistent and leaves no audit trail. Built-in training modules with completion tracking give you evidence that employees acknowledged the policies, which is a specific control auditors check for in SOC 2 and ISO 27001.
7. Prepare for audits and keep improving. Monitor controls, run internal checks, and refine over time. Solo audit prep is reactive and time-intensive; continuous monitoring and audit-ready evidence remove most of the last-minute pressure.
This path is not about building a perfect compliance program upfront. It is about choosing the right approach and building a system that consistently proves your controls are in place. For the extended version, see the GRC implementation roadmap, and for larger organizations, the step-by-step enterprise GRC rollout.
When GRC becomes mandatory: An industry guide
Not every business faces the same compliance obligations. The industry you operate in, the data you handle, and the customers you serve all shape which GRC frameworks apply, and whether compliance is a legal requirement or a market access requirement.
What is GRC in banking?
In banking, GRC coordinates how financial institutions manage credit risk, operational risk, and regulatory capital requirements alongside their information security obligations. Frameworks like Basel III, SOX, and PCI DSS apply at the same time, and GRC provides the unified framework for managing them without duplicating work across teams.
GRC reporting: what metrics to showcase
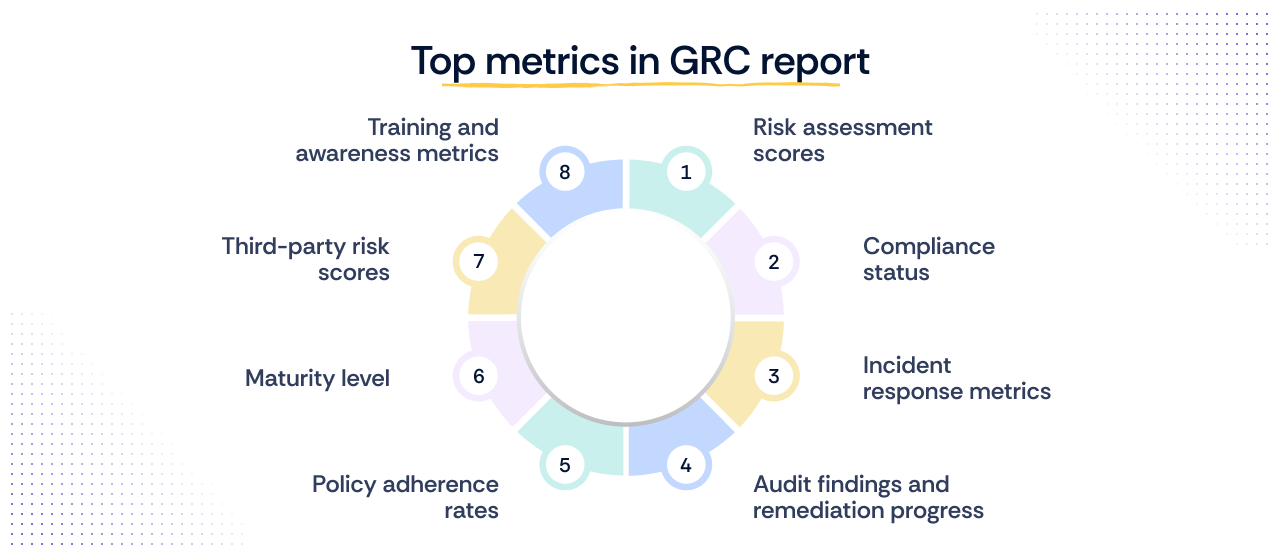
GRC reporting is not the same as a certification, and conflating the two is a common mistake that creates gaps in board-level visibility. A SOC 2 attestation report or an ISO 27001 certificate tells you where you stood at a point in time. GRC reports tell you where you stand right now, and they are the artifact your board should be asking for between audits. These views help leadership assess effectiveness, spot gaps, and make informed decisions. Key metrics include:
- Risk assessment scores – measure exposure across domains to help prioritize mitigation.
- Compliance status – track adherence to requirements and highlight gaps.
- Incident response metrics – number of incidents, response times, and resolution effectiveness.
- Audit findings and remediation progress – results and the corrective actions taken.
- Policy adherence rates – employee compliance with internal policies.
- Maturity level – how far your program has moved from ad hoc toward integrated.
- Third-party risk scores – vendor and partner risk posture.
- Training and awareness metrics – participation in GRC training.
The OCEG GRC capability model
OCEG developed the GRC Capability Model to give practitioners a shared language for what a mature GRC program actually does. If you are benchmarking your own program or explaining GRC to a board, these four components are the reference frame most auditors and consultants use:
- Learn – gather information on risks, regulations, and business goals through assessments and monitoring.
- Align – establish governance structures, policies, and accountability that tie GRC to business and regulatory needs.
- Perform – implement GRC by integrating risk management, compliance processes, training, and technology.
- Review – continuously monitor, audit, and refine to adapt to change and improve efficiency.
How Scrut handles GRC for growing teams
Most founders do not have weeks to spend stitching together policies, evidence, and audit prep. Scrut is built for that situation. It automates evidence collection from your existing stack, maps your controls to frameworks like SOC 2 and ISO 27001, and shows you what is done, what is missing, and what to focus on next.
Scrut pairs the platform with a dedicated InfoSec expert team that supports you from pre-audit through post-audit, so you are not navigating GRC alone and are less likely to hit the mistakes that delay audits or add effort.
Ready to take control of GRC? Schedule a demo.
GRC stands for governance, risk, and compliance. Governance sets the rules and accountability, risk management identifies and prioritizes threats, and compliance proves your controls are working.
A GRC platform is software that connects governance, risk, and compliance into a single system: policy management, a risk register, control monitoring, evidence collection, and audit management. It replaces managing each piece separately across spreadsheets and point tools.
GRC matters for startups when security and compliance start affecting revenue, usually when customers ask for proof of controls, send security questionnaires, or require proof of compliance. Without a structured approach, teams spend time reacting to requests instead of building a system that handles them consistently.
The biggest challenges are usually not technical. They involve unclear ownership, manual evidence collection, and disconnected systems. Many teams also underestimate the time required, especially when evidence has to be gathered retroactively instead of continuously.
Parts of GRC can be automated, especially evidence collection and control monitoring, through integrations with systems like AWS, GitHub, and identity providers. Human judgment is still required for policy decisions, risk acceptance, and audit attestations. The CISO signs the SOC 2 management assertion. No platform does that for you.