

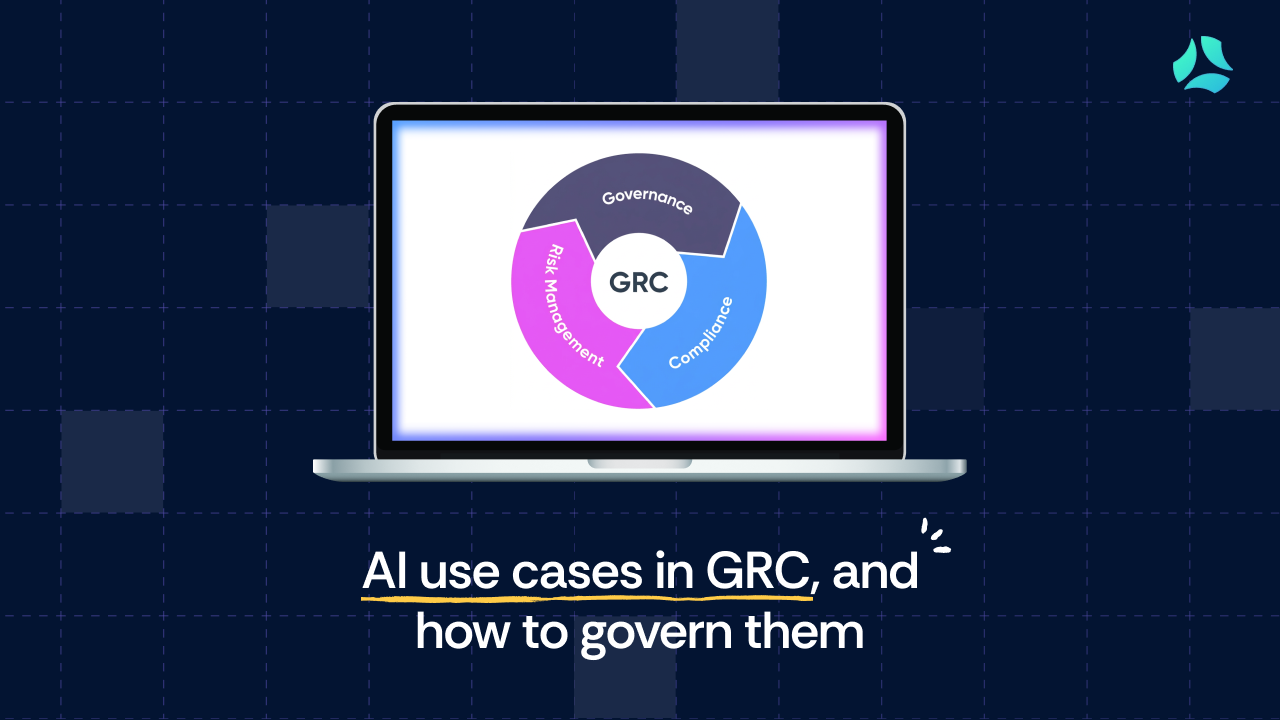


- AI in GRC automates evidence collection, flags control failures in real time, and maps regulatory changes to internal policies, shifting teams from reactive to predictive.
- The highest-value use cases today are AI as a quality checker on compliance work and as a brainstorming partner for control remediation.
- Agentic AI is the next frontier, but fully autonomous remediation without human approval still breaks trust.
- Governing AI itself (ISO 42001, NIST AI RMF) is now a GRC obligation, not just a future consideration.
- Human oversight remains non-negotiable: liability for AI-generated compliance output sits with the named control owner, not the model.
AI in GRC is the application of machine learning, natural language processing, generative AI, and increasingly autonomous systems to the daily work of governance, risk management, and compliance.
In practice, that means software that collects audit evidence on its own, flags a failing control the day it fails, and translates a new regulation into a prioritized list of obligations, rather than a team doing all of that by hand.
This guide is written for the people who now own that work: compliance leaders, GRC managers, CISOs, CTOs, and founders managing risk in an AI-era product.
It covers the use cases that deliver value today, the emerging frontier of agentic AI, the discipline of governing AI itself as a GRC obligation, and an honest account of where AI in GRC currently falls short.
One tension runs through all of it. Business adoption of AI is moving faster than the frameworks and regulations meant to govern it. Most AI-specific regulation globally is still voluntary or in draft. The EU AI Act is the notable exception. That gap is the real backdrop to every use case below.
What is AI in GRC?
AI in GRC refers to the use of machine learning, natural language processing, generative AI, predictive analytics, and agentic systems to automate and strengthen governance, risk, and compliance processes. It is not one technology. It is a stack of them, each solving a different part of the problem, and it is worth understanding which is which before you evaluate any platform's claims.
Here is how the main technologies map to real GRC work:
- Machine learning drives pattern recognition and risk scoring. It surfaces anomalies in access logs and transaction data that a human reviewer would miss at scale, not because the reviewer is inattentive, but because the volume is inhuman.
- Natural language processing (NLP) parses regulatory text, extracts specific obligations, and maps them to your internal policies.
- Generative AI and large language models (LLMs) draft policies, answer control questions, and automate security questionnaire responses, with human review required before anything is final.
- Predictive analytics forecasts risk and detects anomalies, flagging vendor risk signals or emerging control weaknesses before they escalate.
- Agentic AI runs autonomous monitoring and multi-step remediation workflows. It is the newest and least mature category. The governance question it raises, who is accountable when the agent acts, does not yet have a clean answer.
The important distinction is between AI-assisted GRC, where a human stays in the loop and approves every consequential action, and agentic GRC, where the system takes action on its own.
Most of what delivers value today is AI-assisted. Nicholas Muy, CISO and VP of Engineering, Scrut Automation, has described how far this can go inside a platform:
For the operational side of this, see how GRC automation works in practice and how generative AI in GRC is reshaping the discipline.
AI technologies in GRC
AI in governance: Decision support, policy management, and accountability
Governance is where AI's role is most easily misunderstood because AI now sits on both sides of the equation. It supports governance decisions, and it has itself become something that must be governed.
A. Decision support
AI-driven decision support has moved past dashboards. In a modern environment, a real-time risk register updates as controls change, and AI flags anomalies in privileged access activity. An unexpected admin role assumption outside business hours, for example, before a human would notice the pattern.
It provides decision-makers with current insights and scenario analysis rather than a monthly snapshot, so governance becomes something closer to a live system than a quarterly review.
B. Policy management and creation
AI can draft, refine, and update policies by analyzing regulatory requirements and organizational context. That accelerates policy lifecycle management significantly. The draft is where AI's authority ends, though. A human must review and sign off before any policy is adopted, and that is not a formality. Liability for the output sits with the control owner who approves it. The AI produces the draft. What happens next is on the named owner.
C. Transparency and accountability
One of AI's most useful governance contributions is that it can act as an always-on observer, monitoring transactions, activities, and decision processes to create a traceable audit trail. This gives auditors evidence that is generated continuously rather than reconstructed after the fact, and it reinforces a culture of accountability because activity is logged as it happens, not assembled from memory during audit prep.
D. Governing AI as part of governance
Here is the catch that most GRC programs are still catching up to: if your organization uses AI in its products or operations, you now need a governance framework for the AI itself, not just AI for governance.
As Sandip Wadje, Managing Director at BNP Paribas, noted in our podcast Risk Grustlers, AI governance is an evolving trajectory rather than a fixed destination, and tools like Microsoft Copilot have exposed the gap by surfacing access that managers assumed employees never had.
The two primary frameworks for this are ISO 42001, the AI management system standard, and the NIST AI RMF. Building an AI governance framework is now a core GRC deliverable, not a future consideration.
AI in risk management: From reactive to predictive
Risk management is where AI's shift from reactive to predictive is most visible, and where a new category of AI-specific risk has appeared that GRC teams now have to assess directly.
Predictive risk detection
AI analyzes historical data, market signals, and external factors to forecast risks and prioritize them by likelihood and impact. A financial institution can use it to predict credit defaults from customer behavior and transaction patterns; a supply-chain operator can flag likely disruptions before they cascade.
The value is not just prediction, it is prioritization, so teams allocate resources to the highest-consequence risks first instead of treating everything as equally urgent. This connects directly to risk-based prioritization of AI advancements.
Fraud, anomaly, and threat detection
Machine learning analyzes transaction patterns and network behavior to identify anomalies, flagging deviations in real time and reducing false positives so analysts focus on genuine threats rather than noise.
An e-commerce platform can block a fraudulent transaction as it happens; a security team can catch unusual network activity before it becomes a breach.
Control optimization and GRC platform integration
AI evaluates control effectiveness by analyzing where controls are over-tested, under-tested, or missing entirely. Integrated into a GRC platform, it can identify that a risk in your register has no mapped control, flag a control that has not been tested in six months, and surface a pattern of access-review failures before they compound into an audit finding.
AI-specific risks that GRC teams must now assess
This is the gap most overviews miss. Deploying AI creates its own risk surface, and GRC teams are now responsible for governing it. Prompt injection is one of the stickiest problems: it uses crafted inputs to make a model violate its own security policy, and because generative models accept unstructured input, it is genuinely hard to solve.
There are direct forms (a user tricking the model) and indirect forms (a malicious web page embedding instructions that an autonomous agent then executes).
The second risk is less visible but equally consequential: unintentional training. Employees submit sensitive data to third-party models that may train on it, then surface it to other users.
Samsung reportedly submitted confidential code and meeting notes to ChatGPT, and Amazon reportedly found ChatGPT producing responses that closely resembled its internal material.
They are the reason you need a policy on what data may be submitted to AI tools, backed by data classification as a prerequisite.
Agentic risk management raises the sharpest question of all: who is accountable when an AI-driven remediation acts without human approval? That question does not yet have a settled answer, which is why human approval remains the standard.
AI risks that GRC teams must now govern
For the model-poisoning and hallucination angles specifically, see generative AI security risks and how these feed into your risk register.
AI in compliance: Automation, monitoring, and evidence
Compliance is where AI in GRC delivers its most concrete, measurable value today, and also where expectations have overshot reality most often.
A. Regulatory change management
The mechanism that turns a 200-page regulation into a structured obligation feed is NLP. It interprets regulatory language, extracts specific requirements, and maps them to your existing policies, so your team gets a prioritized list, not a document dump.
The EU AI Act is a live example: GRC teams are actively tracking which tier their AI systems fall into as enforcement approaches. See how regulatory change management works as a continuous process.
B. Policy management and obligation mapping
Where regulatory change management surfaces new obligations, policy management closes the loop. AI parses the new requirement, maps it to your existing policy set, identifies which policies need updating, and flags gaps, so your team gets a prioritized list of policy actions rather than a document to read and interpret manually.
The cycle that used to take weeks of manual cross-referencing runs continuously in the background.
C. Internal controls and continuous testing
The shift that matters in internal controls is not detection; it is timing. AI tests controls automatically and continuously, so a failure surfaces the day it happens rather than at the next audit cycle.
The highest-value application here is AI as a quality checker: evaluating whether a policy or a piece of evidence is actually up to the mark before it goes into an audit, rather than after an auditor finds the gap.
This is continuous controls testing, and it reduces dependency on point-in-time reviews that only ever tell you the state of your controls on one date.
D. Third-party and vendor risk
Modern AI-driven third-party risk management is agentic: it continuously scans for changes in a vendor's risk status, negative news, legal actions, and data breaches, rather than relying on an annual questionnaire.
The new wrinkle is LLM-specific vendor risk. When your vendors use large language models, you inherit their unintentional-training and prompt-injection exposure. See how LLMs and third-party risk intersect.
E. AML/KYC
In anti-money-laundering and know-your-customer processes, AI analyzes large volumes of customer data to detect suspicious patterns while reducing false positives.
Rather than flagging everything that trips a static rule, AI weighs behavioral context, which cuts the alert volume analysts have to clear and improves the accuracy of the alerts that remain.
F. Evidence collection
Automated evidence collection is one of AI’s clearest wins. Instead of chasing screenshots across Slack threads and spreadsheets, teams let the platform gather and cross-reference audit artifacts continuously, which cuts audit prep time substantially. This is core to any compliance automation program.
G. Continuous monitoring for ESG compliance
AI enables continuous monitoring for environmental, social, and governance compliance by analyzing data on environmental impact, social responsibility, and governance practices. It assesses adherence to ESG standards, identifies gaps, and supports ongoing compliance rather than periodic reporting.
Where AI compliance use cases fall short: The most ambitious promises have underdelivered. Fully autonomous remediation broke trust because customers still want to approve changes themselves. And AI auto-filling questionnaires, while genuinely useful, misses the larger opportunity.
The more ambitious goal is eliminating the questionnaire process altogether rather than automating a broken artifact.
AI in internal audit
A SOC 2 report is months out of date the moment procurement reads it. That is the stale-PDF problem, and it is the core argument for continuous audit. AI enables always-on audit mechanisms that observe controls constantly, replacing the annual snapshot with something closer to a live feed.
Risk-based auditing is where this pays off first. AI models analyze historical audit data, financial transactions, and operational metrics to identify the highest-risk areas, so auditors allocate their time to the controls that matter most instead of sampling evenly across everything. For continuous compliance programs, this is the difference between an audit that confirms what you already knew and one that finds the problem you missed.
AI also accelerates evidence work, automatically gathering and cross-referencing audit evidence that auditors would otherwise assemble by hand. This is exactly where the accuracy threshold question becomes real. At some point, AI assistance in audit becomes a risk rather than an asset. The guardrail is a human sign-off requirement before any AI-gathered evidence is submitted. Human-in-the-loop is not just good practice here; it is a documented control that ISO 42001 auditors ask to see.
One practical note on the AI features themselves: they need re-assessment on a cadence. The workable baseline is quarterly, with an event-driven reassessment triggered by any major release or fundamental change to how a feature works. Build this into your internal audit checklist and connect it to your broader approach to AI for continuous compliance.
Governing AI itself: ISO 42001, NIST AI RMF, and the EU AI Act
Here is the pivot that defines AI in GRC in 2026: AI is no longer just a tool for doing GRC. It is now a subject of GRC. If your organization uses AI in its products or operations, you have to govern that AI, and three frameworks define how.
ISO 42001
ISO 42001 is the AI management system standard, and structurally it mirrors ISO 27001. The clauses on context, leadership, planning, and support carry over almost directly, so if you hold ISO 27001, much of the management-system scaffolding is already in place. What is genuinely new sits in the controls.
The most unexpected new requirement is the AI system impact assessment. It is not a risk assessment with a new label. It assesses how an AI system affects three distinct areas: the organization, the individuals using it, and society. A biased selection outcome affecting a particular community, for example, is a societal impact that the assessment has to capture.
Beyond that, ISO 42001 introduces an AI tool inventory (an inventory of the models and computing systems you use), data provenance controls, and human-in-the-loop documentation.
You also have to determine which role your organization plays, provider, producer, or user, because that dictates your statement of applicability. See how AI risk assessments work under the standard, and read about Scrut's ISO 42001 certification.
NIST AI RMF
The NIST AI RMF structures AI risk through four core functions: govern, map, measure, and manage. It tells you to define your risk appetite and tolerance before deploying AI, but it does not tell you what those should be for your context. That work is yours. Its strength is exactly this flexibility: you apply it to your situation, not a template someone else designed.
In practice, many teams layer it with the NIST Cybersecurity Framework and the NIST Privacy Framework. The three complement each other and together cover the control surface most organizations need. For a step-by-step approach, see the NIST AI RMF application guide.
EU AI Act
The EU AI Act is the furthest-ahead binding regulation globally. It takes a risk-tiered approach, prohibits certain AI applications outright, and carries penalties for non-compliance if you operate in the EU. The practical implication is immediate: you need to determine which tier your AI systems fall into, because that determines your obligations.
Which framework, and when to certify
ISO 42001 and the NIST AI RMF are complementary rather than conflicting. Use the NIST AI RMF as a framework to structure your thinking and decision-making. Pursue ISO 42001 versus NIST AI RMF certification when you need a third-party-verified credential.
The trigger for formal certification is usually external: a customer asks for it, or you make a material change to AI features in a customer-facing product. If your buyers expect third-party attestations about your practices, that is your signal to certify rather than self-attest.
The minimum documentation for responsible AI, regardless of framework, is consistent: a defined context for each AI system (intended purpose, beneficial use, deployment settings), a risk management procedure, a risk register, the applicable statutory and regulatory requirements, and documented test sets and metrics.
Where AI in GRC delivers real value vs. where it falls short
Most content on this topic is optimistic to the point of being useless. Here is the practitioner-honest version.
What delivers measurable value today:
- AI as a quality checker. The single highest-value use case is AI sanity-checking your own work: is this policy up to the mark, is this evidence actually good enough? It catches gaps before an auditor does.
- AI as a brainstorming partner. Teams use it to work through how a control applies to their environment and what to do about it. A good platform hands you the Terraform, the scripts, or the CLI commands directly instead of making you go find them.
- Continuous monitoring and real-time alerts. AI flags control failures the day they happen rather than at the next audit cycle.
- Automated evidence collection. This reliably cuts audit prep time, which is why it is the most-adopted use case.
Where expectations have fallen short:
- Fully autonomous remediation. Customers still want to approve the change themselves. Removing the human-in-the-loop hurt trust more than it helped.
- AI on ambiguous or judgment-heavy controls. Where a control is novel or the framework is new, the model overpromises, producing a confident answer that an expert then has to unwind. Teams still prefer manual work here.
- AI auto-filling questionnaires as an end goal. Useful, but it automates a broken process instead of eliminating it.
- Hallucination in compliance contexts. An LLM can produce a confident, wrong compliance answer. In a compliance context that is dangerous, which is why a human must always validate. See more on AI hallucinations in GRC.
There is no universal threshold. Set it based on the consequence of a wrong answer. A miscategorized vendor risk is recoverable. A wrong compliance attestation is not. The higher the regulatory or contractual consequence, the lower your tolerance for AI output without human validation. For a deeper treatment, see GRC automation: what works, what doesn't, and what to fix first and the broader role of AI in GRC.
AI in GRC at a glance
The table below summarizes how AI's role, value, and governance considerations differ across the three pillars.
Best practices for using AI in GRC
A. Start by separating two goals that are easy to conflate: using AI to do GRC work, and governing AI as a GRC obligation in its own right. A team that treats these as the same thing often ends up with a risk register that tracks AI tool adoption but no framework for governing the AI itself. They are different programs.
B. Understand your data landscape. Before AI deployment, answer the AI-specific data question: what data are employees submitting to AI tools, is it sanitized, and does it carry PII or PHI exposure risk? Data classification is a prerequisite, not a nice-to-have.
C. Ensure regulatory compliance. For AI-specific obligations, the relevant frameworks are the EU AI Act, the NIST AI RMF, and ISO 42001. Determine which apply based on where you operate and what role you play.
D. Train users on what data they may and may not submit to generative AI tools, not just how the tools work. This is a policy question first and a mechanics question second.
E. Monitor continuously. AI models drift. Build a quarterly re-assessment cadence into your calendar, with event-driven review on any major release.
F. Secure your data. Mitigate prompt injection, restrict what data sources an AI tool can access, and pre-process or redact sensitive data before it goes to any third-party model.
G. Keep humans in the loop. Liability for AI-generated compliance output sits with the human who reviews and approves it. AI output is a draft until a named owner signs off. Think of it like code review: if AI generates the code, accountability sits with the engineer who approves the pull request. Compliance works the same way.
H. Build interdisciplinary collaboration. Legal, AI engineers, and GRC teams have to work together on AI use policy. The risks span IP, privacy, and cybersecurity simultaneously, and no single team has full visibility without the others.
I. Prioritize transparency and explainability. Model explainability is now a regulatory expectation in some jurisdictions, including under the EU AI Act, and auditors will ask for it.
J. Run regular AI system audits. These now include reviewing the model itself, its training data sources, and its output accuracy, not just traditional IT controls.
K. Have an AI use policy. The foundational guardrail is a documented policy for generative AI tool use, covering what data employees can submit, the review process for new tools, and the privacy, legal, and cybersecurity review each tool goes through.
For mid-size teams, the pragmatic move is flexible controls that enable employees rather than block them, focused on protecting crown-jewel data rather than classifying everything as high-sensitivity. This connects directly to your broader approach to AI compliance and vendor risk management for AI, and should sit inside a documented risk management procedure.
Conclusion
AI in GRC has moved from aspiration to operational reality, but the highest-value use cases are not the ones the hype cycle promised. They are AI as a quality checker on compliance work, AI as an always-on monitoring system, and AI as a brainstorming partner for remediation, with a human retaining accountability for every compliance output that leaves the building.
The next frontier is governing AI itself. Organizations that build ISO 42001 and NIST AI RMF discipline into their programs now, before a customer or regulator forces the question, will be the ones that can adopt AI confidently rather than reactively.
The teams that treat AI as both a tool for GRC and a subject of GRC are the ones that will stay ahead of a regulatory landscape still trying to catch up.
Explore how AI can strengthen your GRC program by scheduling a demo with us today.
AI automates evidence collection, flags control failures in real time, maps regulatory changes to internal policies, and supports faster risk decisions. It shifts GRC teams from reactive, point-in-time work to continuous, predictive programs. The highest-value uses today are AI as a quality checker on compliance artifacts and as a brainstorming partner for remediation, with humans retaining accountability for every output.
AI uses predictive analytics to forecast risks, machine learning to detect fraud and anomalies in real time, and continuous monitoring to surface control failures early. It also helps prioritize risks by likelihood and impact, so teams focus on the highest-consequence exposures first rather than treating everything as equally urgent.
Yes. If your organization uses AI in its products or operations, governing that AI is now a GRC obligation. ISO 42001 (the AI management system standard) and the NIST AI RMF are the two primary frameworks, and the EU AI Act is the furthest-ahead binding regulation. This is distinct from using AI to do GRC work.
Liability sits with the named human who reviews and approves the output, not the model. AI-generated compliance work is a draft until an accountable owner signs off, the same way accountability for AI-generated code sits with the engineer who approves the pull request.
Fully autonomous remediation without human approval breaks trust; customers still want to approve changes themselves. AI also overpromises on ambiguous, judgment-heavy controls, producing confident answers that experts have to unwind. Hallucination makes human validation mandatory in compliance contexts, where a confident wrong answer is dangerous.