


Every SOC 2 audit reaches a moment like this. The auditor stops scrolling through the evidence and asks for the actual pentest report, not the line item that says testing happened, the report itself, with findings, severity ratings, and proof that whatever got found actually got fixed.
A question that’s gotten harder to dodge.
The updated Payment Card Industry Data Security Standard (PCI DSS) penetration testing requirements have been fully enforced since the grace period ended in March 2025, raising the bar for how organizations document and perform security testing (Sherlock Forensics, April 2026). What used to pass a review can now get a second look.
The scrutiny isn't limited to the report, either. It's increasingly landing on how the testing was performed in the first place.
Cobalt surveyed 455 security professionals for its 2026 AI and Pentesting Pulse Report and found that 78% had seen a fully automated scanning tool miss a critical vulnerability. The share of respondents willing to rely on AI alone for testing fell from 29% in 2025 to 9% in 2026. (The Register, June 2026).
We've heard a version of the same question from Scrut prospects: was this actually tested by a person, or was it a script left running against the target?
Because nobody is really buying a pentest report. They're buying evidence that has to hold up later, in front of an auditor, a customer security team, or their own security leadership.
That's where CREST accreditation becomes more than a badge.
What just happened
CREST is an international not-for-profit body that has accredited penetration testing and security services providers since 2006. It's the accreditation UK and international regulators, and increasingly US enterprise procurement teams and cyber insurance underwriters, look for as independent proof that a security tester actually meets a defined standard.
CREST approved Scrut for penetration testing on August 24, 2026, extending the vulnerability assessment accreditation the company has held since August 2024. Same CREST membership, now covering both disciplines.
Vulnerability assessment finds and catalogs weak spots. Penetration testing goes further and tries to break them the way an attacker actually would, a different exercise entirely, with a stricter standard for how testing gets planned, executed, documented, and validated.
"For the security teams we work with, this accreditation answers a question they'd otherwise have to take on faith: how do we know the testing was actually done properly? A pen test report showing zero vulnerabilities doesn't prove much by itself, CREST accreditation means the process behind that report has been independently checked, not just self-reported.”
Junaid Mohammed, VP of Customer Success
A CREST-accredited pentest doesn't check a specific box on any one framework. What it delivers is stronger: a report whose methodology, tester, and process have already been independently vetted, not just Scrut's word that the testing happened, before anyone in an audit room ever asks to see it.
Back to the audit room
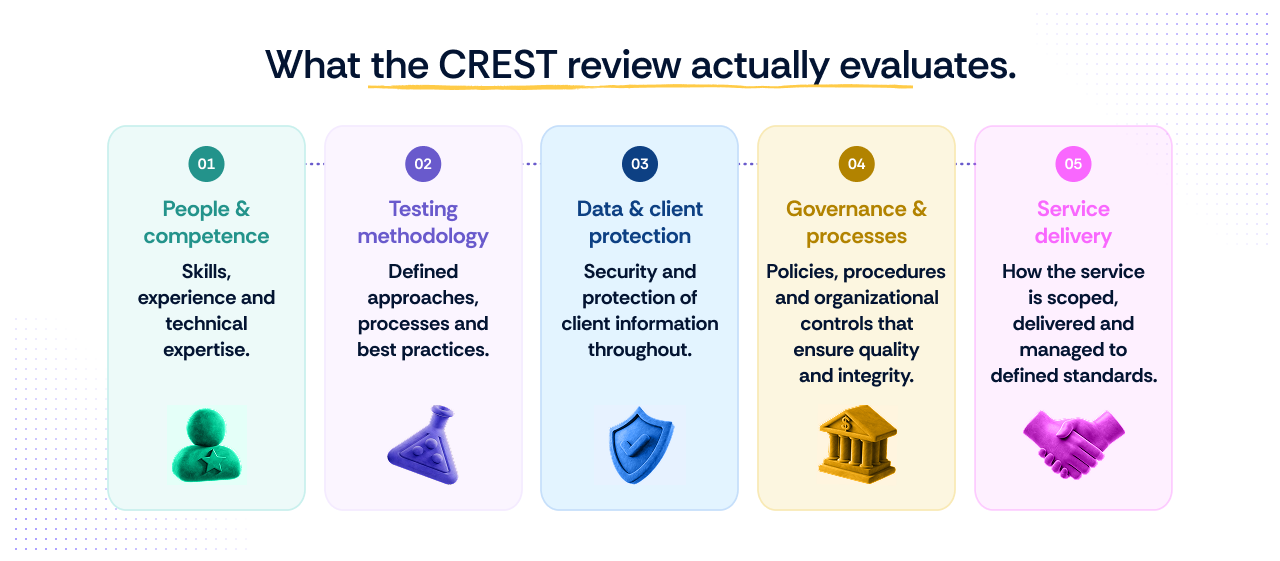
Back to that moment in the audit, and the question sitting underneath it. The honest answer, on every one of those prospect calls, has been the same thing CREST's review exists to confirm: a person ran it twice, then ran it again after the fix went in.
That's the specific thing the accreditation verifies. The wider thing it points to is a platform that doesn't hand the hardest, highest-stakes piece of its evidence chain to someone else to produce, and that's increasingly the difference prospects are actually evaluating.
If you want to see what that looks like, let's talk!