


- RMF (Risk Management Framework) is NIST's structured, 7-step process for integrating security and privacy into the full system development lifecycle, defined in NIST SP 800-37 Rev. 2.
- The seven steps are Prepare, Categorize, Select, Implement, Assess, Authorize, and Monitor. RMF is mandatory for U.S. federal agencies under FISMA and OMB Circular A-130, and commercial organizations can adopt it voluntarily.
- Effective RMF implementation needs cross-functional input, not just a security-team review.
- Continuous monitoring, not a one-time assessment, is what keeps an Authorization to Operate (ATO) defensible.
RMF, short for Risk Management Framework, is the NIST-developed process that integrates security, privacy, and supply chain risk management into the full system development lifecycle. It applies to two broad audiences: U.S. federal agencies, for whom it is mandatory under FISMA, and commercial or private-sector organizations that adopt it voluntarily to bring structure to how they manage risk.
This article walks through what RMF is, what it stands for, the seven steps of the process, and what implementation actually looks like once you move past the theory.
What is RMF (Risk Management Framework)?
RMF is a U.S. federal risk management process developed by NIST and documented in NIST SP 800-37. It provides a structured, repeatable way to manage risk to information systems across their entire lifecycle, from initial design through ongoing operation and eventual decommissioning.
What separates RMF from a plain cybersecurity checklist is scope. It integrates security controls, privacy requirements, and supply chain risk management directly into how a system is designed and run, rather than bolting them on afterward. That integration is the point of the framework, not an optional extra.
“The Risk Management Framework provides a disciplined, structured, and flexible process for managing security and privacy risk that includes information security categorization; control selection, implementation, and assessment; system and common control authorizations; and continuous monitoring.”
(NIST SP 800-37 Rev. 2)
Applicability is broad. U.S. federal agencies are required to implement RMF under OMB Circular A-130, which carries out FISMA, and the Department of Defense mandates it through DoD Instruction 8510.01. Commercial organizations can also adopt it voluntarily when they want a structured, defensible approach to risk. The current version was developed by the Joint Task Force, an interagency working group spanning civilian, defense, and intelligence agencies.
On history: NIST SP 800-37 was first published in 2004 as a guide for security certification and accreditation of federal information systems. The 2010 revision introduced the RMF structure, and Revision 2, the current version, followed in December 2018.
Understanding RMF matters for a reason that gets lost in most compliance-driven treatments: risk management only works when it is grounded in business context, not just a technical checklist. A framework tells you what outcome to achieve. The judgment about what matters for your specific environment is yours. That distinction runs through everything below. If you are comparing approaches, it helps to see RMF alongside other risk management frameworks and to understand where it sits within broader NIST compliance.
The seven steps, at a glance:
- Prepare
- Categorize
- Select
- Implement
- Assess
- Authorize
- Monitor
The framework is documented in the same family as the NIST SP 800-53 controls catalog, and it sits within the wider category of IT risk management framework approaches an organization can adopt.
What does RMF stand for?
RMF stands for Risk Management Framework. In the federal government and cybersecurity context, it refers specifically to the NIST Risk Management Framework documented in SP 800-37. In broader use, “risk management framework” can describe any structured approach to organizational risk, but when security professionals say “RMF” without qualification, they almost always mean the NIST framework.
One point of disambiguation: the NIST AI Risk Management Framework (documented in NIST AI 100-1) is a separate and newer framework built for AI-specific risk. This page covers the information systems RMF in SP 800-37, not the AI RMF.
Why RMF matters: Federal mandate and commercial adoption
For federal agencies, the mandate is straightforward. FISMA requires RMF, and RMF serves as the comprehensive framework for securing, authorizing, and managing IT systems. It defines a cyclical process that begins with initial system protection through Authorization to Operate (ATO) and continues through ongoing risk management via continuous monitoring. RMF has also been incorporated into Department of Defense instructions.
RMF for commercial and private-sector organizations
The framework is not federal-only by design. NIST SP 800-37 Rev. 2 states explicitly that RMF can be applied to any type of system or technology, including IoT and control systems, and within any type of organization, regardless of size or sector. That scope is what makes it useful outside government.
Organizations in regulated industries adopt RMF because it maps cleanly onto obligations they already carry. Healthcare providers find it aligns with HIPAA security rule requirements. Defense contractors and cloud providers find it maps to FedRAMP. The framework's risk-prioritization logic, applying controls based on categorized impact rather than uniformly across every system, is what makes it scalable across organizations of very different sizes. Compliance, approached this way, becomes an attempt to manage well-scoped risk across a population rather than a box to tick.
Here is how RMF compares to other frameworks a growing organization is likely to encounter:
Key cybersecurity and GRC framework comparison
The core distinction: RMF is process-based and produces a formal authorization decision, where CSF is outcome-based and produces a risk profile. If you are mapping across several of these, our overview of compliance frameworks covers where they overlap and where they diverge.
The 7 steps of the NIST RMF process (SP 800-37 Rev. 2)
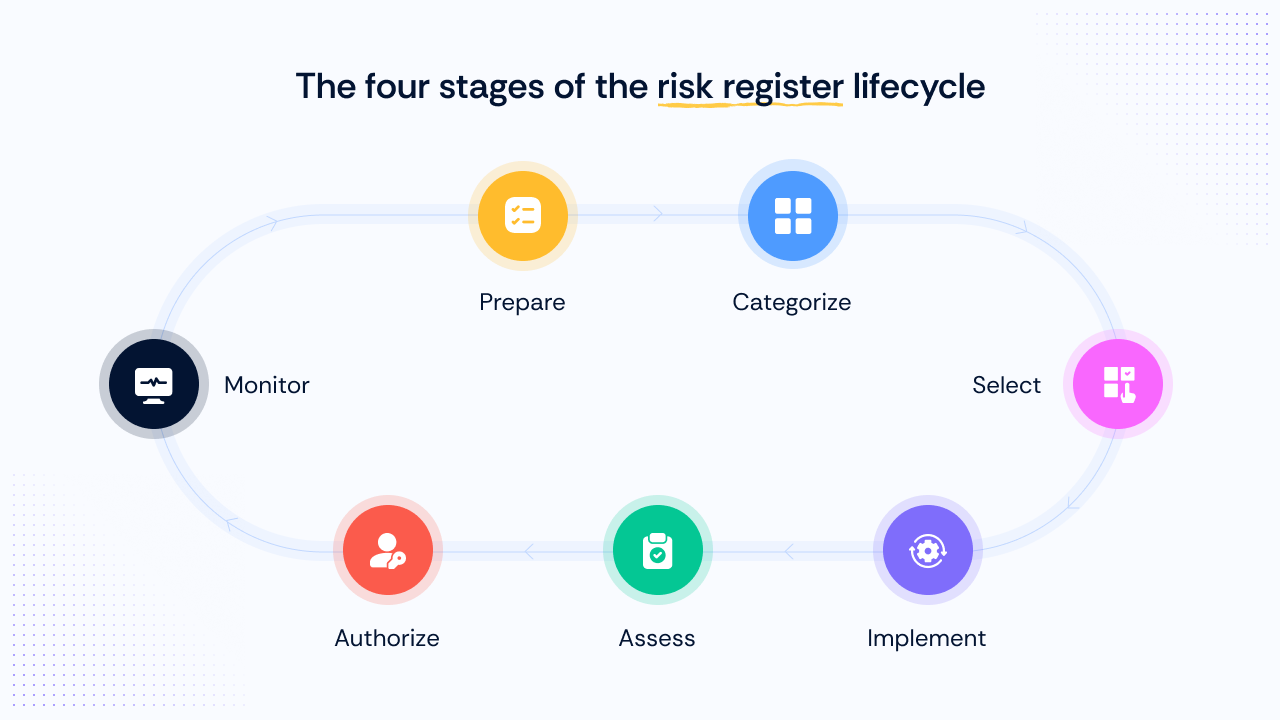
The RMF process is NIST's seven-step methodology for managing cybersecurity and privacy risk across the full lifecycle of an information system: Prepare, Categorize, Select, Implement, Assess, Authorize, and Monitor. The framework runs as a cycle. Each step produces an artifact that the next step depends on, and the final step feeds back into the authorization decision.
Step 1: Prepare
Prepare was added in Revision 2, and it is the step organizations most often skip. That is a mistake, because everything downstream depends on it.
The purpose of Prepare is to establish the organizational context and priorities before any categorization or control work begins.
Prepare operates at two levels: the organizational level and the system level. At the organizational level, the work is to define the risk management strategy and risk tolerance, and to identify common controls that multiple systems can inherit. At the system level, it narrows to the specific system in scope.
Concretely, this step involves a handful of RMF-specific activities. Assign roles and responsibilities, including the Authorizing Official, System Owner, Information System Security Officer (ISSO), and Information System Security Manager (ISSM). Define the organizational risk strategy and risk tolerance. Identify common controls. Develop the organization-level risk assessment strategy.
This is also where a structured GRC implementation roadmap pays off, because the decisions made here shape the entire program.
Most organizations that adopt risk management for compliance treat Prepare as overhead and rush past it. That is exactly how programs end up tracking what a template told them to track rather than what actually matters for their environment.
Step 2: Categorize
Categorization determines how much protection a system needs, and it drives everything in the next step. The work begins by delineating the system boundary and then classifying the system based on the impact a loss of confidentiality, integrity, or availability would cause.
The documents practitioners actually use here are FIPS 199 (Standards for Security Categorization) and NIST SP 800-60 (which maps information types to security categories). FIPS 199 defines three impact levels: Low, Moderate, and High. Each of the three security objectives gets rated independently, and those ratings determine the control baseline selected in Step 3.
To categorize accurately, organizations identify the system's mission, roles, responsibilities, operating environment, intended use, and connections with other systems. For example, a federal agency system processing unclassified but sensitive financial data might be categorized as Moderate confidentiality, Moderate integrity, and Low availability.
Getting that answer right requires input from the people who run the business process, not just the people who run the infrastructure. The output of this step, the system's security categorization, is documented in the System Security Plan and becomes the formal basis for control selection in Step 3.
Step 3: Select security controls
The baseline, Low, Moderate, or High, comes directly from the system's categorization. It is a starting point. Tailoring is what turns it into something that fits the actual system: adding controls where the baseline underweights a specific threat, removing ones that do not apply, and modifying others to match the organization's risk tolerance.
The control catalog is NIST SP 800-53 Rev. 5, and the baselines that map categorization to controls live in NIST SP 800-53B.
Overlays are the other mechanism worth knowing. An overlay is a predefined set of modifications to a baseline, built for a specific community of interest. A cloud overlay, for example, adds or adjusts controls that address cloud-specific risks not fully captured in the standard baselines. Privacy overlays and IoT overlays work the same way for their domains.
Controls fall into three broad types: management, operational, and technical. Understanding the security control types and how they layer is what keeps a control set coherent rather than a pile of individually reasonable requirements that do not add up to a defensible whole.
Step 4: Implement security controls
The System Security Plan is the artifact that makes or breaks Step 4. Without a current SSP, the assessor in Step 5 has nothing authoritative to test against, and the authorization in Step 6 has no evidentiary foundation. Implementation must follow the SSP, which is the primary artifact produced during this step and the reference point for everything that comes after.
Implementation itself has three parts. First, develop tailored policies and procedures that specify how each control is deployed within the organization's infrastructure, customized to the characteristics of each device or system.
Second, thoroughly document the implementation process so administrators have a reliable reference for how each control was applied.
Third, conduct comprehensive implementation activities, which go well beyond installing software or configuring hardware to include testing, validation, and configuration management.
This is also where automation earns its keep. Automated evidence collection captures proof of control implementation as it happens, rather than forcing a scramble to reconstruct it later when the assessor arrives.
Step 5: Assess security controls
By the time an assessor arrives, the question is not whether controls exist on paper. It is whether they are correctly configured, operating as intended, and actually addressing the risks they were selected for.
The assessment procedures live in NIST SP 800-53A Rev. 5, which pairs with the SP 800-53 control catalog to define how each control family is tested. Interview, examine, and test are the three assessment methods, applied in combination depending on the control.
A critical detail for federal systems: the assessment must be performed by an independent assessor or assessment team. The assessor cannot be the system owner. That separation is what gives the resulting Security Assessment Report (SAR) its assurance value. Without it, the report is self-attestation, not independent assurance.
An assessment run against a complete SSP and validated systematically produces findings that the Authorizing Official can rely on. An assessment run against incomplete implementation documentation produces findings nobody should trust. The SAR is not the end product of this step. It is the input to Step 6. The AO cannot make a defensible authorization decision without it.
Step 6: Authorize information system
Authorization is where a named person accepts risk on behalf of the organization. That person is the Authorizing Official (AO), a senior official who reviews the evidence and makes an explicit risk-based decision. This is not a committee vote or a workflow status change. The accountability sits with an individual.
The AO's decision rests on four inputs: a risk assessment that identifies and evaluates operating risk; a risk acceptance decision that weighs residual risk against business value; a Plan of Action and Milestones (POA&M) that documents deficiencies with remediation timelines and owners; and control tracking mechanisms that record each control's current state. All of this is captured in an authorization package that serves as evidence for audits and reviews.
The output is the Authorization to Operate. Authorization periods vary; SP 800-37 Rev. 2 does not fix a single duration, and the AO sets the specific period based on risk. A three-year period is a common practical norm for federal systems, after which re-authorization is required.
Step 7: Monitor security controls
The Monitor step is formally defined by NIST SP 800-137 as Information Security Continuous Monitoring (ISCM), the discipline of tracking control effectiveness, configuration changes, and emerging risk on an ongoing basis. Organizations operate in threat landscapes that shift constantly, and monitoring is what keeps the authorization honest as conditions change.
Monitoring that produces no decisions is not monitoring. It is logging. If risk increases materially, whether through a new vulnerability, a system change, or a personnel change, the AO may need to re-authorize the system or authorize it with conditions. A detection capability without a defined escalation path changes nothing.
Automated tooling does the heavy lifting here. SIEM platforms, cloud security posture management (CSPM) tools, and vulnerability scanners collect and correlate security data, surface configuration drift, and provide near-real-time insight into events and incidents. Feeding that signal into a maintained risk register and running continuous compliance workflows is what turns raw monitoring data into decisions the AO can act on.
RMF implementation in practice: What actually works
The steps above describe what the framework requires. This section covers what it costs, in time, ownership, and organizational discipline, to actually run it.
How long does RMF implementation take?
For a large enterprise, a mature multi-system RMF implementation typically takes 18 to 36 months. The reason is scope: enterprises have multiple domains, different teams that have to work together, and a broad surface area to bring into a harmonious state. Two to three years is a realistic window to reach that point.
For a smaller organization, a 50-person company, for instance, a minimum viable RMF is achievable much faster, but only with ruthless scoping. Focus on the most critical systems first, assign clear ownership, and iterate. The full framework does not need to be applied uniformly to every system at once. What matters most is getting the right people in the room, because understanding how the whole company works usually takes more than one person's knowledge, and a risk assessment built on incomplete information produces an incomplete result.
RMF does not have a finish line. Even after a full implementation, personnel changes, system changes, and evolving threats mean the risk register and the authorization packages need ongoing maintenance. The organization that treats RMF as a one-time project will have a stale program. Not because the framework failed, but because the environment it was built to describe kept changing.
The risk of treating RMF as a compliance checkbox
RMF is supposed to produce defensible risk decisions, not just compliance artifacts. When it gets treated as a documentation exercise, the risk register becomes an audit artifact rather than a management tool, and the whole intent of the framework quietly fails.
Here is what actually goes wrong, in practice. Risk registers lose their value the moment they become catch-alls, filled with entries escalated for organizational reasons rather than strategic ones. A register that says everything is a strategic risk says nothing is.
The template problem is related but distinct. Most organizations that adopt risk management for compliance start from a template and never apply judgment about what actually matters for their environment. Step 1, Prepare, is designed to prevent exactly this, which is why skipping it is so consequential.
Underneath both of these is a harder truth: the documentation side of risk management is comfortable, and the operational side is hard. People are better at making documents than at implementing a process, so a beautifully documented RMF with poorly implemented controls is a common and expensive failure. A well-maintained risk register is one that contains the most impactful risks and drives action, not one that catalogs everything anyone ever wanted to escalate.
RMF risks: What can go wrong
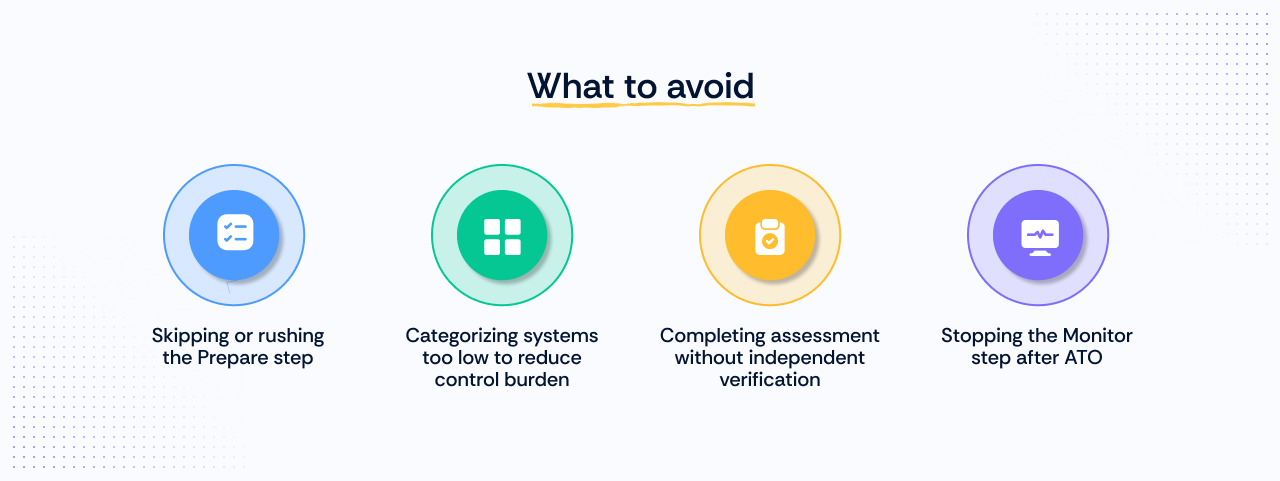
The most common RMF failure modes are organizational, not technical. Standard risk taxonomies, such as infrastructure, application, business continuity, and strategic, are useful for classification. They do not tell you why programs break down in practice.
Failure mode 1: Skipping or rushing the Prepare step. Without defined roles and a stated organizational risk tolerance, every downstream step improvises. The program ends up with no shared understanding of what it is protecting or how much risk it is willing to carry.
Failure mode 2: Categorizing systems too low to reduce control burden. It is tempting to rate a system Low to inherit a lighter baseline, but an ATO built on an understated categorization does not reflect actual risk. The authorization looks clean and means nothing.
Failure mode 3: Completing assessment without independent verification. Self-assessed controls carry lower assurance and often will not withstand external scrutiny. The independence requirement in Step 5 exists precisely to prevent this, and working around it defeats the purpose.
Failure mode 4: The Monitor step stops after ATO. Programs that celebrate authorization and then stop monitoring drift out of compliance and out of security posture. The authorization was real. The program that earned it no longer exists.
A theme runs through all four: aggregating findings without a prioritization process leads to treating everything as critical, which means nothing gets fixed. Understanding inherent vs. residual risk, applying sound risk scoring, and building in automated controls testing are what keep a program from collapsing into a pile of undifferentiated “critical” findings.
Wrapping up
RMF gives you a structure for managing risk, but the results depend on how seriously you treat each step. Take Prepare seriously, categorize systems honestly, keep assessment independent, and keep monitoring long after the ATO is signed. Do those four things, and RMF becomes what it was designed to be: a way to make defensible risk decisions, not a stack of documents assembled for an audit.
For most organizations, the hard part is the operational side: assigning ownership, collecting evidence as controls run, and keeping the risk register current as systems and people change.
That is where the right tooling helps. Scrut's risk management platform supports continuous monitoring workflows and risk register maintenance, helping teams keep the Monitor step live rather than letting it lapse after authorization. If you are looking to automate risk management as part of an RMF program, that is where a tool earns its place, not by making authorization decisions, which remain a named official's responsibility.
Ready to move your RMF program from documentation to day-to-day practice? Book a demo with Scrut.
The RMF is a structured process that helps organizations identify, assess, and mitigate risks to their information systems and data. It provides a framework for managing cybersecurity risks effectively, ensuring the confidentiality, integrity, and availability of information assets. RMF is crucial for organizations, as it helps them establish a proactive approach to cybersecurity and comply with regulatory requirements.
Unlike some other risk management frameworks that focus solely on information security, the RMF takes a broader approach by integrating security into the entire system development lifecycle. It emphasizes continuous monitoring and ongoing assessment of security controls, ensuring that organizations can adapt to evolving threats and vulnerabilities effectively.
The key steps in implementing the RMF include categorizing information systems, selecting appropriate security controls, implementing those controls, assessing their effectiveness, authorizing system operation, and monitoring security controls continuously. These steps ensure that organizations can systematically manage and mitigate cybersecurity risks across their information systems.
The primary objectives of the RMF are to establish a disciplined and structured approach to managing cybersecurity risks, ensure compliance with relevant laws, regulations, and policies, and enhance the overall security posture of organizations’ information systems. By following the RMF, organizations can identify, prioritize, and address security risks effectively.
The RMF helps organizations manage cybersecurity risks effectively by providing a systematic and repeatable process for identifying, assessing, and mitigating risks. It ensures that security controls are implemented based on risk assessments and continuously monitored to address emerging threats and vulnerabilities. Additionally, the RMF promotes a culture of security awareness and accountability throughout the organization, enhancing its overall resilience to cyber threats.