


- Generative AI in compliance delivers real value today in three defined roles: a quality checker for policies and evidence, a brainstorming partner for control implementation, and an accelerator for security questionnaire responses.
- The highest-risk failure modes are hallucination in audit evidence, over-reliance on AI output without human sign-off, and data leakage through unsanitized prompts.
- Frameworks like NIST AI RMF and ISO 42001 provide governance scaffolding, but neither is prescriptive enough to replace context-specific risk assessment.
- Liability for AI-generated compliance output sits with the named control owner who reviews and approves, not the model.
- Minimum viable guardrails are prompt sanitization, PII redaction, an AI tool inventory, and a quarterly reassessment cadence.
There is a gap between what GRC teams expected generative AI to do and what it is actually doing for them right now. The early promise was autonomy: point the model at a control and let it fix things. What teams got instead was something quieter and, in most cases, more useful. A fast, tireless assistant that still needs a human to sign off before anything counts.
That gap exists for a structural reason. Business adoption of AI is moving faster than the regulations and frameworks built to contain it, and that mismatch creates real difficulty for teams who have to assess risk in their own stack and across their supply chain. Most AI-specific regulation is still catching up. The EU has moved furthest, and voluntary frameworks fill the space where enforceable rules do not yet exist.
This is not a "why AI is great for compliance" article. It maps three things: where generative AI in compliance delivers measurable value, where it does not, and what guardrails a practitioner needs in place before deploying an LLM anywhere near an audit-relevant workflow.
What is generative AI?
Generative AI is a class of models that create new content (text, images, code, audio) by learning patterns from existing data and producing novel output. This is different from traditional AI systems built for analysis, classification, and prediction.
Generative AI vs. predictive AI
Predictive AI uses historical data to forecast future events. It analyzes past patterns to estimate what happens next. Sales forecasting and fraud scoring are predictive. Policy drafting, regulatory summarization, and control implementation scripting are generative.
The failure modes differ too: predictive models drift; generative models hallucinate.
Where does generative AI in compliance actually deliver value?
"Measurable value" means something specific here: time saved on evidence collection, faster questionnaire responses, fewer manual document drafts. Not abstract efficiency. Hours you can point to.
The transformative use cases sit in documentation and reporting. Generative AI automates the creation of compliance reports, risk assessments, and policy documents, improving consistency and reducing the errors that create downstream compliance problems.
It also analyzes large volumes of source material quickly, surfacing potential issues and emerging risks so teams stay ahead of regulatory change. The payoff concentrates in two places: AI use cases in GRC that lean on the model as a checker, and workflows where it drafts a first pass, which a human then finishes.
Where expectations exceeded reality
Not everything landed. The clearest disappointment was fully autonomous, hands-off remediation. Teams expected to let an agent just fix the problem, but customers still wanted to approve the change themselves. The human-in-the-loop did not go away, and removing it hurt trust more than it helped.
The second disappointment shows up with judgment-heavy or novel controls: where a framework is new or a control is ambiguous, the model overpromises, producing a confident answer that an expert then has to unwind.
Both cases point in the same direction. Value concentrates where AI accelerates a human's work. It evaporates where it tries to replace human judgment. This is consistent with how practitioners describe the broader role of AI in GRC: a force multiplier, not a substitute for accountability.
How does generative AI boost governance?
Generative AI can boost governance in three areas, each with an implementation reality and a failure mode.
Policy and documentation automation. Generative AI drafts board reports, policy manuals, and governance guidelines, and keeps internal policies aligned with regulatory change. What the AI actually does is produce a coherent first draft fast. What the human still must do is verify that the draft reflects how the organization operates in practice.
The failure mode is treating a generated policy as an implemented control. A policy document is not a functioning control, and an auditor will make that distinction even when your dashboard does not.
Regulatory monitoring and gap assessment. The model continuously scans and summarizes regulatory changes and assesses their impact on your posture. The human decides which changes matter and how the organization responds.
The failure mode here is trusting the summary without checking the source, because a confident summary of a regulation the model half-understood is worse than no summary at all.
Decision support and board reporting. Generative AI extracts relevant information across data sources and generates concise reports for leadership, surfacing trends and anomalies to support decisions. The human owns the decision.
The failure mode is a board that sees a green dashboard and stops asking questions, conflating a clean report with a secure posture.
One prerequisite sits underneath all three. Before deploying any AI tool with broad access to internal content, data classification has to be in place. Practitioners rolling out tools like Microsoft Copilot have found that the tool inherits existing permissions and exposes oversharing that was always there but never scrutinized.
Data classification was a known issue with existing tools, but it was rarely given enough attention until AI made the gap impossible to ignore. Sound governance practices now treat classification as a precondition for deployment, not a cleanup task afterward.
How does generative AI enhance risk management?
Risk management is where generative AI both helps the most and misleads the most.
Risk identification and predictive modeling. The model analyzes large datasets, historical records, and market signals to surface potential risks and build risk models that simulate different scenarios. This works well for pattern-heavy work. It struggles wherever the risk is novel or the data is thin.
Early warning and continuous monitoring. Continuous analysis of internal and external data produces early warnings for emerging risks, giving teams time to act before issues escalate.
Fraud and anomaly detection. In financial and operational contexts, generative AI detects anomalies and patterns associated with fraud, which is valuable in industries prone to it.
Regulatory compliance for risk documentation. In heavily regulated sectors, AI automates the documentation of risk assessments, mitigation plans, and compliance reports, keeping them aligned with evolving requirements.
The hard part of risk assessment is rarely the analysis. It is getting enough information to complete the picture in the first place. Once you have the picture, you can make informed decisions. Before that, you are guessing.
That is why a practical AI risk assessment for a team using LLMs in its product starts with a threat model built from real information: talking to the engineers and researchers who know how the system actually works, understanding where the model is used and what it touches, and only then enumerating weaknesses.
LLMs complicate this because they behave like databases that do not return what you expect. You put something in and get something interesting out. The controls have to account for that unpredictability.
The AI-specific risks that now enter your register
When an organization deploys LLMs in its product, a new set of risks belongs in the risk register. These are largely absent from generic AI-risk coverage. The five categories below map to their primary mitigating controls.
Technical and operational AI risk taxonomy
For depth on the technical side of these, see generative AI security risks and AI hallucinations in GRC. When the risk extends through vendors who themselves use LLMs, treat it as a specialized case of LLMs and third-party risk.
How does generative AI facilitate compliance?
Compliance is where AI's limitations become most consequential. Five areas, each with a different risk profile.
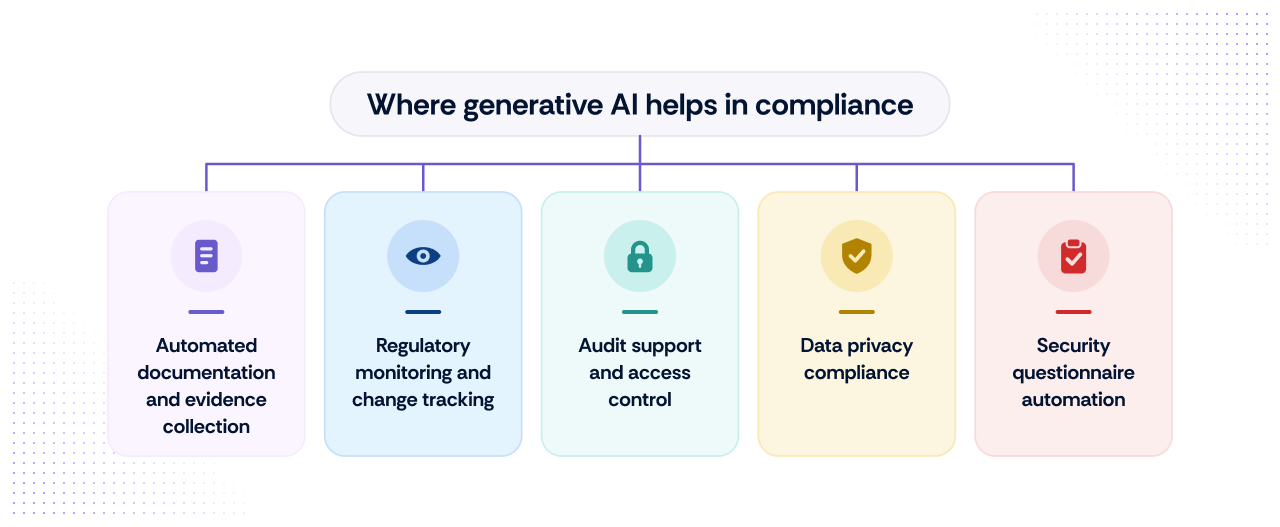
Automated documentation and evidence collection. The model streamlines creation of policy manuals, audit reports, and regulatory filings, and helps gather evidence across tools like Jira, Google Docs, and version control systems, reducing human error in compliance documentation.
Regulatory monitoring and change tracking. Scanning and summarizing regulatory changes is where AI earns its keep: flagging what changed and drafting a first-pass impact summary, so the team is not starting from a blank page.
Audit support and access control. AI prepares audit-related documentation and helps auditors access specific evidence without disrupting the team. For a compliance audit, it also helps enforce least privilege, limiting the data external auditors can reach to only what the review requires.
The audit evidence an ISO 42001 auditor asks for is unusually specific. In Scrut's own certification, the auditor reviewed an AI system impact assessment (distinct from a risk assessment in that it covers organizational, individual, and societal impact), an AI tool inventory, system documentation covering infrastructure and design rationale, and human-in-the-loop review records.
Preparing these before the audit, rather than reconstructing them under pressure, is the difference between a smooth review and a scramble.
Data privacy compliance. For GDPR, CCPA, and similar regimes, the practical value is in data discovery and classification: the groundwork that makes privacy documentation (DPAs, RoPA entries) something other than a manual archaeology project.
Security questionnaire automation. The model generates tailored responses and completes security questionnaires far faster than manual drafting.
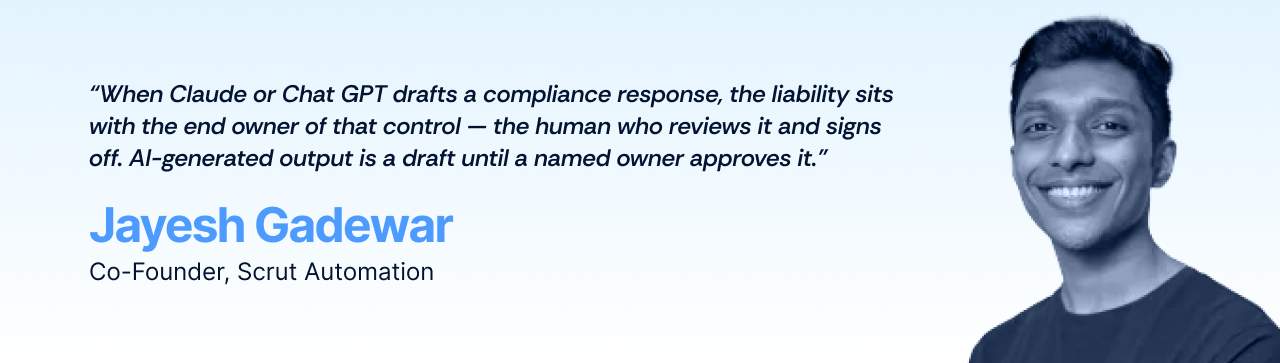
One question sits underneath all of this: when Claude or GPT generates a compliance response and it is wrong, who is liable? The cleanest way to think about it is the engineering parallel. If AI generates code, the responsibility still lies with the engineer who owns the service and approves the pull request.
Compliance is the same. AI-generated output is a draft until a named owner reviews it and signs off. That is also how you build trust in the output: not by trusting the model, but by guaranteeing there is always an accountable human who owns the control.
The comparison below shows how generative AI applies across all three pillars of GRC.
Operationalizing AI across governance, risk, and compliance (GRC)
For the broader context, see AI compliance.
Where generative AI in compliance delivers measurable value, and where it falls short
This is the most opinionated section in the piece, because practitioners want to know what actually works, not a features list.
Where AI delivers value today:
As a quality checker. The quality-checker use case is where AI delivers most consistently. Teams lean on it to sanity-check their own work: Is this policy up to the mark? Is this evidence good enough? It is a gatekeeper, not an author.
As a brainstorming partner. People use it to work through how a control applies in their org, what to prioritize, and how to fix something quickly, often getting the actual Terraform, script, or CLI command rather than a description of it.
For security questionnaire automation. Generating tailored responses and completing questionnaires is a clear, repeatable time saver. For the failure modes to watch, see security questionnaire automation.
Where expectations exceeded reality
Fully autonomous remediation disappointed because customers still wanted to approve changes themselves. Judgment-heavy or novel controls produced overconfident answers that experts had to unwind.
The accuracy threshold question
Nobody can give you the accuracy number. The question is wrong. What you actually need is a governance decision: for this specific use case, at what confidence level does AI output require mandatory human review before it goes anywhere, versus where can it serve as a low-stakes first draft? Set the threshold explicitly, per use case, and assign a named leader to own it.
Access governance for AI agents
When AI agents get access to systems, treat them the way you would any privileged identity.
Short-lived credentials and scoped permissions, not standing admin access. If you cannot model what an agent can touch, you cannot secure it. Building and presenting this well also supports customer trust.
An organized Trust Center that shows verified security and compliance information does more for buyer confidence than any single feature.
Generative AI risks specific to GRC teams
Every use case above assumes the AI deployment itself is reasonably secure. It usually is not, and the risks that emerge when it is not are specific enough to GRC workflows that generic AI-risk lists miss them.
Prompt injection in compliance workflows. Direct prompt injection involves a user deliberately manipulating the model. Indirect prompt injection is subtler: a good-faith operator's agent ingests malicious instructions hidden in external content.
Picture a compliance chatbot with access to your audit evidence store. A direct attack tries to make it reveal another customer's data. An indirect attack plants instructions in a document that the bot summarizes.
Security researchers have chained plugins together to make a model read a malicious web page, ingest hidden instructions, and exfiltrate data from a connected email account (a 2023 demonstration using ChatGPT's now-deprecated plugin architecture; the underlying indirect injection risk persists in any agentic tool-calling setup).
The mitigation is scoping: control what data sources the agent reaches, and gate any function calling behind real authorization.
Unintentional training on sensitive compliance data. Confidential data submitted to a third-party model can be trained on and resurface to another user. Samsung experienced this when employees inadvertently leaked sensitive internal data by pasting it into ChatGPT.
In a GRC context, the exposed data is PHI, confidential risk assessments, or customer contracts: exactly the material that carries regulatory and contractual weight.
Picture a compliance analyst pasting a draft vendor risk assessment into a third-party LLM to get a summary. The assessment contains client names, contract terms, and identified control gaps. If that model trains on the submission, those details become part of its knowledge base, potentially surfacing in responses to other users. Sanitize prompts and redact PII before anything reaches the model.
AI hallucinations in audit evidence. A model can produce a confident, well-formatted, factually wrong answer. In audit evidence, that is dangerous, because the output is convincing enough to be taken at face value. Anything an AI generates for an audit stays a draft until a named owner verifies it against the source. Treating a hallucinated citation as real evidence is how a control that looks compliant fails on inspection. See AI hallucinations in compliance.
Data poisoning and model integrity. Security researchers have demonstrated how a deliberately poisoned model can be nearly uploaded to a public model hub, a concrete example of how model poisoning enters the supply chain. Vet where your models come from before you trust their output.
Privacy regulation violations across jurisdictions. Deploying LLMs across regions triggers overlapping obligations under GDPR, the EU AI Act, and other regimes, and the regulatory picture is still fluid. The durable control is data minimization: collect and process the least personal data necessary, and get jurisdiction-specific legal review before deploying where local rules apply.
The register below reframes these as a GRC team would track them.
Operational risk taxonomy: Generative AI in GRC
For the vendor dimension, see AI vendor risk challenges, and for keeping this current as your deployment evolves, continuous AI risk management.
AI governance frameworks: NIST AI RMF and ISO 42001
Two frameworks come up in every serious AI governance conversation: NIST AI RMF and ISO 42001. They are often presented as alternatives. They are not. They complement each other.
NIST AI Risk Management Framework
The NIST AI Risk Management Framework is organized around four core functions: Govern, Map, Measure, and Manage. Govern establishes the policies and accountability structure. Map identifies where and how AI is used and the risks that follow. Measure evaluates those risks. Manage acts on them.
Like most NIST publications, it is a framework, not a prescription. It is comprehensive but high-level, and it deliberately does not tell you how to implement. It talks extensively about risk tolerance and risk appetite without giving you a road map for determining what those are for your organization: which is exactly the work a GRC team has to do itself.
That is a feature, not a gap. The framework structures your thinking and expects you to make confident decisions about what applies. It also sits well alongside the NIST Cybersecurity Framework and Privacy Framework, so treat the set as layered rather than separate. For implementation, see applying the NIST AI RMF.
ISO 42001
ISO 42001 is a management system standard. When Scrut went through certification, the structural similarity to ISO 27001 was immediately apparent: same clause architecture, same ISMS scaffolding. Much of that carries over directly, and many policy and role controls map cleanly across.
What required genuinely new work was the AI-specific material. The clearest example is the AI system impact assessment. Teams often assume it is a relabeled risk assessment. It is not. It assesses how the AI affects three distinct areas: the organization, the individuals using the system, and society (bias against a community, for instance).
Alongside it, an auditor expects an AI tool inventory, system documentation covering infrastructure, compute, and design rationale, and human-in-the-loop review evidence. You also have to determine which role your organization plays, whether provider, producer, or user, because that drives your statement of applicability. Scope matters too: you can bring only your AI system into the AI management system scope rather than your entire product, which keeps implementation focused.
One recurring friction: when you consume third-party foundation models from providers like Anthropic or OpenAI, the documentation burden shifts to tracking what those providers are doing with their models, and they change them at their discretion, without notice. What matters most, and what neither framework fully covers, is how you use those models: your infrastructure, your guardrails, your fail-safes.
When to certify vs. align
ISO 42001 certification is worth the investment when there is a trigger: a customer asks, a major product release adopts AI, or your business model requires third-party assurance. If your customers expect transparency and certified attestations, adopting a new technology and getting certified on your practices around it is usually enough to justify it.
In the absence of a trigger, aligning with the framework's controls without pursuing the certificate is often sufficient. For the full picture, see ISO 42001 vs. NIST AI RMF and the ISO 42001 implementation guide, or explore NIST AI RMF compliance.
Practical guardrails: What to implement before deploying generative AI in GRC
Here are five guardrails, each with what it looks like in practice.
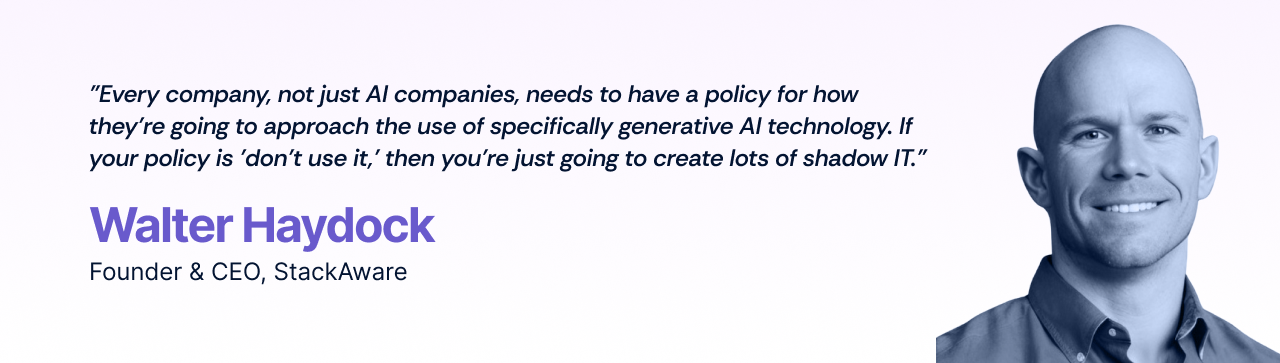
1. Policy before tools. Every company, not just AI companies, needs a policy for how it will approach generative AI. The catch: if the policy is "don't use it," you create shadow IT and inherit all the same problems plus new ones in asset tracking and data flows.
The policy has to define what is and is not acceptable use, then train people on it and establish a process for requesting new tools. A data classification policy is a natural companion, since it defines what data can go where.
2. Data minimization and prompt hygiene. Whatever goes into the LLM must be sanitized. Redact names, API keys, passwords, and IP addresses before data reaches a third-party model, and pseudonymize where you can. Understand each provider's data retention terms, which change and should be verified against current documentation rather than assumed.
3. Human-in-the-loop sign-off for all compliance outputs. No AI-generated compliance output goes anywhere without a named owner reviewing and approving it. Full stop. Everything else in this list is scaffolding around that principle.
4. AI tool inventory and monitoring cadence. Maintain an inventory of the AI tools in use, the same way you track vendors. The practical baseline is a scheduled reassessment every quarter, plus event-driven reassessment whenever something material changes: an authentication change, a major release, or a fundamental shift in how a feature works. Fold this into your compliance monitoring and AI for continuous compliance.
5. Access control and scope limitation for AI agents. Give agents short-lived credentials and scoped permissions, never standing admin access. If you cannot model what an agent can touch, you cannot secure it. Map that first.
Implementing generative AI in GRC: An 8-step roadmap
A common misstep is choosing a tool before defining the problem it should solve. This roadmap starts with scope and ends with audit readiness, so each decision builds on the one before it.
1. Define context and use case scope. Name the specific problem and the intended outcome before evaluating tools. "Improve security questionnaire turnaround time" is a context. "Use AI" is not. Context drives everything downstream, including your risk tolerance.
2. Establish an AI usage policy. Put the policy in place before deploying anything. A policy that says "don't use generative AI" does not prevent use. It moves use off your asset inventory. Define what is acceptable, what requires approval, and what is prohibited.
3. Select the deployment model. Choose between a third-party API and self-hosting. A third-party provider maintains security hygiene and patching for you but limits your visibility into data handling. Self-hosting gives you control and rollback but demands the resources to manage infrastructure and its own security risks. Neither is inherently riskier. The right choice depends on your data sensitivity.
4. Prepare and sanitize data inputs. Clean and structure the data you feed the model, and redact sensitive fields before they reach a third party. This step is where unintentional training and privacy violations are prevented.
5. Pilot test on non-sensitive workflows. Run the model against a small, low-stakes dataset first, for example, drafting internal policy templates rather than customer-facing audit responses, so you can evaluate accuracy before anything consequential depends on it.
6. Implement monitoring and logging. Put purpose-built AI observability in place, not just your standard application logging. Tools like Langfuse or LangSmith give you tool-call accuracy, cost, and latency in one view. Pair tracing with a PII-scrubbing layer. Otherwise, your observability tool quietly becomes your single biggest data-leak surface, because full prompt and response logs capture usernames, PII, and even access tokens.
7. Set a reassessment cadence. Quarterly baseline, event-driven on material changes. Name the person who triggers the out-of-cycle review, and document what "material change" means for your specific deployment before you need to invoke it, not in the moment.
8. Document for audit readiness. Maintain the AI tool inventory, system documentation, impact assessment, and human-in-the-loop records. A useful discipline: do not write internal controls you would not be able to follow, because an auditor will hold you to what you wrote.
For related roadmaps, see the GRC implementation roadmap and broader compliance automation guidance, plus context on how GenAI is reshaping GRC. To see this in practice, explore Scrut's compliance automation platform.
Summing up
There is no single verdict on generative AI in compliance. It delivers real, measurable value in defined, human-supervised use cases: quality checking, brainstorming, questionnaire acceleration. It creates real risk in autonomous, unsupervised ones. The line between the two is human judgment, and the teams getting value are the ones who kept it in the loop.
The regulatory direction is clear, even where the details are not. The EU AI Act entered into force in August 2024, with obligations phasing in from February 2025. A 2026 amendment pushed most high-risk requirements back to December 2027, and to August 2028 for AI embedded in regulated products. NIST AI RMF remains a voluntary reference framework.
ISO 42001 is starting to come up in enterprise security reviews as buyers ask for transparency and third-party assurance. Buyers have stopped asking whether vendors use AI. They now ask how that AI is governed.
The most important control is not technical. It is human accountability. A named person reviews, approves, and owns every AI-generated compliance output, and that single principle is what makes everything else in this article defensible to deploy.
Generative AI creates new content, text, images, code, by learning patterns from existing data. It differs from predictive AI, which forecasts outcomes from historical data. Generative excels at content creation. Predictive excels at estimating what happens next. Their failure modes differ too: predictive models drift, generative models hallucinate.
It streamlines policy creation, documentation, and board reporting, and keeps policies aligned with regulatory change. But it produces drafts, not implemented controls, and a policy document is not a functioning control. Data classification should be in place before deploying any tool with broad access to internal content.
It analyzes large datasets for early risk identification, improves assessment accuracy, and strengthens predictive modeling. Its limitation is novel or judgment-heavy risk, where it overpromises. The hardest part of risk assessment, getting enough information to complete the picture, still requires human legwork.
It automates documentation and evidence collection, tracks regulatory change, accelerates security questionnaires, and supports audits and data privacy work. Every output remains a draft until a named control owner reviews and approves it.
The specific challenges are prompt injection (direct and indirect), unintentional training on sensitive data that can resurface to other users, and hallucinations in audit evidence: confident output that is factually wrong. Add data poisoning and cross-jurisdiction privacy violations, and manage them with sanitization, human sign-off, and an AI tool inventory.