



- Operational risk management (ORM) is the process of identifying, assessing, and mitigating risks that arise from failed internal processes, people, systems, or external events, and it is distinct from strategic and financial risk.
- The four core pillars are risk identification, assessment, mitigation, and continuous monitoring.
- The primary objective is loss prevention through controls, not risk elimination, which is neither possible nor the goal.
- Most SMB risk registers fail because they are built once, misclassify severity, or conflate compliance risk with the full operational risk picture.
- Automation can surface and score high-priority risks, but human judgment stays non-negotiable for risk acceptance decisions and board communication.
Operational risk management is one of the few disciplines every scaling company eventually needs, whether or not anyone planned for it.
This guide covers what ORM is, how it differs from enterprise risk management, the process that makes it work, and the practitioner-level details that separate a living risk program from an audit artifact.
What is operational risk management?
Operational risk management is the systematic process of identifying, assessing, and mitigating risks that arise from failed or inadequate internal processes, people, systems, or external events. Its purpose is to reduce potential losses from day-to-day operations to a level the business can accept, not to eliminate risk entirely.
Where enterprise risk management chases risk-reward tradeoffs, ORM is loss-averse by design. It works backward from what could go wrong to the controls that contain it, rather than forward from an opportunity to a payoff. That orientation matters because it scopes ORM correctly: it is not audit-only thinking, and it is not the same as the broader risk framework it sits inside.
Practitioners increasingly distinguish three things that get conflated in early-stage programs: compliance risk, operational risk, and strategic risk. ORM owns the middle.
Four operating principles, drawn from U.S. military ORM doctrine and widely adopted in enterprise risk practice, keep an ORM program honest: accept risk when the benefits outweigh the cost; accept no unnecessary risk; anticipate and manage risk proactively rather than reactively; and make risk decisions at the right organizational level. These principles have aged well because they force a program to be deliberate about what it carries and who decides.
One shift worth noting: ORM used to run on an annual cadence, with a once-a-year interview or workshop feeding a static register. That model is fading. Practitioners now run continuous check-ins, revisiting risks whenever the business changes materially rather than waiting for a calendar date.
ORM vs. ERM: Where the line actually sits
ORM is built around losses you didn't choose. ERM is built around bets you did. The table below makes the distinction operational.
Some organizations use integrated risk management to reconcile the two into a single view. In practice, they almost never share a home. Financial and operational risks tend to sit under the CFO or COO, while IT and security risks live in the CISO's office, and true consolidation almost never happens, even inside Fortune 500 companies. It is worth wanting, but do not expect one register or one risk management framework to unify everything on its own.
Operational Risk Management (ORM) vs. Enterprise Risk Management (ERM)
Why ORM became a formal discipline
ORM did not start as paperwork. It started as doctrine. The U.S. Navy formalized operational risk management to keep decisions disciplined under pressure, and the financial sector followed as its own operational failures grew too expensive to leave informal.
The Basel Committee on Banking Supervision, established in 1974 by the central bank governors of the G10 countries, gave banks a shared vocabulary for operational risk. The COSO Internal Control Framework, published in 1992, moved internal control into a structured management responsibility. The Sarbanes-Oxley Act of 2002 attached personal accountability to control failures in public companies. Each one moved operational risk from an informal concern into a governed function with owners, evidence, and review cycles.
The most recent push is regulatory resilience. The Digital Operational Resilience Act (DORA) extends operational resilience obligations to financial entities and, critically, to their ICT third-party providers, which is exactly the exposure that tech-native SaaS and fintech companies carry. For teams building a GRC implementation from scratch, this history is not trivia.
The current version of that pattern is AI adoption. Copilot deployments at financial institutions have exposed access-control weaknesses that managers assumed were theoretical. Employees had permissions their roles were never meant to carry, and the tool made those permissions visible overnight.
Existing ORM frameworks did not anticipate this category of exposure, and practitioners are building controls for it now. The through-line is this: every time the business environment changed faster than existing controls could track, regulators and organizations formalized ORM in response. AI is just the latest iteration.
Operational risk examples
Operational risks span a wide range of failure modes. The table below covers the standard categories, with two that the 2025-2026 landscape made unavoidable.
Operational risk: Taxonomy and examples
The examples that catch tech-native companies off guard rarely appear on a standard list. A company expanding into a new country often faces trickle-down operational risks: data localization requirements that force controls to be re-architected, or payment-law changes that alter how the product works. Foreign exchange rate swings can quietly blow up the budget for controls you pay for in USD.
A cloud provider outage in a single availability zone can become a business continuity event if you were not architected for it. These are operational risks with a direct effect on your third-party risk and cybersecurity risk posture, and none of them show up on a standard SOC 2 register.
The components of operational risk management
Four pillars structure operational risk management: identification, assessment, mitigation, and monitoring. Identification is the work of surfacing what could go wrong before it does, using scenario analysis, loss-data review, and workshops with the people who actually run the processes.
Assessment scores each risk on likelihood and impact so you can prioritize. The output is a risk register with named owners, not a scary list. Getting the right people in the room matters more than the scoring method. A risk assessment built on incomplete information produces a bad register no matter how elegant the math.
Mitigation is where the register becomes a decision log. Each risk gets one of four treatments, reduce, transfer, avoid, or accept, and the choice has to be documented, not assumed.
Monitoring tracks whether controls keep working over time, using key risk indicators and periodic residual-risk checks. This is the pillar that decays first, because there are always new fires and reassessing a control you already implemented rarely feels urgent.
Useful KRIs cluster by category: HR (unplanned attrition in critical roles), Process (time-to-patch, failed change rate), and Technology (percentage of assets outside patch SLA). A good Key Risk Indicator tells you a risk is trending toward its threshold before it materializes, not after.
Two concepts anchor the monitoring conversation and are worth keeping distinct. Inherent risk vs residual risk separates raw exposure from what remains after controls. Risk appetite vs. risk tolerance separates the strategic declaration from the operational trigger that makes it enforceable.
Governance parameters: Risk appetite vs. risk tolerance
What is the primary objective of operational risk management?
The primary objective of operational risk management is to minimize losses from failed processes, people, systems, and external events by reducing risk to an acceptable level. It is not to eliminate risk, which is impossible, but to prioritize and contain the risks most likely to hurt the business.
You cannot eliminate risk without eliminating the business. If you want zero cyber risk, turn off all your technology, and you also turn off the company. Risk is inherent to operating. The job is prioritization and remediation sequencing: deciding what gets fixed first and what the business knowingly accepts.
For the treatment options that follow from this objective, see our guides to risk mitigation strategies and the effective risk management process.
Types of operational risk: A category breakdown
The table below consolidates the standard failure modes, with an AI/model risk row that the current landscape makes non-optional.
Core operational risk categories and descriptions
People risk is not just fraud or error. It includes key-person dependency, where too much institutional knowledge sits with one engineer, and the talent volatility that peaks whenever hiring markets tighten. Technology risk now includes a category most frameworks did not anticipate.
As AI tools spread through organizations, a copilot can expose access permissions that managers assumed employees never had, turning latent access-control weaknesses into live operational risk. Tech-native companies need to watch this closely. See our guides to AI risk management and third-party and vendor risk.
How to implement an operational risk management program: a step-by-step process
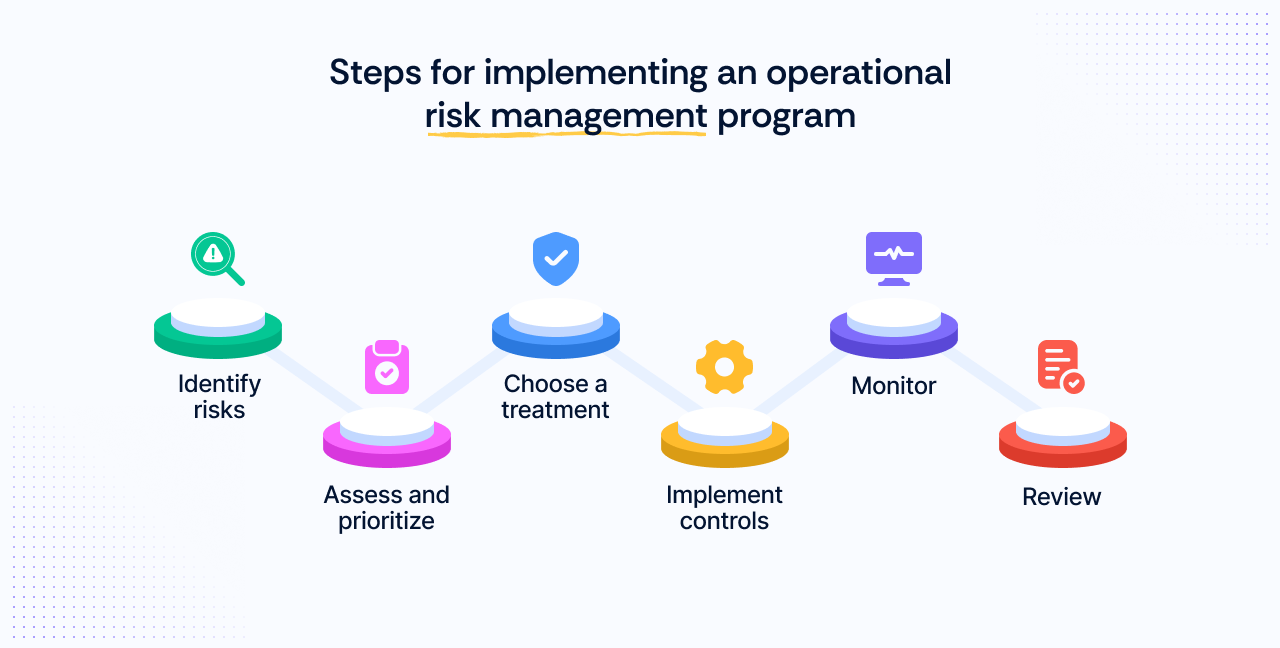
Step 1 - Identify risks. Combine workshops with structured techniques: scenario analysis to explore how failures cascade, and loss-data analysis to learn from past incidents. Talk to people across functions, not just security. One person rarely understands how the whole company works. The goal is not an exhaustive list but a defensible one that captures the risks with the greatest potential impact.
Step 2 - Assess and prioritize. Score likelihood and impact using a risk matrix, and produce a risk register with named owners for each entry. Prioritization is the real deliverable. Most companies end up with a cluster of high-impact, medium-to-high-likelihood risks and have to make honest trade-offs about which one is most likely to hurt them first.
The risk matrix is a tool for that conversation, not a substitute for it. A score of 12 means nothing if the people in the room have not agreed on what a 12 requires them to do.
Step 3 - Choose a treatment. Every prioritized risk gets one of four treatments. Accepting a risk does not mean doing nothing. Accepted risk materializes constantly, as credential stuffing on a login page or transaction fraud on a checkout flow, and the business proceeds because the benefit outweighs the cost.
When it does, the documentation and escalation path have to be clear so the decision is traceable. The practical test: does the control cost more than the loss it prevents? If yes, it rarely earns its place.
Risk treatment options and application guidelines
Step 4 - Implement controls. Controls fall into three functions: preventative (stop the event, such as enforced MFA), detective (spot it, such as alerting on privileged access), and corrective (fix it, such as an incident runbook). Documentation is not implementation. A well-documented control that nobody actually operates catches nothing.
The practical test: does someone in the company know they own this control, and can they show you the last time they ran it? If the answer to either is no, the control exists on paper only. A risk control matrix maps controls to risks and helps expose gaps.
Step 5 - Monitor. Track control effectiveness with KRIs and watch for drift. This step connects directly to residual risk: after a control goes in, you are supposed to reassess whether the remaining exposure actually dropped as expected. A practical forcing function: when a control goes in, set a calendar reminder 90 days out to ask one question. Did the residual risk score actually drop? If nobody checks, the control exists on paper and the register lies.
Step 6 - Review. Match review frequency to how fast the business actually changes. For most SMBs, a defensible minimum is a quarterly check-in question, "has enough changed to revisit this?", and a comprehensive top-to-bottom review at least once a year. The register is a byproduct of that assessment cadence, not a substitute for it. For treatment design, our guide to risk mitigation strategies goes deeper on control selection.
The risk register in practice
A risk register is a strategic document of the organization's top risks, each with a named owner, likelihood and impact scores, a treatment decision, and a review date. It is not a vulnerability tracker and it is not a compliance checklist. The register is not a security Jira board. Vulnerability management belongs in its own pipeline.
Most risk registers fail for predictable reasons. They get built once for an audit and never updated. They get polluted with whatever someone wanted resources for, because people learn to use the register as a secret escalation path: add a pet issue, get attention, get budget. And they get populated with softball items that are easy to define rather than the real weaknesses the business has to manage because they are baked into how the product works.
Size is the tell. The register should only be as big as the team is genuinely willing to act on. According to Nicholas Muy, CISO at Scrut Automation, the risk register at a multi-billion dollar company he previously worked at rarely exceeded roughly 100 entries because the goal was strategic, not exhaustive.
If everything is a strategic risk, nothing is. To triage a bloated register, sort by impact to the business rather than by how interesting or how frequent each item is, and be honest about whether an item ever went through a real risk assessment or just got shoved in.
For the mechanics, see how to create a risk register, risk register maintenance, and the shift from point-in-time to continuous risk management.
Operational risk vs. compliance risk: Where SMEs get blindsided
Tech-native companies routinely mistake compliance risk for the whole risk picture. A company that runs SOC 2 or ISO 27001 often believes it has covered operational risk, but a security compliance framework only addresses a subset of operational exposure.
The trap is understandable. Compliance risk, really audit risk, is tangible and urgent because there is a deadline and a customer asking. Operational and strategic risks can seem far away and abstract until they are not. So teams pour hours into evidence collection, and the risks that fall outside the framework go unmanaged: key-person dependency, geographic expansion (data localization mandates, payment-law changes), business continuity failures, and cloud dependencies on a single availability zone.
There is also a hidden cost. Every hour an engineer spends chasing audit evidence is an hour not spent monitoring the CI/CD pipeline or watching for outages. Compliance-only thinking creates real opportunity cost, and the operational risk it displaces can be larger than the audit risk it addresses. For the full distinction, see compliance risk management, compliance vs information security, and cyber risk management frameworks.
Challenges in operational risk management and how to overcome them
The table maps the most common failure modes to practical fixes.
Frameworks and quantitative models are the crunchy side of risk management. Culture, stakeholder empathy, and control-ownership conversations are where most programs actually fail. Documentation does not equal implementation.
The practitioners who make risk programs stick tend to do three things: start small with incremental improvements rather than sweeping mandates, listen before talking so they understand why a team resists a control, and bring genuine empathy to control-ownership conversations.
A control nobody has bought into is an academic exercise, no matter how well it is documented. Risk management automation helps with the crunchy side, but it cannot substitute for the human one.
Risk communication and board reporting
The uncomfortable truth about board reporting is that most boards do not care about the details. They care that nothing bad is going to happen. And every board cares about something different, so there is no universal format you can copy.
What lands is narrative, not a dollar figure. Tie each significant risk to a specific business commitment leadership already signed off on, rather than presenting a quantified loss estimate that invites endless methodology debate about where the number came from. A risk anchored to a promise the CEO personally made is harder to wave away than a spreadsheet cell.
Stop presenting the things that create confusion: raw vulnerability lists, KRI data without context, heat maps with no story attached. And treat the board update itself as a product. Ship a version, collect feedback, iterate, the same way you would run product research, until you find the format your specific board actually finds actionable. For more on the format problem, see risk reporting, communicating your security posture, and the broader GRC management benefits.
Automating operational risk management: What works and what doesn't
Automation earns its place in specific parts of ORM: evidence collection, control monitoring, continuous testing, and surfacing high-confidence signals on the risks that matter most. The strongest version does not try to score every risk. It identifies the critical items, often by learning from a large network of similar organizations, flags them, and leaves the final classification to a human. Customers rarely want a fully automated score for everything. They want to know which signals you are actually monitoring.
What cannot be automated is judgment. Risk acceptance decisions, stakeholder communication, deciding whether an item belongs on the register, and the board narrative all stay human. Automation that produces heat maps without helping you understand the underlying risk is reporting theater. It is indistinguishable from asking a chatbot to generate a heat map and filling it with random values.
There is also a gap automation quietly exposes. After controls go in, residual risk rarely gets reassessed in small organizations, because there are always new fires. Automation that keeps the residual-risk question in front of you, honestly and defensibly, is genuinely useful.
Automation that hides it behind a green dashboard is worse than nothing. See our guides on automating risk management, GRC automation, and continuous compliance.
How Scrut helps you run operational risk management
Scrut's risk management platform maps to the ORM process described in this guide rather than bolting compliance features onto it.
- Identification and assessment: Start from a categorized template of common operational risks, then score likelihood and impact to build a prioritized register with named owners, so Step 1 and Step 2 produce a working artifact, not a blank spreadsheet.
- Integrated risk view: Bring operational, IT, and vendor risks into one place so the fragmentation that normally hides exposure gets easier to see, supporting the integrated risk management goal.
- Automation with judgment retained: Automate evidence collection and control monitoring while leaving classification and acceptance decisions to your team, which is exactly where human judgment belongs.
- Risk control matrix: Map controls to risks so gaps surface before an auditor or an incident finds them, connecting Step 4 to Step 5.
- Continuous monitoring: Track control effectiveness and residual risk over time through dashboards, so the pillar that usually decays first stays alive.
For a deeper walkthrough, see how Scrut helps with risk management.
Final thoughts
ORM is a prioritization discipline, not a protection guarantee. The goal is knowing which risks get addressed first and which the business has consciously chosen to carry. The risk register is only as valuable as the discipline behind it. And the acceptance decisions and board conversations? Those stay yours, regardless of how much you automate.
Ready to build a risk program that runs continuously instead of resurfacing every audit cycle? See how Scrut's risk management platform supports the full ORM process, or start with our risk management strategy guide to map your next steps.
Operational risk management (ORM) is the systematic process of identifying, assessing, and mitigating risks from failed internal processes, people, systems, or external events. Its aim is to reduce operational losses to an acceptable level rather than eliminate risk entirely.
The primary objective is loss prevention. ORM works to minimize losses from operational failures by prioritizing and containing the risks most likely to harm the business. It does not seek to eliminate risk, which is impossible. It reduces risk to a level the business can accept.
ORM manages unintentional risk from day-to-day operations and is loss-averse. Enterprise risk management is broader and opportunity-seeking, covering strategic bets like mergers and new products. Some organizations use integrated risk management to reconcile the two.
The four pillars are identification, assessment, mitigation, and monitoring. Supporting practices include risk and control self-assessments, key risk indicators, incident recording, and the appetite-versus-tolerance distinction that governs when action is triggered.
Match the cadence to how fast the business changes. For most SMBs, a defensible minimum is a quarterly check-in asking whether anything has changed meaningfully, plus a comprehensive top-to-bottom review at least once a year.