

Choose risk-first compliance that’s always on, built for you.
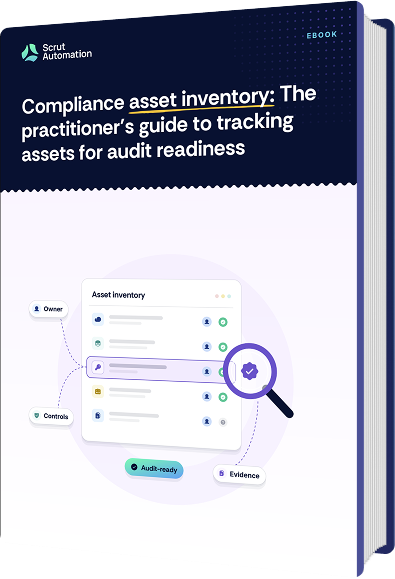
Learn how to build an asset inventory that holds up through audits, framework consolidation, and tool migration.
Your program is in good shape. Controls are documented, policies are approved, and the evidence folders are filling up on schedule.
Then the auditor asks to see a tool they noticed in a screenshot. A support team signed up for it a few months ago and expensed it. It isn't in your asset inventory. Nobody on the compliance team has heard of it.
The auditor makes a note and moves on. From that point on, they stop treating your inventory as reliable. Every control that depends on knowing what you have, from access reviews to vendor assessments, now needs more proof than it did an hour ago.
Or you are halfway through consolidating frameworks onto one GRC platform. Three teams have been keeping their own asset lists. The same database appears under three names, two of them with different owners, and one with no control mappings at all. You won't know which version is right until someone asks.
This is the inventory problem most compliance leaders hit without seeing it coming. Not a breach. Not a failed control. Just the realization that the list everything else depends on is less complete than everyone assumed.
That gap, between the assets you run and the assets you can account for, is what this guide is about. Use this guide before your next audit kickoff, framework consolidation, or GRC tool migration.
The 10-question diagnostic below will show you where your inventory stands and where an auditor's first sample is likely to land.
Score each item: 0 = not in place, 1 = partially in place, 2 = fully in place with evidence.
| # | Can you do this today, without asking another team? | Score (0 to 2) |
|---|---|---|
| Completeness and discovery | ||
| 1 | Produce a complete list of the SaaS tools in use, including the ones IT didn’t buy | |
| 2 | List every cloud account and resource, including test instances and storage buckets | |
| 3 | Account for browser extensions, third-party integrations, API keys, and service accounts | |
| 4 | Detect a new cloud resource or SaaS sign-up without someone reporting it | |
| Ownership | ||
| 5 | Name a person, not a team, who owns each asset | |
| 6 | Reassign an asset’s owner as soon as someone changes roles or leaves the company | |
| Data, controls, and evidence | ||
| 7 | Show the data sensitivity level of every asset that holds company or customer data | |
| 8 | Show which controls each asset is in scope for | |
| 9 | Show which frameworks each asset maps to, from a single inventory | |
| 10 | Pull the evidence for any asset an auditor samples | |
| Keeping records current | ||
| 11 | Show when each asset record was last verified | |
| 12 | Show when each asset entered the environment and who approved it | |
| 13 | Keep the inventory accurate across an audit observation period without a pre-audit cleanup | |
| AI tools and agents | ||
| 14 | List the AI tools and agents in use, with the data they can reach and the actions they can take | |
| 15 | Show whether a person approves an AI agent’s actions before they take effect | |
| 16 | Name an owner and a last review date for every AI tool | |
| Consolidation and reporting | ||
| 17 | Reconcile your inventory across every tool and spreadsheet it lives in today | |
| 18 | Give every asset one ID, so the same asset never appears twice under different names | |
| 19 | Confirm that owners, control mappings, and evidence links carried over in your last tool or framework migration | |
| 20 | Report unowned, stale, and unmapped assets to leadership without building the report by hand | |
0 to 16
Your inventory is reactive. An auditor’s first sample is likely to find an asset you can’t account for.
17 to 27
The foundations are there, but gaps will show under sampling. A focused push on ownership and discovery closes most of them.
28 to 35
Operationally solid. Focus on keeping records current and protecting them through consolidation or migration.
36 to 40
Your inventory is a trusted system of record. Use it to shorten audit prep and de-risk framework consolidation.
Early inventories are built by hand, and that works for a while. A small IT team approves every tool. Engineering knows which cloud accounts exist. Someone updates the spreadsheet before each audit.
Growth changes the math. Employees sign up for tools with a work email and expense them. Engineers spin up resources for a test and move on. Teams adopt AI assistants faster than anyone can review them. The environment changes every day, and the inventory changes when someone remembers.
Inventories rarely fail all at once. They break in three predictable ways.
Break 1
Completeness: assets in use that were never recorded
Break 2
Ownership: assets on the list that nobody is accountable for
Break 3
Staleness: records that were right once and have drifted since
The most visible failure is the asset that isn't there. A SaaS tool nobody approved, an orphaned storage bucket, a browser extension with access to company email. When an auditor finds one, the problem isn't the single missing row. It's that they can no longer trust the list.
Completeness problems are usually staleness problems in disguise. The inventory was complete when it was built. It just couldn't keep up with how quickly the environment changed afterward.
"It's almost always completeness caused by staleness. Teams spin up new SaaS tools or cloud instances every day. If you rely on manual updates, your list is outdated the second you hit 'save.'"
Aditya Parab, Lead Product Manager, Scrut Automation
An asset with no owner is an asset nobody is checking. When the auditor asks who owns a sampled system and the answer is “engineering” or a long pause, they hear that access, data handling, and review for that asset are probably unmanaged too.
Ownership has to land on a person. A team name feels accountable, but nobody on the team is responsible for keeping the record current or answering for it in fieldwork.
For a SOC 2 Type II report, the auditor tests whether controls operated across the entire observation period. An inventory that was accurate at kickoff and untouched for months doesn't support that. Neither does an owner who left the company in the second quarter but is still listed against a dozen assets.
Start of the observation period
The inventory matches the environment
Early in the period
New SaaS sign-ups and test instances appear, and not all of them are logged
Mid-period
Owners change roles or leave, and their records still list them
Fieldwork
The auditor samples from across the period and finds the gaps
Spreadsheets are a reasonable place to start. The question is when they stop keeping up.
In Aditya Parab's experience as Lead Product Manager at Scrut Automation, spreadsheets work for roughly the first 50 employees and break down somewhere between 200 and 500. At that stage, employees are expensing new SaaS tools every day. For a compliance leader trying to consolidate frameworks at that size, the spreadsheet is a blind spot and a compliance liability.
 A spreadsheet works when |
 It breaks down when |
|---|---|
| A few people approve every tool | Employees buy and expense tools on their own |
| You run one framework | Several frameworks each have their own list |
| Someone updates it when an asset changes | Assets change faster than anyone can log them |
| The auditor needs a point-in-time list | The auditor needs to see when assets entered the environment and who reviewed them |
The cost of hitting that ceiling during an audit is real. Aditya Parab has seen companies lose three to six weeks, and sometimes push an audit into the next quarter, when the inventory is the reason fieldwork stalls. Auditors hand the spreadsheet back and pause until the team can show where its data lives. Any sales deal waiting on that certification waits with it.
That's not a tooling problem. It's a revenue problem.
An IT asset list tells you what you have. A compliance-grade inventory tells an auditor why each item is controlled.
The difference is the connections. A compliance-grade inventory links every asset to its owner, the data it holds, the controls it falls under, the frameworks those controls serve, and the evidence that proves they work.
If an auditor picks any asset at random, you should be able to follow that chain from end to end.
Both major frameworks ask for this. SOC 2 identifies and manages the inventory of information assets as a focus under CC6.1. ISO/IEC 27001:2022 Annex A control 5.9 requires an inventory of information and other associated assets, including their owners.
In practice, a compliance-grade inventory captures a consistent set of fields for every asset:
| Field | What it represents |
|---|---|
| Asset ID and category | A unique identifier and the type of asset (cloud resource, SaaS application, data store, AI tool, and so on), so the same asset is never recorded twice. |
| Named owner | The person accountable for keeping the record current, confirming access, and answering for the asset during an audit. |
| Data held and sensitivity | What data lives in or passes through the asset, classified using your data classification policy (for example: public, internal, confidential, restricted). |
| Controls in scope | The controls that apply to the asset, such as access review, encryption, or change management. |
| Frameworks | Every framework the asset is in scope for, recorded on the same record rather than in separate lists. |
| Evidence location | Where to find proof that those controls operate. |
| Discovery source and approval status | How the asset was found and whether it has been reviewed and approved. |
| Last verified date | When the record was last confirmed as accurate, so stale entries are visible. |
This structure is what turns a list into a system of record. Without the connections, the inventory can't support the controls built on top of it.
Laptops and servers are rarely the problem. Audit findings come from assets that never went through procurement, or that nobody thinks of as assets. A simple rule closes most of these gaps: if an employee can use it to process or store company data, it's an asset, and it needs to be tracked.
| Asset category | Why it gets missed |
|---|---|
| Unapproved SaaS applications | Signed up for with a work email and expensed, without passing through IT |
| Orphaned cloud resources | Created for short-term work and never removed or reassigned |
| Browser extensions and third-party integrations | Installed by individuals, often with broad permissions to email or files |
| API keys and service accounts | Credentials rather than tools, so they rarely feel like assets |
| Code repositories | Treated as engineering territory rather than compliance scope |
| Data stores, replicas, and backups | Forgotten once they are set up and running |
| AI chatbots, assistants, and agents | Adopted quickly by individual teams, often before any review |
A standard SaaS tool mostly stores data. An AI agent can act on it. It can send emails, update records, or make decisions based on what it reads. That difference changes what the inventory needs to capture.
If your teams use AI in engineering, support, analytics, or internal productivity, your inventory should answer two questions for each tool: what can it see, and what can it do?
| Field | What it represents |
|---|---|
| Data scope | What internal company or customer data the model is trained on or allowed to read. |
| Action permissions | What the agent is authorized to do on its own, such as sending emails or modifying databases. |
| Human approval | Whether a person reviews or approves the agent's actions before they take effect. |
| Provider and version | Who supplies the model and which version is in use. |
| Owner and review date | Who is accountable for the tool and when its access and permissions were last reviewed. |
"A standard SaaS tool generally just stores data; an AI agent actively makes decisions based on it, which radically shifts your security risk."
Aditya Parab, Lead Product Manager, Scrut Automation
If you are working toward ISO/IEC 42001, these records also give you a practical starting point for defining which AI systems your AI management system covers.
By the time a company reaches 200 to 500 employees, many compliance leaders are managing more than one framework. They're running SOC 2 and ISO 27001 side by side, with HIPAA, PCI DSS, or GDPR in scope for parts of the business. And many are consolidating that work onto a single platform at the same time.
This is where inventories quietly multiply. Each framework effort builds its own asset list. Each list drifts on its own schedule. By the next audit cycle, audit prep has turned into reconciliation, and the inconsistencies you miss are the ones the auditor notices.
The fix is structural. Record each asset once, and tag that record with every framework it is in scope for. SOC 2 and ISO 27001 ask for overlapping information, so a single well-built record can serve both.
| Expectation | SOC 2 | ISO/IEC 27001:2022 |
|---|---|---|
| Where the inventory requirement sits | CC6.1 point of focus on managing the inventory of information assets | Annex A 5.9, inventory of information and other associated assets |
| Ownership | Supports access decisions for each asset | Owners are named in the control text |
| Classification | Supports protecting assets based on the data they hold | Annex A 5.12, classification of information |
| Fields that serve both | Named owner, data sensitivity, controls in scope, framework tags, evidence location, last verified date | |
When another framework comes into scope, add it as a tag on the same records rather than starting a new list, and check that framework's own language for any additional fields it expects.
Consolidating GRC tools is where inventories are most likely to lose information. The risk isn't that assets disappear outright. It's that they arrive in the new system incomplete, and nobody notices until an auditor samples one.
The same asset often appears under different names in different sources. Owners recorded in one tool don't always match user accounts in the next. Control mappings and evidence links don't always carry across. AI tools are a common blind spot, because they may only appear in one team's list, such as security's or procurement's.
| Step | What it protects against |
|---|---|
| Export every source, including team spreadsheets | Assets that only exist in one team's list |
| Match records across sources and assign one ID per asset | The same asset being migrated two or three times |
| Merge duplicates and record where each one came from | Conflicting owners or classifications with no way to resolve them |
| Confirm owner, sensitivity, mappings, and evidence links on every record | Records that arrive in the new system incomplete |
| Compare record counts before and after the move | Silent losses that only appear during fieldwork |
| Keep the old source read-only until every gap is closed | Losing the only copy of the original data |
Reconciliation adds time to the migration plan. It also decides whether the consolidation reduces audit effort or creates a new set of findings.
Most teams start building an inventory by writing down what they believe they have. That order creates rework. Discovery almost always turns up assets that nobody listed, and the documentation has to be revisited. A better sequence starts with what is actually running.
Discover what's in use
Consolidate into one source
Assign named owners
Tag data sensitivity
Map to controls and frameworks
Monitor continuously
Discover what's in use. Turn on automated discovery for logins, cloud resources, and SaaS sign-ups so the inventory reflects what employees actually use, not only what IT bought.
Consolidate into one source. Bring spreadsheets, wiki pages, and tool exports into a single inventory with one version and one timestamp.
Assign named owners. Attach a person to every asset. That person keeps the record current, confirms who has access, and answers when the auditor asks.
Tag data sensitivity. Classify each asset using your data classification policy. The tag decides which controls apply and how closely the asset is reviewed.
Map to controls and frameworks. This step lets an auditor trace from a control requirement to the assets it covers and the evidence behind it.
Monitor continuously. Set alerts for new cloud resources, new SaaS subscriptions, new third-party integrations, and departing employees who still own assets. Discovery isn't a one-time project. It's what keeps the other five steps true.
"Human processes will always lag behind engineering and employee speed."
Aditya Parab, Lead Product Manager, Scrut Automation
Auditors don't expect a perfect inventory. They expect a reliable one. Good enough means you can prove you have a reliable, repeatable way to discover assets, assign an owner, and know whether sensitive data lives there.
Teams often over-invest in the wrong places, tracking every minor configuration change or version number by hand instead of answering the core question for each asset: who owns this, and is it secure?
| Put your effort here |
Don't over-invest here |
|---|---|
| A discovery method that you can show the auditor | Logging every minor configuration change by hand |
| A named owner on every asset | Tracking version numbers in a spreadsheet |
| Sensitivity tags on every asset | Custom fields for metadata nobody uses |
| Links from assets to controls and evidence | Detailed descriptions for low-risk assets |
| A record of when each asset was last verified | Rebuilding the inventory from scratch before each audit |
Auditors typically test a sample, so the practical question is whether any asset they pick has a complete record. You can find out before they do.
Pick 10 assets at random, across different categories. For each one, try to answer five questions using only your inventory, without opening another system or messaging IT.
| Question | What a gap here tells you |
|---|---|
| Who owns it? | Accountability for the asset is unclear |
| What data does it hold, and how sensitive is it? | You can't show which controls should apply |
| Which controls cover it? | The asset sits outside your control framework |
| Which frameworks is it in scope for? | Framework inventories may be drifting apart |
| Where is the evidence? | Fieldwork will slow down on this asset |
Any question you couldn't answer from the inventory alone is a gap an auditor could find.
Inventory maturity doesn't show up in the inventory itself. It shows up when someone outside the compliance team needs an answer.
Auditors sample assets during fieldwork
Framework or tool consolidation tests every record
Leadership asks where the risk sits
In each of these moments, the difference between a static list and a working system of record is easy to see.
The auditor sends a sample of assets and asks for the supporting records.
With a static inventory, the request turns into a scramble. The compliance team searches the spreadsheet, finds two assets missing and three with outdated owners, and starts messaging IT and engineering for answers.
Some of the evidence lives in shared folders, some in screenshots, some in someone's memory. Fieldwork slows down while the team assembles it, and the auditor starts expanding the questions.
With an operational inventory, every sampled asset already has an owner, a sensitivity tag, mapped controls, and an evidence location. The team confirms the records rather than reconstructing them. New assets discovered during the observation period are already in the inventory, with the date they were added and who reviewed them.
The audit moves from evidence collection to verification.
You are moving SOC 2, ISO 27001, and a new framework onto one platform. With separate inventories, the migration exposes every inconsistency at once. The same assets appear under different names. Owners conflict. Control mappings exist in one source and not another. The team either migrates the mess and inherits it, or pauses the project to clean it up under deadline pressure.
With a single inventory and a reconciliation step built into the plan, each asset arrives in the new system once, with its owner, classification, mappings, and evidence intact. Record counts are compared before and after the move. The consolidation reduces audit effort instead of creating new findings.
See how CometChat consolidated SOC 2, ISO 27001, GDPR, and HIPAA into a single compliance program and met its ISO recertification deadline despite a compressed migration timeline.
Your CISO or CFO asks a simple question: Where is our audit risk right now?
With a static inventory, the honest answer is that nobody knows until the next audit. Building a coverage view means pulling the spreadsheet apart by hand.
With an operational inventory, the answer is a short report: how many assets are tracked, how many have no named owner, how many haven't been verified recently, which AI tools are overdue for review, and which migration records still have gaps. Leadership sees the risk in the same terms the auditor will, before the auditor does.
That is what it means for an inventory to work for the people above you as well as the people maintaining it.
A compliance asset inventory isn't measured by how many rows it has or how detailed each one is.
It's measured by whether you can answer three questions about any asset, on any given day, without an emergency:
What is it? Who owns it? Can we prove it's under control?
Compliance leaders who handle audits, consolidations, and migrations smoothly treat the inventory as the system of record everything else depends on. The ones who struggle find out during fieldwork that the list they trusted was missing the asset the auditor picked.
That gap is closable. Discovery keeps the inventory complete, named owners keep it accountable, and continuous monitoring keeps it current. The earlier you put those in place, the more every audit, framework, and migration that follows will benefit.
Book a demo to see how Scrut helps you discover assets, assign every one a named owner, and map it to the controls and frameworks it falls under.

With Scrut, your security program isn’t just about keeping pace; it’s about setting the pace. Embrace the new kind of GRC that fuels growth and resilience.