Choose risk-first compliance that’s always on, built for you.


For security and compliance leaders whose programs pass every audit but still trigger fire drills. A research-backed whitepaper on why point-in-time compliance is failing and what replaces it.
Over the past decade, compliance has evolved from a back-office obligation into a core pillar of organizational trust.
Frameworks such as SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS, SOX, and emerging regulations like DORA are no longer peripheral requirements. They now sit directly on the critical path for enterprise sales, partnerships, geographic expansion, and long-term business viability.
Despite this shift, most compliance programs remain designed as point-in-time efforts rather than durable systems.
Organizations pass audits, obtain certifications, and satisfy formal requirements, yet continue to experience repeated findings, prolonged audit cycles, operational disruption, and growing skepticism from customers and partners.
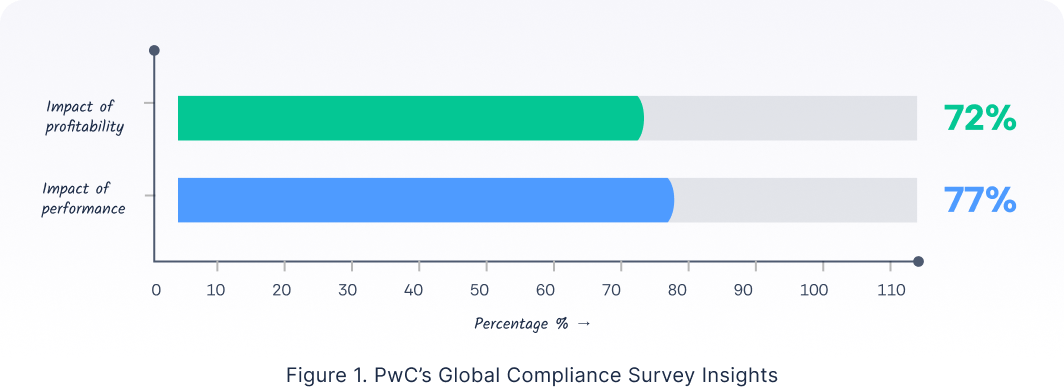
The scale of this challenge is substantial. According to PwC’s Global Compliance Survey 2025, 77% of senior leadership teams report that the sheer complexity of compliance is generating a tangible negative impact on organizational performance, while 72% indicate that escalating regulatory demands have directly compromised business profitability.
SOC 2 has made this gap particularly visible. Because it intersects security, operations, engineering, sales, and customer trust, SOC 2 often becomes the first framework where organizations feel the strain of manual processes, fragmented tooling, and reactive workflows.
As compliance becomes more closely tied to revenue and reputation, a challenge has emerged across the ecosystem: symbolic compliance. Reports are increasingly used to unblock deals or meet contractual expectations, while the underlying systems that those reports are meant to represent receive less scrutiny.
In this environment, possessing a compliance report no longer guarantees meaningful assurance. Buyers, auditors, and regulators are beginning to look beyond the presence of certifications to assess how compliance is actually achieved and maintained.
This report introduces Compliance Quality as the missing lens: a way to evaluate whether compliance programs are built to withstand growth, change, and scrutiny, not just survive the next audit.
If compliance requires a coordinated push before every audit → your system is likely point-in-time, not continuous.
Modern compliance operates under a fundamental tension. Audits are designed to evaluate controls at a specific point in time, while organizations operate in environments defined by continuous change.
Cloud infrastructure evolves weekly, access models shift as teams grow, vendors are added and removed, and deployment cycles accelerate.
Compliance, however, is still largely assessed as a snapshot. Compliance officers themselves worry about what they can’t see between audits. This mismatch has a cost.
In NAVEX’s 2025 State of Risk & Compliance Report,
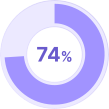
According to CUBE’s Cost of Compliance Report 2025, 74% of organizations report that implementing new regulations can take more than a year. These delays and rising costs compound as regulatory complexity accelerates.
The SANS 2024 SOC Survey identified lack of automation and orchestration as the single most frequently cited barrier to effective security operations, with 71 respondents naming it their biggest obstacle.
This gap is not caused by a single failure, but by compounding breakdowns in how compliance systems operate at scale.
 Manual processes strain as organizations grow.Ownership ambiguity delays remediation.Evidence is collected framework by framework, multiplying effort while eroding confidence in accuracy.Tool fragmentation obscures system-wide control health, and control drift often goes undetected for months.
Individually, these issues appear manageable; together, they silently accumulate risk while reducing visibility.
The impact is felt unevenly across the organization. Security leaders sense growing uncertainty between audits. Compliance teams are held accountable for outcomes they cannot consistently observe.
Engineering teams experience compliance as an unpredictable interruption rather than a continuous practice.
According to the State of DevOps 2026 report,
Executives receive assurance without operational context. Auditors encounter evidence that technically satisfies requirements but provides a limited signal about ongoing control effectiveness.
The result is compliance optimized for audit moments, not long-term control health, where risk and disruption persist even after a successful audit
Compliance theater is audit success without operational assurance. The program is optimized to produce artifacts on demand, not to prove that controls remain effective as systems change.
Real-world incidents illustrate this further. In October 2023, attackers breached Okta’s customer support system and accessed files belonging to 134 customers, including organizations such as Cloudflare and 1Password. The incident demonstrated how attackers could exploit support-system access and session tokens even when formal compliance certifications were in place.
As regulatory and commercial pressure increases, many organizations drift into compliance theater where the goal becomes producing a report, not proving resilience.

Policies exist, but aren’t operationalized

Controls are tested only near audit time

Evidence is collected retroactively

Remediation addresses symptoms, not systems
Figure 2. Common signs of compliance theatre
SOC 2 assessments rarely fail because organizations lack security policies. Instead, failures usually occur when controls are not consistently executed or properly documented.
Guidance from Schellman and Coalfire shows that common causes include pursuing Type 2 audits without sufficient readiness, weak documentation of control evidence, fragmented ownership of security processes, and gaps in core operational controls such as access management and change management. These symptoms are increasingly common.
A recent independent survey of CFOs and compliance professionals revealed that
This concern has been echoed by industry analysts. Security researcher Justin Pagano argued in his widely circulated critique “SOC 2 Is Dead, Long Live SOC 2” that the Trust Services Criteria are often interpreted so broadly that organizations can technically satisfy them while maintaining weak operational controls.
Manual evidence collectionFragmented toolingFrameworks are treated as isolated projectsExecution sits outside the compliance systemOver time, this approach weakens trust. Customers increase the depth of their security reviews. Auditors become more skeptical. Regulators expect stronger operational proof. Internally, teams expend more effort to achieve the same outcomes, and leadership confidence in compliance reporting erodes.
Compliance theater rarely collapses immediately. It fails gradually, through repeated friction, rising costs, and accumulating risk, until a triggering event makes the weakness visible. Regulators are also tightening oversight of audit quality.
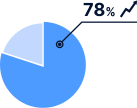
The PCAOB Enforcement Activity 2024 shows that monetary penalties imposed by the U.S. Public Company Accounting Oversight Board reached $35.7 million in 2024, a 78% increase from the previous year, signaling that audit rigor itself is now under scrutiny, not just the organizations being audited.
Compliance Quality is the degree to which a compliance program produces reliable evidence, sustains control effectiveness through change, and consistently closes control failures.
Industry surveys show that leading compliance and legal officers are starting to focus on resilience and scalability, not just checklists. For example, in Gartner’s survey of Legal, Risk & Compliance leaders, the top priorities included “ensuring compliance programs can keep pace with fast-moving regulatory requirements” (cited by 39% of respondents), alongside improving third-party risk management (40%) and strengthening compliance’s strategic impact on the company (42%).
Compliance Quality reframes compliance as a system rather than a project. Instead of asking whether a framework has been satisfied, it asks whether the underlying compliance program is capable of withstanding growth, change, and scrutiny over time.
At its core, Compliance Quality evaluates whether compliance work compounds or resets as organizations evolve.
High-quality compliance systems become more efficient, reliable, and informative as the scope expands.Low-quality systems become increasingly fragile, expensive, and disruptive.This shift in perspective matters because most organizations do not fail compliance due to a lack of intent or expertise. They fail because their compliance systems were never designed to operate continuously.
Across regulatory regimes, industries, and organizational stages, four factors consistently determine whether compliance programs stabilize or collapse. These pillars are not framework-specific; they describe properties of the compliance system itself.
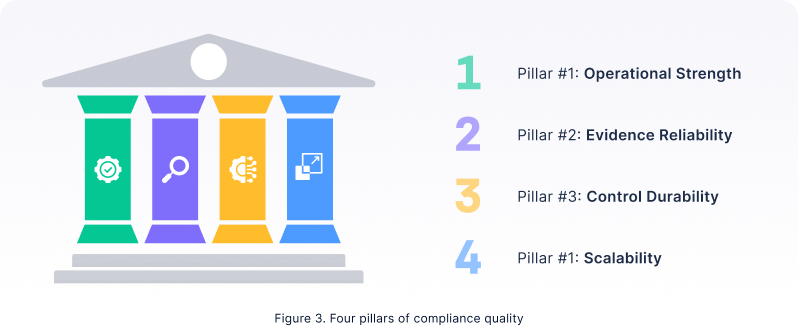
Operational strength reflects whether compliance functions as an organizational capability or as a recurring emergency.
In strong systems, ownership is clearly defined, processes are documented and repeatable, and compliance activities continue smoothly despite personnel changes or organizational growth. Audits follow predictable patterns, and preparation does not depend on a small number of individuals holding institutional knowledge.
Where operational strength is weak, compliance becomes fragile. Knowledge is siloed, processes must be rediscovered each cycle, and audits trigger fire drills. Over time, the organization becomes increasingly dependent on individual effort rather than system reliability.
Evidence is the foundation of audit, but not all evidence carries equal weight. Evidence reliability measures whether evidence is accurate, current, complete, and easy to verify.
High evidence reliability means that evidence is generated continuously as a byproduct of normal operations, stored centrally, and reflects system behavior. Both internal teams and external auditors can quickly assess control health without extensive manual effort.
In low-reliability programs, evidence collection becomes an activity in its own right. It manifests as screenshot-driven audits, manual exports, and ad-hoc reconciliation.
Evidence is collected episodically, often under time pressure, increasing the likelihood of gaps and inconsistencies. Over time, this erodes confidence not only among auditors but also within the organization itself.
Across frameworks, evidence reliability is one of the strongest predictors of audit friction and repeated findings. Programs that invest in continuous control monitoring and evidence automation see far fewer auditor questions and rarely have findings related to missing or insufficient evidence.
Modern environments are defined by constant motion. Infrastructure evolves, access patterns shift, vendors rotate, and teams reorganize.
Durable controls are designed to survive this change. They adapt automatically where possible, surface drift early, and degrade gracefully rather than failing silently..
Fragile controls
Pass until conditions changeDrift silently between auditsProduce surprise findings laterRepeated findings, surprise remediation efforts, and audit regressions almost always trace back to weak control durability rather than missing controls.
WEC highlights that 76% of CISOs report that fragmentation of regulations across jurisdictions greatly impedes their ability to maintain compliance.
In scalable systems, work done for one framework reinforces others. Controls map cleanly across requirements, evidence is reused, and new regulations integrate into existing structures.
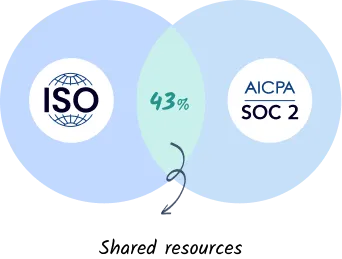
A recent audit-firm source from A-LIGN says that SOC 2 and ISO 27001 have a 43% overlap in evidence requirements.
In other words, if you have already completed a SOC 2 assessment, you may have already met 43% of the evidence needed for ISO 27001.
In low-scalability environments, each framework is treated as a separate initiative. Controls are duplicated, evidence streams multiply, and compliance costs grow faster than the business itself. What begins as a manageable effort becomes an ongoing drag on growth.
Across the industry, compliance is moving from a reporting function to an execution-driven operating model. AI is evolving from an assistive layer that helps with understanding and documentation into an operational capability that drives action and follow-through.
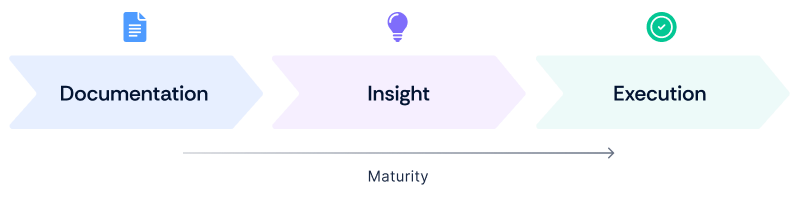
As a result, GRC systems are transitioning from systems of record to systems of action, i.e.,platforms that not only track compliance status, but actively reduce risk and prevent drift. This shift is giving rise to AI-native vertical players that own compliance outcomes rather than simply selling compliance tools.
These systems function less like dashboards and more like operational partners that absorb execution debt and reduce risk over time. This transition is about building resilience, consistency, and reliable outcomes at scale.
As regulation accelerates and scrutiny deepens, organizations will increasingly be judged not by whether they pass audits, but by whether their compliance systems deserve confidence over time.
While the industry is clearly shifting toward execution-driven compliance, most organizations do not move directly from manual processes to fully autonomous systems. Instead, they operate within a small number of dominant compliance operating models, often combining elements of multiple approaches at once.
Understanding these models helps explain why many organizations continue to experience audit friction, repeated findings, and operational drag even as tooling and automation improve.
(Internal Levels 0–1: Manual Operations + Basic Automation)
In documentation-centered compliance, the primary goal is to produce audit artifacts. Compliance work is organized around documentation, evidence collection, and status tracking, rather than execution and prevention.
This model includes both fully manual environments and early automation platforms. While tools may centralize controls and evidence, execution remains external to the system and heavily human-driven.
Operationally, this model is characterized by:
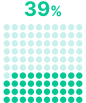
Point-in-time audits and readiness checksManual or semi-automated evidence collectionReactive remediation close to audit deadlinesHigh dependence on individual effort and coordinationThe Public Company Accounting Oversight Board found that 39% of the audits it inspected in 2024 contained significant deficiencies where auditors failed to obtain sufficient evidence to support their opinion, illustrating how compliance documentation can exist without reliably demonstrating operational control effectiveness.
Audits may be passed, but risk accumulates between audit windows, and findings often repeat year over year.
(Internal Level 2: Automation with Assistive AI)
Insight-centered compliance represents an evolution of the documentation-centered model. Here, automation is augmented with AI to improve understanding, summarization, and guidance.
According to Gartner, 76% of compliance leaders are now prioritizing better data and insight into third-party risks and similar areas, showing the demand for more continuous intelligence in compliance programs.
AI assists with tasks such as drafting policies, summarizing audit reports, interpreting control gaps, and suggesting next steps. Compliance teams gain faster insight and better clarity into what needs attention.
However, execution still occurs outside the system. Humans must translate insights into action, coordinate remediation through tickets and follow-ups, and verify closure manually.
Operationally, this model is characterized by:
Improved visibility and reportingFaster documentation and audit preparationAI-assisted interpretation without embedded executionCompliance becomes easier to understand, but not easier to operate at scale.
(Internal Level 3: System of Action / AI-Native Execution)
Execution-centered compliance represents a structural shift in how compliance is delivered. In this model, execution is embedded directly into the compliance system itself.
Controls are continuously monitored, and failures trigger automated triage, prioritization, and remediation workflows. AI operates within guardrails and approval paths, generating implementation-ready guidance, assigning ownership, tracking progress, and validating resolution with updated evidence. Compliance work no longer lives outside the platform. The system actively reduces backlog and prevents drift.
Operationally, this model is characterized by:
Continuous control monitoringClosed-loop remediation and validationReduced reliance on manual coordinationCompliance operating as an always-on functionCompliance becomes a durable trust capability rather than a recurring disruption.
Most organizations today operate between documentation-centered and insight-centered compliance. While tooling and AI have improved visibility and reporting, execution remains largely external and manual. As a result, effort remains high, outcomes remain unstable, and Compliance Quality plateaus. The transition to execution-centered compliance enables compliance quality to compound rather than reset, turning compliance from a periodic obligation into operational infrastructure.

With Scrut, your security program isn’t just about keeping pace; it’s about setting the pace. Embrace the new kind of GRC that fuels growth and resilience.