

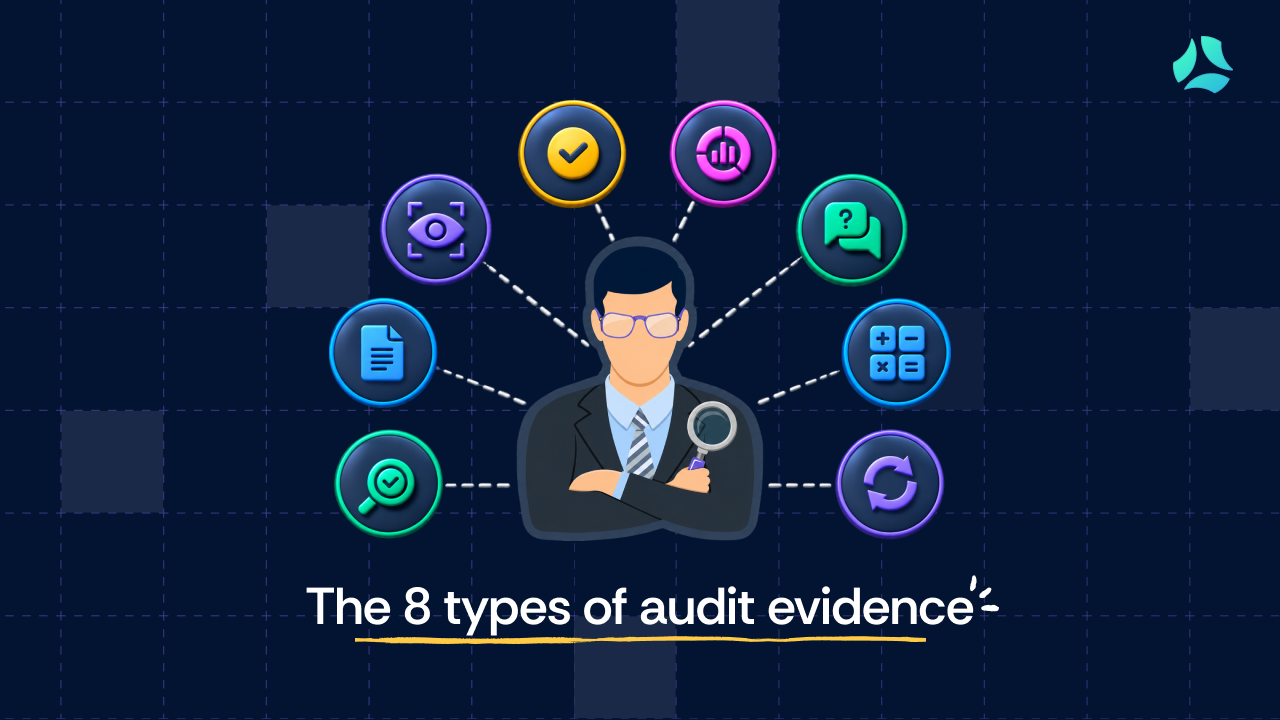


- The types of audit evidence break into 8 categories: physical examination, documentation, observation, confirmation, analytical procedures, inquiry, recalculation, and reperformance. Auditors do not treat them equally.
- Reliability runs on a hierarchy. Evidence the auditor obtains directly outranks evidence the client produces about itself.
- Auditors judge evidence on sufficiency (quantity) and appropriateness (relevance and reliability). Both must be met.
- Poor evidence organization, not missing controls, is one of the most common causes of audit friction, findings, and delayed reports.
- Continuous, control-indexed evidence collection removes most of the audit-window scramble.
If you are preparing for a SOC 2 or ISO 27001 audit, audit evidence is the thing your auditor actually forms an opinion on. Not your intentions, not your architecture diagram, and not the fact that you have a policy. Evidence is the proof that a control was designed correctly and operated the way you say it did.
ISA 500 describes audit evidence as the information on which an auditor bases the conclusions that support an opinion. PCAOB AS 1105 sets the bar it has to clear: evidence must be sufficient and appropriate to provide a reasonable basis for that opinion. These standards were written for financial audits, but the principles are identical whether the audit is SOC 2, ISO 27001, or a financial statement review.
The evidence is different; the way it is evaluated is not. This has become the whole game. As Loris Gutic, Global CISO at Bright Security, put it:
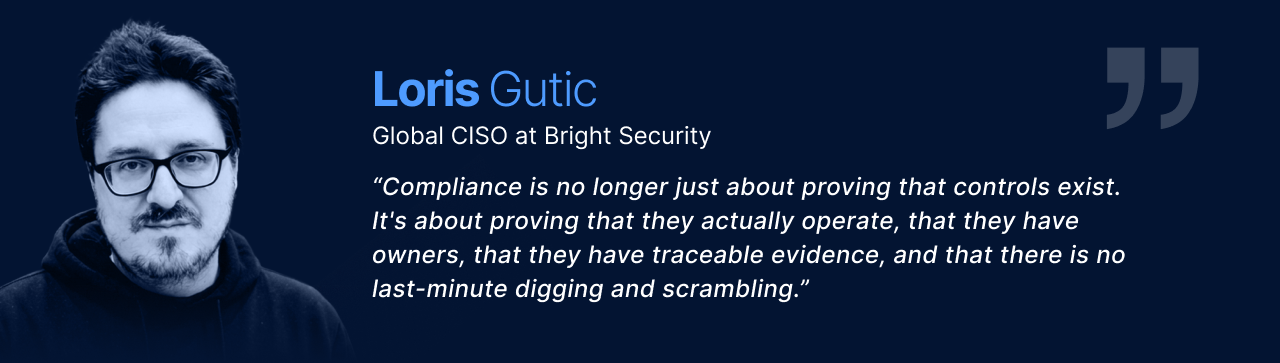
This guide covers the 8 types of audit evidence, how auditors weigh their reliability, how evidence is actually obtained, how it gets evaluated, and what separates audit-ready evidence management from the pre-audit scramble. If you are earlier in the process, it pairs with our broader guide to the compliance audit and our walkthrough of audit readiness.
Why is audit evidence important?
Audit evidence is the basis for the auditor's conclusion. Without it, an audit is just a conversation. With weak or disorganized evidence, the auditor cannot conclude that your controls work, no matter how good those controls actually are.
Two professional standards anchor this. ISA 500 establishes audit evidence as the information an auditor relies on to reach an opinion. The IIA Standards (including Standard 2310 on identifying information) describe quality evidence as information that is sufficient, reliable, relevant, and useful for the engagement's objectives. PCAOB AS 1105 adds the third anchor and the sharpest one: evidence must be sufficient and appropriate to provide a reasonable basis for the auditor's opinion.
For a SOC 2 or ISO 27001 audit, this plays out across time, not at a single moment. A SOC 2 Type II observation period runs a minimum of six months, and for renewals it typically covers a full year. The auditor is not asking whether a control works today. They are asking whether it worked on every relevant day across that window. Incomplete or poorly organized evidence directly affects the opinion, because a gap in the record reads as a gap in the control.
The Type I/Type II distinction becomes concrete here. A Type I report tests whether controls are suitably designed at a single point in time. A Type II report tests whether those same controls operated effectively across the observation period. Type I evidence is a snapshot. Type II evidence is a track record, and it is the difference that most enterprise buyers care about.
There is one hard consequence of this timing worth internalizing. As Aditya Iyer, who leads internal compliance at Scrut, describes it: with SOC 2, the internal audit you run partway through gives you time to correct mistakes, but once the audit period ends and the auditor's fieldwork begins, there is no going back. If there is a finding, there is a finding. This is also why the audit risk model matters, which is where we turn next.
The audit risk element
Audit risk is the possibility that an auditor issues a clean opinion when material problems still exist. Auditors decompose it into three parts, and understanding them tells you which of your controls will get the heaviest scrutiny.
- Inherent risk is the raw exposure before any controls exist. A control governing production database access carries higher inherent risk than one governing a marketing dashboard, simply because the consequences of failure are more severe.
- Control risk is the chance that your controls fail to prevent or detect a material problem. A control with a weak design or an inconsistent operating history carries higher control risk, and it pulls more auditor attention.
- Detection risk is the chance that the auditor's own procedures miss a material problem. Auditors manage this one by adjusting how much and how deeply they test.
A worked example makes this tangible. Suppose an auditor is testing 25 controls and one of them is access control. They find an employee who had production access, left the company, and never had that access revoked, because the offboarding process was weak and the access review process was flawed. That single control now represents high inherent risk and high control risk, and the auditor will expand evidence requests around it.
Compare that to a contractor who retained access to a deprecated, low-sensitivity dashboard. Same category of finding, but low risk, so it does not trigger the same escalation. The auditor quantifies the risk, and the controls with the highest scores get the deepest testing. This is closely related to the distinction between inherent risk vs. residual risk.
Worth knowing: the audit risk model is internal to the audit firm. You never see the calculation. What you experience is the outcome, which is that some controls get sampled far more heavily than others. Better firms run a more rigorous model and, when they find a deficiency in one control, they drill down and expand testing around it rather than accepting a surface-level pass. That expansion is a direct signal of how auditors allocate testing depth.
The 8 types of audit evidence
Professional standards, PCAOB AS 1105 for public-company audits and AU-C 500 as the AICPA's equivalent for non-issuer audits, enumerate a consistent set of evidence types. There are eight. Each carries a different reliability weight, and each shows up differently in a SOC 2 or ISO 27001 audit.
Physical examination
Physical examination is the auditor's direct inspection of a tangible asset to confirm its existence and condition. In a cloud-native SOC 2 or ISO 27001 audit this is rare, but it appears in data-center walkthroughs, hardware inventory checks, and physical access control reviews. Because the auditor observes the asset themselves, it ranks among the most reliable evidence types.
Documentation
In a SOC 2 or ISO 27001 audit, documentation is what most of the evidence package actually consists of: change tickets, access review logs, firewall sign-off emails, policies, contracts, vendor reports. Its reliability is not uniform. A system-generated log from your identity provider carries more weight than a manually maintained spreadsheet, because the auditor can trust the source. That distinction matters more than the volume of documents you produce.
Observation
Observation is the auditor watching a process being performed, such as sitting in on a quarterly access review as it happens or watching an incident response walkthrough. It confirms that a process runs the way it is documented, but it only proves what happened during the moment observed, which limits its standalone evidentiary weight.
Confirmation
When a cloud provider sends you their SOC 2 report, or a sub-processor provides a written attestation, that is confirmation evidence. It originates outside your organization, which is why auditors weight it more heavily than your own records covering the same fact. You did not produce it; they did.
Analytical procedures
Analytical procedures compare data across periods or against expectations to surface anomalies. An auditor might trend the volume of change tickets or provisioning events across the observation period and flag an unusual spike or gap for follow-up. Strong for directing attention, but it usually points to where deeper testing is needed rather than concluding on its own.
Inquiry
Inquiry is information gathered by asking people, through interviews and walkthroughs with control owners and staff. It is essential for understanding how a process actually runs, but PCAOB AS 1105 is explicit that inquiry alone is not sufficient to reduce audit risk. It must be corroborated with other evidence. Expert input, a specialist's opinion on a complex configuration for example, is treated as a form of inquiry rather than a separate evidence category.
Recalculation
Recalculation is the auditor independently checking the mathematical accuracy of a record, such as recomputing a control metric or reconciling a report total against its source. Because the auditor performs the calculation themselves, it is highly reliable within its narrow scope.
Reperformance
Reperformance is the auditor independently executing a control the organization performs, to verify it works as intended. Re-running an access review against the same population, or independently reprocessing a transaction, are examples. Like recalculation, it is highly reliable because the auditor does the work rather than trusting the client's output.
Audit evidence types and reliability hierarchy
A practical note on where to spend effort:
Not every evidence type costs the same to produce or returns the same value. Policy drafting consumes time that should go to implementation, the thing auditors actually test. Vendor questionnaires for non-critical vendors are high-effort and low-yield, because the auditor mainly checks that critical vendors were assessed on time.
Cloud security configurations, by contrast, are often low-effort and high-impact once continuous monitoring is in place. And small items matter more than they look: in Scrut's own EY audit, a missing sign-off email on one quarter's firewall review became a surprise request.
Every piece of evidence should close the loop, because a small gap is exactly what an auditor catches. You can reduce the manual side of this with automated evidence collection and disciplined audit evidence documentation.
Which type of audit evidence is most reliable?
Reliability runs on a hierarchy, and knowing where a piece of evidence sits tells you how much weight it will carry, and where to invest collection effort.
Audit evidence reliability hierarchy and weighting rationale
Reliability is not fixed. Internal evidence from a company with strong, well-monitored controls can outrank poorly sourced external evidence. The point of the hierarchy is direction, not a rigid rule. And it explains auditor behavior in practice: a better audit firm drills down, quantifies the finding, and expands sampling when the initial evidence looks unreliable. If you want the record to hold up across the whole period rather than at a snapshot, continuous compliance monitoring is what keeps it defensible.
How is audit evidence obtained?
Knowing which evidence type carries weight is only half the picture. The other half is how auditors go about collecting it. Evidence is gathered through defined audit procedures, and the choice of procedure depends on the assertion being tested and what the evidence needs to prove.
PCAOB AS 1105 sets out seven procedures:
1. Inspection: examining records, documents, or physical assets. In a SOC 2 context, this is reviewing a change ticket, a firewall rule set, or a policy document.
2. Observation: watching a process or control being performed in real time, such as sitting in on a quarterly access review as it happens.
3. Inquiry: asking control owners and staff how a process works. On its own, inquiry is not sufficient to reduce audit risk and must be corroborated.
4. Confirmation: obtaining evidence directly from an independent third party, such as a sub-processor attestation or a cloud provider's SOC 2 report.
5. Recalculation: independently checking the mathematical accuracy of records, such as recomputing a control metric or reconciling a report total.
6. Reperformance: independently executing a control the organization performs, such as re-running an access review against the same population.
7. Analytical procedures: evaluating data through comparisons and trends to identify anomalies worth investigating, such as an unusual spike in provisioning events across the observation period.
Auditors do not test everything. They may examine 100% of items, select specific high-risk items, or apply audit sampling. Sample size scales with assessed risk: the greater the risk of material misstatement, the deeper the evidence search goes, and that risk grows with every inconsistency the auditor sees. When a firm finds a deficiency in one control, the practical response is to drill down and expand testing rather than move on. For a fuller walkthrough of how this unfolds, see our guides to the SOC 2 audit process and building an internal audit checklist.
Evaluation of audit evidence
Gathering evidence is only half the work. The auditor then evaluates everything collected on two axes that ISA 500 establishes: sufficiency and appropriateness.
Sufficiency is about quantity. Is there enough evidence to support the conclusion? This scales with the size and complexity of the organization and with the assessed level of risk. Higher risk demands more evidence.
Appropriateness is about quality, and it has two components. Relevance asks whether the evidence actually bears on the assertion being tested. Reliability asks whether the evidence can be trusted, which depends on its source, the strength of the controls behind it, and its nature.
Evidence the auditor obtains directly is more reliable than evidence the client produces about itself. PCAOB AS 1105 is clear that quantity does not substitute for quality: a large pile of weak evidence does not add up to appropriate evidence.
So what does inadequate evidence look like in practice? It is rarely a total absence. More often, it is evidence that exists but fails on appropriateness:
- A change approval that happened as a thumbs-up emoji on a Slack message, which no auditor accepts as a record.
- A control screenshot with no date, so it cannot be tied to the observation period.
- A point-in-time screenshot with no population context, so the auditor cannot tell whether it represents the full set or a cherry-picked sample.
- A missing sign-off email for one quarter of an otherwise consistent quarterly control.
Every one of these failures has the same fix: someone internally needs to challenge the evidence before the auditor does.
There is a compounding cost here too. When evidence is inconsistent, the auditor's confidence drops, they escalate their risk assessment, and they request more. Consistent, well-organized evidence keeps risk assessments low; inconsistency raises them. Ongoing compliance monitoring is what keeps the record clean across the full period, rather than forcing a reconstruction under pressure.
Special considerations in audit evidence
Fraud detection. Auditors carry a responsibility to detect material misstatement arising from fraud, which calls for heightened professional skepticism and, occasionally, forensic techniques. For most GRC teams this is a secondary concern, but it explains why unexplained inconsistencies attract disproportionate scrutiny.
Going concern. In financial audits, auditors weigh evidence about an organization's ability to continue operating. Largely tangential to a security or privacy audit, but the underlying logic carries over: doubt in one area colors the auditor's view of everything else.
The computerized environment. This is where most GRC and security teams actually live, and it is where evidence has changed most. Modern evidence is increasingly cloud-native: automated pulls from CSPM tools, identity provider logs, and endpoint management platforms. That shifts the auditor's focus to digital evidence integrity, specifically the metadata, timestamps, and audit trails that prove when something happened and that it was not altered after the fact.
The distinction that matters most is between a screenshot and a system-generated log. A screenshot is point-in-time and easy to stage. A system-generated log is continuous and far harder to fake, so auditors weight it more heavily. This is why practitioners argue that auditors should have direct, scoped access to your source systems to pull information automatically, rather than depending on manually captured screenshots.
That shift has a practical consequence that surprises teams who assume cleaner evidence always means a smoother audit. In Scrut's own EY audit, the platform captured exact time-and-date logging for BCP testing and access review testing. Because the results kept coming back green, the auditors kept increasing the sample. Clean, system-generated results looked almost too good, so they went deeper to check.
Platform-generated evidence can, counterintuitively, invite more sampling, but it also survives that sampling: a compliance automation platform runs a 100% sample on checks like endpoint status, access reviews, and BCP testing, rather than the auditor's smaller manual sample. You can push more of this onto rails with automated controls testing and evidence management automation.
Audit evidence management: What good looks like (and what poor organization costs)
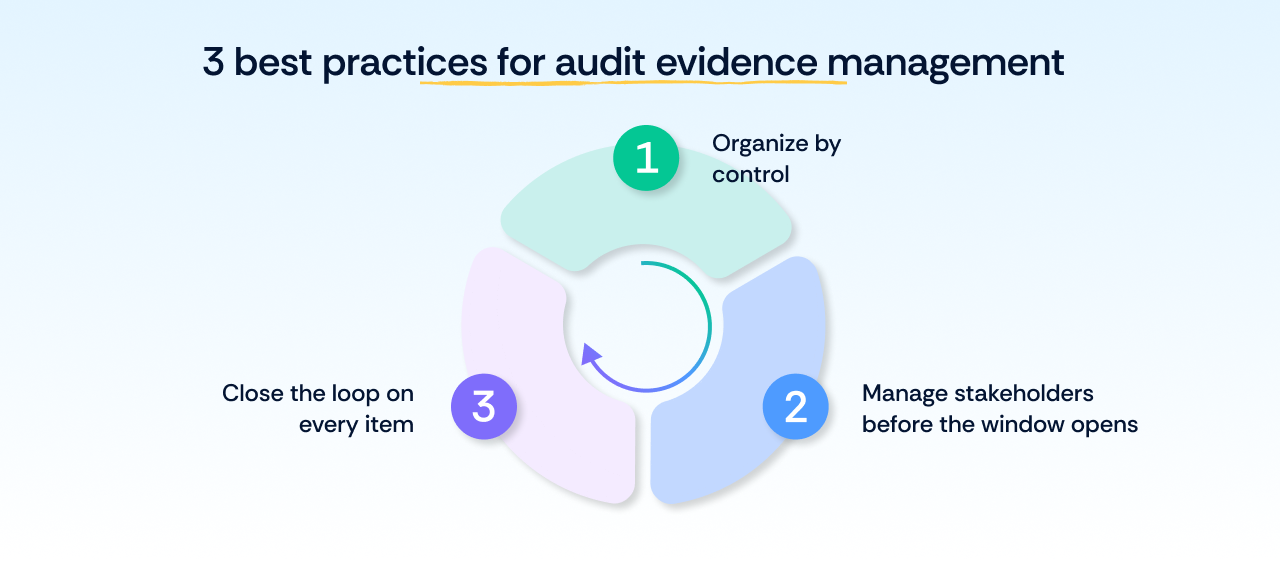
The most common audit friction point is not a missing control. It is disorganized evidence that exists but cannot be produced on time. Here is what separates audit-ready evidence management from the pre-audit scramble.
Organize by control, not by date or department. ISO 27001 has 93 controls in the 2022 revision of Annex A. File evidence by control and retrieval is instant when an auditor asks for proof of a specific control. As Aditya Iyer, GRC program manager at Scrut, puts it: when you make control-wise evidences and the auditor asks for cryptography evidence, you know exactly where it is, which saves both sides time and avoids fumbling on the call. The common failure mode is filing by date or by team, which turns every request into a scavenger hunt.
Understand what fieldwork disorganization costs. During fieldwork, the auditor asks for the population and pulls random samples from it. If a GRC manager responds by chasing department heads for samples in real time, the auditor is watching them struggle. Disorganization at this stage reads as process immaturity and can elevate the risk assessment applied to every subsequent request. Failing to produce a single sample item compounds it further.
Manage stakeholders before the window opens. Evidence ownership often spans teams. Access reviews, for instance, need the master employee list from HR and the access data from IT, and the two have to be reconciled. Define who owns what before the audit begins, not during it. Our user access review guidance covers how these hand-offs typically break down.
Close the loop on every item. Every piece of evidence should carry a clear scope period, an identified reviewer or approver, and a sign-off that constitutes a real record: an email, a platform log, or a tracked ticket. A thumbs-up on Slack is not evidence. Neither is an orphaned resource: an active Google Drive belonging to a departed employee goes unnoticed until an auditor pulls that person's name as a sample, and then it becomes a finding.
Know what "audit-ready" means. As Michael Skiles, Co-founder at ConstellationGRC, noted:
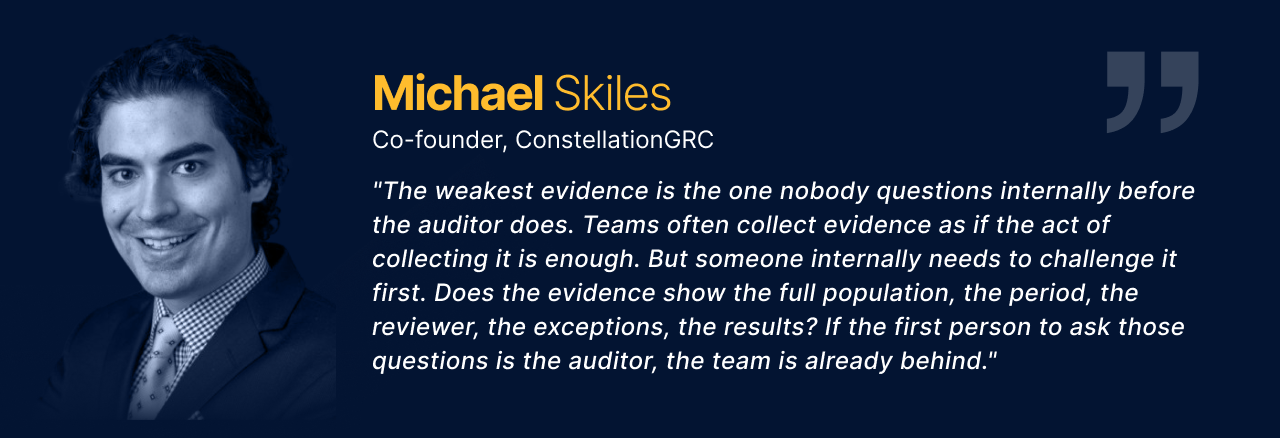
Audit-ready means the evidence is available the same day an auditor asks, not two weeks later. That requires continuous collection, not pre-audit reconstruction. A central audit center, automated evidence collection, and a repeatable internal audit checklist are what make same-day retrieval realistic.
Emerging trends in collecting and processing audit evidence
Evidence management is changing faster than most audit programs have adapted. AI and analytics have changed what auditors can see. Large datasets that manual sampling would miss are now processable, and control performance is visible at a level of granularity that wasn't practical three years ago. An auditor who previously sampled 25 access review events can now evaluate the full year's population in the same time, which changes what "sufficient" evidence means in practice. This shifts auditors from spot-checking toward evaluating the full population.
Agentic AI and shadow AI. Auditor attention is moving toward AI governance, specifically toward uncontrolled deployment. As Abhijit Kumar of EY India has noted, the hard part is identifying and controlling shadow AI: teams build or adopt AI capabilities outside the official governance framework because of business pressure, and that becomes a serious compliance concern. Expect evidence requests around AI inventory, ownership, and controls to grow.
Continuous, request-driven evidence. Calendar-driven compliance is giving way to something harder: request-driven compliance, where the question is not "can we get ready for this audit?" but "can we prove this tomorrow morning when a customer or regulator asks?" This is the practical alternative to point-in-time screenshot collection: evidence that is always on and always ready. Some organizations formalize this with a trust portal, a standing repository of artifacts where the first response to any auditor, customer, or regulator request is "here's your menu" rather than a scramble to prepare something. The portal is the proof that always-on evidence collection is working.
For deeper treatment of these shifts, see our work on the continuous audit era, AI for continuous compliance in GRC, and GRC automation.
Wrapping up
Three things carry the weight here. The 8 types of audit evidence matter because auditors treat them differently, and knowing the hierarchy tells you where a given piece of proof will land. Reliability determines where to invest collection effort, so favor evidence the auditor can obtain directly or verify independently. And continuous, control-indexed evidence management is what removes the audit-window scramble, because evidence organized by control and collected as you go is evidence you can produce the same day it is requested.
If you are mapping out your next audit, the most useful next step is a structured internal audit checklist so you catch gaps while you still have time to fix them. For teams preparing for SOC 2 or ISO 27001, compliance automation reduces the operational cost of keeping evidence audit-ready year-round, and SOC 2 audit readiness is a good place to benchmark where you stand today.
Audit evidence refers to the information and documentation that auditors collect and evaluate during an audit to support their conclusions about the financial statements. It plays a crucial role in auditing, as it helps auditors assess the fairness and accuracy of the financial information presented in those statements. Audit evidence provides a basis for the auditor’s opinion on whether the financial statements are free from material misstatements and can be relied upon by stakeholders.
Audit evidence can be categorized into several primary types, including: – Documentary evidence: This includes financial statements, invoices, contracts, and other written records. – Physical evidence: Tangible items like inventory, equipment, or property that auditors physically inspect. – Oral evidence: Information obtained through discussions and interviews with company personnel and third parties. – Analytical evidence: Data analysis and comparisons that help auditors identify patterns or anomalies. – External evidence: Information from external sources, such as bank statements, confirmations from third parties, or legal opinions. Auditors gather evidence through procedures like inspection, observation, inquiry, and confirmation, depending on the type of evidence and audit objectives.
Auditors use professional judgment to assess the reliability and sufficiency of audit evidence. They consider factors such as the source, nature, and reliability of the evidence. For instance, evidence obtained directly from an independent third party may be more reliable than evidence prepared by the entity being audited. The sufficiency of evidence depends on the audit risk and the materiality of the item being tested. Auditors aim to collect enough evidence to provide reasonable assurance that the financial statements are free from material misstatements.
Common types of audit evidence in financial audits include: – Bank statements and reconciliations – Invoices, purchase orders, and sales contracts – Payroll records and tax filings – Inventory counts and observations – Confirmation of balances with third parties – Minutes of meetings and board resolutions – Legal opinions and agreements – Financial reports and ledgers – Management representations and confirmations These forms of evidence are used to verify transactions, account balances, and the overall presentation of financial information in the statements.
Auditors encounter various challenges, including dealing with uncooperative or dishonest clients, complex transactions, and issues related to the availability and reliability of evidence. These challenges are addressed through professional skepticism, thorough audit planning, the use of specialized audit procedures when necessary, and adherence to ethical and professional standards. Auditors may also seek legal advice or engage specialists to address complex issues and ensure the quality of audit evidence. Clear communication with the client and professional skepticism in evaluating evidence help mitigate these challenges.