
Security teams need AI. Can they keep it in check?
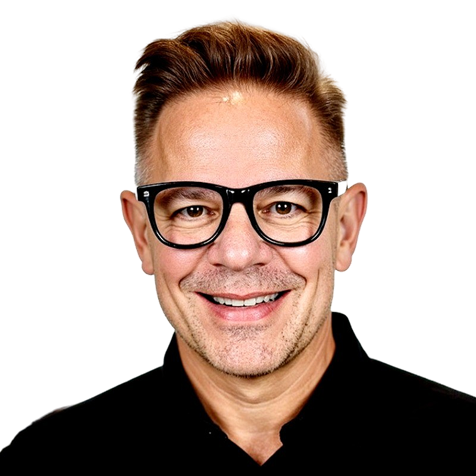
Security teams have spent years being told to do more with less. AI has arrived with a slightly different proposal: do more, faster, while attackers do the same. For defenders, refusing to use AI is not much of a strategy. Treating it as a magic fix is not one either. In this episode of Risk Grustlers, Charlie Thomas (CEO of Mitiga) joins Nicholas Muy (CISO and VP of Engineering at Scrut Automation) to discuss what happens when new capabilities arrive faster than the security programs meant to manage them, and why the real test of a security program begins when prevention does what it eventually does: fail.


Listen on Your favourite platforms


Description
Charlie and Nick move past the basic question of whether defenders should use AI and examine what using it inside a real enterprise requires. They discuss the roles frontier, open-weight, and internal models could play, including during investigations where security teams need dependable access to the right capabilities.
The conversation then turns to the less glamorous plumbing: tracking agents, mapping human and non-human identities, and monitoring activity across cloud and SaaS environments that may not provide adequate logs. Charlie also explains Mitiga’s approach to runtime detection and containment, while the pair consider regulatory pressure, long procurement cycles, and security programs designed for a much simpler time.
It is a conversation about everything that must sit around the AI before defenders can depend on it.
What listeners will take away:
- How frontier, open-weight, and internal models can play different roles in defensive security work
- Why security teams need a clear inventory of agents and human and non-human identities
- Where runtime detection and containment fit when preventive controls or SaaS visibility fall short
Quote from the episode
“Security teams need an accurate census of the agents running across their enterprise, even though the CISO may not own every agentic workflow. Everything starts with identities, both human and non-human. Without an accurate inventory, it is difficult to know what you are defending.”
— Charlie Thomas, CEO, Mitiga
About the Risk Grustlers Podcast
Risk Grustlers is a podcast for people working in security, risk, and governance who want sharper conversations than the usual industry soundbites. Each episode features CISOs, security leaders, and risk practitioners sharing how they think through the real operational challenges behind cybersecurity, compliance, AI governance, and enterprise risk.
Hosted by Aayush Ghosh Choudhury (CEO and Co-founder of Scrut Automation) and Nicholas Muy (CISO at Scrut Automation), this podcast series focuses on practical lessons, hard-earned perspectives, and the nuance that comes only from years spent in the security and compliance space.


Related Podcasts