


- Risk management techniques are structured methods used across four stages: identify, assess, respond, and monitor. Each stage needs its own approach, not one generic process.
- Most companies run formal programs but lack advanced capabilities. The gap is execution and ownership, not strategy.
- Techniques range from asset inventorying and threat modelling at the identify stage to FAIR quantification and heat maps at the assess stage. Choose based on your company's maturity, not textbook preference.
- Monitoring needs automation, documented review cadences, and clear ownership. Without those, a risk register becomes an audit artifact nobody reads.
Risk is not a future problem. It is a current reality, and most teams already know that. The gap is rarely awareness. Ask any GRC Manager, Security lead, or VP of Engineering whether risk matters, and the answer is obvious. Ask them whether their risk process is repeatable, owned, and measurable across the organization, and the answer gets quieter.
That is the real tension this audience lives with. The techniques are not secret. The templates exist. What breaks down is operationalization: making risk work repeatable, assigning someone to own each decision, and setting a review cadence that actually happens. The data backs this up.
An Accenture survey found that only 14.5% of organizations had truly advanced risk capabilities, such as tech-driven analytics and data-connected workflows.
The Government Enterprise Risk Management 2024 Survey by the Association for Federal Enterprise Risk Management (AFERM) found that 85% of organizations run a formal Enterprise Risk Management program, yet most remain basic setups with limited visibility and manual controls. The programs exist. The execution is where they fall down.
This playbook is about closing that gap technique by technique.
What is risk management?
Risk management is the process of figuring out what could go wrong and deciding what to do about it before it does. It is not the same as compliance, and conflating the two is where a lot of programs quietly fail.
Here is the distinction that matters. Compliance proves you followed a process. Risk management determines which processes matter and why. When you focus only on the risk of failing an audit, you end up with evidence and artifacts that are all nice and shiny, and you miss the changes to your business that no audit checklist covers.
That is the most common failure mode: teams treat compliance risk, essentially audit risk, as the complete risk picture. Operational, strategic, and financial risks fall outside that frame entirely, right up until one of them materializes.
A cloud outage, a third-party vulnerability, a regulatory change in a new market, a missed renewal on a critical tool. These are not hypotheticals. They are the things that actually slow launches, break customer trust, and drain resources.
Risk management gives your team a clear picture of where things could go off track and the authority to act before they do. Behind every effective program are specific techniques: practical methods that help you identify, assess, respond to, and monitor risk with consistency.
What is a risk management technique?
A risk management technique is a structured method used to carry out one of the four core stages: identify, assess, respond, and monitor. Techniques break complex risks into manageable actions, like using a risk matrix to prioritize threats or automated tools to detect vulnerabilities. The right technique improves visibility, strengthens decisions, and makes the process repeatable across teams.
Pick the technique your team will actually finish. That means matching it to your capacity, the data you have available, and whether the output will change any decision you are going to make.
Maturity matters, but it is not the only variable. A 50-person SaaS company and a 500-person fintech can be at the same stage of risk management and still need entirely different techniques, because their data, their team size, and their decision-makers are different.
The practitioner reality behind this is simple. The exercise you actually commit to doing is the best one. Textbook methods like Monte Carlo simulation and FAIR quantification are powerful, but if your team never completes them, they produce nothing. Meanwhile, heat maps get used everywhere, not because they are the most rigorous, but because teams actually finish them and stakeholders can act on the output.
Pick the risk management framework technique you will run, then build a risk register from what it surfaces.
Techniques to identify risks
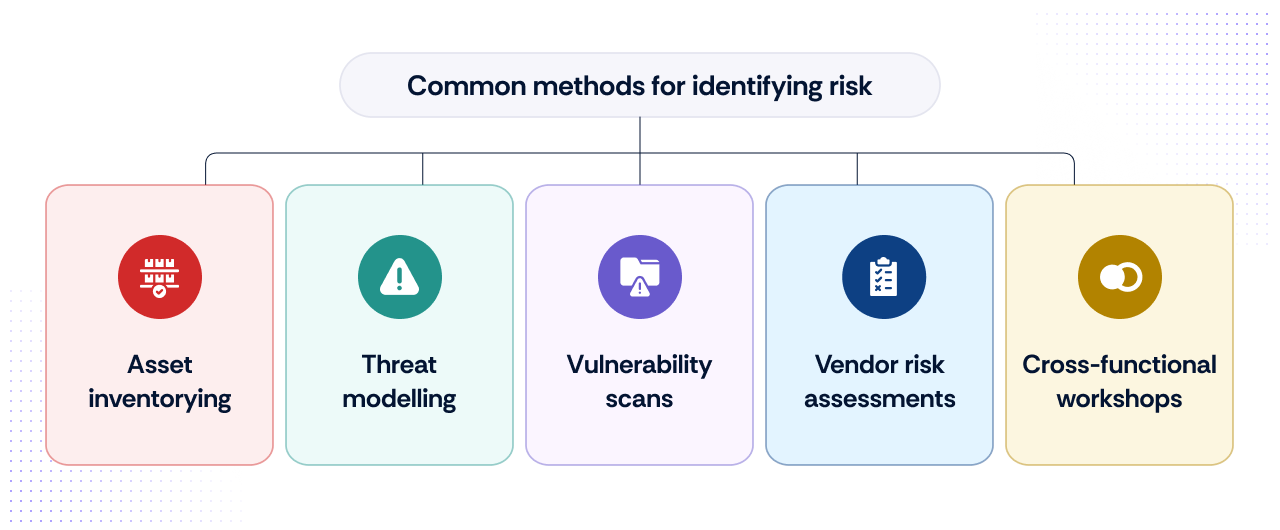
To spot risks effectively, you need visibility into your systems, people, vendors, and workflows. These techniques uncover hidden vulnerabilities, dependencies, and blind spots before they become incidents.
Order matters here: asset inventorying is the prerequisite for everything else, because you cannot threat-model or scan a system you have not inventoried.
1. Asset inventorying
This is the foundation. It means building a clear, current list of all systems, applications, devices, data stores, and cloud resources your organization uses. Knowing what you have is murky now. If you are running SaaS subscriptions and outsourcing development, you have to ask whether it is your name above the fold in the media if there is a breach, even when someone else controls the security.
The practical test practitioners use: do you know everywhere your data lives, and who has access to it? If you cannot answer that, no other technique will save you.
2. Threat modelling
Using frameworks like STRIDE or PASTA, teams map systems, data flows, and access points, then work through how those could be exploited. This surfaces not just technical bugs but design flaws and trust assumptions. It is best done early in system design. Its most common failure is being run once at launch and never revisited.
3. Vulnerability scans
Scanners like Qualys or Nessus automatically flag outdated software, misconfigurations, and unpatched systems. The scanning is the easy part. The real work is triage: a tool will surface hundreds of findings, and humans have to prioritize them based on business criticality, not just raw CVSS score. Acting on unfiltered scanner output is how teams burn a week fixing findings that never mattered.
4. Vendor risk assessments
Review third-party certifications, send due diligence questionnaires, and assess contract terms, especially for vendors handling sensitive data or holding access to your systems. Map your data flows to vendors, review their attestations, and do not treat every vendor identically. The failure mode is applying the same depth of scrutiny to a payroll SaaS as to a low-risk marketing tool.
5. Cross-functional workshops
Interviews and workshops uncover risks tools miss, like inconsistent processes and undocumented workarounds. Do not limit these to security and IT. Risk identification should pull in engineering, operations, finance, and legal, because operational and strategic risk signals rarely originate in the security team.
Risk identification techniques, application contexts, and common failure modes
Techniques to assess risks
Once risks are identified, you need to understand which ones deserve attention and why. Before the technique list, one framing decision shapes everything: qualitative versus quantitative.
Qualitative methods (heat maps, risk matrices) are the right starting point for most 50-to-500-person organizations. Quantitative methods (FAIR, Monte Carlo) require data maturity, business context, and experienced practitioners to produce defensible output. Reaching for quantitative rigor before you have the inputs produces confident-looking numbers built on estimates layered on estimates.
1. Risk matrix
Plots risks on a grid of likelihood versus impact. A data breach with high impact and high likelihood gets top priority; a low-likelihood system timeout may be accepted or monitored passively. Simple, fast, and usable at any stage.
2. Heat maps and scoring
Visual grids that rank and compare large numbers of risks quickly. Heat maps are the most widely used technique in practice, and that is intentional. They are not the most rigorous method, but they produce output that executives and boards can act on. That trade-off is valid: a technique stakeholders understand and use beats a rigorous one that never leaves the analyst's laptop.
3. FAIR model
The FAIR model is a quantitative method that estimates potential loss in dollar terms. The model is powerful, but it is only actionable when the inputs, threat frequency, and loss magnitude are grounded in real organizational data. The honest test before running it: will this change any decision you are going to make? If the answer is no, the effort is hard to justify at a 50-to-200-person company.
4. Inherent vs. residual risk scoring
Assess the raw exposure first, before any controls, then score what remains after controls are applied. Skipping this split means you never actually know whether your controls moved the needle. See our guide on inherent vs. residual risk for how to score each cleanly.
5. Define risk appetite and tolerance
Appetite sets which risks leadership is willing to accept in pursuit of objectives. Tolerance defines the operational threshold that triggers action. Appetite without tolerance thresholds is decoration, not policy. “We have a low risk appetite” means nothing until it becomes “any residual risk scored above 12 escalates to the CISO within five business days.” Connect the two, or the appetite statement stays on paper. Our breakdown of risk appetite vs. risk tolerance and risk scoring covers this in depth.
Risk scoring and evaluation techniques
Techniques to respond to risks
Not all risks need to be fixed, but all need a decision. The response you choose should be driven by whether the risk exceeds your defined tolerance. Frameworks name these slightly differently: NIST uses avoid, transfer, mitigate, accept, while ISO 31000 uses modify, avoid, retain, share. The mechanics are the same.
1. Avoid
Walk away from the risky activity altogether. A startup avoids handling financial data by outsourcing payment processing to Stripe. Clean, but not always available: you cannot avoid risk that is inherent to your business model.
2. Reduce
Apply controls to lower likelihood or impact. This is the most complex response, and it splits three ways. Preventative, detective, and corrective controls do different jobs. Preventative controls stop the event (MFA, encryption). Detective controls catch it in progress (logging, monitoring, alerting). Corrective controls handle the aftermath (incident response, patch cycles). A mature response layers all three rather than leaning on one. Our take on risk avoidance vs. risk reduction covers where each fits.
3. Transfer
Shift risk to a third party. The obvious form is cyber insurance and contractual liability clauses in vendor agreements. Two forms get missed: the shared responsibility model, where cloud providers cover infrastructure security while you own data security configuration, and liability clauses in your own customer contracts. Transfer never means the risk disappears; it means someone else absorbs a defined portion of it.
4. Accept
Deliberately tolerate a risk. This is the riskiest response and needs the most governance rigor, yet it often gets treated as a shrug. Accepting a risk does not mean you have no controls. It means you have asked whether there is anything reasonable you can do about it, decided the residual exposure is worth the business benefit, and documented that decision with justification, an owner, and a review date.
Escalation authority matters here: treat it like procurement approval levels. A director can accept up to a threshold, a VP more, and anything above goes to the CISO or board. When nobody claims the decision, everyone keeps pointing fingers at everybody else, and the risk sits unowned until it materializes. That is the failure mode that risk acceptance is supposed to prevent.
Techniques to monitor risks
Choosing a response strategy is the easy part. The harder question is whether that decision is still the right one six months later, and whether the controls you put in place are actually working.
Set a cadence that matches business change velocity. Review frequency should track how often your business actually changes, not the calendar. If the processes, technologies, and people tied to a risk do not change often, updating your register weekly means nothing. Quarterly check-ins are a reasonable baseline for most organizations, full reassessment annually, with out-of-cycle reviews triggered by material change: a new product line, geographic expansion, a major vendor swap, or a breach at a peer company.
Automated control testing: Automated control testing continuously checks that controls like MFA enforcement, data retention compliance, access provisioning and deprovisioning, and encryption configurations are actually in place. What it cannot do is decide whether a control is effective or whether a risk should be accepted. Those remain human judgment calls. Automation reduces toil on the mechanical checks so people can spend time on the decisions.
Dashboards: Dashboards give risk owners and leadership a live view of posture across departments. Their limit is the same as any dashboard: they show what is being measured, not what is being missed. A green dashboard on a stale register is worse than no dashboard at all.
Residual risk reassessment: After a control goes in, revisit the risk score. This is the step small, action-oriented teams skip most often, because there is always a new fire. But if residual risk still exceeds tolerance after the control, you either need additional treatment or a formally revised threshold with documented sign-off. Putting a control in place and never checking whether it worked is not monitoring; it is hoping.
Risk register hygiene: Preventing bloat is a monitoring discipline. Archive resolved risks, and keep the register strategically focused rather than letting it sprawl into a vulnerability list. More on this next.
Incident simulations and audit logs: Tabletop exercises test your response to real scenarios and expose gaps in the plan, but only if the learnings feed back into documented continuous compliance monitoring and risk register updates. Audit logs give you a tamper-proof, queryable record for investigations.
The risk register: Making it operationally useful, not just an audit artifact
Most risk registers are built for an audit, not for decision-making. They get populated, submitted, and forgotten. That is the failure mode that quietly kills the value of the whole exercise.
The first discipline is knowing what belongs. Strategic and material risks belong in the register: the real weaknesses in how your business operates that you cannot simply eliminate because they are part of your model. What does not belong is your entire vulnerability backlog, individual security tickets, or every risk imaginable. The risk register is not the vulnerability management process. You can run a security queue in Jira for that. Conflate the two, and the register becomes unreadable.
A minimum viable register is not complicated. Each entry needs a risk description, an inherent score, the control in place, a residual score, a named risk owner, a review date, and a treatment decision. That is enough to make it a decision-making tool rather than a document.
Then there is the politics problem. Risks get added to registers as an escalation tactic, a way to force attention on a project, or a lever for securing resources.
A register filled this way loses its strategic value. If everything is a strategic risk to the company, then nothing is. Discipline about what earns a place, and what gets sunset when the risk profile materially changes or a control has demonstrably pushed residual risk below tolerance, is what keeps it strategic. A register should only be as big as you are actually willing to care about it.
Even for a multibillion-dollar public company, 200 entries is too many. Learn how to create a risk register that stays lean.
Risk management techniques by company maturity: What actually gets used
A 50-person company attempting FAIR quantification is likely wasting effort it does not have. A 500-person company still running on a single heat map is leaving real risk visibility on the table.
Technique selection is maturity-dependent, and being honest about your stage saves you from both over-engineering and under-investing.
At the early stage (50 to 150 people, first compliance program), the goal is not comprehensiveness. It is getting the right people in the room. Much of the framework process is straightforward; the hard part is that no single person understands how the whole company works across every function. Pull in someone who knows the technology, someone who knows operations, someone who knows the back office, and you can cover most of your real risk. Most early-stage companies work from a template, copy in the risks that apply, and start there.
By the time you reach 150 to 500 people with a GRC function emerging, the template-and-copy approach stops working. You need vendor risk assessments, inherent and residual scoring, and a documented risk appetite statement, not because a framework requires them, but because the business has enough complexity that informal judgment calls no longer hold. Companies further along the journey already maintain a list of risks, often in a CISO's spreadsheet, and the work becomes importing and formalizing that rather than starting cold.
At the mature stage (500+ people, a formal risk committee), quantitative methods become viable where data supports them, response decisions route through a risk committee for high-residual risks, and board-level reporting and post-control residual reassessment become standard.
Operational Risk Management (ORM) maturity model evolution
Our GRC implementation roadmap and guide to risk management automation go deeper on scaling each stage.
Key components of using risk management techniques
The right technique run badly still fails. These are the structural elements that determine whether a risk program actually holds together.
1. Clear ownership. The musical-chairs problem, where everyone points at someone else when a risk materializes, almost always traces back to one thing: nobody's name was on it. Every risk and every control needs a named owner, not a team or a function. Assigning risk ownership is the single highest-leverage structural fix in most programs.
2. Defined thresholds. Without a defined threshold, "too risky" is just an opinion. Thresholds turn that opinion into a rule: residual risk above X escalates to the CISO within five days, full stop. That specificity is what makes appetite enforceable.
3. Integrated tooling. Automation reduces the manual effort of evidence collection, control monitoring, and scoring signals. Tools connected to your cloud, identity, and ticketing stack cut toil; disconnected tools just add another system to babysit.
4. Strong documentation. Every decision must be traceable, with justification, owner, and date. Risk documentation is what turns an accepted risk from a blind spot into a defensible choice.
5. Consistent review cycles. A quarterly review on a business that changes daily is theater. A weekly review on a business that barely changes is noise. Tie the cadence to how fast your actual risk drivers move, not to a calendar someone set two years ago.
6. Communication. This is where operationally sound programs still break down. Risk management is decision support: if you are not making the decision, someone else is, and if you cannot communicate the risk in a way that lands, they cannot decide well. There is a crunchy, framework-obsessed side to this discipline and a softer human side, and the human side gets far too little attention. Get risk ownership and communication right, and the rest of the program follows.
Who should be involved in risk management?
Risk management is a team sport. GRC teams may lead it, but risks live across systems, vendors, and workflows, so input from every function matters, and each brings knowledge the others lack.
Leadership sets risk appetite and owns the strategic risks. They alone can decide how much risk the business will accept in pursuit of growth, and without that decision, security defaults to maximum caution.
Engineering and IT know the technical exposure: the architecture weaknesses, the access patterns, the systems that cannot be encrypted or easily replaced. They see risks no framework will surface for you.
Business and operations own process and continuity risk, the operational failures that fall outside any security framework's scope, from key-person dependencies to a contact center the business fully depends on.
Legal and compliance own regulatory exposure and understand how a change in one jurisdiction ripples through the business.
Employees surface the undocumented workarounds and day-to-day friction that formal reviews miss. The person who knows that a critical process depends on one engineer's personal Dropbox folder, or that a vendor login is shared across three teams, is rarely in the room when risks are formally assessed.
The uncomfortable reality: in most SMBs and mid-market companies, no single person owns the integrated risk management view. Financial risk sits with the CFO, operational risk with the COO, cyber risk with the CISO, and they rarely consolidate. The desire to bring it together exists, but it usually stays siloed. Name that reality rather than pretending integration is seamless.
When a risk acceptance decision is needed, it typically escalates to whoever holds the authority level matching the financial exposure. That is why GRC teams need a clear escalation map before the decision arrives.
What are some risk management tools?
As risks grow across systems and teams, purpose-built tools help you move beyond spreadsheets. Here is what each category does, when it fits, and where its limits are.
A risk register is only as useful as the discipline behind it. The tool is simple: track risks, assign owners, and manage treatment. What kills it is the same thing that kills every register. Nobody reviews it after the first audit, and it becomes a longer spreadsheet with better formatting.
Continuous control monitoring tools automatically test key controls in real time. Valuable once manual checks become unsustainable, though they monitor whether a control exists, not whether it is genuinely effective.
Vulnerability scanners identify misconfigurations and unpatched systems. Essential for technical environments, but they generate findings, not priorities. You still need humans to triage.
Vendor risk management tools automate due diligence and risk scoring for third parties. Valuable once your vendor count grows past what one person can track, though they still require you to define which vendors are genuinely critical.
Risk quantification tools translate risks into financial terms. Powerful at mature stages with good data; misleading when fed estimates instead of real inputs.
Once you are running two or more frameworks simultaneously, a GRC platform stops being optional and starts being the only way to avoid duplicating work across every audit cycle. The caveat: a platform that does not integrate with your cloud, identity, and ticketing stack just becomes another system to babysit.
One boundary matters for credibility. Tools can automate evidence collection, continuous control monitoring, and scoring signals. A good platform surfaces what it knows are inherently critical items rather than trying to scientifically score everything.
What tools cannot do is decide whether a risk should be accepted, whether a control is genuinely effective, or whether a new business decision created a risk the register does not yet reflect. Those remain human judgment calls.
Integration is the other non-negotiable. Risk tools should connect to your cloud providers, identity providers, and ticketing systems. Disconnected tools create more work, not less. Our guides on GRC platforms, vendor risk management, and how to choose risk management software go deeper on selection.
How Scrut simplifies risk management for your organization
Scrut brings your risk management techniques into one place: identifying risks through automated asset discovery and vulnerability scanning, assessing them with configurable risk matrices and real-time scoring, and tracking responses through continuous control monitoring.
With 100+ integrations, Scrut automates evidence collection and gives you real-time visibility into your posture.
Where spreadsheets let anyone drop in incorrect data with no checks and balances, Scrut's risk register keeps everything versioned and permissioned, with a clear record of changes across the organization.
That turns the register from a static artifact into a living decision-making tool. And because risk management and compliance overlap, Scrut's built-in SOC 2 solution maps your risk techniques directly to the Trust Service Criteria, so each mitigation step links to the evidence and controls your auditor needs, whether you are managing ISO 27001, SOC 2, or your own register.
The CISO, Chief Risk Officer, or Head of GRC usually leads. They design the strategy, set priorities, and align it with frameworks like ISO 27001 or SOC 2. In smaller companies, this is often not even a full-time role: it lands on whoever is closest to IT and security, frequently a VP of Engineering or a head of IT wearing the compliance hat.
Yes. Compliance risks are one category within risk management. The same techniques, risk assessments and control monitoring, identify and track regulatory and standards-related risks. The caution is treating compliance risk as the whole picture, which leaves operational, strategic, and financial risks uncovered.
Organizations typically manage several: operational risks (process failures, human error, system breakdowns), security risks (breaches, malware, insider threats), compliance risks (violations of laws like GDPR or HIPAA), strategic risks (market shifts, competition, business decisions), third-party risks (vendors and partners), financial risks (fraud, budget overruns, revenue loss), and reputational risks (loss of customer trust, brand damage). Each needs to be identified, assessed, and managed, ideally in one ongoing process rather than in silos.
It depends on how fast your business actually changes. If your processes, technology, and people stay relatively constant, updating quarterly is fine, with a full top-to-bottom reassessment once a year. If your business changes fast, or a material event happens (a new product line, a market expansion, a peer breach), do an out-of-cycle review. Daily updates on a stable business mean nothing.
Yes, the four cover everything that matters. NIST calls them avoid, transfer, mitigate, accept; ISO 31000 uses modify, avoid, retain, share. Different labels, same mechanics. The count is not the issue. What breaks programs is choosing the right strategy and then not backing it with an owner, a documented rationale, and a review date.