


- Security controls have two dimensions: implementation type (administrative, technical, physical) and function (preventive, detective, corrective, compensating, deterrent, directive).
- One MFA configuration satisfies SOC 2, ISO 27001, HIPAA, and PCI DSS simultaneously when the control is mapped to all four frameworks from the start.
- IBM's 2025 data: organizations using AI and automation in security average $2.2 million lower breach costs than those without.
- Continuous control monitoring separates mature programs from annual audit exercises: automated testing surfaces failures in hours, not at the next assessment.
Cyber threats continue to accelerate. IBM's 2025 Cost of a Data Breach Report puts the global average breach cost at $4.44 million, with the U.S. average reaching $10.22 million.
Organizations that rely on automated security controls and continuous monitoring demonstrate consistently lower breach costs and faster detection times than those operating with manual, point-in-time controls.
Security controls are the measures, configurations, processes, and procedures that prevent, detect, and respond to these threats. For DevOps and GRC teams, the challenge is knowing which controls to implement for which frameworks, how to verify they are working, and how to evidence that to an auditor across SOC 2, ISO 27001, NIST, and CIS Controls simultaneously.
This guide will help you understand the different types of security controls, their functionality, and how you can scale these controls against multiple frameworks.
What are security controls?
Security controls are measures designed to protect systems, networks, and data from cyber threats. NIST's Computer Security Resource Center defines them as actions, devices, procedures, techniques, or other measures that reduce the vulnerability of an information system.
They prevent, detect, and respond to security risks, minimizing vulnerabilities and limiting potential damage.
Security controls are also the mechanism through which compliance frameworks are satisfied.
For example: A policy that states all production access requires MFA is a security policy. The MFA enforcement in the identity provider, the quarterly access review that verifies no exceptions exist, and the alert that fires when MFA is disabled on an account are the security controls that implement that policy.
Auditors evaluate controls, not policies. A documented policy with no underlying control implementation does not satisfy a SOC 2 or ISO 27001 requirement.
NIST SP 800-53 makes the relationship explicit: controls are the safeguards and countermeasures prescribed for an information system to protect the confidentiality, integrity, and availability of the system and its information. Policies establish the requirement. Controls satisfy it. Evidence demonstrates it ran.
Types of security controls: The two dimensions
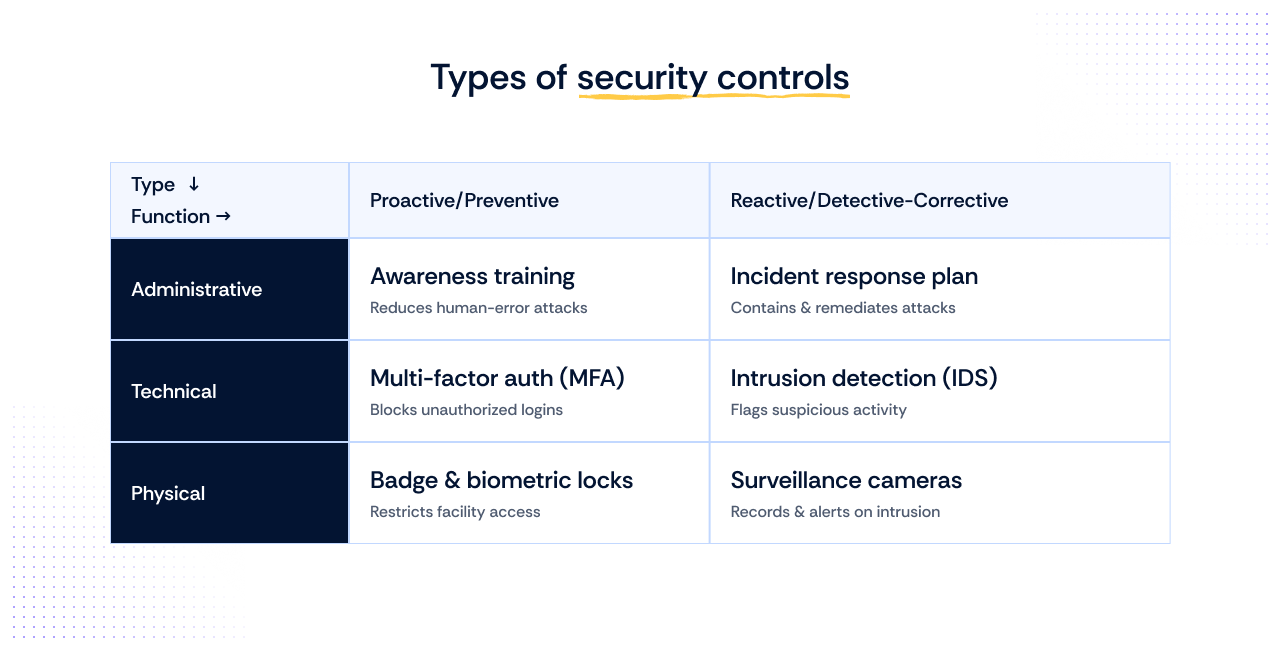
Security controls are classified along two independent dimensions.
- Implementation type describes how a control is applied.
- Function describes what the control does when a threat occurs.
Every control belongs to one implementation type and serves one or more functional categories.
Types of security controls based on function
Function-based categories describe how controls respond to security threats and their role in an organization's defense strategy.
1. Preventive controls
Preventive controls are proactive measures designed to stop security incidents before they occur. They reduce the attack surface by blocking threats and unauthorized access. Preventive controls are the highest-value category because they eliminate the need for detection and response.
- Purpose: Stop security incidents before they occur
- Main function: Reduce attack surface by blocking threats and preventing unauthorized access
- Examples: Firewalls blocking malicious traffic; MFA preventing unauthorized logins; encryption protecting sensitive data; security awareness training preventing human-error attacks; network segmentation limiting lateral movement
2. Detective controls
Detective controls identify and alert organizations to security incidents or policy violations after they occur. They provide visibility into threats that bypass preventive measures and enable timely response.
- Purpose: Identify and alert organizations about security incidents by monitoring systems for suspicious activity
- Main function: Surface security threats that preventive measures miss
- Examples: Intrusion detection systems (IDS) monitoring network activity; SIEM platforms correlating log data; audit logs tracking user activities; anomaly detection tools identifying suspicious behavior; vulnerability scans identifying unpatched systems
3. Corrective controls
Corrective controls respond to and fix security incidents after detection. They minimize damage, restore systems, and prevent recurrence. Corrective controls are the recovery layer when preventive and detective measures are insufficient.
- Purpose: Mitigate the impact of an incident and restore normal operations
- Main function: Ensure business continuity by recovering from breaches
- Examples: Incident response plans containing and remediating attacks; data backups restoring lost or corrupted data; system patches fixing post-incident vulnerabilities; malware removal tools cleaning infected devices; account suspension terminating compromised credentials
4. Directive controls
Directive controls guide, prescribe, and mandate security actions through policies, guidelines, training, and standards. They set expectations for behavior and processes, providing the governance foundation that other control types implement.
- Purpose: Define security policies, guidelines, and compliance requirements
- Main function: Provide the framework ensuring preventive, detective, and corrective measures are properly implemented
- Examples: ISO 27001 and NIST security frameworks; organizational security policies for access management; acceptable use policies; data classification standards; regulatory mandates like GDPR and HIPAA; change management procedures
5. Deterrent controls
Deterrent controls discourage malicious actions by signaling the presence of security measures and increasing the perceived risk of being caught. They reduce the likelihood of attacks without technically preventing them.
- Purpose: Discourage attacks by making detection and consequences visible
- Main function: Reduce the likelihood of cyberattacks and insider threats by warning potential attackers
- Examples: Security warning banners on login screens; surveillance cameras in secure areas; published SOC 2 or ISO 27001 certifications signaling security maturity; legal consequence notifications; visible security policies and monitoring disclosures
6. Compensating controls
Compensating controls are alternative security measures implemented when primary controls are not feasible. They must provide equivalent or greater protection and require documented justification explaining why the primary control cannot be implemented.
- Purpose: Provide alternative protection when primary controls are unavailable or technically infeasible
- Main function: Reduce security risks when primary preventive or detective controls cannot be deployed
- Examples: Enhanced monitoring and IP allowlisting for a legacy system that cannot support MFA; manual security reviews when automated scanning tools are unavailable; additional network segmentation when a firewall cannot be deployed
Compensating controls are not a permanent workaround. Auditors evaluate whether a compensating control genuinely provides equivalent protection, not simply whether one has been documented.
Types of security controls based on implementation
1. Technical controls
Technical controls use technology to enforce security policies and protect digital assets. They provide automated protections that operate without requiring human action for each event, and they produce machine-generated evidence that is directly usable in audits.
- Purpose: Use technology to enforce security policies and protect systems, data, and networks
- Main function: Provide automated security protections to detect, prevent, and mitigate cyber threats
- Examples: Firewalls and network segmentation; endpoint protection and antivirus software; data encryption at rest (AES-256) and in transit (TLS 1.3); MFA for secure login; audit logging and SIEM integration; vulnerability scanning and patch management automation; data loss prevention (DLP) tools
2. Administrative controls
Administrative controls are policies, procedures, and guidelines that govern security practices and ensure compliance. They focus on managing people and processes, establishing the requirements that technical and physical controls implement.
- Purpose: Govern security practices through policies, procedures, and training
- Main function: Define and enforce security best practices and compliance requirements
- Examples: Employee security awareness training programs; risk assessment and compliance audits; access control policies and privilege management; vendor risk management and third-party security review processes; incident response plans; change management procedures
3. Physical controls
Physical controls protect personnel, hardware, and data from physical threats. In cloud-first organizations, physical controls primarily apply to offices, endpoints, and data centers. ISO 27001:2022 dedicates 14 controls in Annex A7 to physical security.
- Purpose: Protect physical assets and restrict unauthorized access to facilities and equipment
- Main function: Prevent physical breaches, theft, and damage to infrastructure
- Examples: Badge access systems and electronic locks on server rooms; security cameras and motion detectors; visitor management logs; biometric authentication; equipment disposal procedures (secure wiping, physical destruction); clean desk policies
Why security controls are critical for organizations
A strong cybersecurity strategy requires a layered combination of function-based and implementation-based controls. Layering creates a multi-tiered defense where a failure in one layer is contained by controls in another.
Protecting against cyber threats
- Prevent unauthorized access to sensitive data and systems
- Detect and mitigate security breaches, reducing breach impact
- Ensure business continuity by minimizing disruptions caused by security incidents
Strengthening compliance and risk management
- Help organizations comply with SOC 2, ISO 27001, NIST, GDPR, HIPAA, and PCI DSS
- Support audit and reporting requirements with documentation and security logs
- Reduce financial, legal, and reputational risks from non-compliance and data breaches
Enhancing data protection and privacy
- Encrypt and safeguard sensitive information from unauthorized access
- Enforce access controls ensuring only authorized users interact with critical systems
- Prevent data leaks and insider threats through monitoring and security policies
Supporting incident response and recovery
- Enable rapid detection and response to security incidents
- Provide backup and recovery mechanisms to restore operations after an attack
- Establish security protocols for handling breaches efficiently
Managing reputation and customer trust
- Strengthen customer confidence by demonstrating commitment to security and compliance
- Reduce reputational damage from data breaches and cyber incidents
- Enhance brand value by maintaining a strong, documented security posture
Mapping security controls to major frameworks
The same underlying security control satisfies requirements across frameworks when it is documented, tested, and evidenced against each framework's specific language.
For example: A single MFA enforcement configuration can simultaneously satisfy SOC 2 CC6.1, ISO 27001 Annex A 5.17, HIPAA 164.312(d), and PCI DSS Requirement 8.
See the SOC 2 control list for a starting inventory of controls with cross-framework applicability.
NIST SP 800-53 is often used as a baseline for structuring security controls because its 1,006 controls across 20 families provide the most granular coverage.
Organizations that structure their control library against NIST 800-53 families can cross-reference to ISO 27001, SOC 2, and PCI DSS requirements to identify shared evidence opportunities.
How to choose the right security controls for your organization
Selecting the right security controls requires a strategic approach based on risk, compliance obligations, and operational context. NIST SP 800-53 Rev 5 contains over 1,000 security and privacy controls across 20 families.
No organization needs to implement every one. The selection process determines which controls provide the highest risk reduction for the specific environment.
- Conduct a risk assessment. Identify potential threats, vulnerabilities, and the business impact of security failures. Prioritize controls based on the combination of risk severity and the likelihood that the threat will be realized without the control in place. See Scrut's cyber risk management frameworks guide for a structured starting point.
- Align with compliance requirements. Identify which frameworks and regulations apply based on customer geography, data type, and contract requirements. Map the required controls for each framework and identify the shared controls that can be implemented once to satisfy requirements across frameworks.
- Categorize assets and data. Identify critical assets and classify sensitive data to apply appropriate controls. Encryption for sensitive data at rest, access controls for restricted systems, and enhanced monitoring for high-value assets are prioritized based on the classification.
- Implement a layered approach. Choose a mix of preventive, detective, corrective, directive, deterrent, and compensating controls across all three implementation types. A layered approach ensures that a failure in one control is contained by controls in adjacent layers.
- Evaluate business operations and scalability. Ensure selected controls support operational needs and can scale with growth. Controls that create friction in normal workflows generate pressure for exceptions that accumulate into compliance gaps over time.
- Automate monitoring and evidence collection. Leverage automated security tools for continuous monitoring, anomaly detection, and real-time threat response. Automated tools generate timestamped evidence as a byproduct of normal operation, eliminating the manual evidence collection sprint before each audit.
- Test and update controls regularly. Security threats evolve. Controls that were effective when implemented may require updates as attack patterns change, systems are modified, and new vulnerabilities emerge. Annual penetration testing, continuous vulnerability scanning, and periodic control effectiveness reviews are the operational mechanism.
Security controls in cloud and Zero Trust environments
Cloud environments change the implementation landscape for security controls without changing the underlying requirements. The shared responsibility model determines which controls the cloud provider owns and which the customer owns.
For example: AWS, Azure, and GCP carry their own SOC 2 and ISO 27001 attestations covering the physical and logical infrastructure layer. Application, identity, data, and access controls above that layer are the customer's responsibility.
Zero Trust architecture reorganizes the preventive control layer around the principle that no network location is inherently trusted. Access decisions are made per-request based on identity, device health, and behavioral signals.
For DevOps teams, Zero Trust translates into specific control implementations:
- Identity-based access policies replacing network-perimeter access
- Device health checks as a condition of access
- Continuous session monitoring
- Micro-segmentation limiting blast radius when a credential is compromised
AI-assisted security controls are an emerging category in 2026.
Behavioral analytics tools identifying anomalous user activity, automated threat intelligence platforms updating blocking rules based on current threat data, and AI-driven vulnerability prioritization systems ranking remediation by exploitability and business impact are entering the control landscape.
These detective and preventive controls with automated decision components require governance to ensure they operate within defined risk parameters.
According to the IBM 2025 Cost of a Data Breach Report, organizations using AI and automation in security had average breach costs $2.2 million lower than organizations without these capabilities. Automated monitoring surfaces control failures in days; manual review surfaces them at the next audit.
How to implement security controls: A step-by-step approach
The implementation lifecycle for security controls follows four phases that repeat as the environment changes.
Phase 1: Identify and prioritize
Map the frameworks in scope to their specific control requirements. Conduct a gap assessment documenting what is in place, what is partially implemented, and what is absent. Prioritize gaps by audit risk and security risk.
Build a shared control library from the start with explicit cross-framework references, so a single MFA implementation satisfies SOC 2 CC6.1, ISO 27001 Annex A 5.17, HIPAA 164.312(d), and PCI DSS Requirement 8 simultaneously.
See the SOC 2 scope guide for how to set the right boundary before building the control library.
Phase 2: Design and assign ownership
For each required control, document what it does, what systems it applies to, how effectiveness will be measured, and what evidence it produces when it runs. Assign a named owner to every control. The owner is accountable for the control's configuration, the evidence it produces, and the response when it fails. GRC teams own the monitoring program. Control owners own the controls.
Phase 3: Test and validate
Control testing verifies that a control is operating as designed and producing expected results, distinct from verifying its initial implementation. Technical controls are tested through automated configuration checks, vulnerability scans, and penetration testing.
Administrative controls are tested by reviewing process records and sampling evidence of process execution. Physical controls are tested through facility walkthroughs and access log reviews.
Annual penetration testing is required by PCI DSS 4.0.1 and expected by ISO 27001 and SOC 2 auditors, covering the full boundary of in-scope systems. See what auditors actually look for for the four evidence criteria auditors apply when evaluating control testing.
Phase 4: Monitor and maintain continuously
Controls drift. An MFA policy enforced on all accounts today may develop exceptions as service accounts are created without MFA or temporary exceptions are configured and never revoked. Continuous control monitoring automates periodic testing: daily MFA enforcement checks, weekly access permission reviews, continuous encryption configuration validation.
Each automated test produces a timestamped result. Failures trigger alerts routed to the control owner with the specific framework requirement and remediation guidance.
Evidence accumulates throughout the year, available for assessment on demand.
See how Scrut approaches continuous compliance monitoring for the operational model.
Simplifying your compliance journey with Scrut
Scrut streamlines security controls implementation and continuous management by automating control mapping to required frameworks, providing a centralized dashboard for oversight, and enabling real-time compliance monitoring across SOC 2, ISO 27001, HIPAA, PCI DSS, NIST, CIS Controls, and other frameworks from a single control library.
See the 2026 Business Impact of Compliance Automation report for benchmarks on how organizations using Scrut reduced manual effort and accelerated audit readiness.
To know how Scrut helps DevOps and GRC teams implement, test, and monitor security controls continuously across SOC 2, ISO 27001, and NIST. Request a demo.
Prevention controls block threats before they occur, while detection controls identify and alert organizations about incidents that bypass preventive measures. Prevention stops attacks, whereas detection ensures missed threats are quickly addressed. Together, they create a layered security approach.
IT security controls protect an organization’s infrastructure, including networks and servers, using firewalls, access controls, and encryption. Digital security controls have a broader scope, covering data privacy, online identity protection, and secure transactions. While IT security focuses on technical infrastructure, digital security extends to overall online safety and personal data protection.
Security controls support regulatory compliance by protecting sensitive data, mitigating risks, and enforcing security policies required by standards like ISO 27001, NIST, GDPR, and HIPAA. They prevent breaches, detect threats, and streamline audits, aiding risk assessments and compliance reporting while reducing fines and reputational risks.
NIST security controls are a set of guidelines defined in NIST Special Publication (SP) 800-53 to help organizations manage cybersecurity risks. These controls cover various aspects of security, including access control, data protection, incident response, and risk management.
NIST SP 800-53 serves as a baseline for various compliance frameworks, including ISO 27001, SOC 2, HIPAA, GDPR, and FedRAMP. Organizations can map their security controls to NIST guidelines to streamline compliance efforts.