



- SaaS compliance is documented proof that security practices meet framework requirements. Enterprise buyers ask for compliance documentation before anything else.
- SOC 2 is the right first framework for most U.S. enterprise deals. HIPAA and PCI DSS are mandatory obligations, not choices, when relevant data is in scope.
- 70% of controls required by SOC 2, ISO 27001, and HIPAA overlap. One shared control library makes every framework after the first considerably cheaper.
- Teams that automate evidence collection spend days preparing for audits. Teams that reconstruct evidence manually spend four to eight weeks.
An enterprise prospect is three weeks into your sales cycle. The deal is moving. Then their procurement team sends a 200-question vendor security questionnaire and asks for your SOC 2 Type 2 report. You do not have one. The deal stalls.
This is the moment SaaS compliance stops being an abstract best practice and becomes a revenue problem. In 2026, enterprise buyers in every vertical treat compliance documentation as a procurement gate.
The question is not whether to build a compliance program. It is how to build one that wins customers, scales with the business, and does not consume the engineering team in the process.
This guide covers the frameworks that matter for SaaS companies, the compliance vs security distinction that trips up most founders, a step-by-step implementation roadmap, and a checklist that turns compliance into a repeatable operational discipline.
SaaS compliance vs SaaS security: What is the difference and why it matters
Security and compliance are related but distinct disciplines, and conflating them produces programs that are strong in one dimension and weak in the other.
- SaaS security is the set of technical and operational controls that protect systems, data, and users from unauthorized access, data loss, and service disruption. Encryption, access management, vulnerability scanning, incident detection, and penetration testing are all security practices. They reduce actual risk.
- SaaS compliance is the documented, auditable proof that those security practices meet the specific requirements of a recognized framework, regulation, or contractual obligation.
A SOC 2 report is compliance documentation. An ISO 27001 certificate is compliance documentation. A completed HIPAA risk analysis is compliance documentation. Compliance does not create security; it demonstrates that security exists and operates consistently.
Which compliance frameworks matter for SaaS companies in 2026
SOC 2: The U.S. enterprise default
SOC 2 is the starting point for the majority of SaaS companies selling to U.S. enterprise buyers. Issued by the AICPA, it evaluates security controls across five trust service criteria.
The Security criterion is mandatory. Availability, Processing Integrity, Confidentiality, and Privacy are optional depending on the scope of services. See SOC 2 scope guide for how to define your boundary before readiness begins.
SOC 2 is not a certification. It is an audit report issued by a licensed CPA firm. A clean report means your controls were tested and held up during the observation period. The report covers a specific time window and must be renewed annually.
SOC 2 Type 1 evaluates whether controls are designed correctly at a point in time. Type 2 evaluates whether those controls operated effectively over a three to twelve month period. Enterprise buyers require Type 2.
Budget six to nine months for a first Type 2 audit. First-year cost including tooling, internal time, and auditor fees typically runs between $20,000 and $80,000 for a growth-stage SaaS company.
ISO 27001: The global enterprise standard
ISO 27001 is the international information security management system (ISMS) standard, recognized by enterprise buyers in Europe, the UK, Asia-Pacific, and the Middle East. It produces a certificate issued by an accredited certification body after a two-stage audit.
Annex A of the 2022 version contains 93 controls across four themes. For SaaS companies with European or global revenue, ISO 27001 is often a procurement requirement, not a differentiator.
According to the A-LIGN 2024 Compliance Benchmark Report, SOC 2 and ISO 27001 share a 43% overlap of evidence requirements.
Organizations that have already achieved SOC 2 can typically complete ISO 27001 in three to five months by extending the existing control library, without rebuilding from scratch.
GDPR and data privacy regulations
The General Data Protection Regulation applies to any SaaS company that processes personal data of EU or UK residents, regardless of where the company is incorporated. Fines reach four percent of global annual revenue.
Key requirements include
- A documented lawful basis for processing
- Data subject rights processes (access, deletion, portability)
- Breach notification to the relevant supervisory authority within 72 hours of discovery
- Data protection impact assessments for high-risk processing
- Data Processing Agreements (DPAs) with every vendor that processes personal data on your behalf.
GDPR compliance is a baseline legal obligation for SaaS companies with European users or employees, not a competitive differentiator. The California Consumer Privacy Act (CCPA) and its amendment CPRA, apply similar obligations to California residents. SaaS companies with users across jurisdictions typically operate against a combination of privacy frameworks simultaneously.
HIPAA: Mandatory for healthcare SaaS
The Health Insurance Portability and Accountability Act applies to SaaS companies that create, receive, maintain, or transmit protected health information (PHI) as a covered entity or as a business associate of a covered entity.
There is no opt-in: if PHI flows through your system, HIPAA obligations apply. Core requirements include a completed and documented risk analysis, a risk management plan, executed Business Associate Agreements (BAAs) with every vendor handling PHI, workforce training, and defined breach notification processes with a 60-day notification window.
A completed BAA is a prerequisite for any healthcare customer contract. OCR ran 22 enforcement actions in 2024 and 21 in 2025, with inadequate risk analysis cited in the majority of settled cases. See healthcare cybersecurity frameworks guide for the full regulatory picture.
PCI DSS: Mandatory for payment processing
PCI DSS 4.0.1 applies to any SaaS company that stores, processes, or transmits payment card data. The most effective compliance strategy is scope reduction: using tokenization, outsourced payment processing, or validated point-to-point encryption to remove payment card data from your systems entirely.
Every system that falls out of scope reduces the assessment surface, the evidence burden, and the ongoing maintenance cost. See who needs PCI DSS compliance to determine your level and obligations.
Additional frameworks by use case
SaaS compliance vs cloud compliance: Where do the boundaries sit?
Cloud compliance and SaaS compliance overlap but are not the same obligation.
- Cloud compliance refers to the security and data residency obligations that apply to the cloud infrastructure layer, typically managed by the cloud provider under a shared responsibility model.
AWS, Azure, and GCP carry their own SOC 2, ISO 27001, FedRAMP, and PCI DSS attestations for the infrastructure they operate.
These attestations cover the physical and logical infrastructure layer, not the application you build on top of it.
- SaaS compliance is the obligation that sits above the infrastructure layer.
As a SaaS vendor, you are responsible for how your application handles data, who can access it, how breaches are detected and reported, and how you contractually bind the vendors you rely on.
Your cloud provider's SOC 2 report does not satisfy your customers' request for your SOC 2 report. The shared responsibility boundary ends at the infrastructure layer; your compliance program begins there.
Your cloud provider is responsible for the security of the cloud. You are responsible for security in the cloud. Your SaaS compliance program covers everything in your control: application configuration, access management, data handling, vendor relationships, and incident response.
The SaaS compliance implementation roadmap
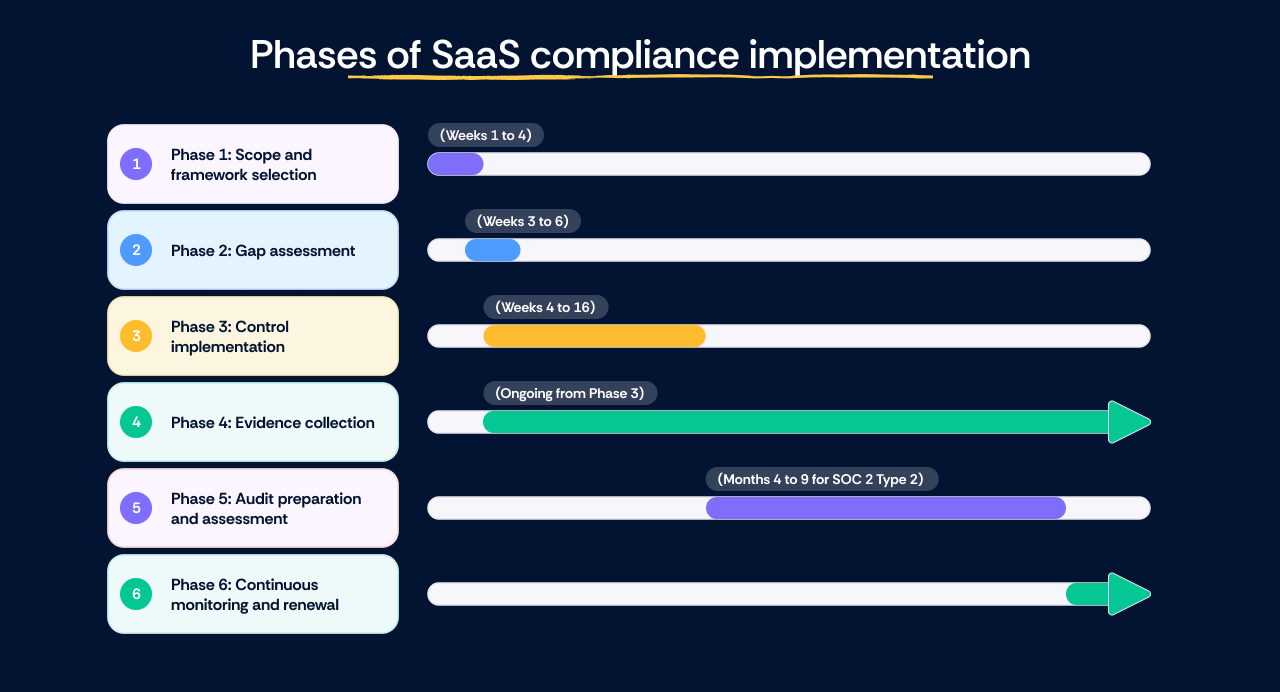
Phase 1: Scope and framework selection (Weeks 1 to 4)
Define which compliance frameworks apply based on the customer geography, data type, and contract requirements driving the compliance conversation. Identify the systems, vendors, and processes that fall within scope for each framework.
Map your data flows, specifically where customer data enters your systems, where it is stored, how it is processed, and where it exits to third parties. See the SOC 2 scope guide for a step-by-step approach to scoping decisions.
Key point: The scoping decision is the highest-leverage choice in the entire compliance program. A narrowly but accurately defined scope reduces the assessment surface, the control burden, and the cost of every future audit. A scope that is too broad creates unnecessary compliance work. A scope that is too narrow creates audit findings.
Phase 2: Gap assessment (Weeks 3 to 6)
Assess your current control environment against the requirements of each framework in scope. Document what is in place, what is partially implemented, and what is missing. Prioritize gaps by their audit risk (how likely they are to produce a finding) and their business risk (what happens if the control fails).
The most common gap categories for early-stage SaaS companies are:
- No formal access review process with documented evidence
- No executed vendor agreements (BAAs, DPAs, subprocessor lists)
- No written incident response plan that has been tested
- No formal risk assessment
- No audit logging with a documented review schedule
Phase 3: Control implementation (Weeks 4 to 16)
Implement controls starting with the highest-risk gaps identified in the assessment. Assign a named owner to every control. Document the implementation, including what the control does, what systems it applies to, how effectiveness is measured, and what evidence it produces. Build a shared control library from the start.
A single MFA enforcement policy maps to SOC 2 CC6.1, ISO 27001 Annex A 5.17, HIPAA 164.312(d), and PCI DSS Requirement 8 simultaneously.
See the SOC 2 control list for a starting inventory with cross-framework applicability.
Universal controls, including AES-256 encryption, TLS 1.3, vendor inventories, incident response runbooks, and automated evidence collection, make an organization approximately 70% audit-ready across SOC 2, ISO 27001, and HIPAA. Map these shared controls from day one; retrofitting the mapping later costs a disproportionate amount of additional time.
Phase 4: Evidence collection (Ongoing from Phase 3)
Evidence collection is the operational bottleneck in most compliance programs. For each control, document what evidence demonstrates the control is operating: configuration exports, access review records, training completion logs, vendor agreement files, penetration test reports, and vulnerability scan results. Establish who collects each type of evidence, how frequently, and where it is stored.
Organizations that collect evidence manually before each audit spend four to eight weeks in a reconstruction sprint. Organizations that automate evidence collection from their existing cloud infrastructure, identity systems, and security tools accumulate audit-ready evidence continuously. When the auditor arrives, the evidence exists and only needs to be organized.
Phase 5: Audit preparation and assessment (Months 4 to 9 for SOC 2 Type 2)
For SOC 2 Type 2, the observation period is a minimum of three months. The auditor tests whether controls operated effectively throughout that period, and not only at the point of assessment.
Engage your auditor before the observation period begins so scope and control objectives are agreed. Conduct an internal readiness review or mock audit at the midpoint of the observation period to surface gaps while remediation is still feasible.
The pre-assessment phase is for validation, not discovery. Every gap found in the final month before the auditor arrives is a remediation timeline that may not close before the assessment.
Teams that discover gaps during the auditor's review create management responses and findings that appear in the final report.
See SOC 2 audit best practices for a phase-by-phase preparation guide.
Phase 6: Continuous monitoring and renewal
Compliance does not end when the report is issued. SOC 2 requires annual renewal. ISO 27001 requires annual surveillance audits with recertification every three years. HIPAA requires ongoing risk analysis updates and policy reviews. PCI DSS requires quarterly vulnerability scans and annual penetration testing.
The operational discipline that determines whether a compliance program scales is the same discipline described in Phase 4: continuous evidence collection and control monitoring.
Teams that build this infrastructure during the first audit cycle enter every subsequent cycle with a documented baseline and a year's worth of evidence already collected.
Build your SaaS compliance foundation
Use this practical checklist to make sure you have the essential policies, controls, data protections, and evidence in place.
What changes in 2026 that SaaS companies need to act on
Three regulatory and market developments in 2026 affect SaaS compliance programs in ways that were not visible in earlier years.
- ISO 42001 is appearing in enterprise procurement checklists. ISO 42001, the AI management system standard, published in December 2023, is increasingly referenced in enterprise vendor assessments for SaaS companies with AI-embedded features. Organizations that have ISO 27001 in place have a structural head start: ISO 42001 builds on the same ISMS architecture and shares significant control infrastructure.
- NIST CSF 2.0 changes the governance conversation. NIST CSF 2.0, published in February 2024, added a sixth function, Govern, to the framework. For SaaS companies managing U.S. government or regulated industry customers, CSF 2.0 shifts the expectation from security as a technical practice to security as an organizational governance program, with documented roles, policies, and board-level accountability.
- AI tool usage creates new compliance obligations. General-purpose AI tools used by employees may process customer data. Under GDPR, HIPAA, and SOC 2, AI tools that receive personal data or PHI require the same contractual protections as any other vendor: DPAs under GDPR, BAAs under HIPAA, and subprocessor disclosure under most enterprise data processing agreements. Organizations that have not audited their AI tool stack for compliance obligations carry undisclosed risk.
How Scrut helps SaaS companies build and scale compliance programs
Scrut is built for the SaaS compliance reality: the first compliance framework needs to be achieved fast enough to unblock enterprise deals, and every framework added after the first needs to reuse the work already done, not replicate it.
According to the 2026 Business Impact of Compliance Automation report, 80% of organizations using Scrut established customer trust earlier in their sales cycles after implementing structured compliance processes.
The platform integrates with the cloud infrastructure, identity systems, security tools, and business applications that SaaS companies already use, and automates evidence collection as a byproduct of normal operations.
Controls are mapped across SOC 2, ISO 27001, HIPAA, PCI DSS, NIST, GDPR, and other frameworks simultaneously from the first implementation. When a new framework is added, the existing control library extends; it does not start over.
- For founders: the compliance roadmap from scope to audit becomes measurable and predictable.
- For GRC managers: the evidence library exists year-round, available for assessment on demand.
- For engineering teams: compliance obligations surface as a structured program with named owners and defined timelines, not recurring fire drills before each audit.
It depends on the framework and starting point. SOC 2 Type 2 is typically the first target for SaaS companies, and the realistic timeline from starting readiness work to receiving a Type 2 report is six to nine months, including a minimum three-month observation period. ISO 27001 takes a similar timeline as a standalone effort, but organizations with SOC 2 in place can compress it to three to five months given the significant control overlap. HIPAA compliance does not have a fixed timeline; it is an ongoing obligation requiring an initial risk analysis and BAA execution before any PHI is handled. PCI DSS assessment timelines depend on the chosen level and scope.
For most U.S.-focused SaaS companies, SOC 2 Type 2 is the right first framework. It is the standard enterprise buyers in the U.S. recognize and request during procurement. ISO 27001 should follow when European or international expansion creates procurement requirements for it. If the product handles PHI, HIPAA obligations exist independently and cannot be deferred. If the product processes payment card data, PCI DSS is mandatory from the first transaction. The decision should be driven by which framework is currently blocking deals or creating mandatory legal obligations. See our compliance frameworks guide for a decision tree.
Yes, and many SaaS companies pursuing global enterprise customers achieve both. According to the A-LIGN 2024 Compliance Benchmark Report, SOC 2 and ISO 27001 share 43% of evidence requirements, meaning the second framework requires extending the existing control library, not constructing a new one. Organizations that map their controls across both frameworks from the first implementation typically achieve ISO 27001 in three to five months after completing SOC 2. See the SOC 2 vs HIPAA comparison for a framework-to-framework control mapping reference.
A SOC 2 report is an audit document prepared by a licensed CPA firm describing the results of testing your controls against the AICPA Trust Services Criteria. It is not a certificate and it is not issued by the AICPA. It is issued by your auditor and covers a specific observation period. An ISO 27001 certificate is a formal certification issued by an accredited certification body (CB) confirming that your information security management system meets the requirements of the ISO 27001 standard. The certificate is valid for three years with annual surveillance audits. Enterprise buyers in the U.S. typically ask for your SOC 2 report. Enterprise buyers in Europe and internationally typically ask for your ISO 27001 certificate.
Organizations that collect evidence manually before each audit spend four to eight weeks of GRC and engineering team time per audit cycle reconstructing evidence of what controls were doing throughout the year. Continuous compliance monitoring automates that evidence collection from the tools and systems the organization already uses, accumulating audit-ready evidence throughout the year. When the auditor arrives, the evidence is organized and ready. According to the 2026 Business Impact of Compliance Automation report, 87% of engineering respondents reported reduced manual effort after implementing Scrut. The team time saved by automated evidence collection is the primary cost driver that continuous monitoring addresses.